

firmware
 brucedevices/firmware
Predatory ESP32 Firmware
bluetooth-securityembedded-systems-securityexploitation+9
brucedevices/firmwarePredatory ESP32 Firmware

 gmh5225/awesome-llvm-security
Curated collection of LLVM security resources covering binary lifting, code obfuscation, static analysis, symbolic execution, sanitizers, and…
 0sec-labs/0
Full-stack AI security OS for your browser, terminal, and agents. Find, verify, and fix vulnerabilities. Prioritized by business impact instead of…
 lucadibello/tmux-fuzzing
Enhanced fuzzing for tmux using OSS-Fuzz. Includes custom `cmd-fuzzer` and `argument-fuzzer` harnesses for improved code coverage and a PoC for…
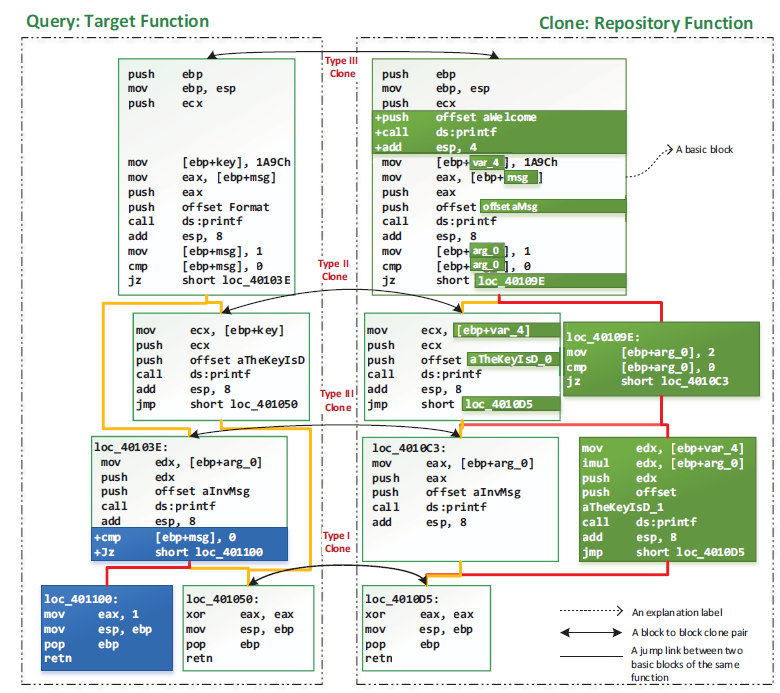 mcgill-dmas/kam1n0-community
Scalable assembly analysis platform for indexing, clone search, and executable classification using static, dynamic, and machine-learning techniques…
 githubsecuritylab/seclab-taskflows-fuzzing
An LLM-driven fuzzing pipeline powered by the GitHub Security Lab Taskflow Agent
 vesjolyjd/kaspersky_cve-2024-3094
Security review of CVE-2024-3094 (XZ Utils backdoor) including threat modeling, static/dynamic code analysis, fuzzing with AFL++, and a…
 khoatran107/cve-2025-38001
C-based proof-of-concept exploit for CVE-2025-38001, demonstrating vulnerability exploitation and code analysis for security research.
 enessar/libpng_oss-fuzz
Security research project on fuzzing libpng with OSS-Fuzz. Includes seed corpus analysis, custom read/write fuzzers, and a proof-of-concept exploit…
 nidhihcl/external_expat_2.1.0_cve-2022-43680
C library for stream-oriented XML parsing with a focus on vulnerability analysis and exploitation of CVE-2022-43680, enabling fuzzing and…
 jack0we/cve-2024-6387
Proof-of-concept exploit for CVE-2024-6387, a remote code execution vulnerability in OpenSSH server, demonstrating exploitation techniques for…
 trinadh465/platform_external_libvpx_v1.4.0_cve-2023-5217
C library for VP8/VP9 video encoding and decoding, with a focus on security patching for CVE-2023-5217.
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
 r00tkitsmm/pishi
Pishi is a code coverage tool like kcov for macOS.
 horkimhab/cve-2026-442_
CVE-2026-44289, CVE-2026-44290, CVE-2026-44291, CVE-2026-44292, CVE-2026-44294, CVE-2026-44295 - protobuf.js
 off-by-1-labs/flawed
Fix-Like Artifacts With Embedded Defects
