
skipfish
 spinkham/skipfish
Web application security scanner created by lcamtuf for google - Unofficial Mirror
crawlerdynamic-analysis-sandboxingfuzzing+7
878
spinkham/skipfishWeb application security scanner created by lcamtuf for google - Unofficial Mirror
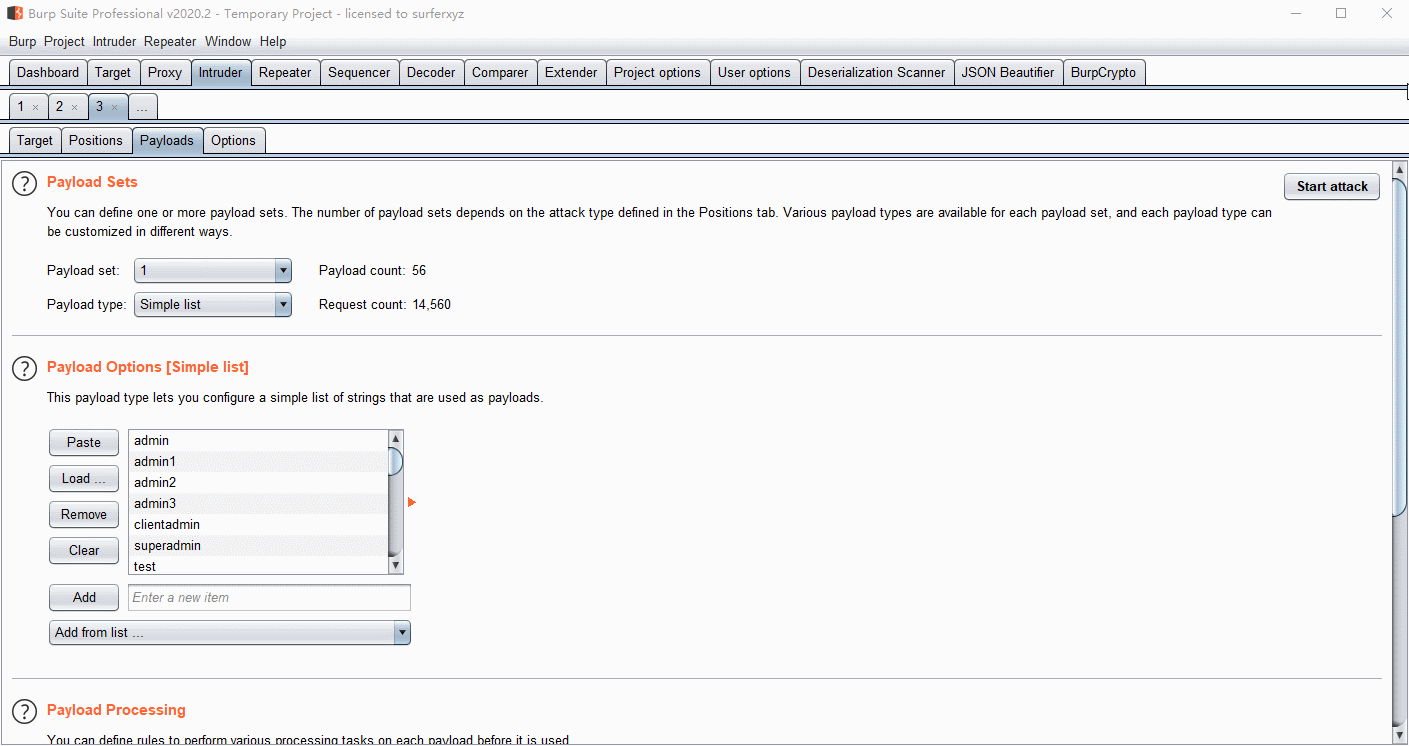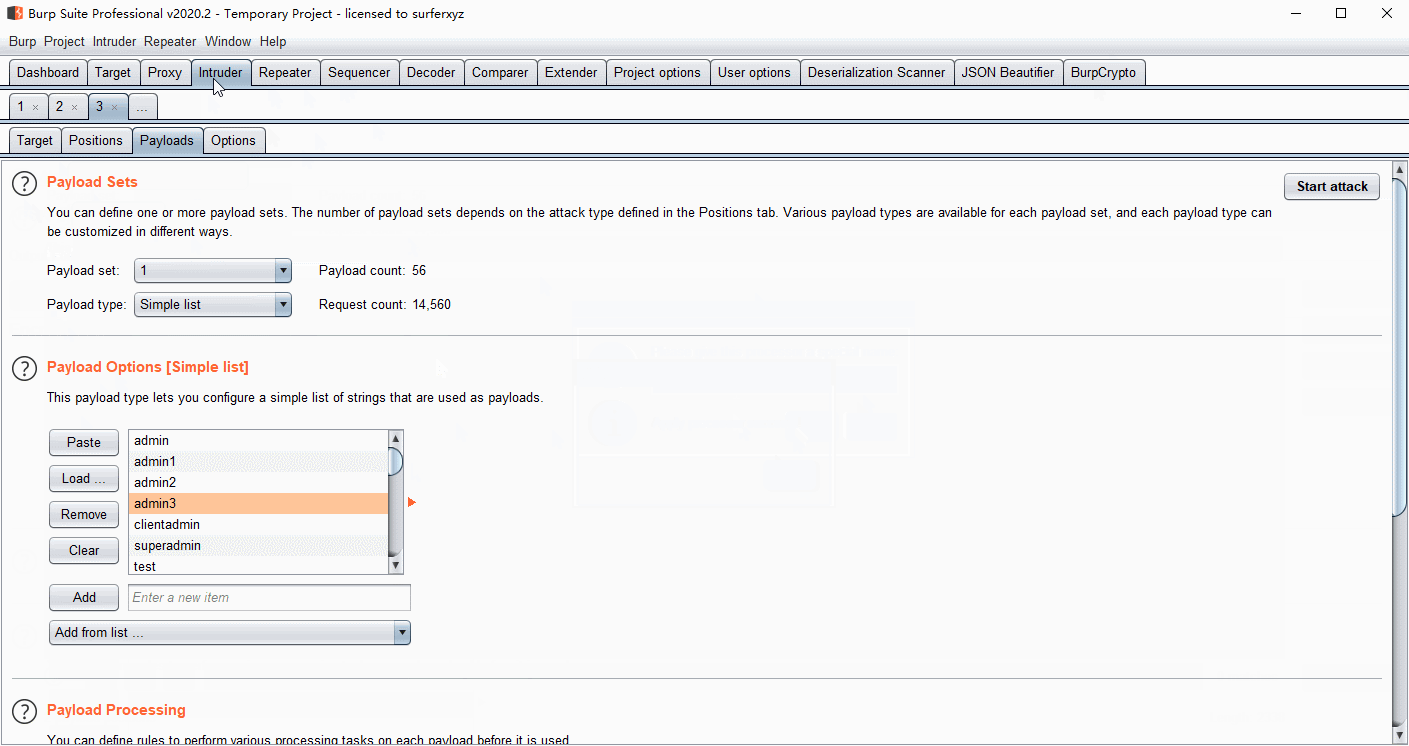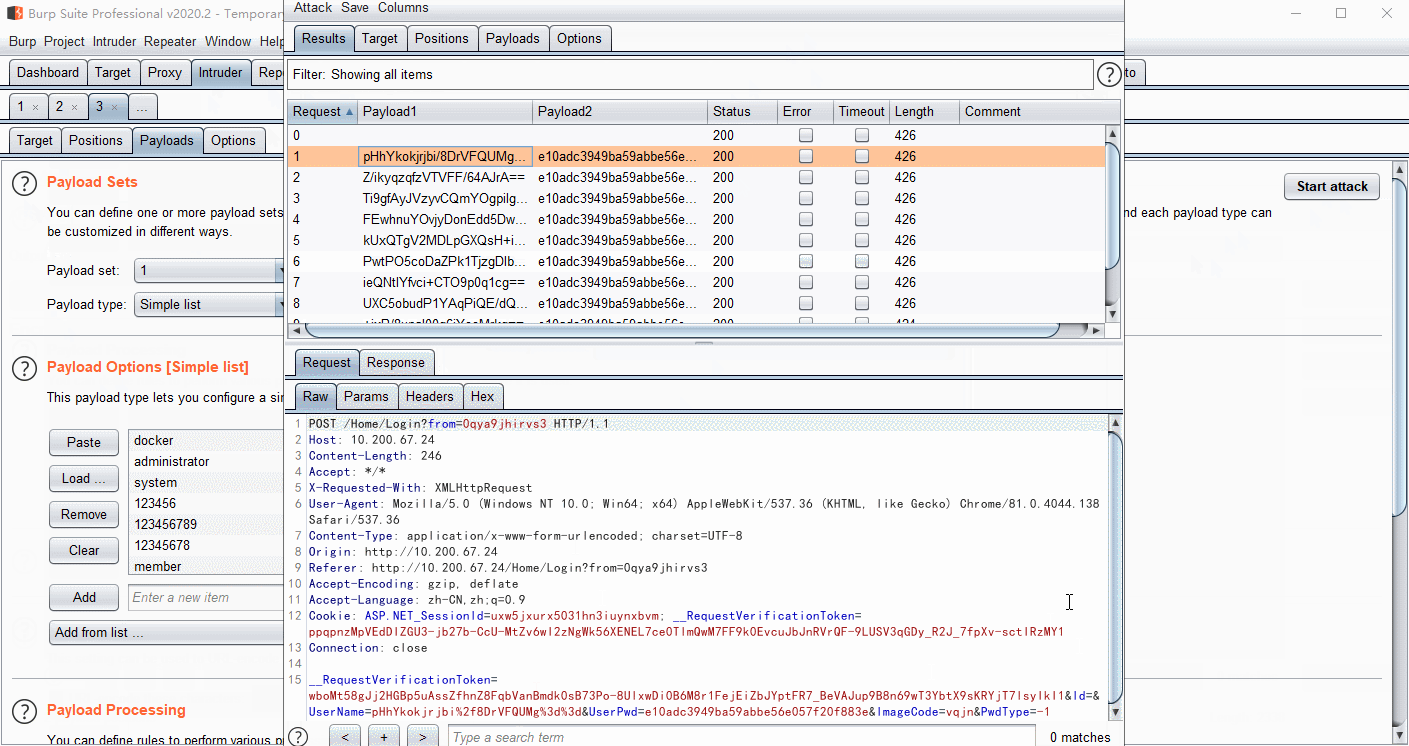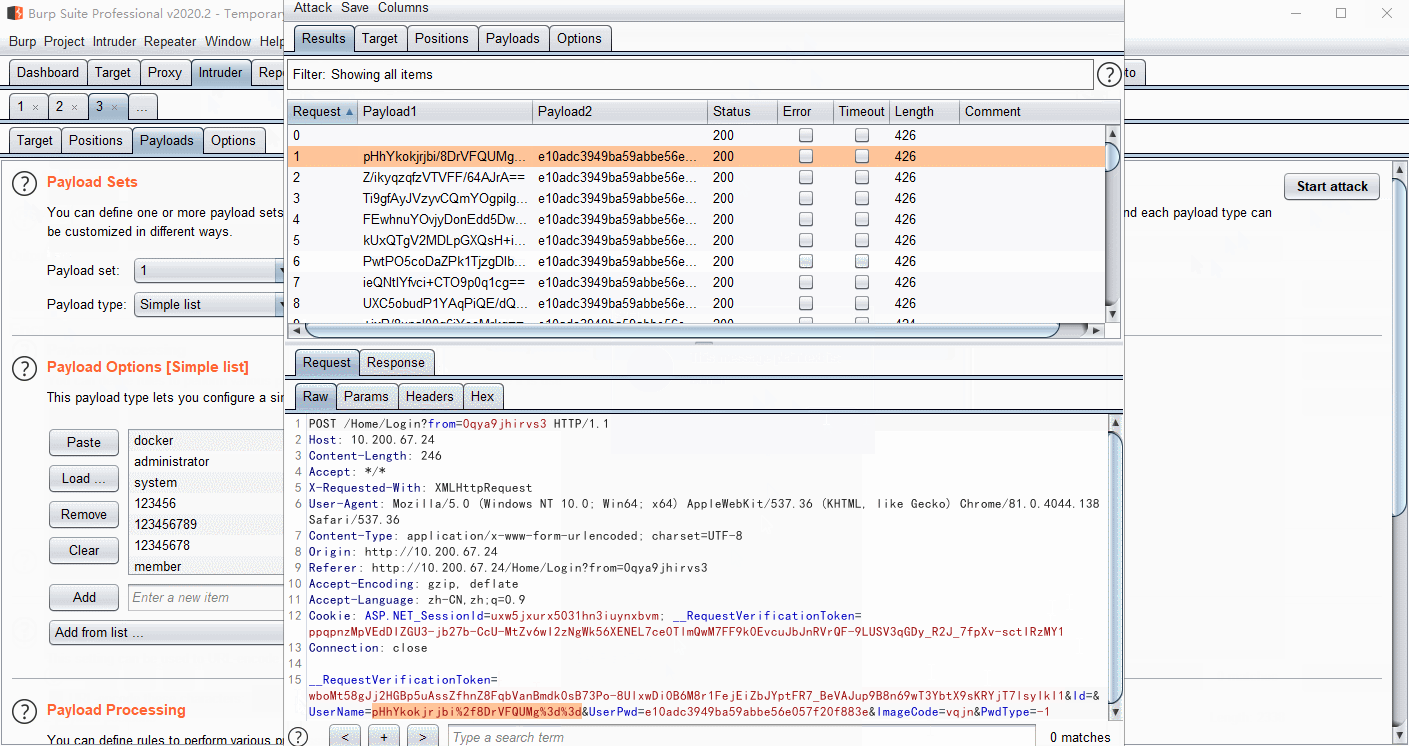 whwlsfb/burpcrypto
BurpSuite plugin for encrypting payloads with AES, RSA, DES, or custom JS code, enabling automated decryption of front-end encrypted traffic during…
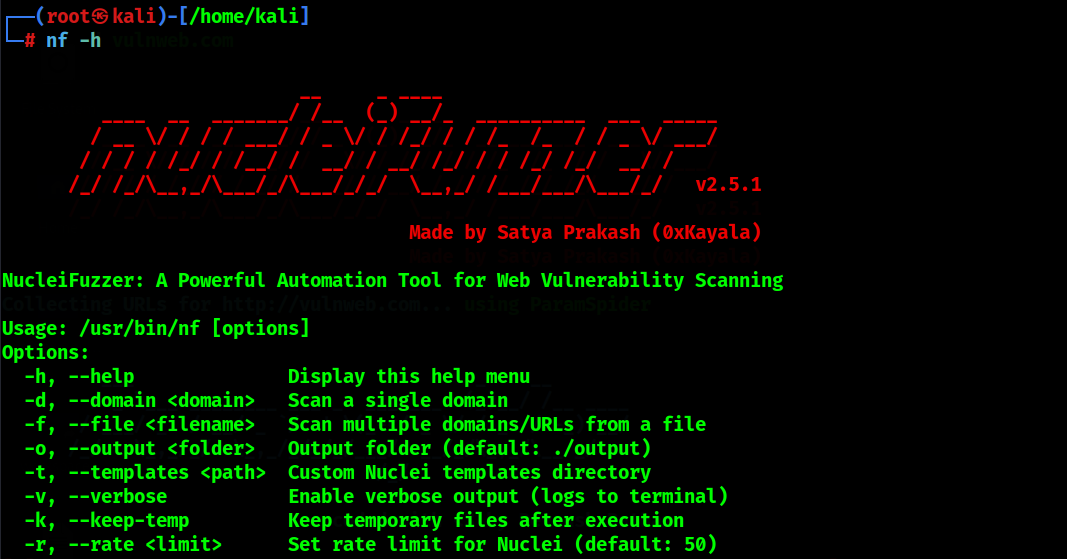 0xkayala/nucleifuzzer
Automated web vulnerability scanner combining URL discovery tools (ParamSpider, waybackurls, gauplus, hakrawler, katana) with Nuclei fuzzing…
 fcavallarin/htcap
htcap is a web application scanner able to crawl single page application (SPA) recursively by intercepting ajax calls and DOM changes.
 danmcinerney/xsscrapy
XSS spider - 66/66 wavsep XSS detected
 gbrindisi/xsssniper
An automatic XSS discovery tool
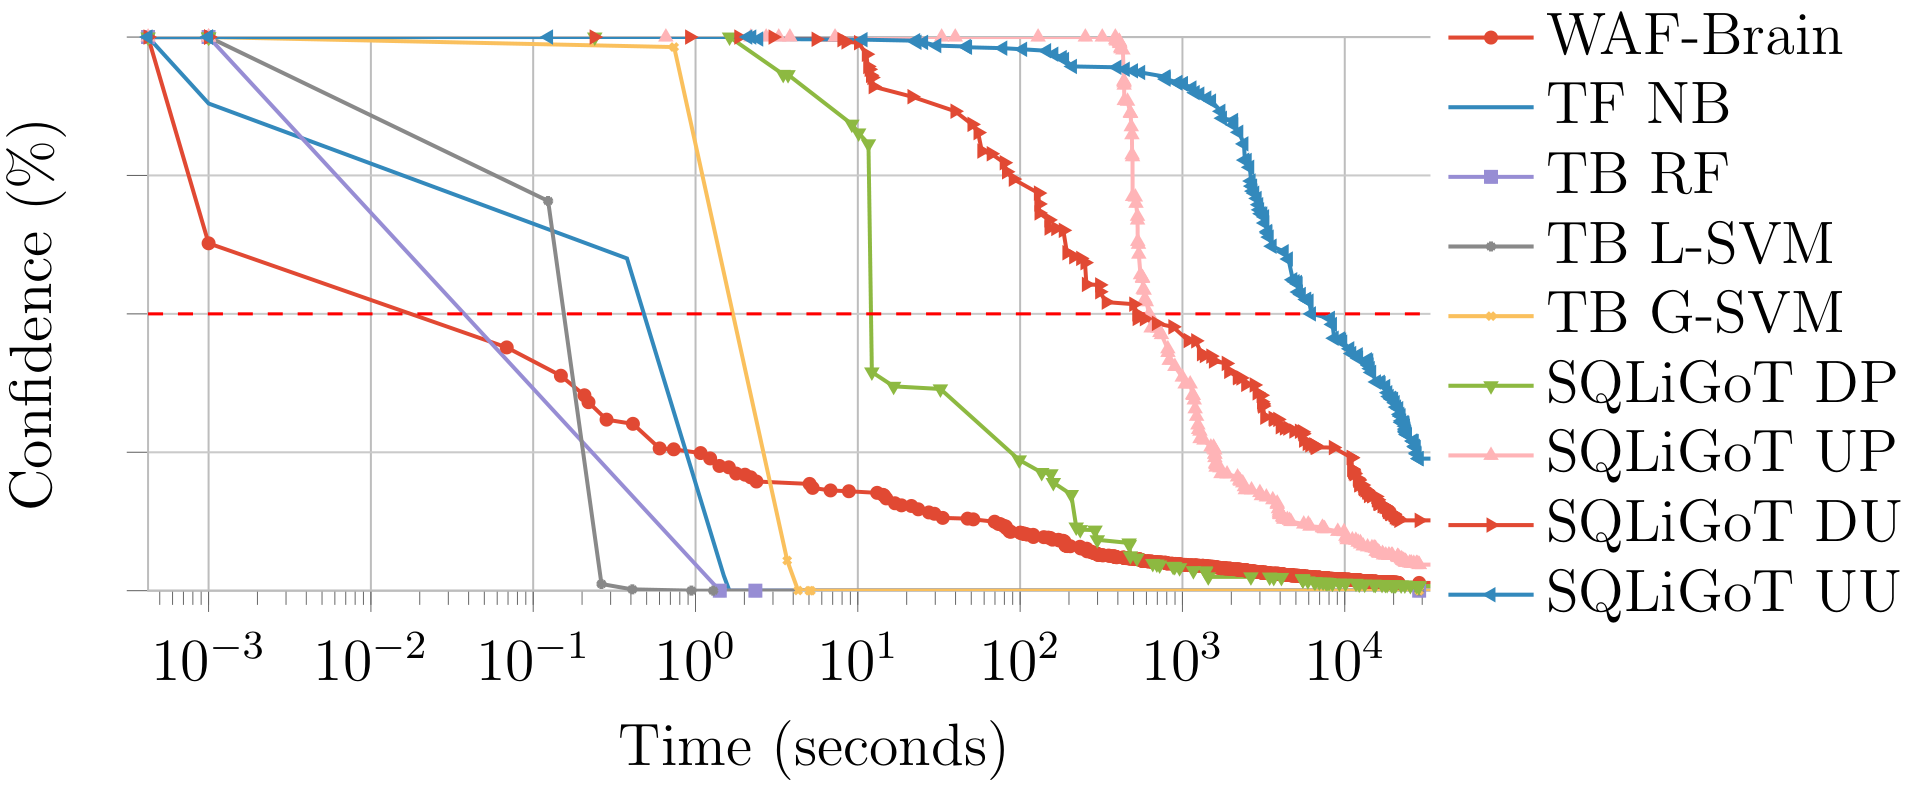 avalz/waf-a-mole
A guided mutation-based fuzzer for ML-based Web Application Firewalls
 chrislockard/api_wordlist
A wordlist of API names for web application assessments
 dzonerzy/gowapt
Go Web Application Penetration Test
 redsection/pfuzz
Modular WAF bypass fuzzer with multi-threading, request manipulation, and payload encoding for red team web application testing.
 net-hunter121/api-wordlist
Curated wordlists of API function names, verbs, and nouns for fuzzing web application endpoints with Burp Suite Intruder.
 gogo2464/cve-2024-5124
Exploit for CVE-2024-5124 targeting ChuanhuChatGPT via TLS timing side-channel attack. Uses tlsfuzzer to perform character-by-character credential…
 fuzzdb-project/fuzzdb
Dictionary of attack patterns and primitives for black-box application fault injection and resource discovery.
 hackmanit/tinja
TInjA is a CLI tool for testing web pages for template injection vulnerabilities and supports 44 of the most relevant template engines for eight…
 mvdevnull/ci_fuzz
Command Injection Web Fuzzer Script for mitmproxy
 ianxtianxt/cve-2019-5096-goahead-web-server-dos-exploit
Python exploit for CVE-2019-5096, a use-after-free vulnerability in GoAhead web server's upload handler, causing denial of service via double-free.
 angorafuzzer/angora
Coverage-guided fuzzer that uses taint tracking and scalar optimization to solve path constraints without symbolic execution, improving branch…
 michenriksen/jdam
A structure-aware JSON fuzzer