
like-dbg
 0xricksanchez/like-dbg
Fully dockerized Linux kernel debugging environment
binary-exploitationctfdebuggers+2
0xricksanchez/like-dbgFully dockerized Linux kernel debugging environment
 xairy/linux-kernel-exploitation
A collection of links related to Linux kernel security and exploitation
 chenaotian/cve-2023-0386
Local privilege escalation exploit for CVE-2023-0386 targeting Linux kernel overlayfs. Includes detailed vulnerability analysis, PoC code, and…
 bobfuzzer/cve-2019-18885
Proof-of-concept for a null pointer dereference in the Linux kernel BTRFS filesystem (CVE-2019-18885), including a crafted image, reproduction steps,…
 zpol/cve-2026-23398-poc
Reproducible lab for CVE-2026-23398, a Linux kernel NULL dereference in icmp_tag_validation() triggered by ICMP Fragmentation Needed packets, causing…
 sunblaze-ucb/exploitgym
ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.
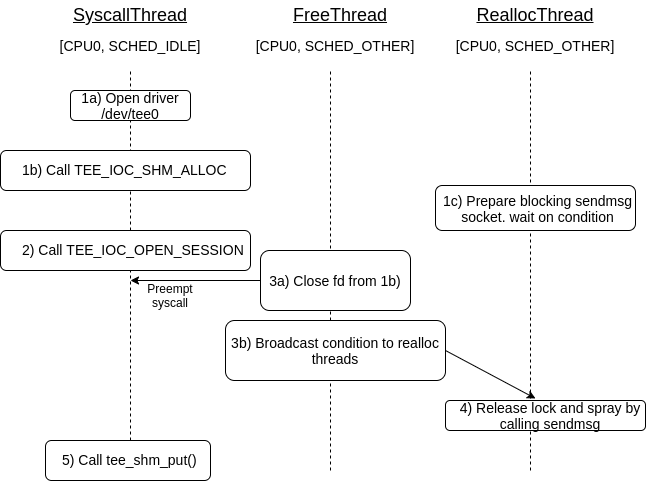 pjlantz/optee-qemu
Environment with vulnerable kernel for exploitation of the TEE driver (CVE-2021-44733)
 runtimeverification/kernel-c-to-rust-spike
Hardening kernel C parsers via Rust rewrite + differential fuzzing + formal verification. First target: UVC (CVE-2024-53104).
 erikdervishi03/cve-2026-31024
Proof of Concept (PoC) for a stack-based buffer overflow in Steghide 0.5.1. Demonstrates how long file paths trigger a crash (DoS) and leak sensitive…
 cao-wuhui/cve-2025-69720
Advisory for CVE-2025-69720: stack-based buffer overflow in GNU ncurses infocmp (CWE-121)
 ashemery/exploitation-course
Offensive Software Exploitation Course
 seanheelan/anamnesis-release
Evaluation framework for studying LLM agents that automatically generate working exploits from vulnerability reports, bypassing modern security…
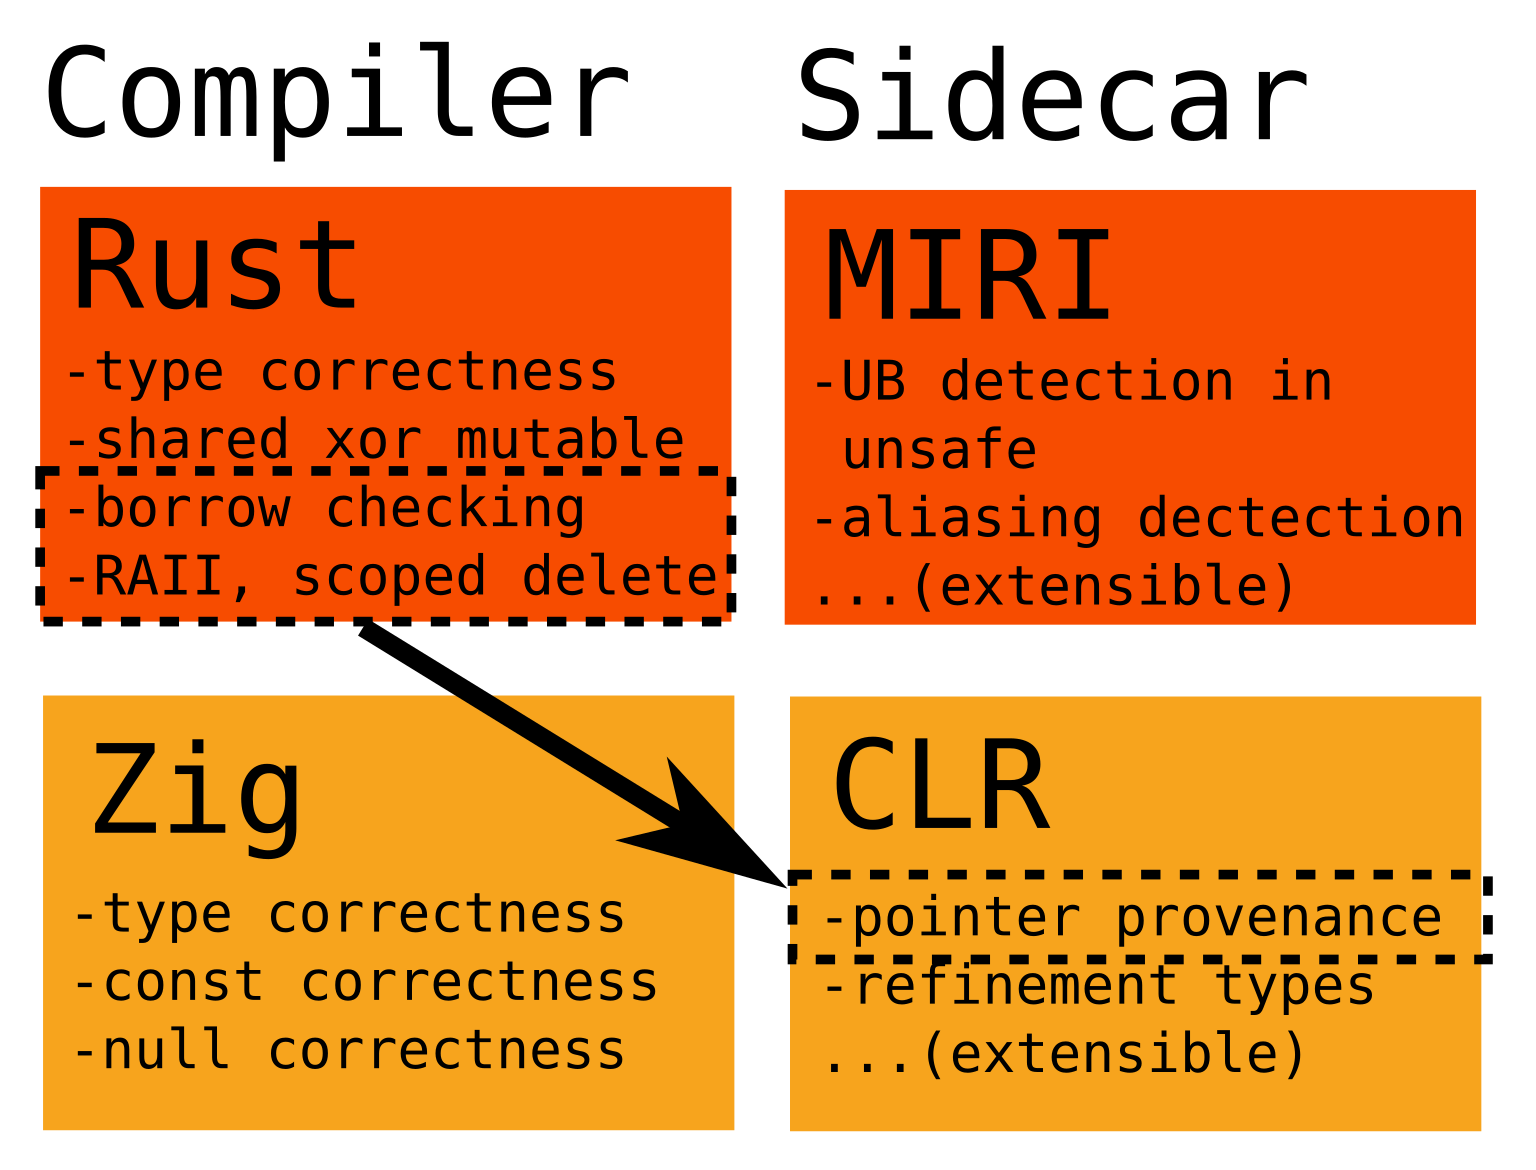 ityonemo/clr
Checker for Lifetimes and other Refinement types
 nevesnunes/z80-sans
OpenType font that disassembles Z80 instructions
 zx41r/awesome-reverse-engineering-and-malware-analysis
A verified map of reverse engineering and malware analysis. Disassemblers, unpacking, exploit dev, fuzzing, DFIR, and the deep-cut writeups other…
 zznop/sploit
Go package that aids in binary analysis and exploitation
 ggfuchsi-oss/spectrida-reverse_engineering_stack
Parallel IDA Pro binary analysis with AI-powered function naming, Neo4j knowledge graph, and phantomrt emulation/hooking/fuzzing engine for automated…
 knowledge-wisdom-understanding/recon
Enumerate a target Based off of Nmap Results