
CVE-2023-30226
 ifygecko/cve-2023-30226
Documentation of a denial-of-service vulnerability in the Rizin reverse engineering framework's ELF parser, caused by a forged DT_VERNEEDNUM value…
binary-analysisexploitationfuzzing+2
ifygecko/cve-2023-30226Documentation of a denial-of-service vulnerability in the Rizin reverse engineering framework's ELF parser, caused by a forged DT_VERNEEDNUM value…
 tarantula-team/cve-2019-19203
An issue was discovered in Oniguruma 6.x before 6.9.4_rc2. In the function gb18030_mbc_enc_len in file gb18030.c, a UChar pointer is dereferenced…
 skrkcb2/cve-2025-0851
Proof-of-concept exploit for CVE-2025-0851, a file traversal vulnerability in Deep Java Library's tar/zip model extraction utility, enabling…
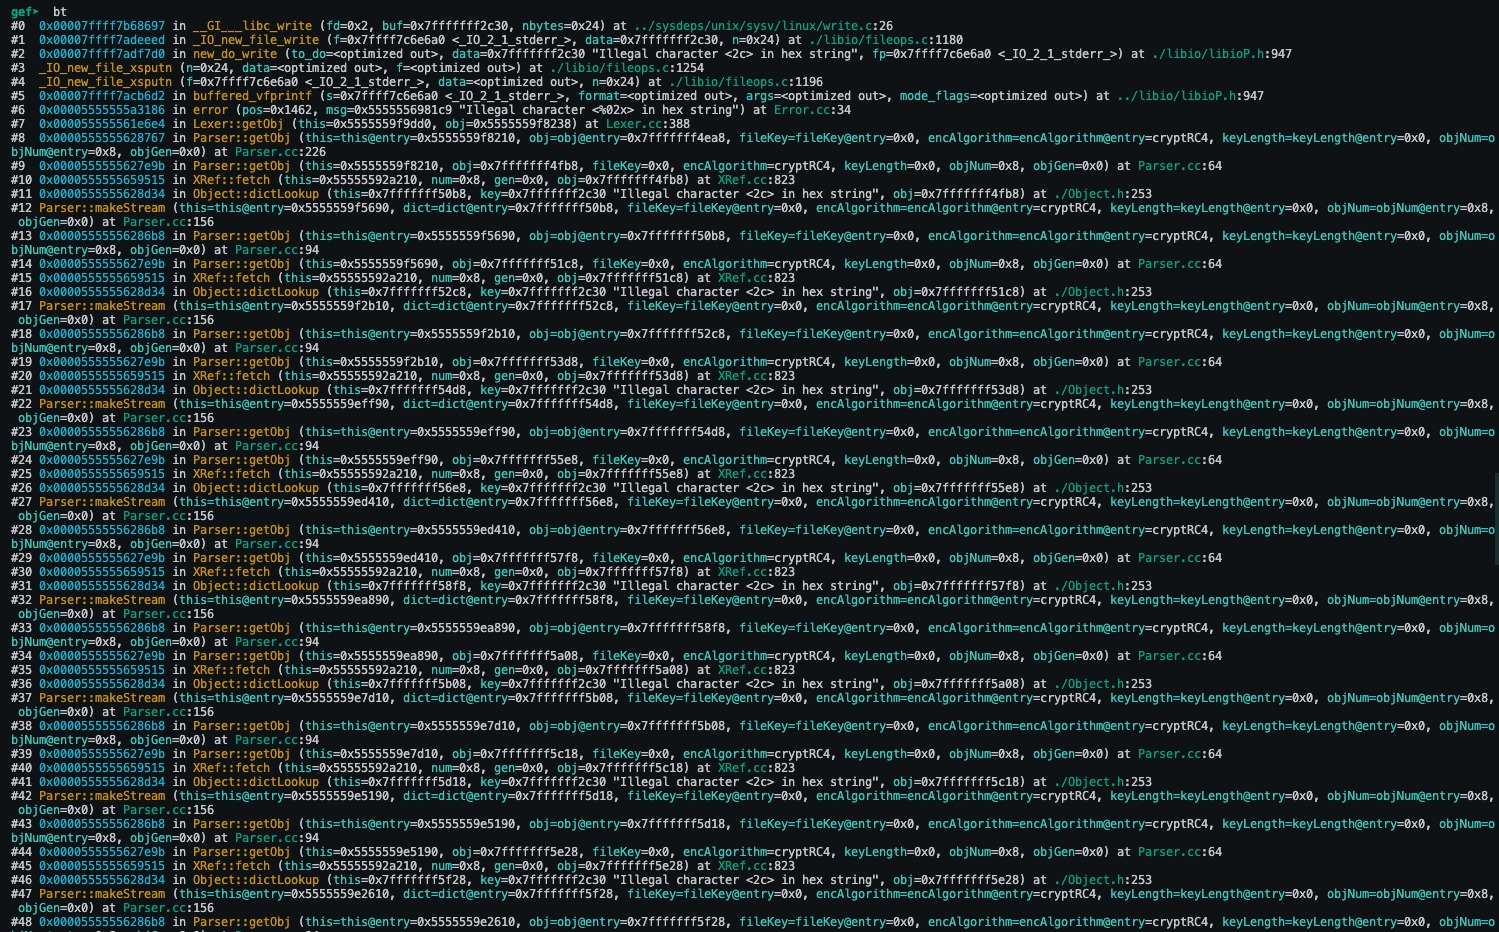 fineas/cve-2019-13288-poc
Proof-of-concept exploit for CVE-2019-13288, demonstrating infinite recursion denial-of-service in Xpdf 4.01.01 via a crafted PDF file.
 terribledactyl/cve-2025-55891
Proof-of-concept for CVE-2025-55891: heap corruption in TIFFCP.EXE via malformed TIFF file, triggering segmentation fault during LZW decompression in…
 kha-beleh/poc-cve-2025-69421
Minimal CVE-2025-69421 reproducer demonstrating a NULL pointer dereference in OpenSSL PKCS#12 processing via a malformed PFX file with absent…
 devrodt2/cve-2026-28609-matroska-pcm-oob
Proof-of-concept and instrumented reproduction harness for CVE-2026-28609, an out-of-bounds write in Android's MatroskaExtractor reachable via a…
 olafdaf/cve-2022-40363
A buffer overflow in the component nfc_device_load_mifare_ul_data of Flipper Devices Inc., Flipper Zero before v0.65.2 allows attackers to cause a…

 ioactive/melkor_elf_fuzzer
Melkor is a very intuitive and easy-to-use ELF file format fuzzer to find functional and security bugs in ELF parsers.
 amossys/memitm
Tool to make in memory man in the middle
 bshyuunn/bandiview-7.05-vuln-poc
bandiview (7.05) vuln PoC | CVE-2024-45870, CVE-2024-45871, CVE-2024-45872
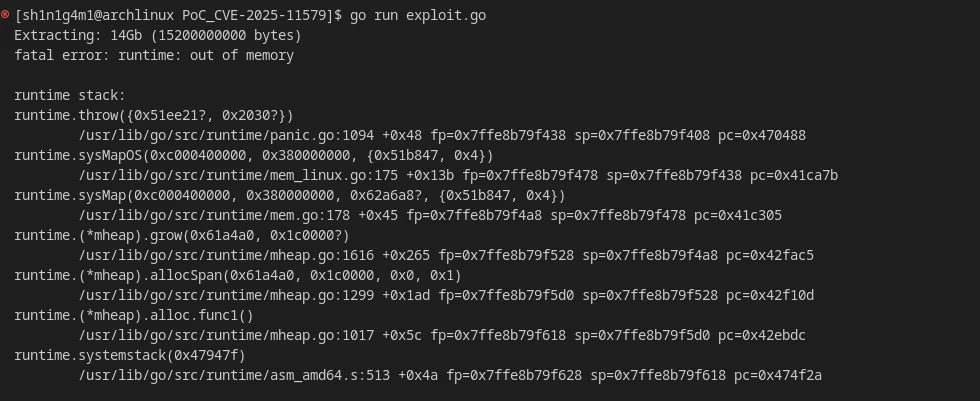 shinigami-777/poc_cve-2025-11579
Proof-of-concept exploit for CVE-2025-11579, a denial-of-service vulnerability in rardecode that triggers an out-of-memory crash via a crafted RAR…
 r3n3r0/cve-2026-27280
In-depth analysis and proof-of-concept for CVE-2026-27280, an out-of-bounds write in Adobe DNG SDK's dng_render_task::ProcessArea, reachable via…
 kevinbackhouse/djvulibre-poc-cve-2025-53367
Proof-of-concept exploit for CVE-2025-53367, a vulnerability in the DjVuLibre library. Demonstrates exploitation of a memory corruption bug in DjVu…
 driverunload/cve-2024-25423
Cinema 4D out-of-bounds write vulnerability when parsing c4d files
 jfrog/jfrog-cve-2023-43786-libx11_dos
Proof-of-concept for CVE-2023-43786, a libX11 integer overflow causing infinite loop DoS. Demonstrates triggering the vulnerability via sxpm with a…
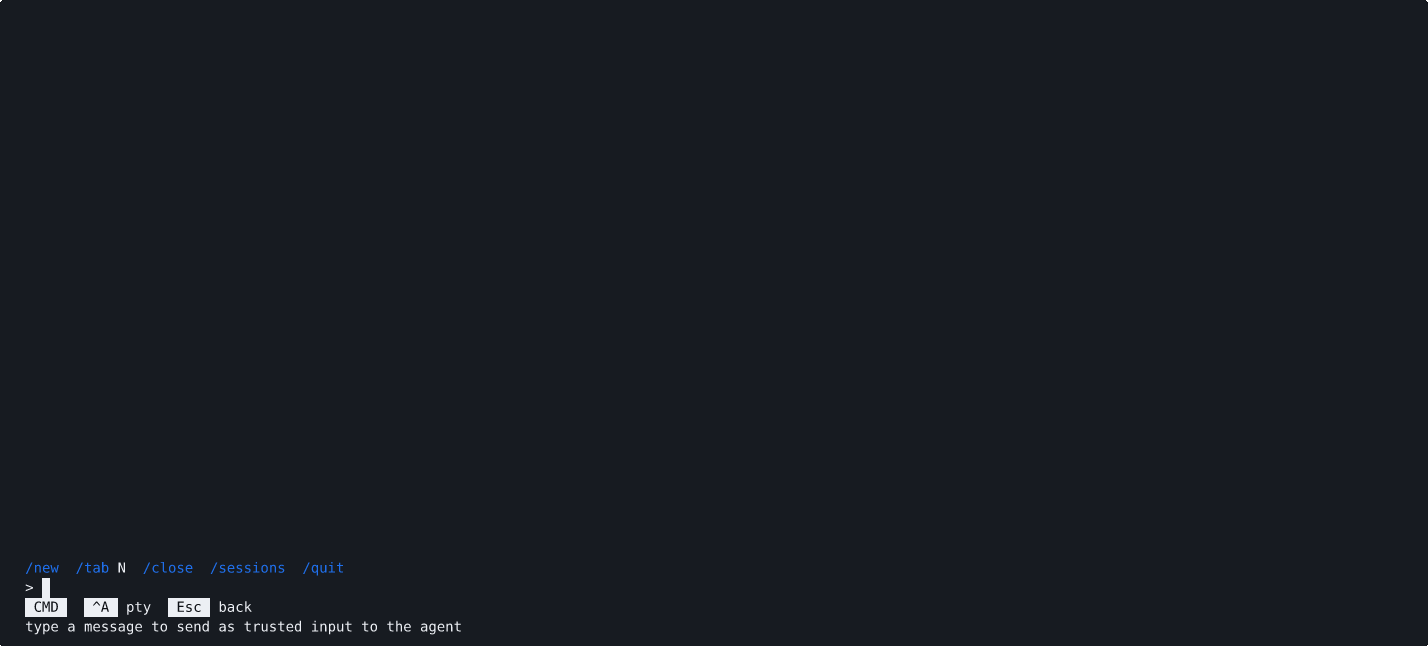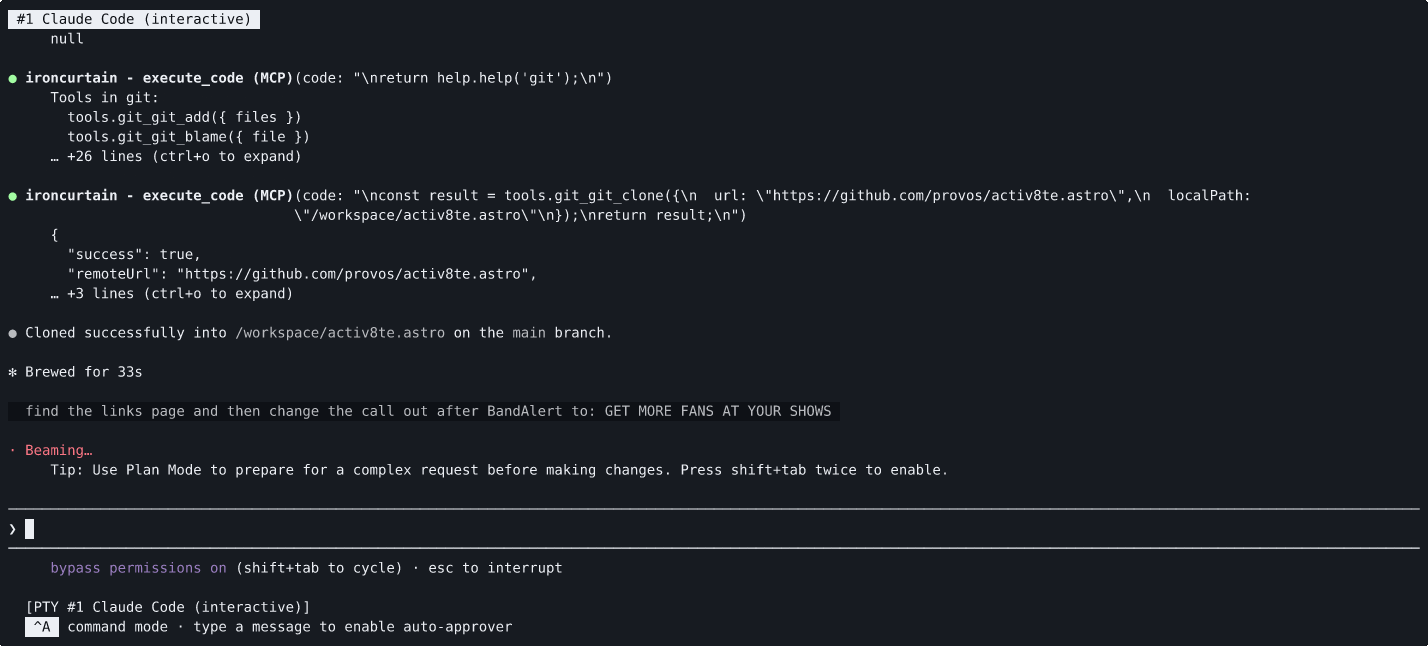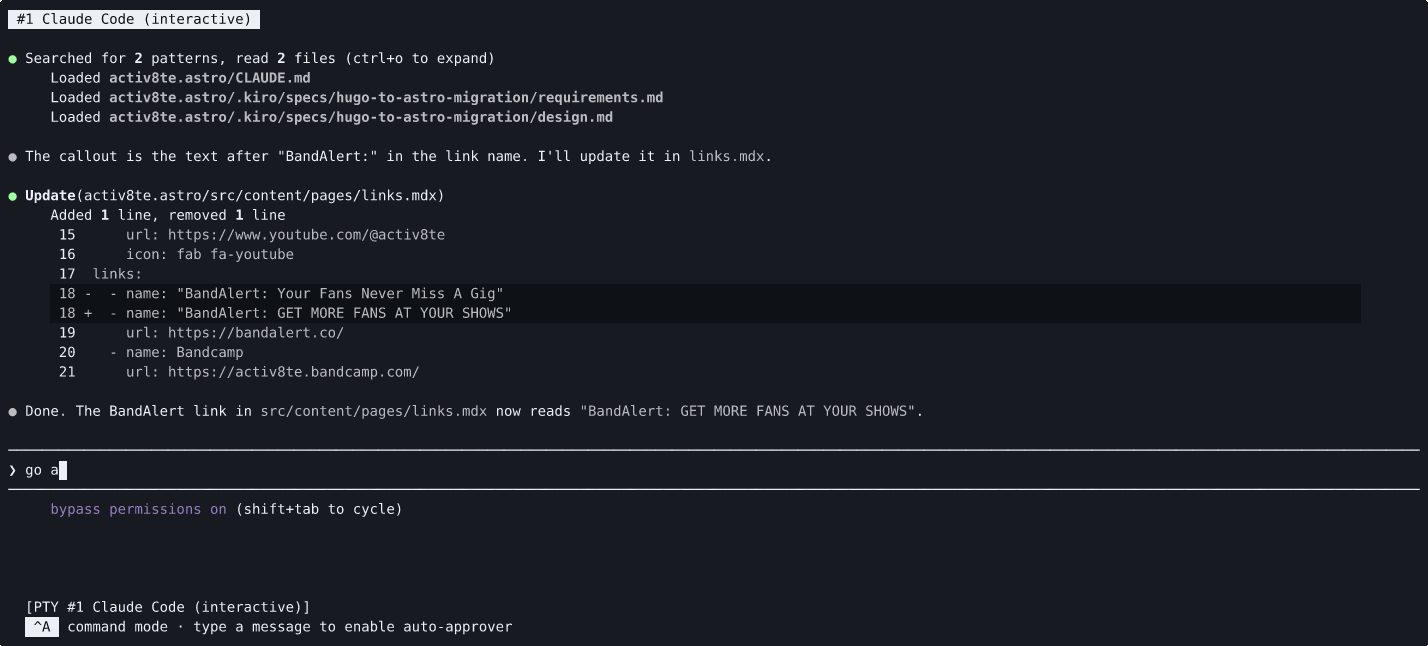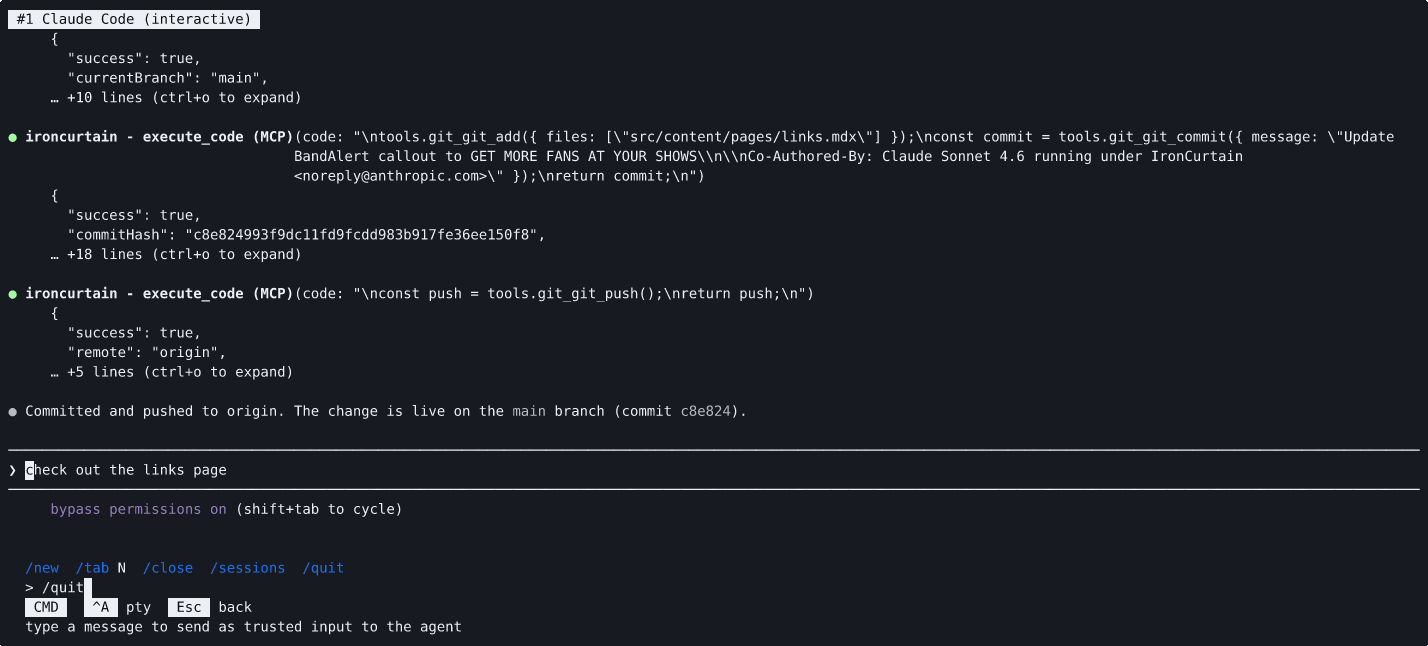 provos/ironcurtain
A secure* runtime for autonomous AI agents. Policy from plain-English constitutions. (*https://ironcurtain.dev)