

BurpAPISecuritySuite
 teycir/burpapisecuritysuite
Burp Suite extension for API security testing with 15 attack types, 108+ payloads, intelligent fuzzing, BOLA/IDOR detection, AI integration, and…
api-securityapi-security-testingfuzzing+4
340
teycir/burpapisecuritysuiteBurp Suite extension for API security testing with 15 attack types, 108+ payloads, intelligent fuzzing, BOLA/IDOR detection, AI integration, and…
 meliht/mr.sip
SIP Security Assessment Framework for VoIP Pentesters. Presented at DEFCON, BlackHat & Offzone.

 esentire/cve-2015-7547-public
PoC attack server for CVE-2015-7547 buffer overflow vulnerability in glibc DNS stub resolver (public version)
 harsh-bothra/bheem
Scope-based reconnaissance automation framework that orchestrates multiple open-source tools for subdomain enumeration, vulnerability scanning, and…
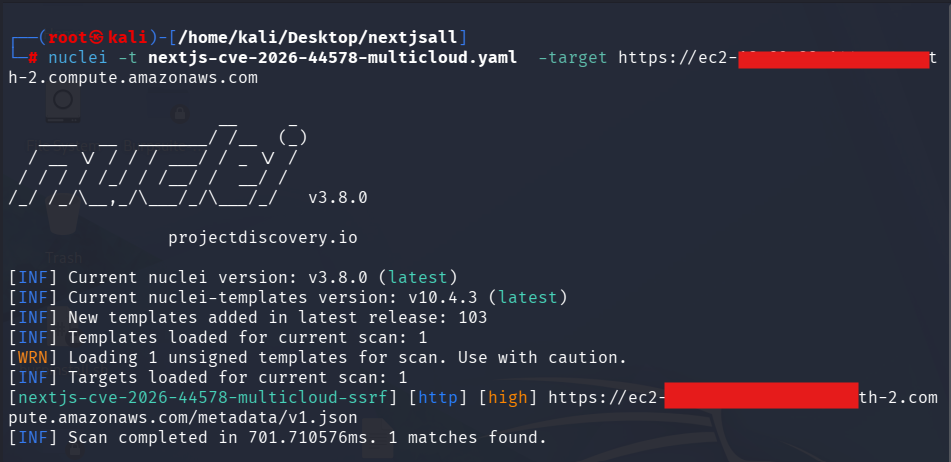 love07oj/nextjs-cve-2026-44578
Nuclei templates for detecting CVE-2026-44578 (Next.js WebSocket Upgrade SSRF) with multi-cloud metadata validation, Next.js fingerprinting, and…
 abrewer251/cve-2024-38475_sonicboom_apache_url_traversal_poc
Proof-of-concept scanner for CVE-2024-38475 (SonicBoom) Apache URL traversal. Automates TLS negotiation, directory scanning, traversal verification,…
 0xsobky/hackvault
A container repository for my public web hacks!
 syaifulandy/cve-2024-38475
CVE-2024-38475 Scanner using FFUF + Seclists
 praetorian-inc/augustus
LLM security testing framework for detecting prompt injection, jailbreaks, and adversarial attacks — 190+ probes, 28 providers, single Go binary
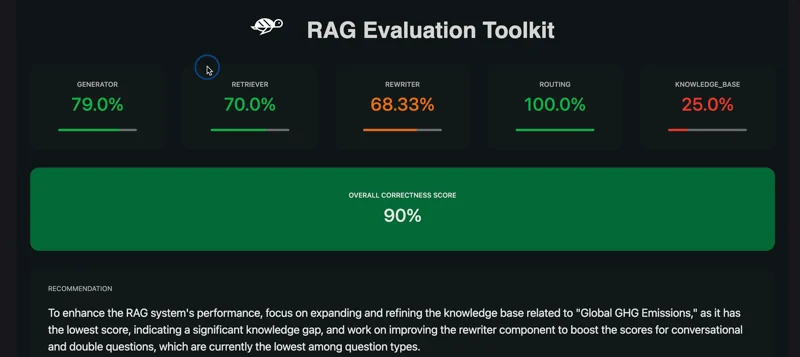 giskard-ai/giskard-oss
🐢 Open-Source Evaluation & Testing library for LLM Agents
 imperva/automatic-api-attack-tool
Imperva's customizable API attack tool takes an API specification as an input, generates and runs attacks that are based on it as an output.
 cifertech/esp32-div
ESP32DIV is a multi-purpose wireless offensive and defensive toolkit powered by an ESP32
 1n3/intruderpayloads
A collection of Burpsuite Intruder payloads, BurpBounty payloads, fuzz lists, malicious file uploads and web pentesting methodologies and checklists.
 ghosttroops/scan4all
Official repository vuls Scan: 15000+PoCs; 23 kinds of application password crack; 7000+Web fingerprints; 146 protocols and 90000+ rules Port…
 darkflippers/unleashed-firmware
Custom firmware for Flipper Zero enabling Sub-GHz radio, NFC/RFID emulation, infrared, and BadUSB attack features for hardware security testing.