bettercap
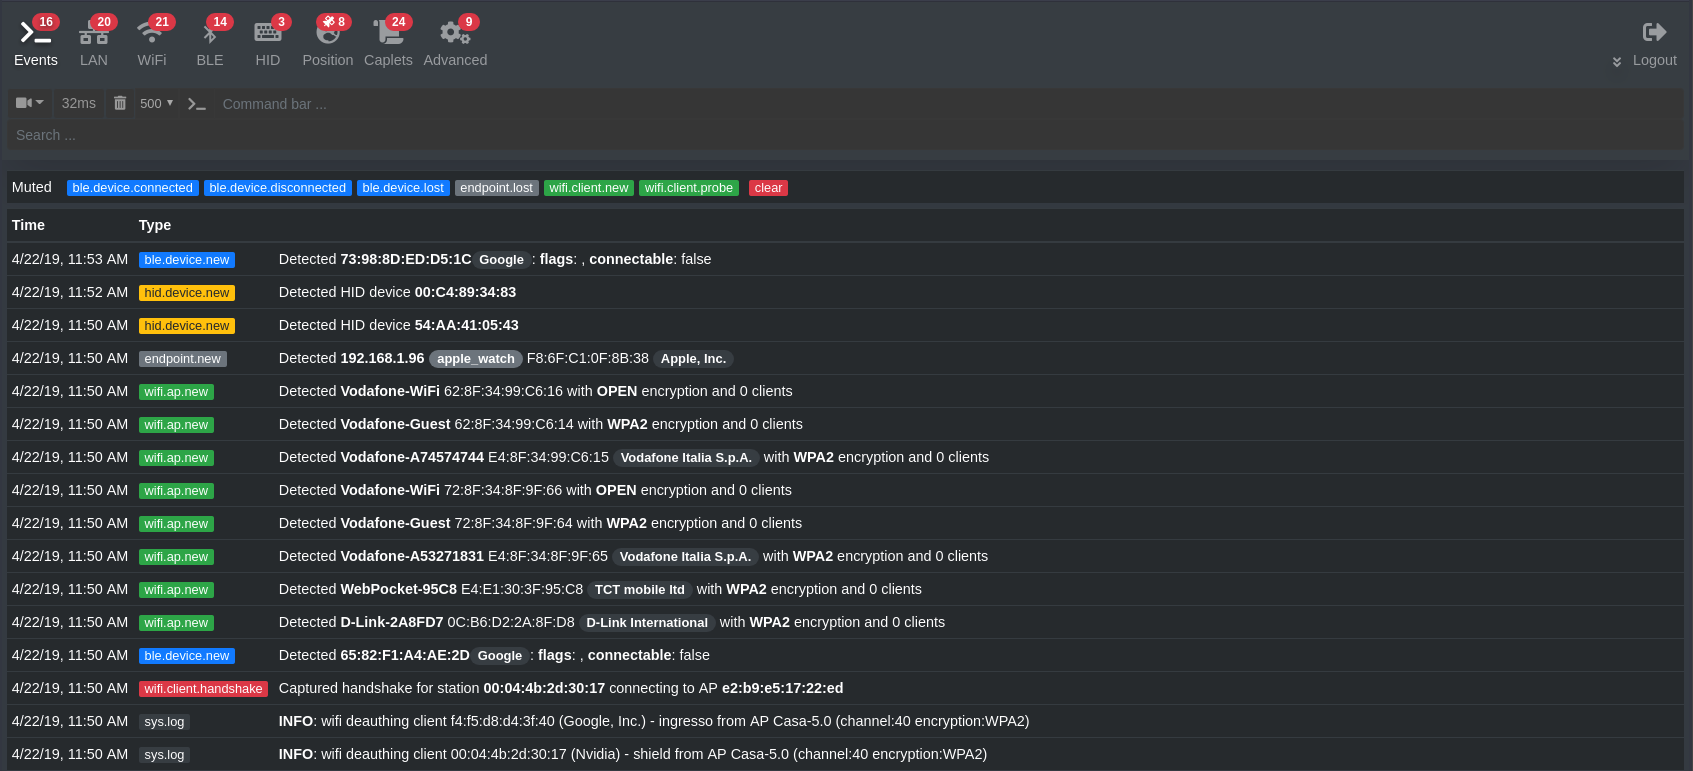
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
bluetooth-securitydata-exfiltrationfingerprint-spoofing+16
20.1k
bettercap/bettercapThe Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 angr/angr
A powerful and user-friendly binary analysis platform!
 google/oss-fuzz-gen
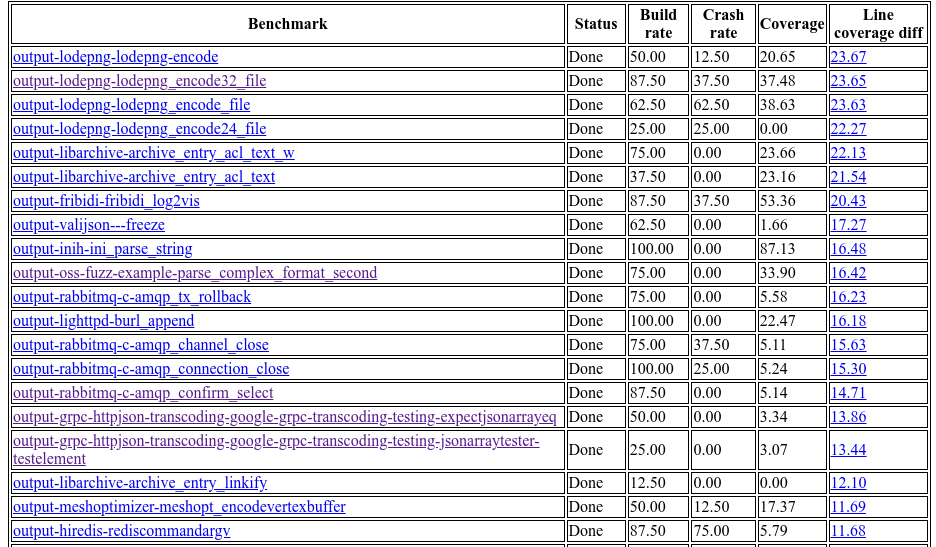
LLM powered fuzzing via OSS-Fuzz.
 danielbohannon/invoke-dosfuscation
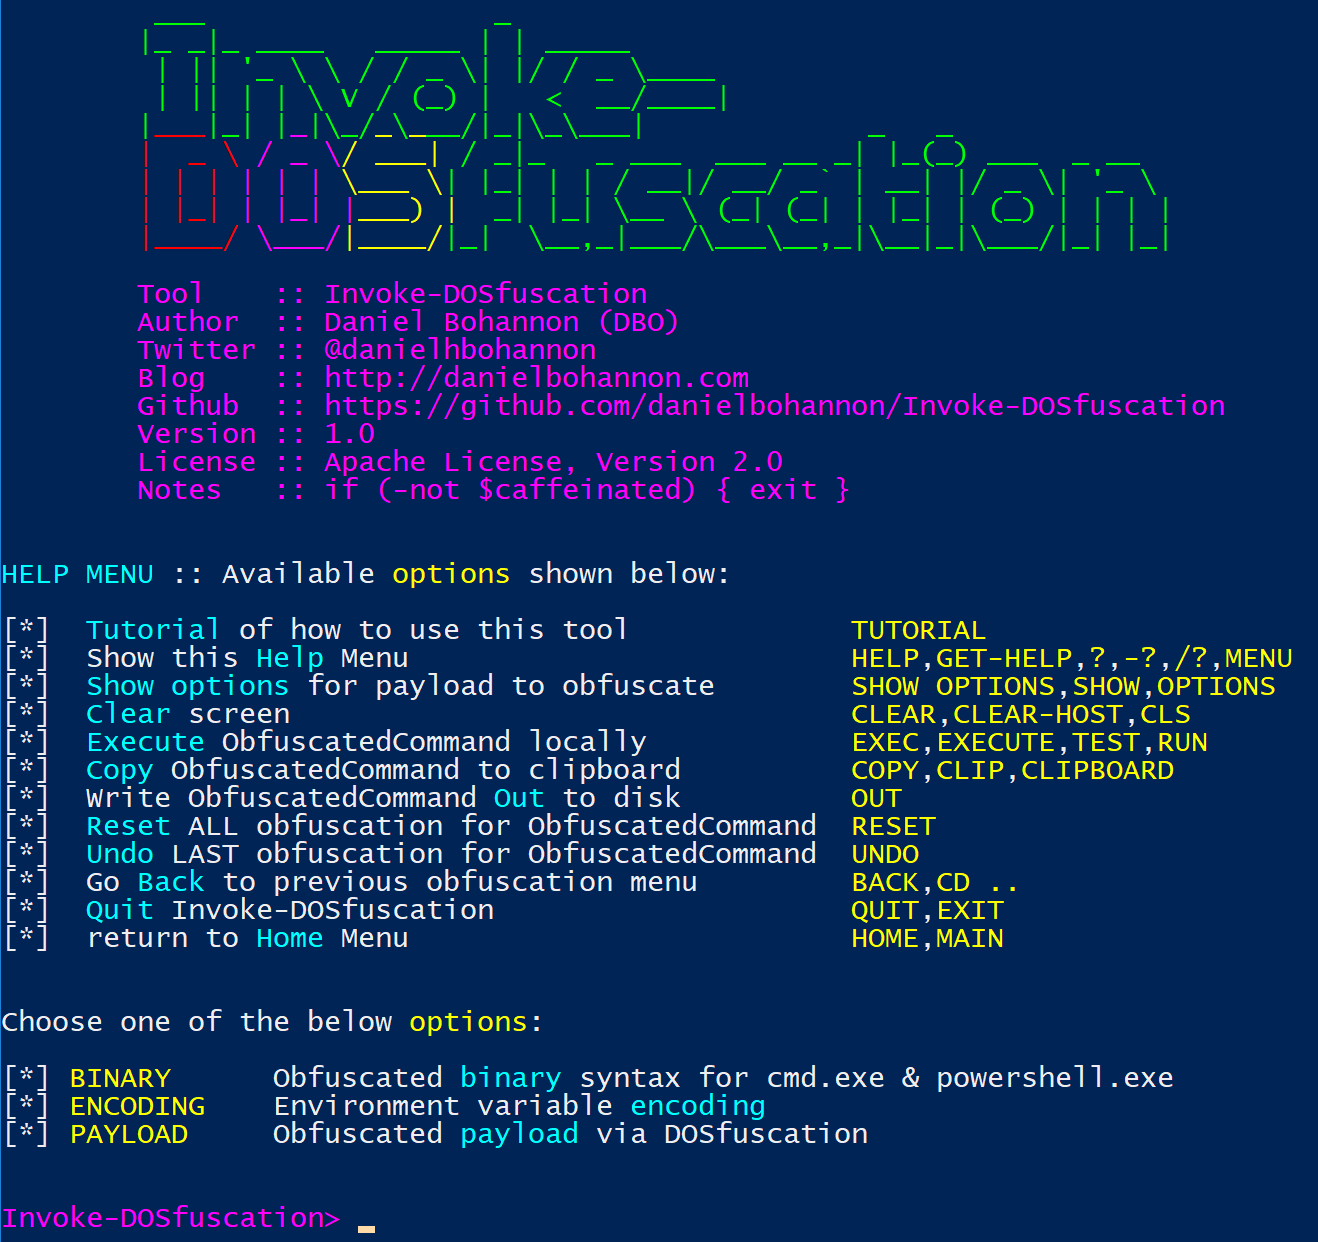
Cmd.exe Command Obfuscation Generator & Detection Test Harness
 riverloopsec/killerbee
IEEE 802.15.4/ZigBee Security Research Toolkit
 cisco-talos/mutiny-fuzzer
Network protocol fuzzer that replays PCAP traffic through a mutational engine (Radamsa) to quickly discover vulnerabilities in target hosts via…
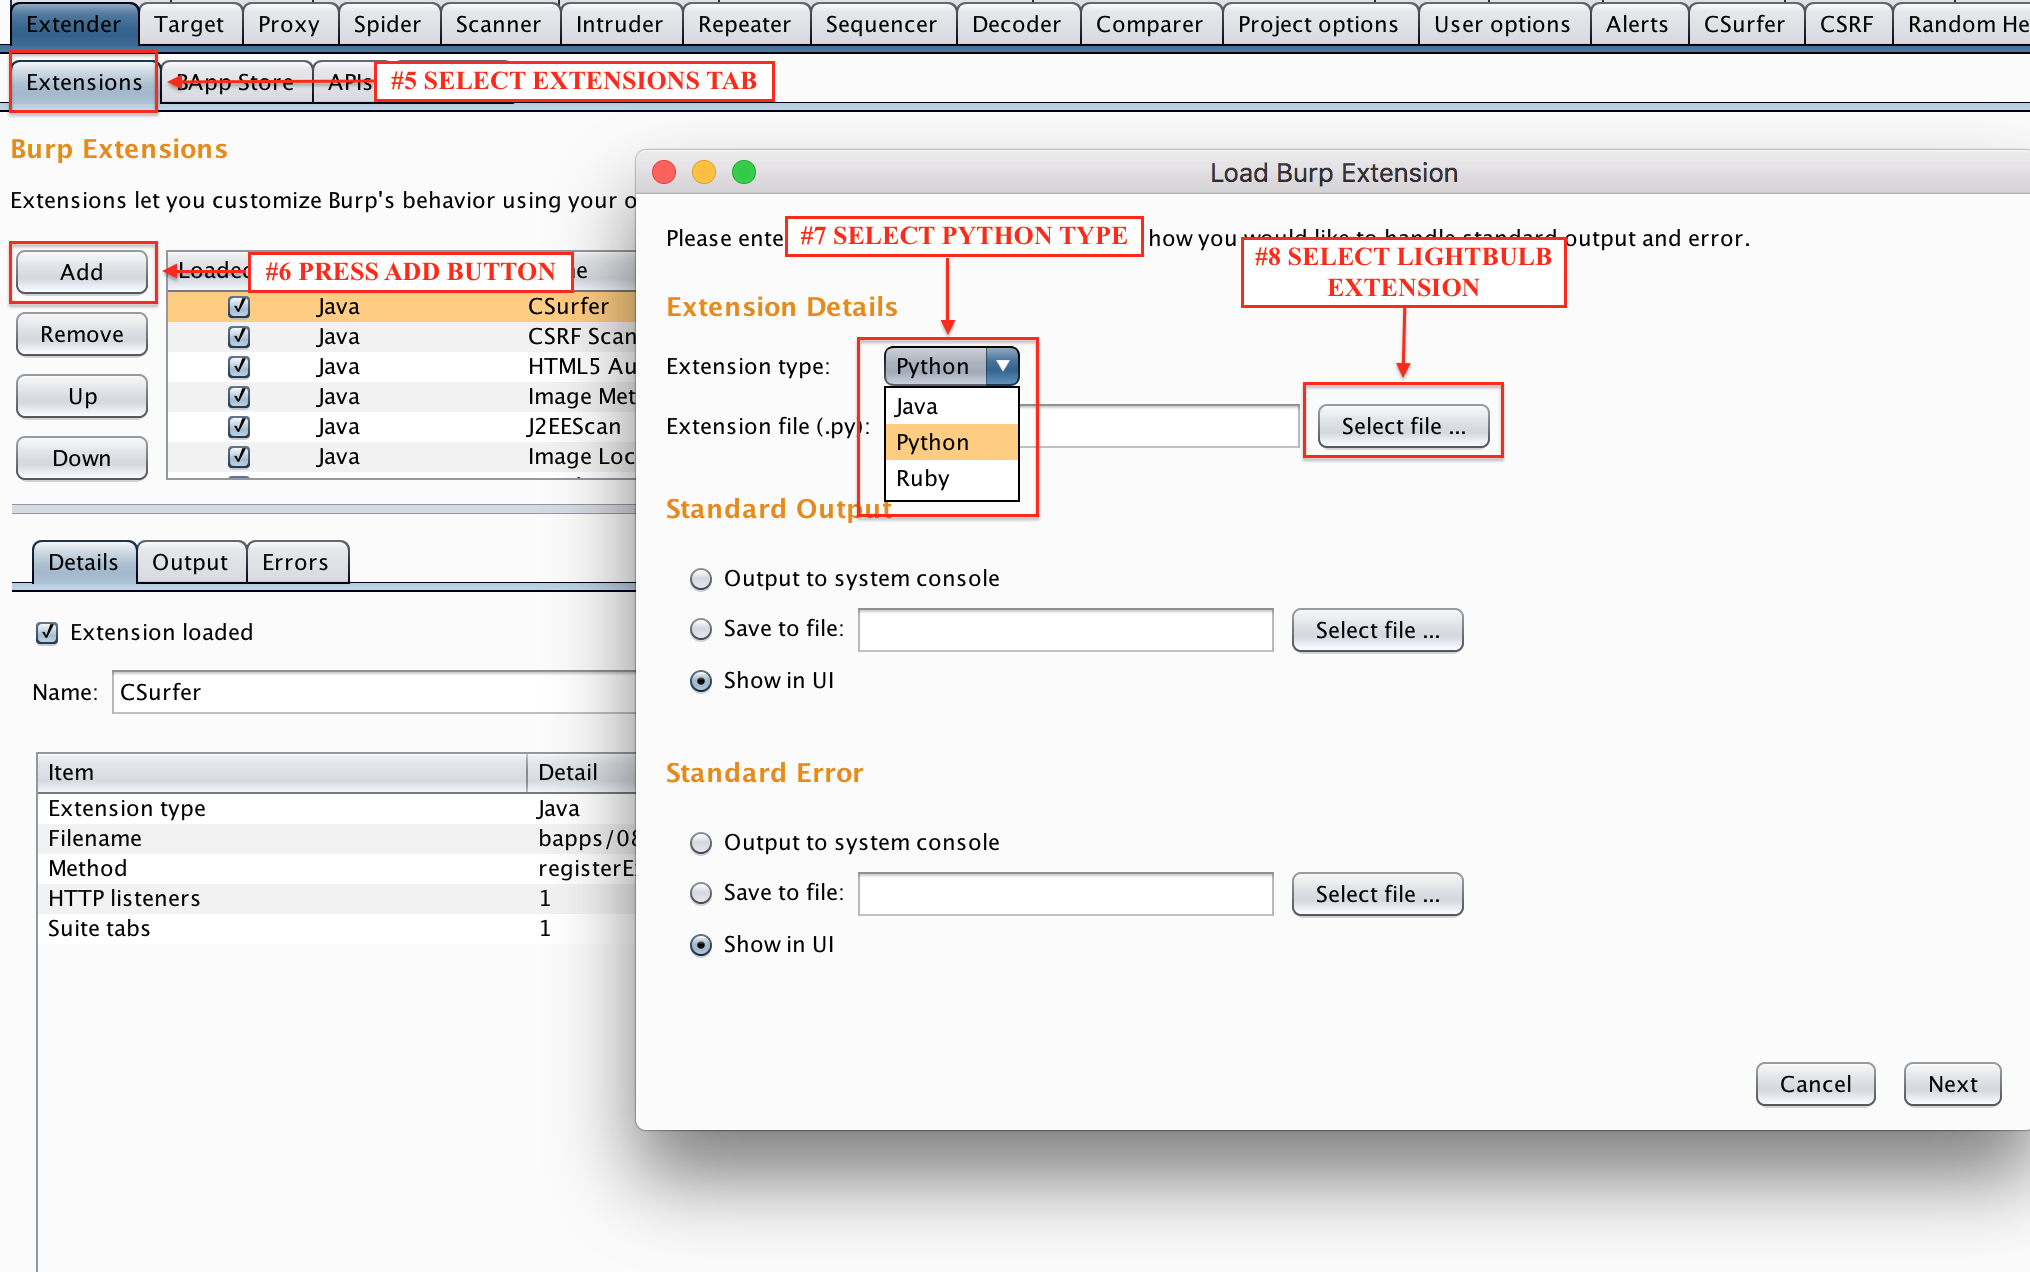 lightbulb-framework/lightbulb-framework
Tools for auditing WAFS
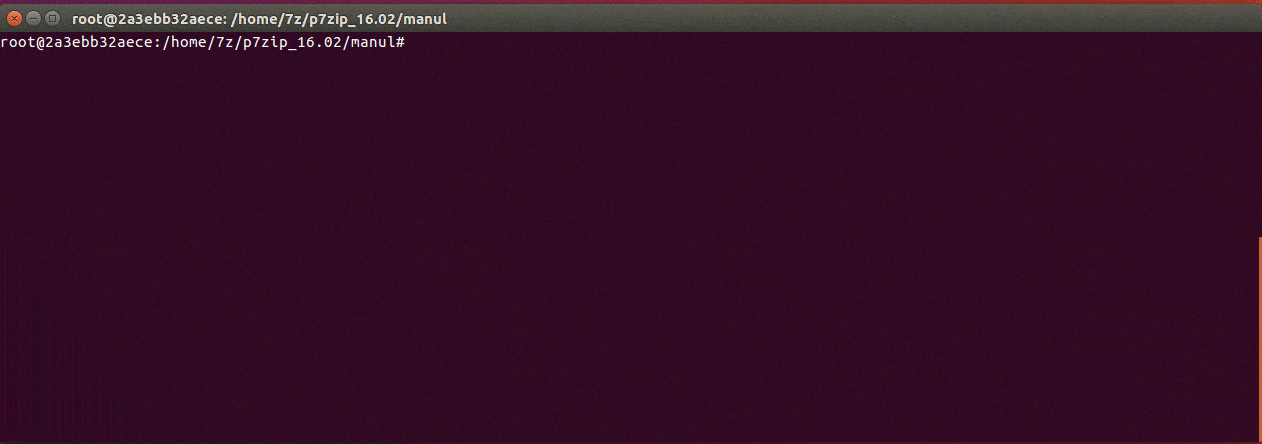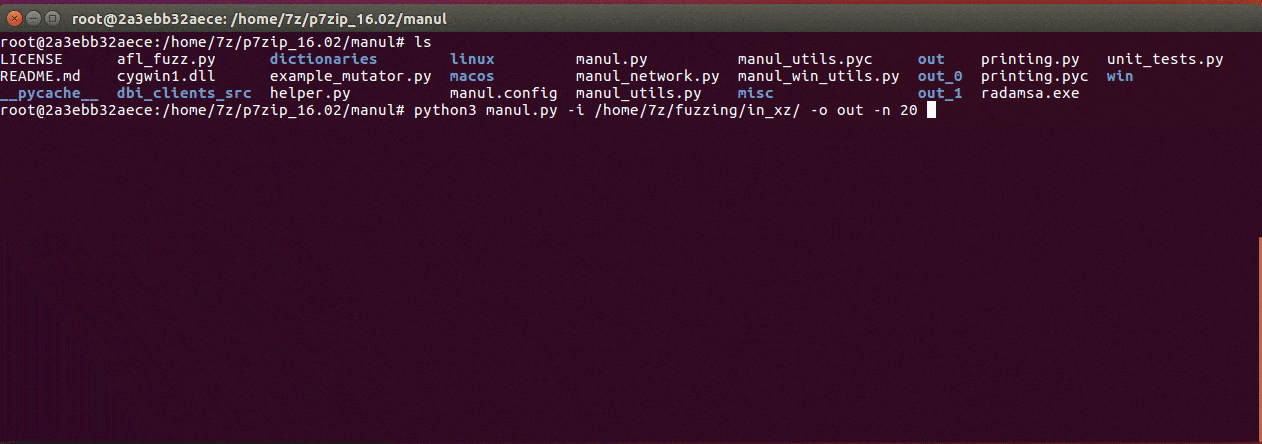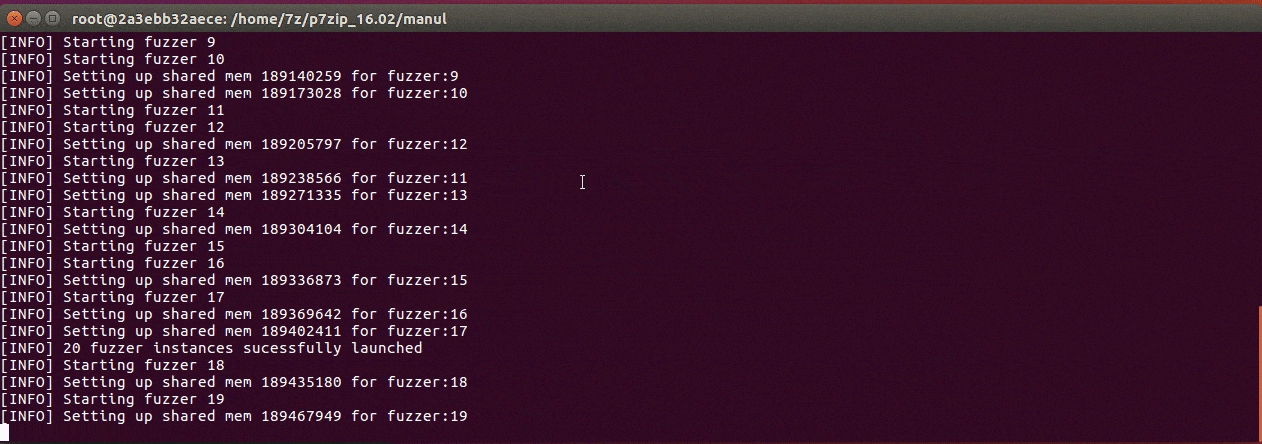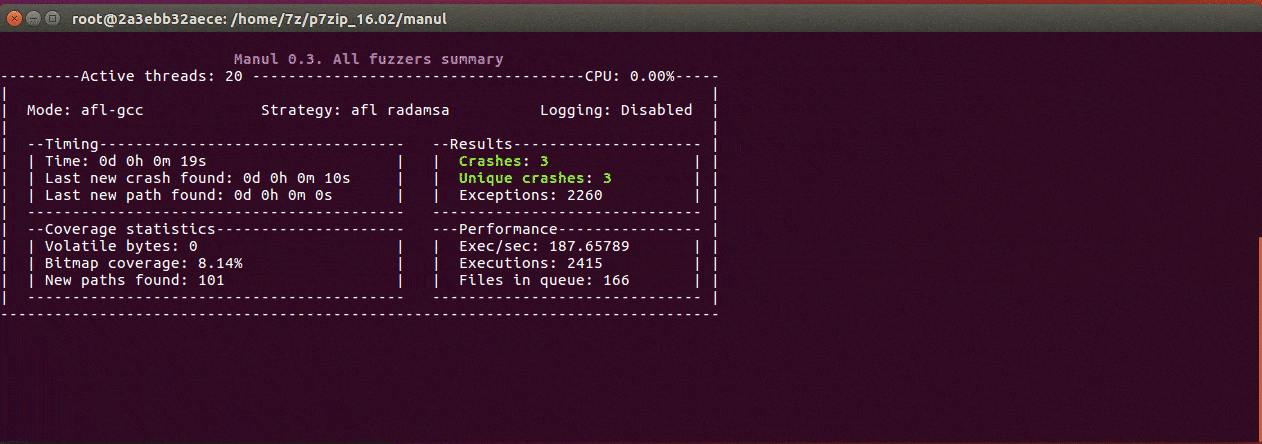 mxmssh/manul
Manul is a coverage-guided parallel fuzzer for open-source and blackbox binaries on Windows, Linux and MacOS
 hunters-sec/cve-2025-43300
This is POC for IOS 0click CVE-2025-43300
 thisistfs/rogue-framework
Desktop workbench for AFL++ fuzzing, cross-architecture QEMU emulation, harness development, Ghidra headless analysis, custom mutators, and patch…
 xpcmdshell/cve-2022-26711
Integer overflow in Apple ImageIO WebP parsing (macOS/iOS)
 puppetm4ster/koyane-framework
Modular wordlist generation, editing, analysis, and discovery toolkit for password cracking, fuzzing, and ethical security testing. Supports…
 dark-life944/cve-2025
This is POC for IOS 0click CVE-2025-43300
 ifygecko/cve-2023-30226
Documentation of a denial-of-service vulnerability in the Rizin reverse engineering framework's ELF parser, caused by a forged DT_VERNEEDNUM value…
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
 pedrib/poc
Advisories, proof of concept files and exploits that have been made public by @pedrib.