
ffufw
 puzzlepeaches/ffufw
Automates web content discovery and directory bruteforcing with multithreaded ffuf execution, tech-aware wordlists, endpoint filtering, WAF…
fuzzinginformation-gatheringpenetration-testing+2
146
puzzlepeaches/ffufwAutomates web content discovery and directory bruteforcing with multithreaded ffuf execution, tech-aware wordlists, endpoint filtering, WAF…
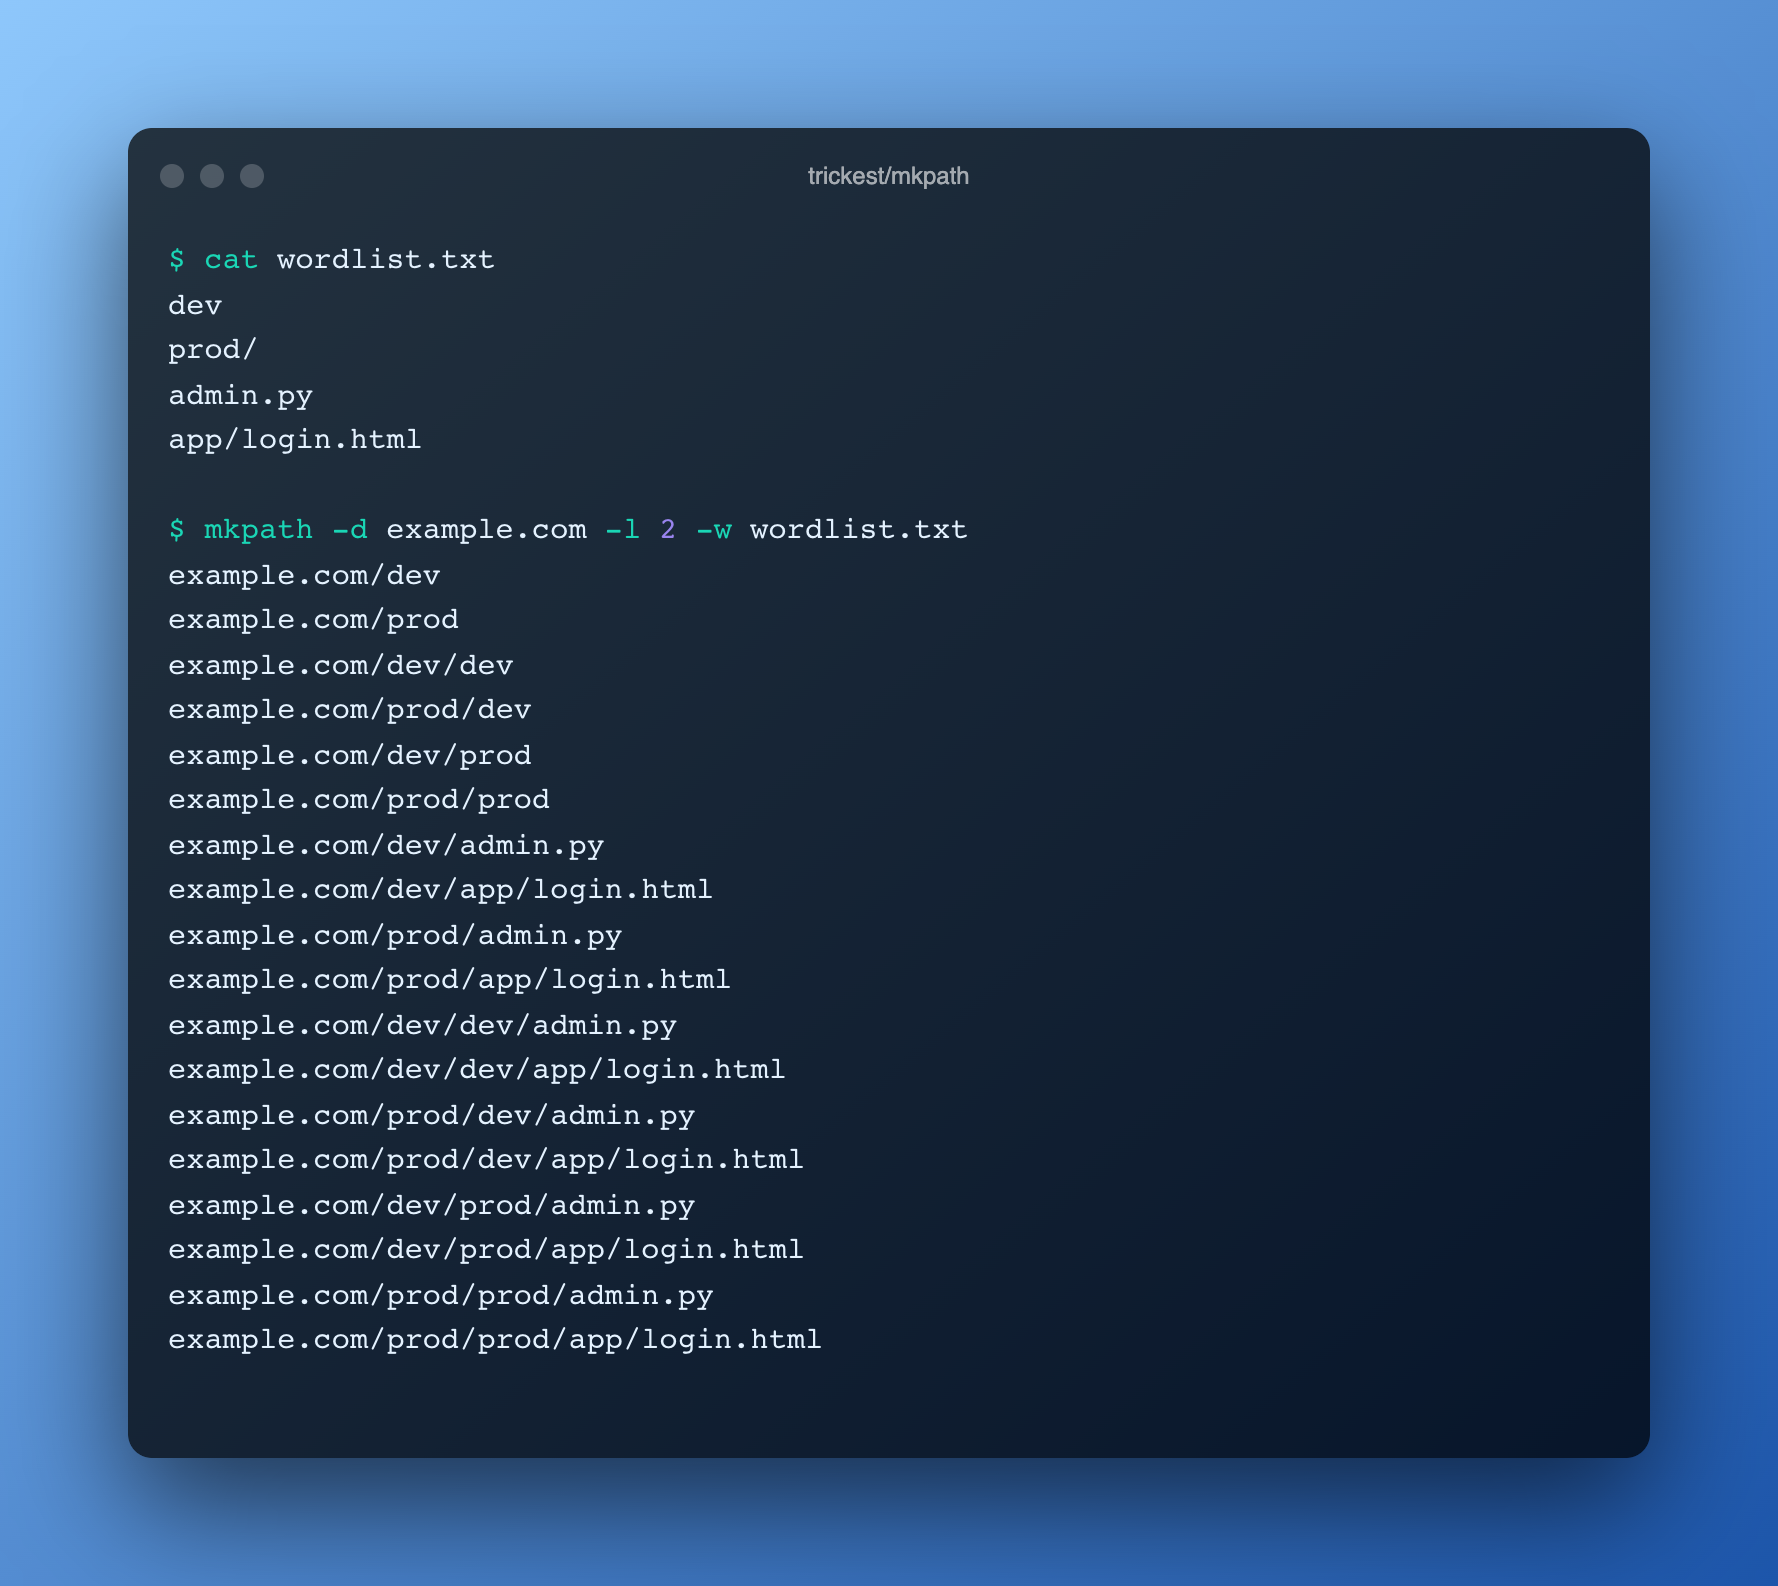 trickest/mkpath
Make URL path combinations using a wordlist
 nccgroup/memscan
Searches for strings, regex, credit card numbers of magnetic stripe card tracks in a Windows process's memory space
 ethicalhackingplayground/wordlistgen
Generates target specific word lists for Fuzzing with fuff
 yslxotwod/imsisting
GTK4 and CLI cellular security toolkit with 57 modules for 2G GSM, 3G UMTS, 4G LTE and 5G NR air interface, core network, SIM identity, RF tracking,…
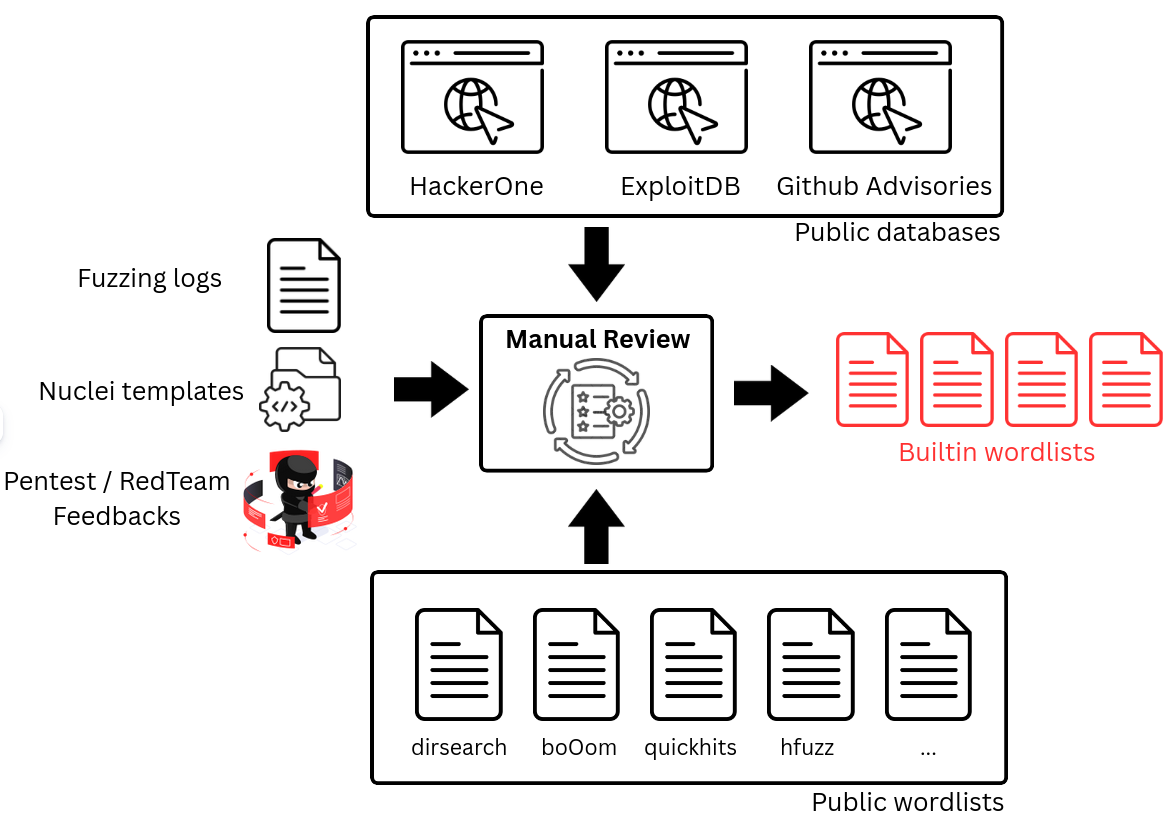 synacktiv/dicozorus
A tool to generate and maintain wordlists for Web fuzzing.
 orange-cyberdefense/bof
BOF (Boiboite Opener Framework) is a testing framework for industrial protocols implementations and devices.
 ffmancera/pentesting-multitool
Different utility scripts for pentesting and hacking.
 internon/inter-recon
Script to perform automatic initial web and vulnerability recon
 n0kovo/danish_phone_wordlist_generator
Generate wordlists of Danish phone numbers by area and/or usage (Mobile, landline etc.) Useful for password cracking or fuzzing Danish targets.
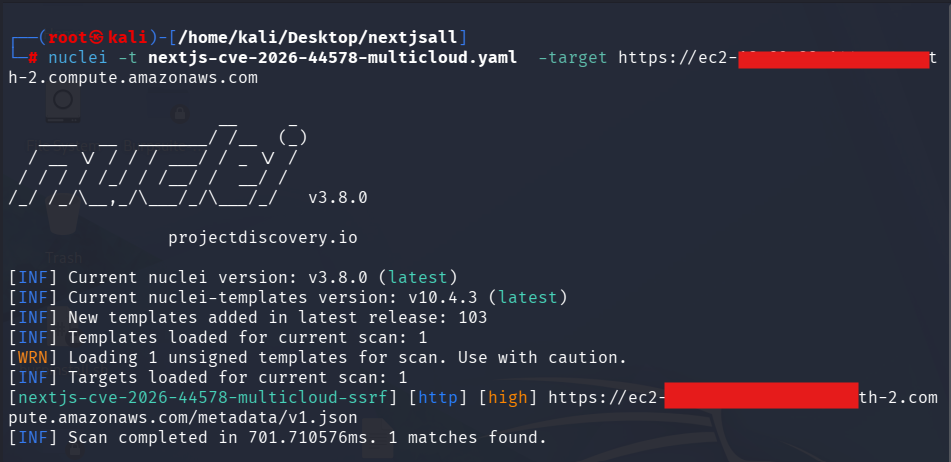 love07oj/nextjs-cve-2026-44578
Nuclei templates for detecting CVE-2026-44578 (Next.js WebSocket Upgrade SSRF) with multi-cloud metadata validation, Next.js fingerprinting, and…
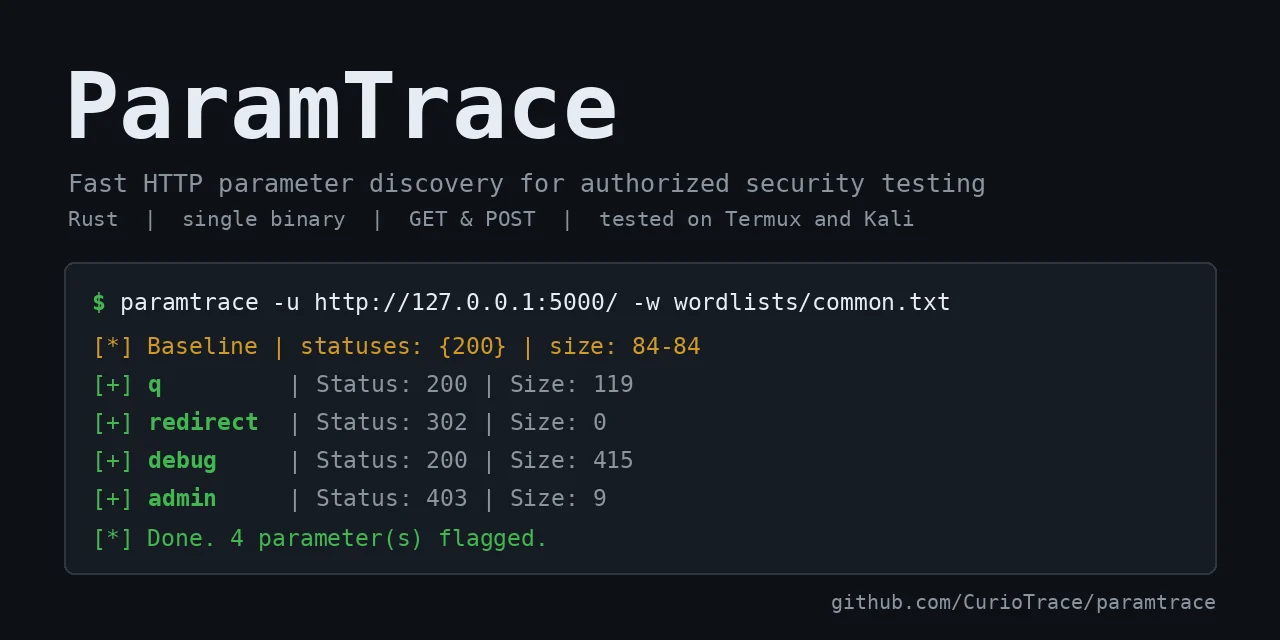 curiotrace/paramtrace
Fast HTTP parameter discovery for authorized security testing
 mycode83/godirb
Fast and easy-to-use directory brute-forcer written in Go.
 vighnesh91/omnisec-hex
Browser-local security monorepo with six modules for mobile APK/IPA triage, client-side DAST fuzzing, OSINT directories, offline AI threat scoring,…
 jackieya/vitevulscan
针对CVE-2025-30208和CVE-2025-31125的漏洞利用
 madexploits/ninja-form-exploit
CVE-2026-0740