
gobuster
 oj/gobuster
Directory/File, DNS and VHost busting tool written in Go
cloud-securitydns-subdomain-enumerationfuzzing+3
oj/gobusterDirectory/File, DNS and VHost busting tool written in Go
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
 kabiri-labs/rcekit
RCE detection and confirmation toolkit that tests URLs or captured HTTP requests for command injection, SSTI, blind and OOB paths, returning tiered…
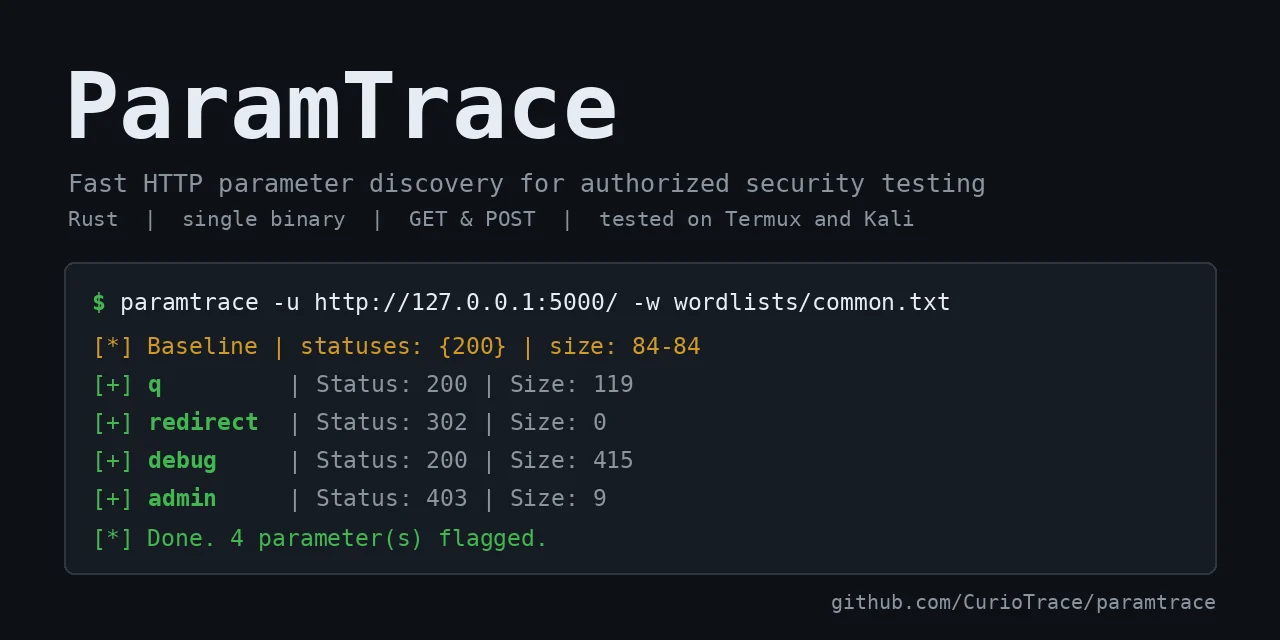 curiotrace/paramtrace
Fast HTTP parameter discovery for authorized security testing
 horkimhab/cve-2026-442_
CVE-2026-44289, CVE-2026-44290, CVE-2026-44291, CVE-2026-44292, CVE-2026-44294, CVE-2026-44295 - protobuf.js


 firerpa/lamda
Android Full-Stack Device Control Platform: WebRTC/H.264 remote desktop, UI/OCR/image-matching automation, one-click MITM, built-in Frida,…
 xmendez/wfuzz
Modular web fuzzer for automated security testing. Injects payloads into any HTTP request field to discover vulnerabilities, brute-force parameters,…
 ticarpi/jwt_tool
:snake: A toolkit for testing, tweaking and cracking JSON Web Tokens
 s0md3v/arjun
HTTP parameter discovery tool that finds valid query parameters for URL endpoints using a large dictionary, supporting GET/POST/JSON/XML requests,…
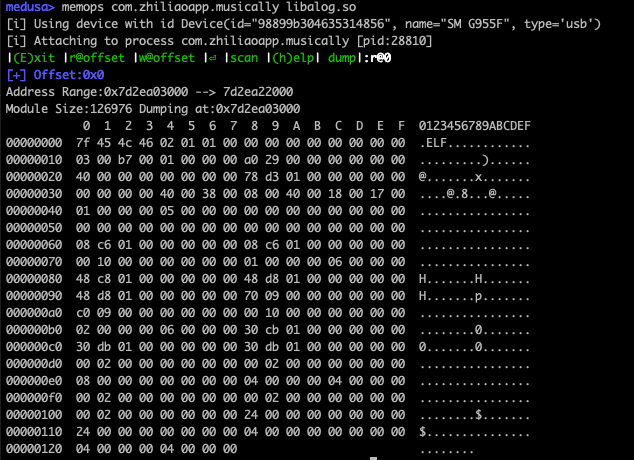 ch0pin/medusa
Mobile Edge-Dynamic Unified Security Analysis
 jtpereyda/boofuzz
A fork and successor of the Sulley Fuzzing Framework
 wapiti-scanner/wapiti
Web vulnerability scanner written in Python3
 portswigger/turbo-intruder
High-speed Burp Suite extension for sending large volumes of HTTP requests with a custom stack, Python-based attack configuration, and advanced…
 m0bilesecurity/rms-runtime-mobile-security
Runtime Mobile Security (RMS) 📱🔥 - is a powerful web interface that helps you to manipulate Android and iOS Apps at Runtime
 marin-m/pbtk
A toolset for reverse engineering and fuzzing Protobuf-based apps
 pedrib/poc
Advisories, proof of concept files and exploits that have been made public by @pedrib.