

 1n3/blackwidow
A Python based web application scanner to gather OSINT and fuzz for OWASP vulnerabilities on a target website.
 hardik05/damn_vulnerable_c_program
An example C program which contains vulnerable code for common types of vulnerabilities. It can be used to show fuzzing concepts.
 aircrack-ng/mdk4
IEEE 802.11 Wi-Fi testing tool for protocol weakness exploitation, including beacon flooding, deauthentication, packet fuzzing, and IDS evasion.…
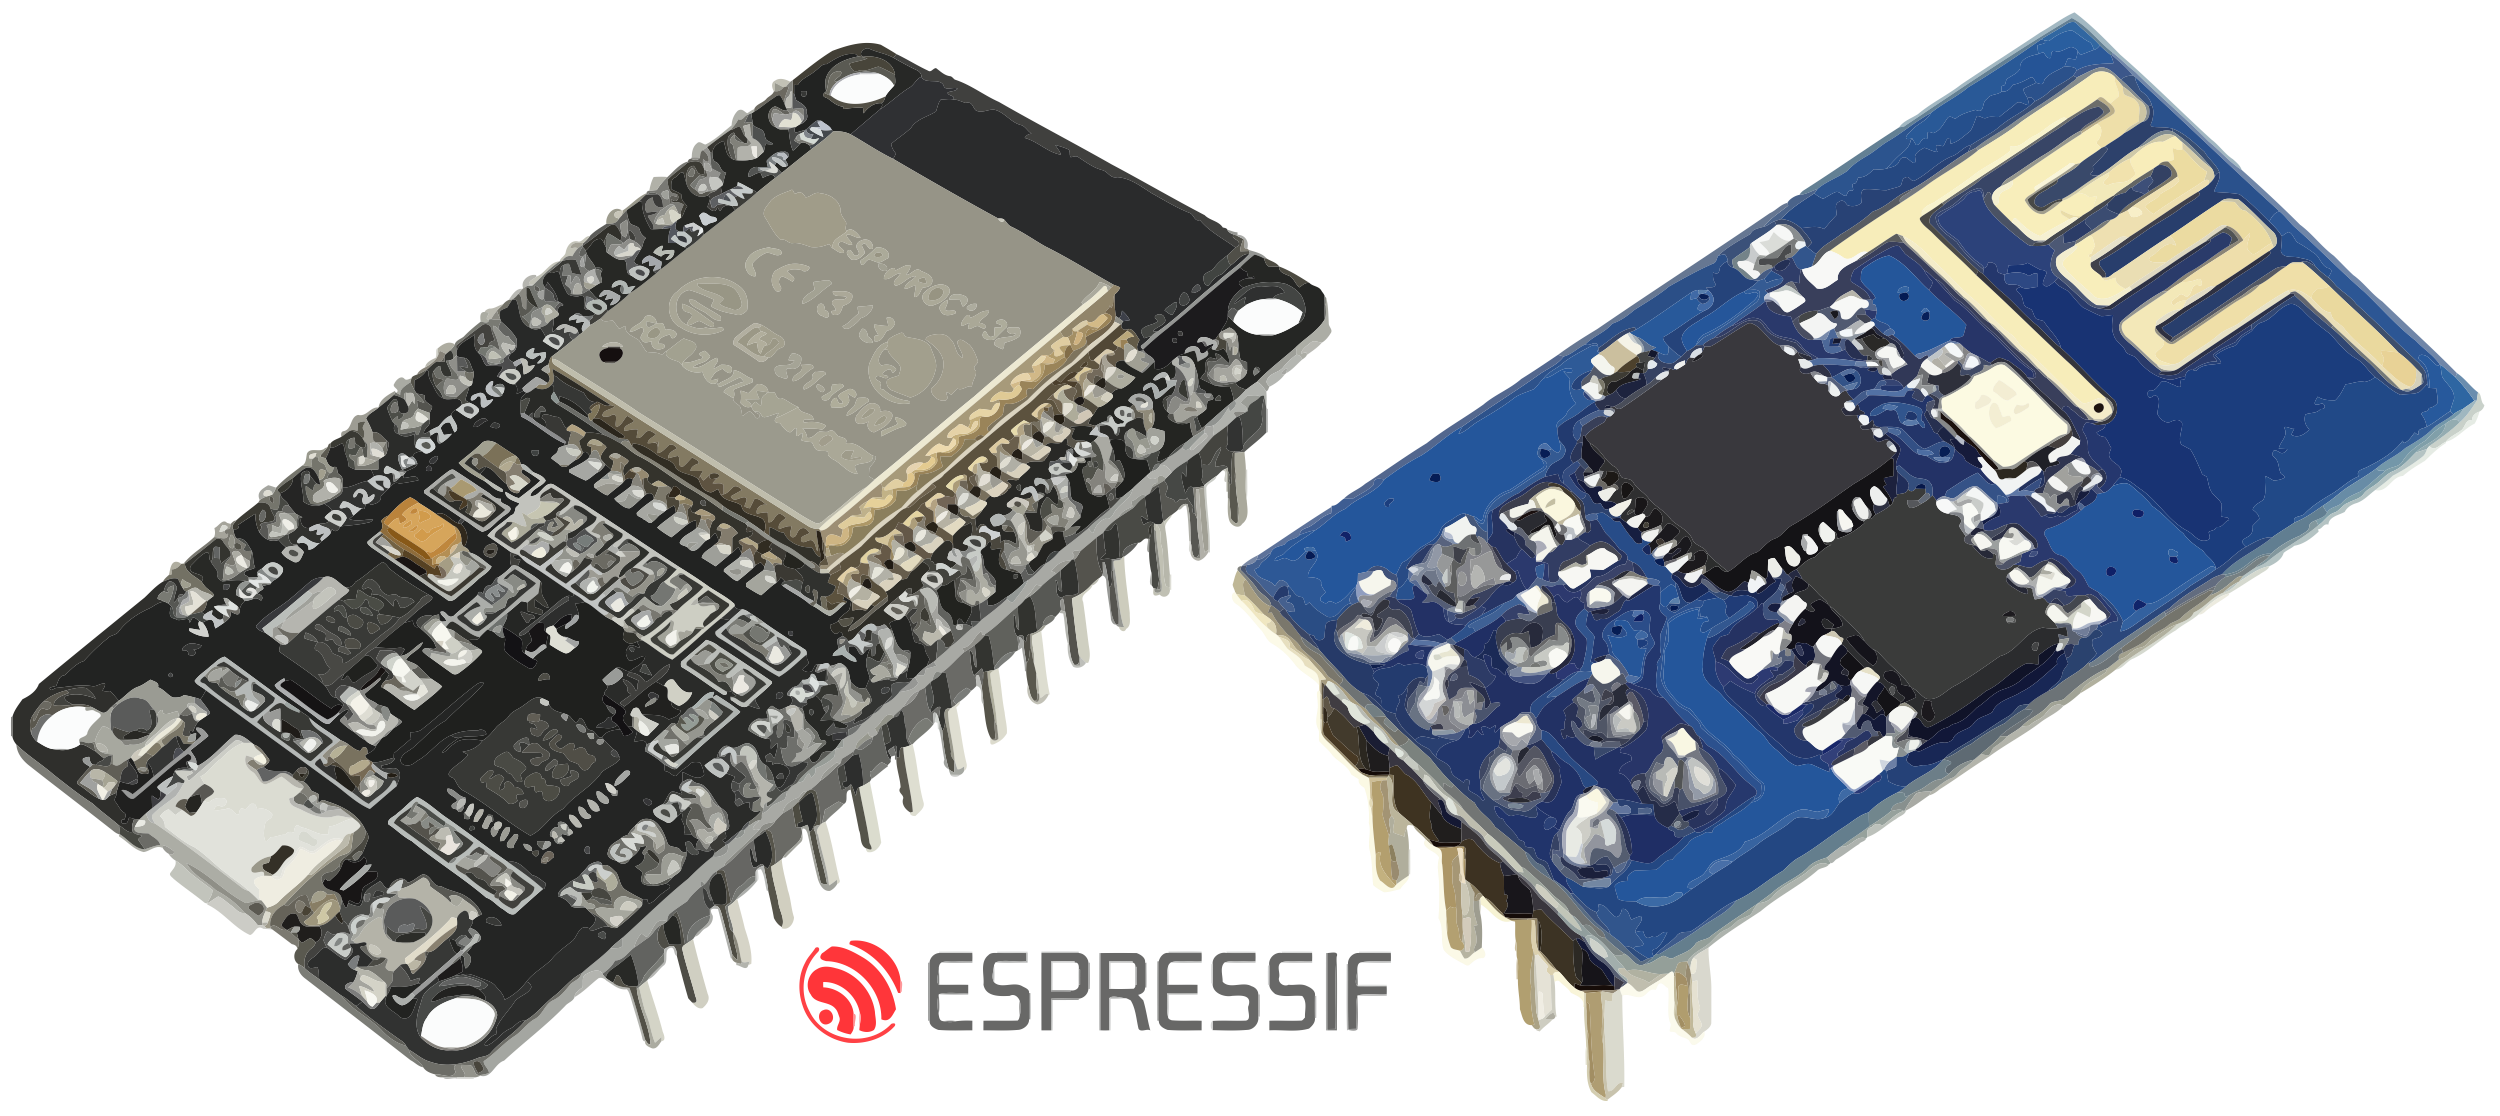 matheus-garbelini/esp32_esp8266_attacks
Proof of Concept of ESP32/8266 Wi-Fi vulnerabilties (CVE-2019-12586, CVE-2019-12587, CVE-2019-12588)
 redteampentesting/monsoon
Fast HTTP enumerator
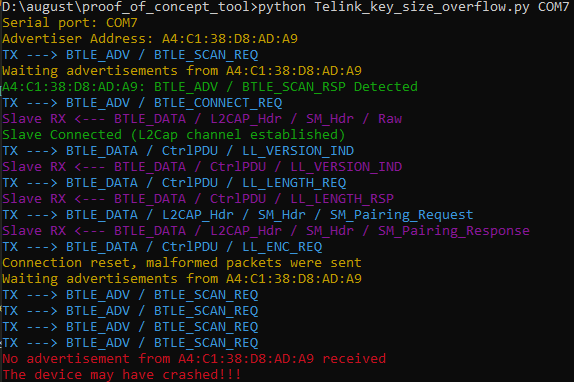 matheus-garbelini/sweyntooth_bluetooth_low_energy_attacks
Proof of Concept of Sweyntooth Bluetooth Low Energy (BLE) vulnerabilities.
 uds-se/formatfuzzer
Template-driven binary format fuzzer that generates and parses valid test inputs at high speed, with AFL++ integration for coverage-guided fuzzing.

 concollmic/concollmic
LLM-agent-powered concolic execution engine that instruments source code, summarizes path constraints in natural language, and generates test cases…
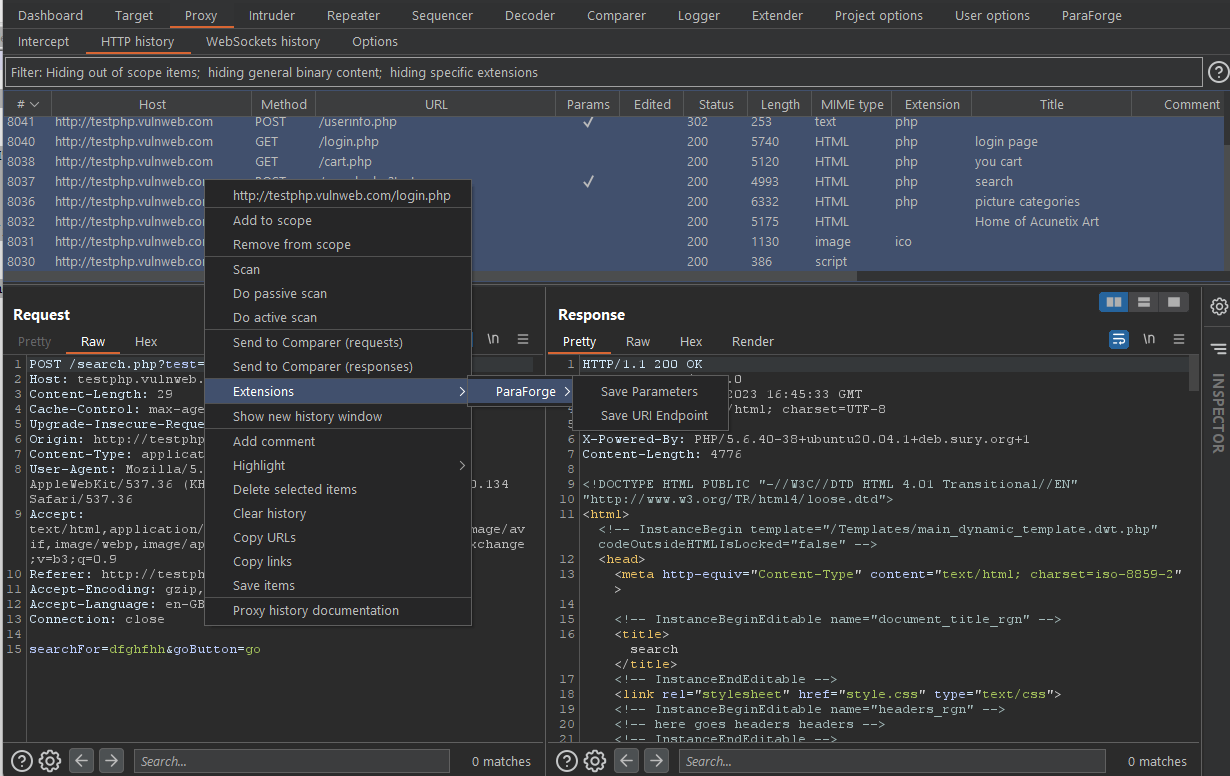 anof-cyber/paraforge
A BurpSuite extension to create a custom word-list of endpoint and parameters for enumeration and fuzzing
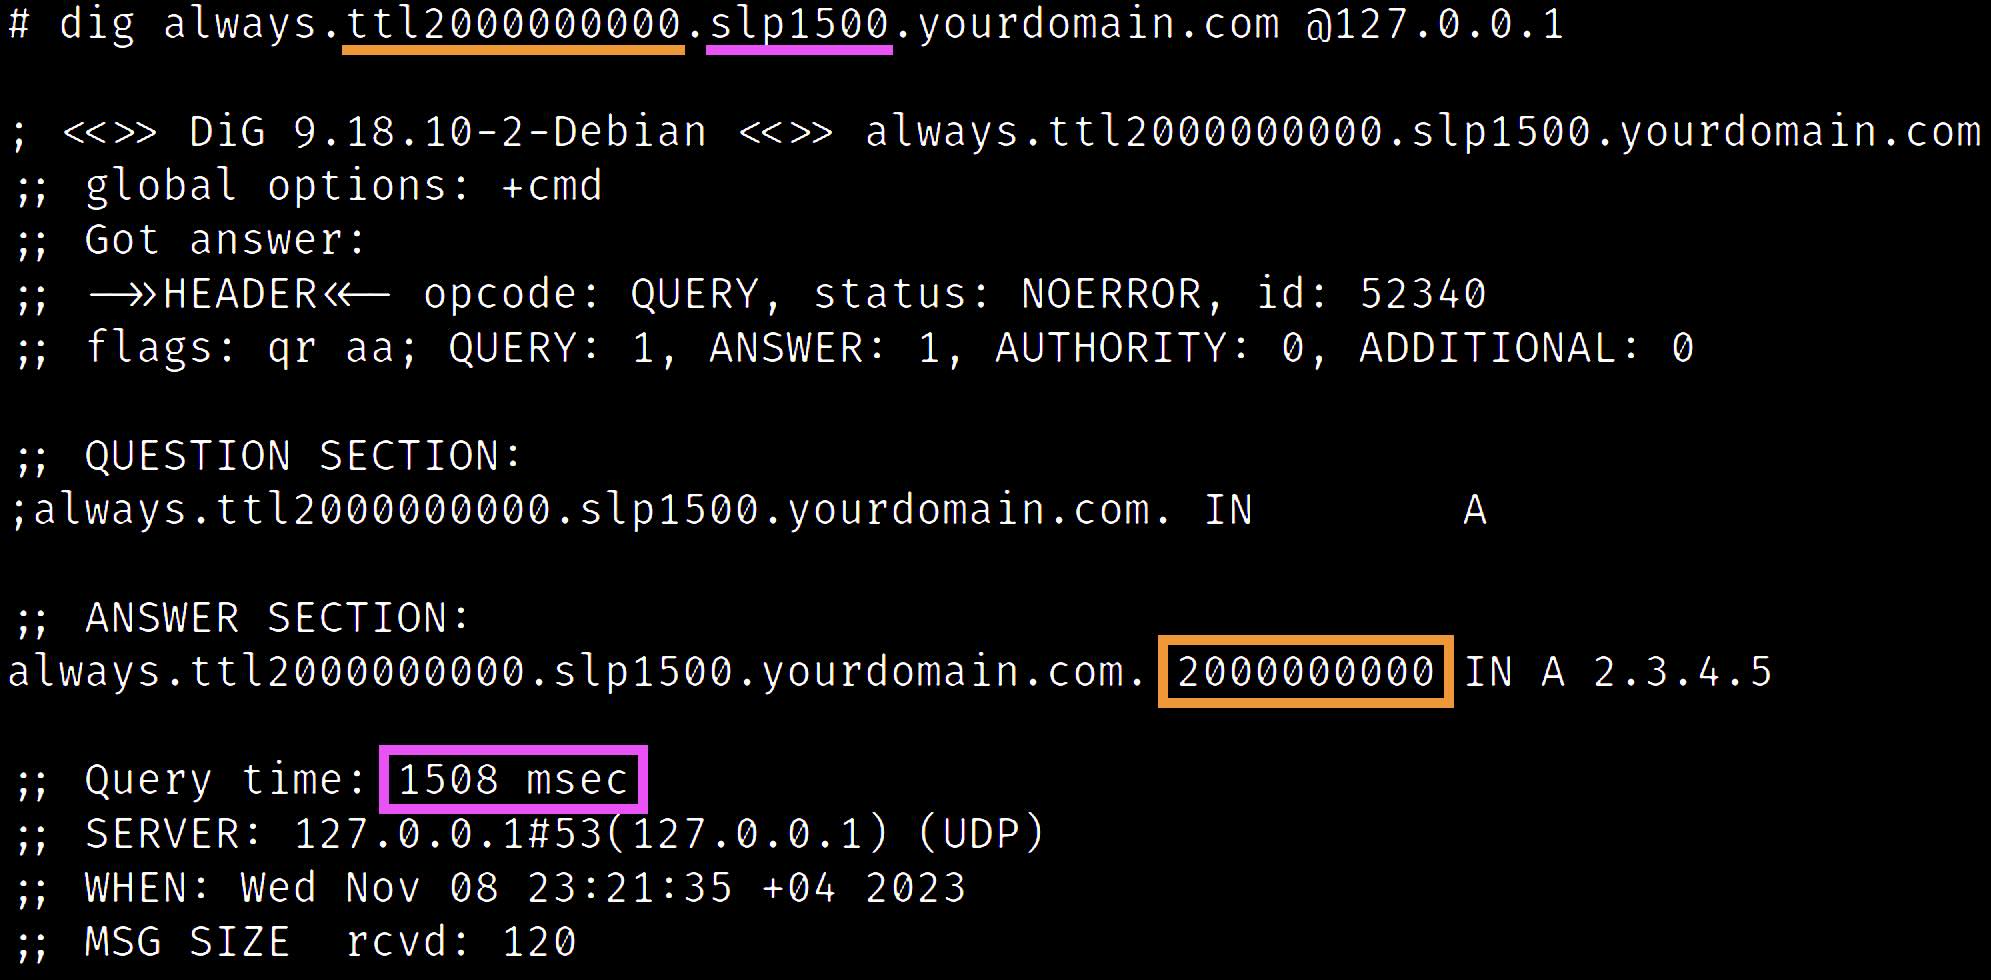 oryxlabs/polardns
PolarDNS is a specialized authoritative DNS server suitable for penetration testing and vulnerability research.
 samsung/utopia
UT based automated fuzz driver generation
 payatu/cve-2018-14442
PoC for Foxit Reader CVE-2018-14442
 sec-tools/litefuzz
A multi-platform fuzzer for poking at userland binaries, network clients and servers
 zeusbox/cve-2021-21017
Proof-of-concept exploit for Adobe Reader type confusion leading to heap overflow, with detailed root-cause analysis and detection guidance.