
CVE-2011-0762
 s3mpr1linux/cve-2011-0762
Um script automatizado melhorando o exploit do cve-2011-0762 postado no exploit-db
exploitationfuzzingpenetration-testing+2
s3mpr1linux/cve-2011-0762Um script automatizado melhorando o exploit do cve-2011-0762 postado no exploit-db
 freefv/cve-2020-6308-mass-exploiter
Mass exploiter for CVE-2020-6308 with multi-worker support, enabling automated exploitation of vulnerable SAP NetWeaver systems.
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
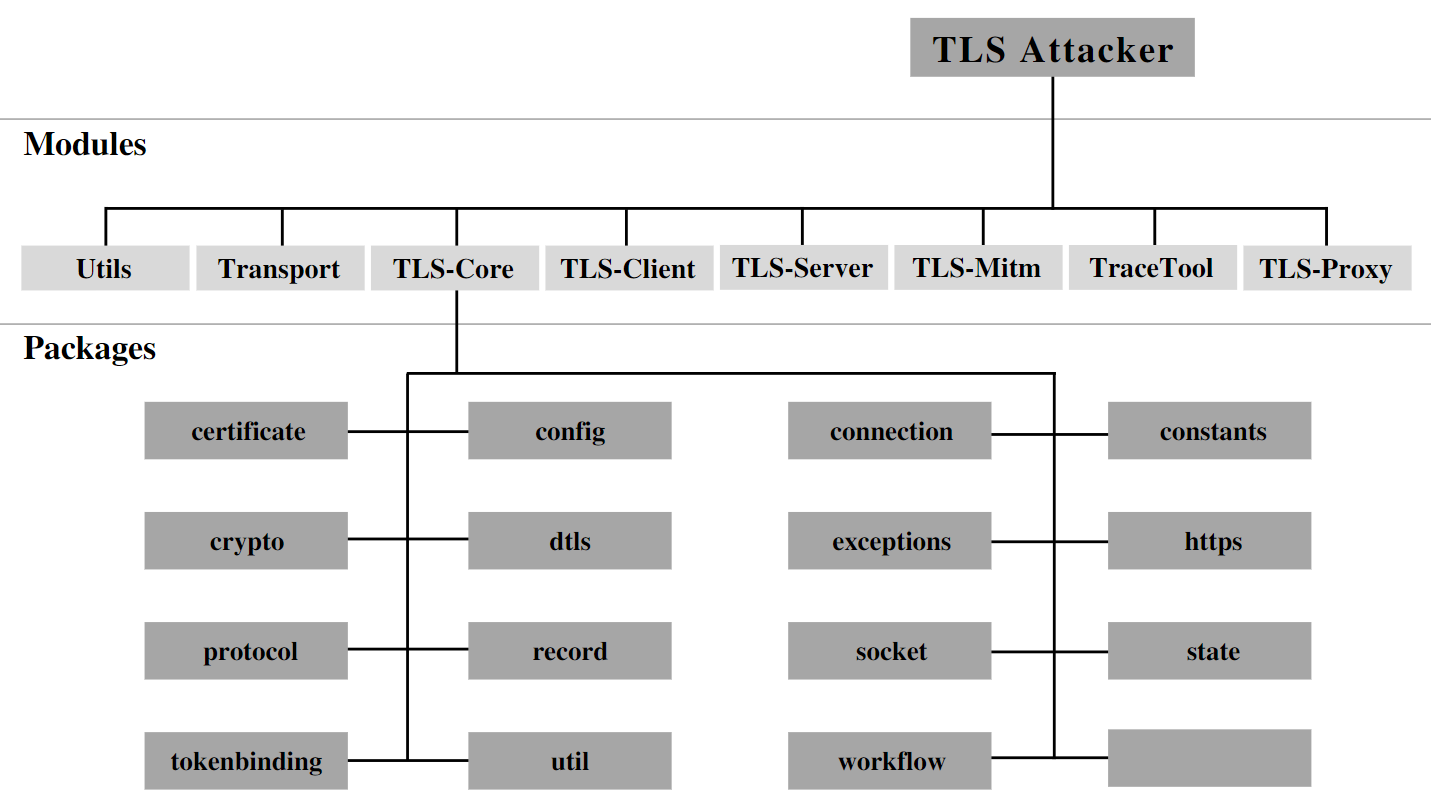 tls-attacker/tls-attacker
Java-based framework for systematic fuzzing and analysis of TLS libraries. Enables arbitrary protocol message crafting, modification, and testing of…
 angorafuzzer/angora
Coverage-guided fuzzer that uses taint tracking and scalar optimization to solve path constraints without symbolic execution, improving branch…
 homjxi0e/cve-2017-9430
Proof-of-concept exploit for CVE-2017-9430, a stack-based buffer overflow in dnstracer 1.9, triggered via a long command-line argument causing denial…
 skylined/bugid
Detect, analyze and uniquely identify crashes in Windows applications