
OneListForAll
 six2dez/onelistforall
Curated, categorized wordlist generator for web fuzzing, directory enumeration, and subdomain discovery. Automatically syncs 36+ sources, classifies…
curated-resourcesfuzzinginformation-gathering+3
3.3k
six2dez/onelistforallCurated, categorized wordlist generator for web fuzzing, directory enumeration, and subdomain discovery. Automatically syncs 36+ sources, classifies…
 0xinfection/tidos-framework
The Offensive Manual Web Application Penetration Testing Framework.
 x3omdax/penbox
PenBox - A Penetration Testing Framework - The Tool With All The Tools , The Hacker's Repo
 kmkz/exploits
Original CVEs, exploit PoCs, and security advisories with detailed vulnerability chains, privilege escalation, and container escape techniques for…
 dmontgomery40/pentest-mcp
NOT for educational purposes: An MCP server for professional penetration testers including STDIO/HTTP/SSE support, nmap, go/dirbuster, nikto, JtR,…
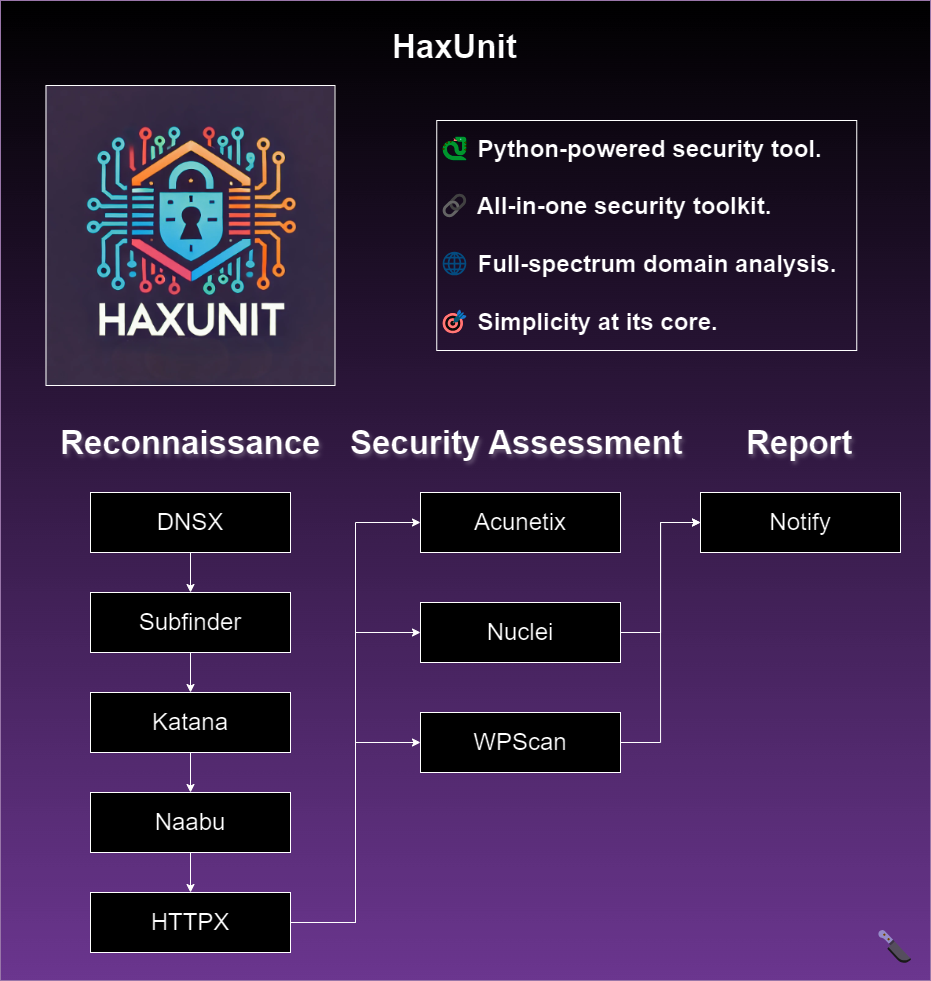 bandit-haxunit/haxunit
Automated web domain reconnaissance and security assessment tool integrating subdomain enumeration, port scanning, vulnerability scanning, and…
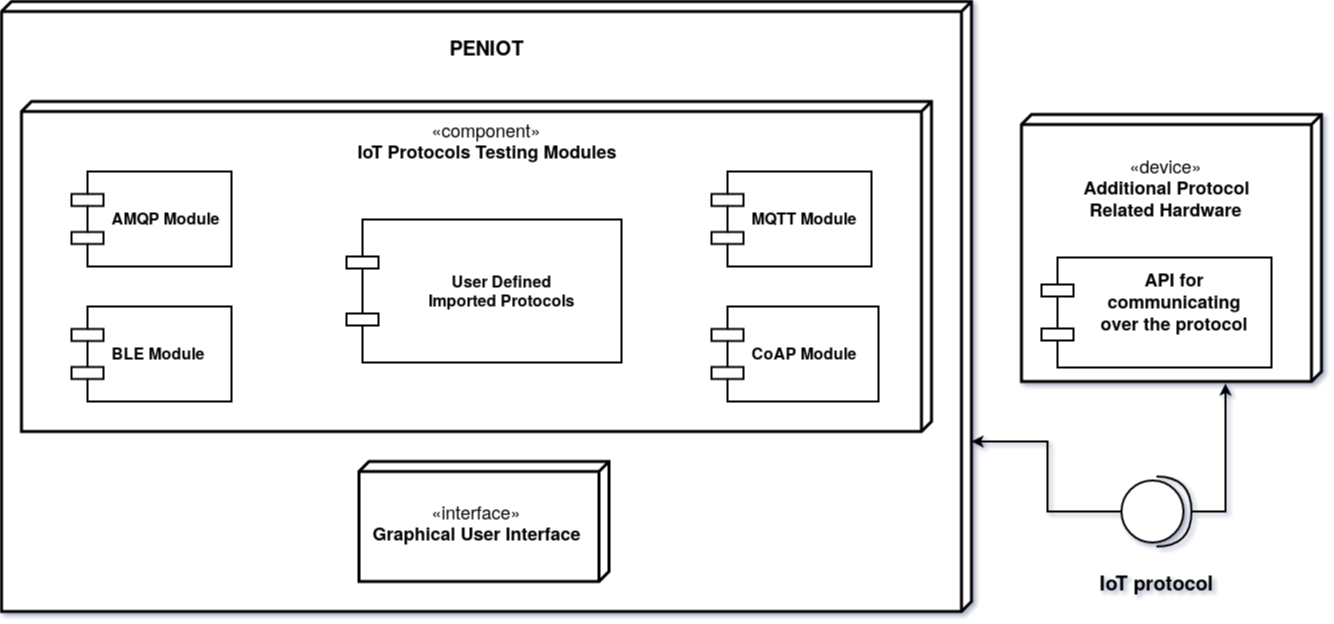
 rapiddns/afuzz
Automated web path fuzzing tool that detects hidden directories, files, and endpoints using intelligent language detection, blacklist/whitelist…
 syss-research/wirebug
WireBug is a toolset for Voice-over-IP penetration testing
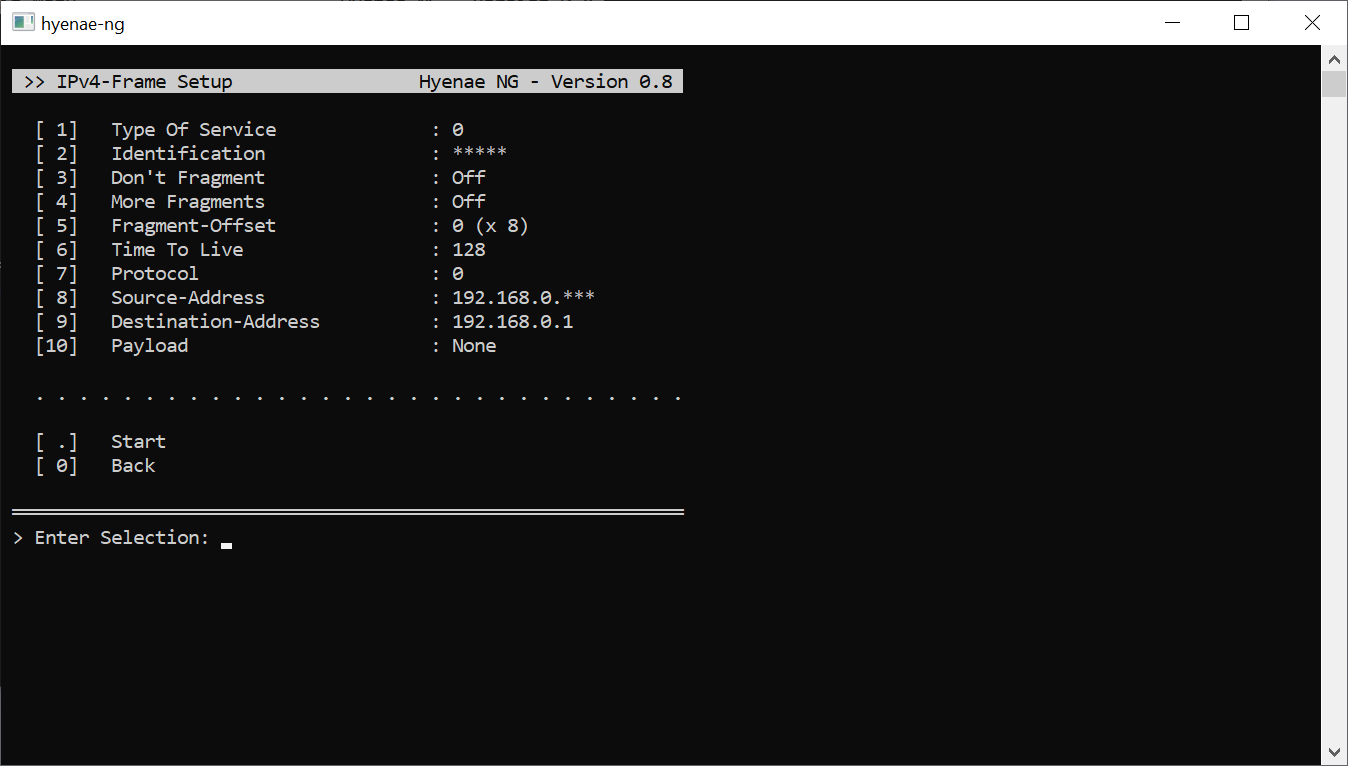 r-richter/hyenae-ng
Cross-platform network packet generator with full layer spoofing, pattern-based address randomization, and flood detection evasion for stress-testing…
 agampreet-singh/redroot
RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…
 nu11secur1ty/insect
High-performance web path discovery and directory brute-forcing tool. Discovers hidden files, directories, and endpoints using customizable…
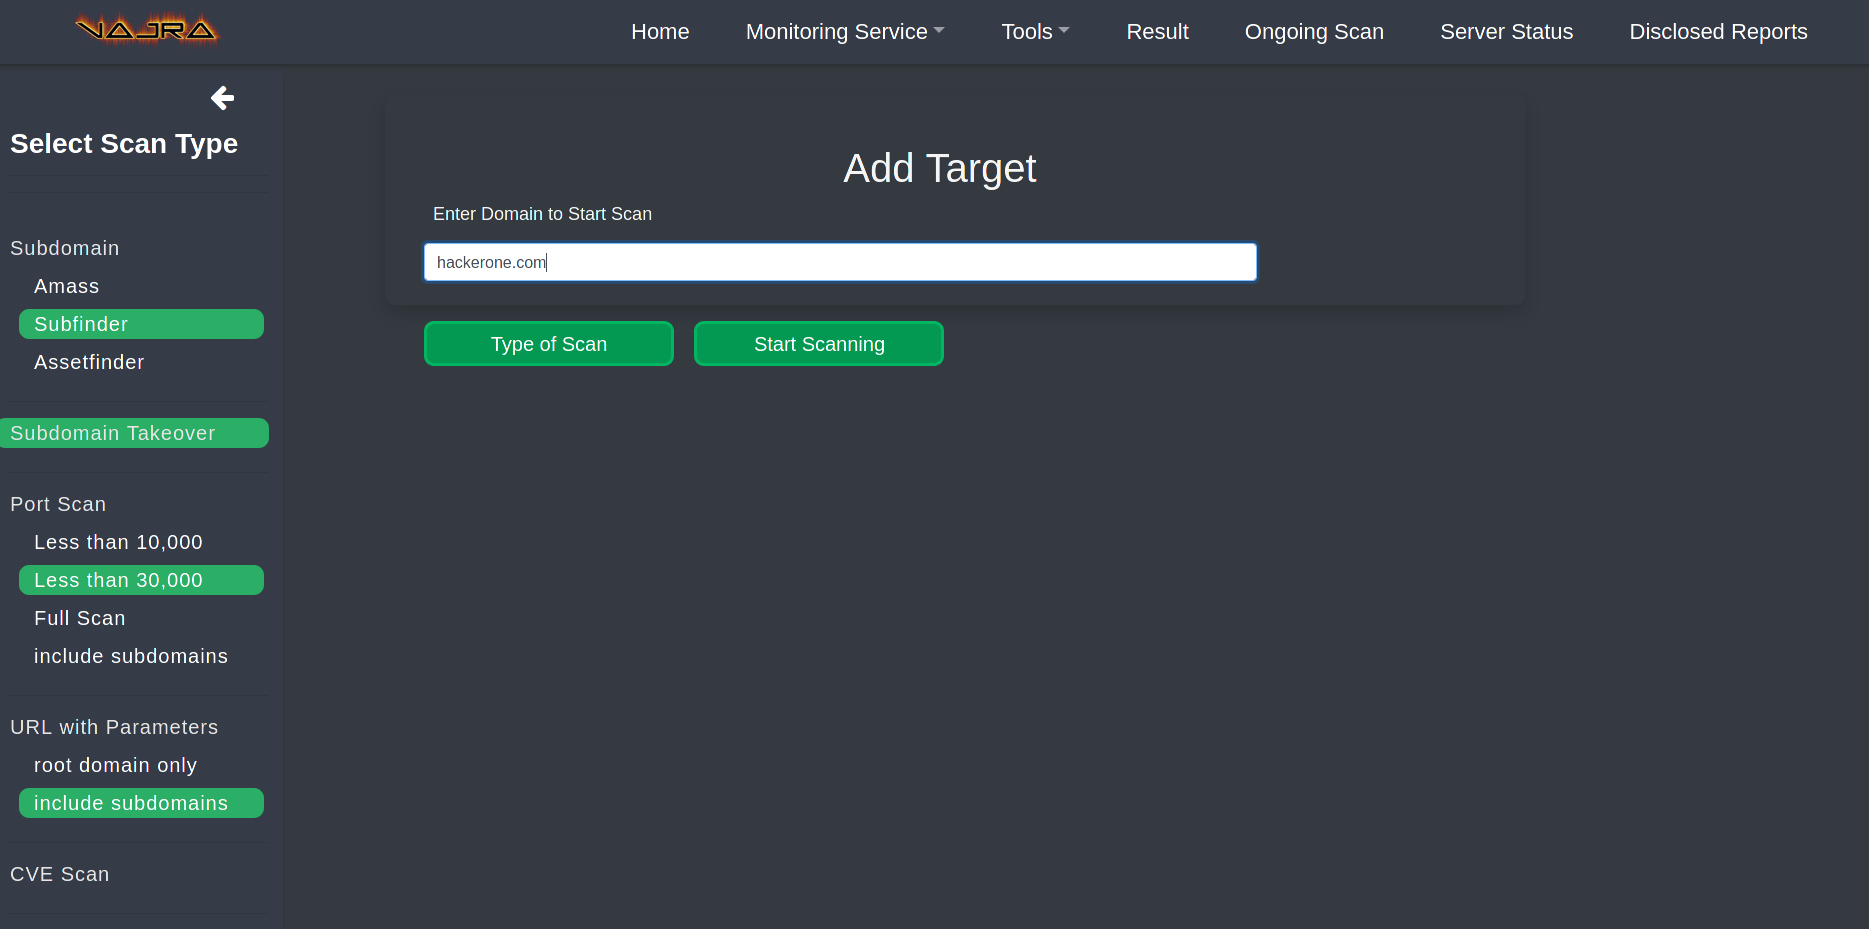 r3curs1v3-pr0xy/vajra
Vajra is a highly customizable target and scope based automated web hacking framework to automate boring recon tasks and same scans for multiple…
 khalilbijjou/wafninja
WAFNinja is a tool which contains two functions to attack Web Application Firewalls.
 mindpatch/lorsrf
Fast CLI tool to find the parameters that can be used to find SSRF or Out-of-band resource load :artificial_satellite: :crab:
 nescau-ufla/fuzzingtool
Software for fuzzing, used on web application pentestings.
 seungsoo-lee/delta
PROJECT DELTA: SDN SECURITY EVALUATION FRAMEWORK