
DHCPig
 kamorin/dhcpig
DHCP exhaustion script written in python using scapy network library
exploitationfuzzingnetwork-security+3
kamorin/dhcpigDHCP exhaustion script written in python using scapy network library
 bw3ll/sharem
SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…
 praetorian-inc/augustus
LLM security testing framework for detecting prompt injection, jailbreaks, and adversarial attacks — 190+ probes, 28 providers, single Go binary
 seanheelan/anamnesis-release
Evaluation framework for studying LLM agents that automatically generate working exploits from vulnerability reports, bypassing modern security…
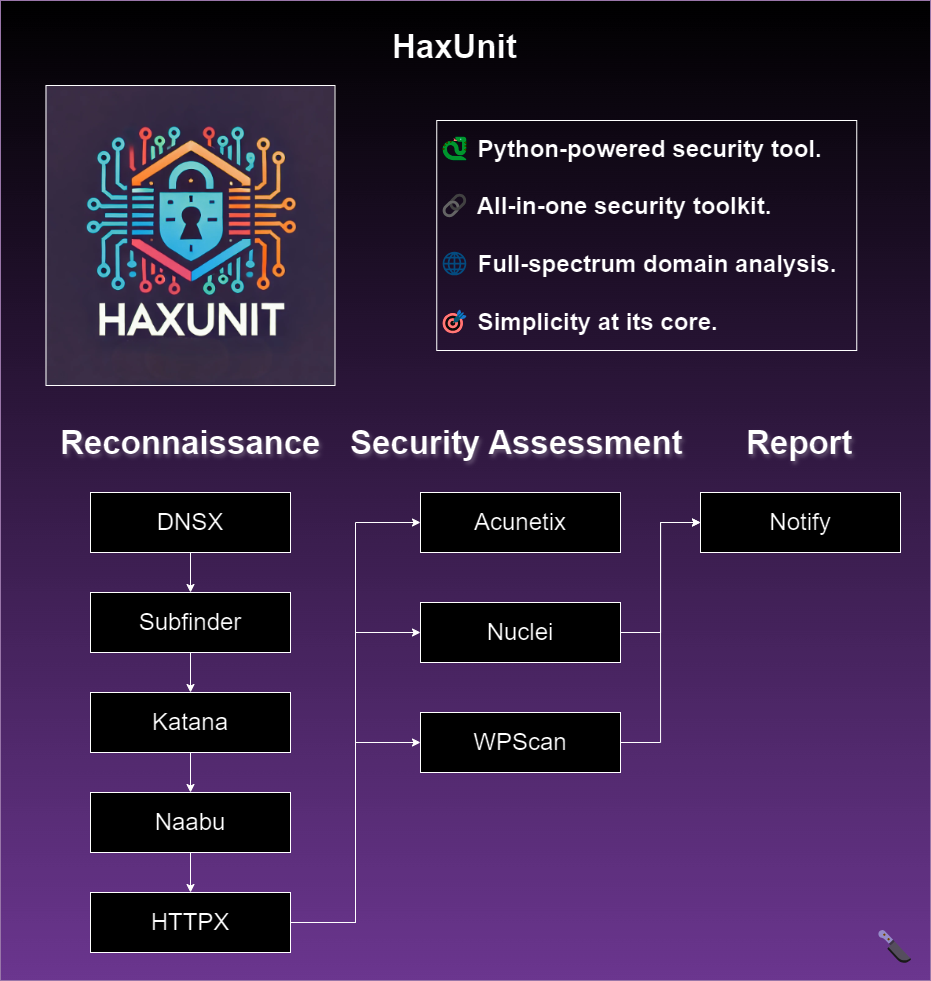 bandit-haxunit/haxunit
Automated web domain reconnaissance and security assessment tool integrating subdomain enumeration, port scanning, vulnerability scanning, and…
 concollmic/concollmic
LLM-agent-powered concolic execution engine that instruments source code, summarizes path constraints in natural language, and generates test cases…
 shenli/distributed-system-testing
AI-agent skills for distributed-systems testing
 hellsender01/llmmap
Automated prompt injection testing framework for LLM-integrated applications with dual-LLM architecture.
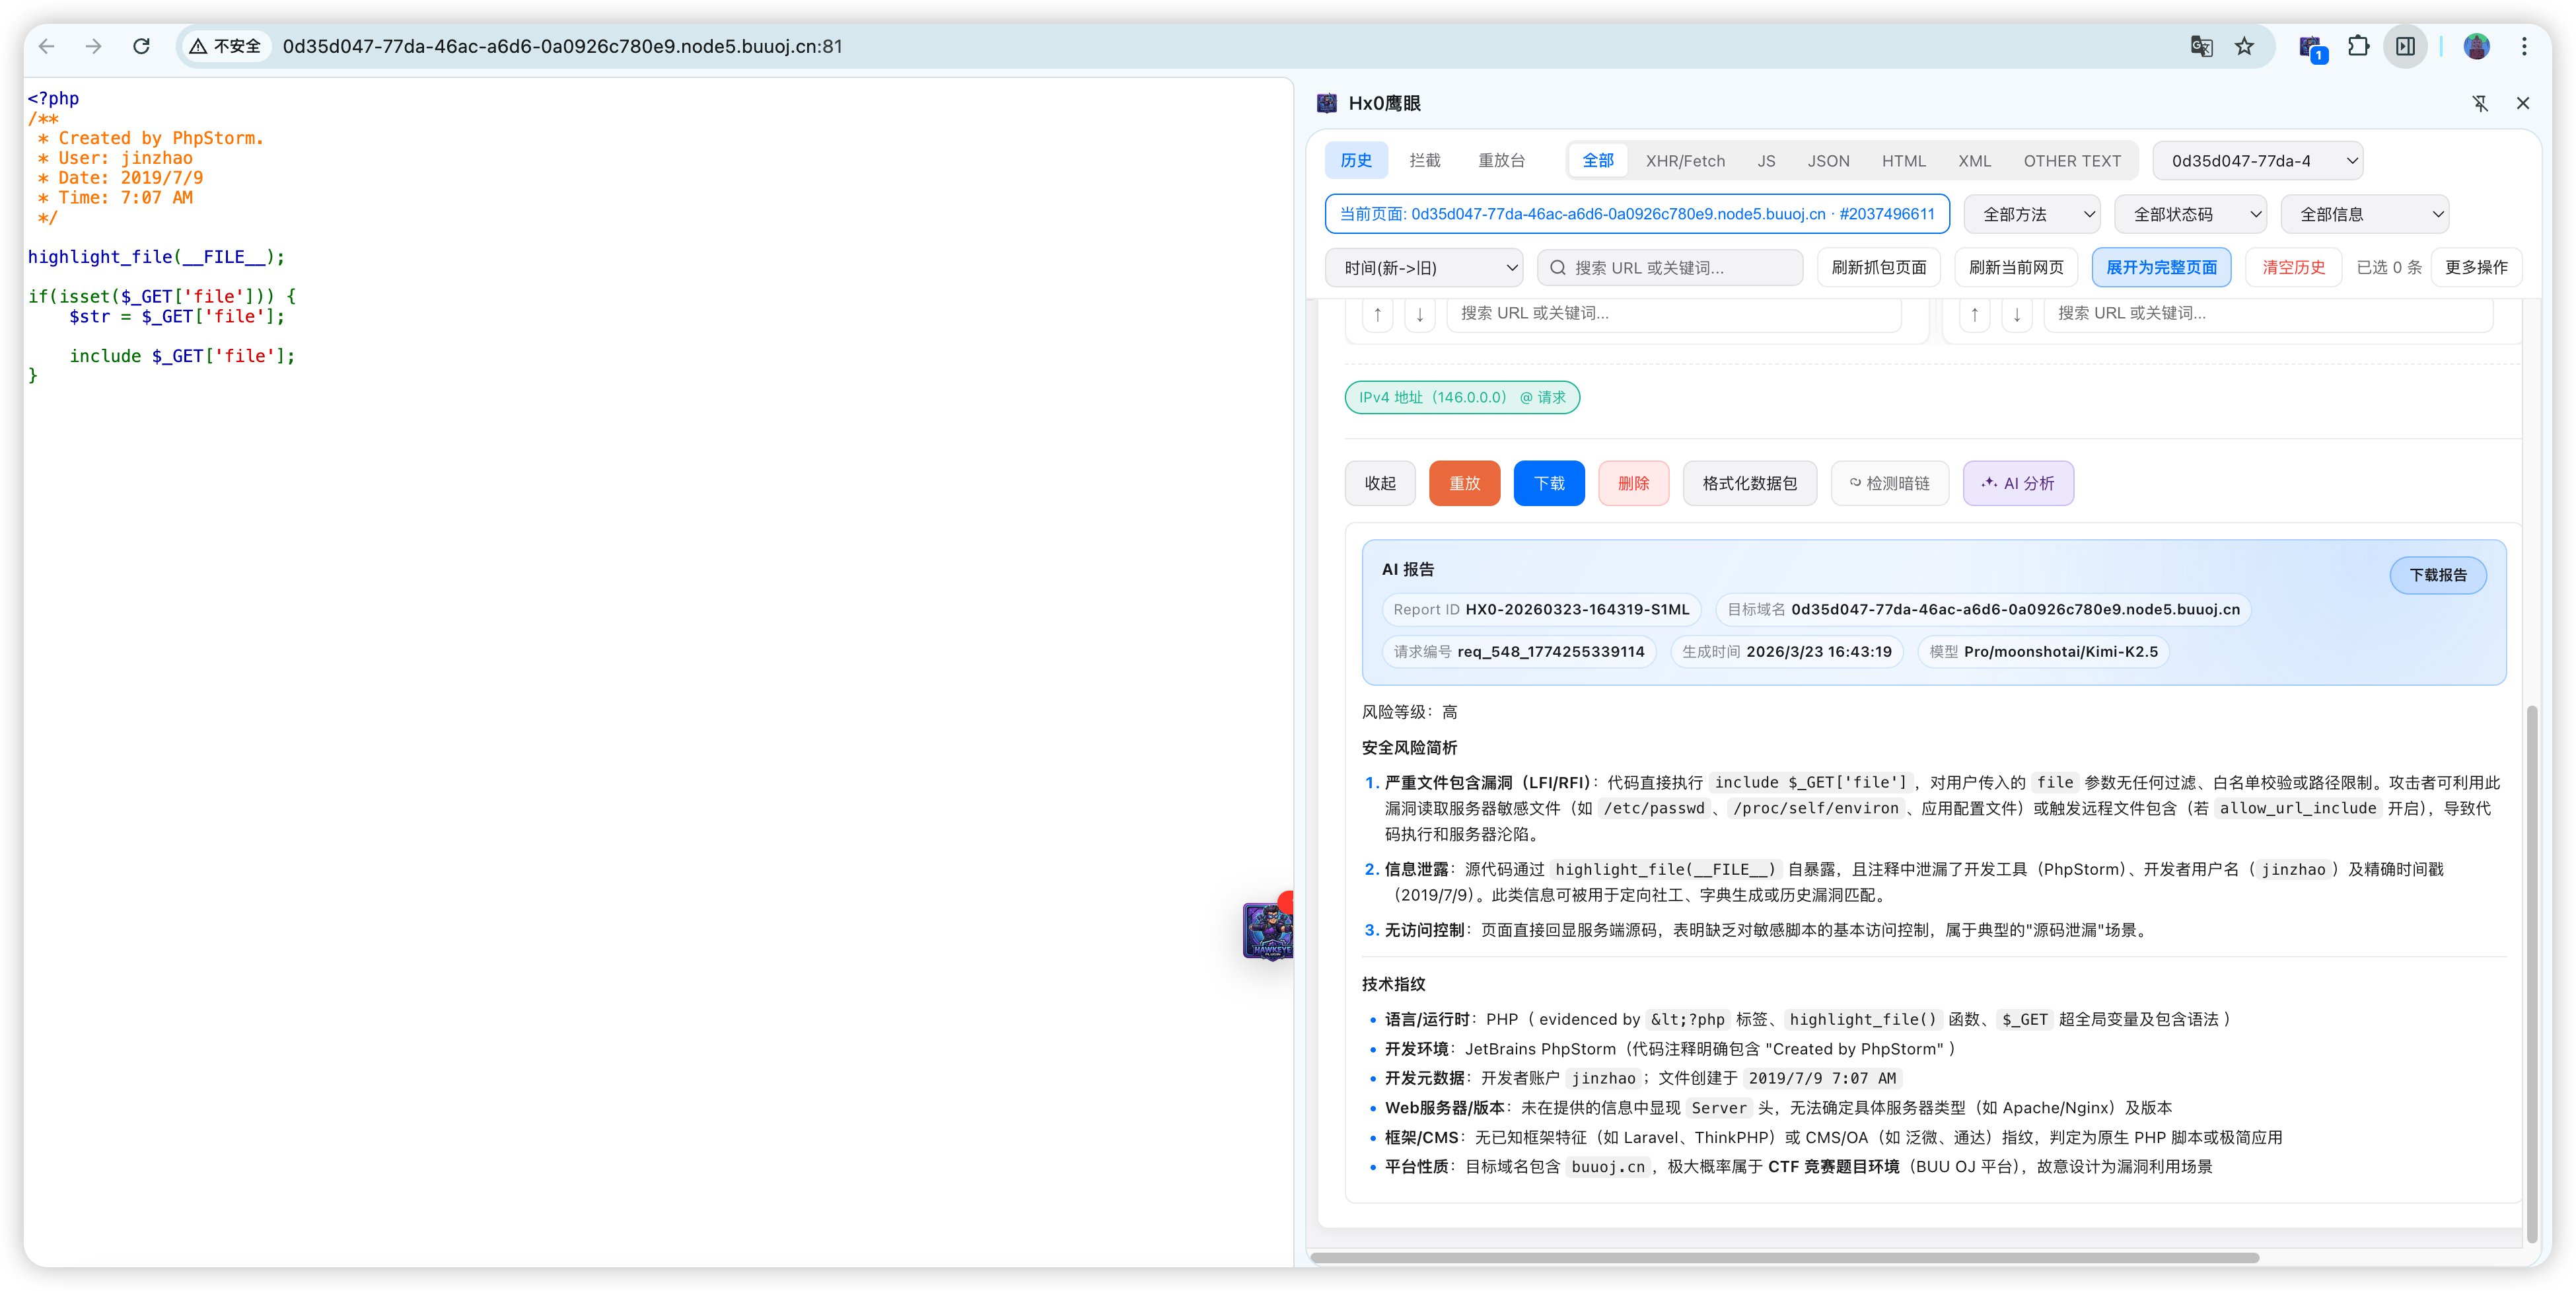 asaotomo/hx0-hawkeye
一个轻量级浏览器抓包与安全分析扩展,在浏览器侧边栏中即可完成抓包、拦截、修改、重放、规则检测与AI辅助分析的完整工作流。(A lightweight browser extension for traffic capture and security analysis, enabling…
 l33tdawg/aether
AI Smart Contract Security Analysis and PoC Generation Framework
 off-by-1-labs/flawed
Fix-Like Artifacts With Embedded Defects
 turtlesec-software/crlf-desyncs
Nuclei templates and exploit resources for CRLF based desync attacks
 fuzzingbrain/fuzzingbrain-bench
A benchmark for LLM-driven bug discovery: 77 challenges across 43 open-source projects (C/C++/Java).
 bishopfox/cve-2022-22274_cve-2023-0656
Proof-of-concept exploit for SonicWall SonicOS stack-based buffer overflows (CVE-2022-22274, CVE-2023-0656) that tests and triggers crashes via…
 ericmtzmtz/pwnproxy
An open, local-first security testing platform for pentesters, AI agents, CI/CD pipelines, and teams.
 d4rk007/f5-big-ip-cve-2020-5902-mass-exploiter
Mass exploiter for CVE-2020-5902 targeting F5 Big-IP devices, with multi-threaded scanning and exploitation capabilities for unauthenticated remote…
 foxirain/linux-kernel-codex-harness
Evidence-driven Linux kernel vulnerability research harness used in the investigation of CVE-2026-31720
 spiralbl0ck/ai_hacking
Collection of CVE(work) on tenserflow binary pwning it