
CANToolz
 cantoolz/cantoolz
CANToolz - Black-box CAN network analysis framework
embedded-systems-securityfuzzinghardware-iot-security+3
cantoolz/cantoolzCANToolz - Black-box CAN network analysis framework
 airbus-seclab/gustave
GUSTAVE is a fuzzing platform for embedded OS kernels. It is based on QEMU and AFL (and all of its forkserver siblings). It allows to fuzz OS kernels…
 zcutlip/bowcaster
Python-based exploit development framework with payloads, encoders, and connect-back servers, focused on MIPS CPU architecture but designed for…
 nccgroup/nobex
nOBEX allows emulating the PBAP, MAP, and HFP profiles to test vehicle infotainment systems and similar devices using these profiles
 arthastang/router-exploit-shovel
Automated Application Generation for Stack Overflow Types on Wireless Routers
 0ldev/politician
Modern WiFi auditing library for ESP32 using advanced 802.11 techniques. Captures WPA/WPA2/WPA3 handshakes via PMKID extraction and CSA injection…
 hacefresko/cve-2025-40634
Exploit for stack-based buffer overflow found in the conn-indicator binary in the TP-Link Archer AX50 router
 nccgroup/cecster
A GUI-based tool to perform security testing against the HDMI CEC (Consumer Electronics Control) and HEC (HDMI Ethernet Channel) protocols

 tin-z/cve-2023-35086-poc
POC of CVE-2023-35086 only DoS
 fundacion-sadosky/vbox_cve_2017_10235
[CVE-2017-10235] Description and PoC of VirtualBox E1000 device Buffer Overflow
 libriscv/libloong
The fastest LoongArch sandbox
 geeoon/fault-injection-finder
Automatically find and execute fault injection attacks
 fi01/libmsm_acdb_exploit
Exploit for CVE-2013-2597, a stack-based buffer overflow in the Qualcomm ACDB audio driver, enabling privilege escalation on affected Android devices.
 nccgroup/edidfuzzer
EDID (Enhanced Display Identification Data) Fuzzer
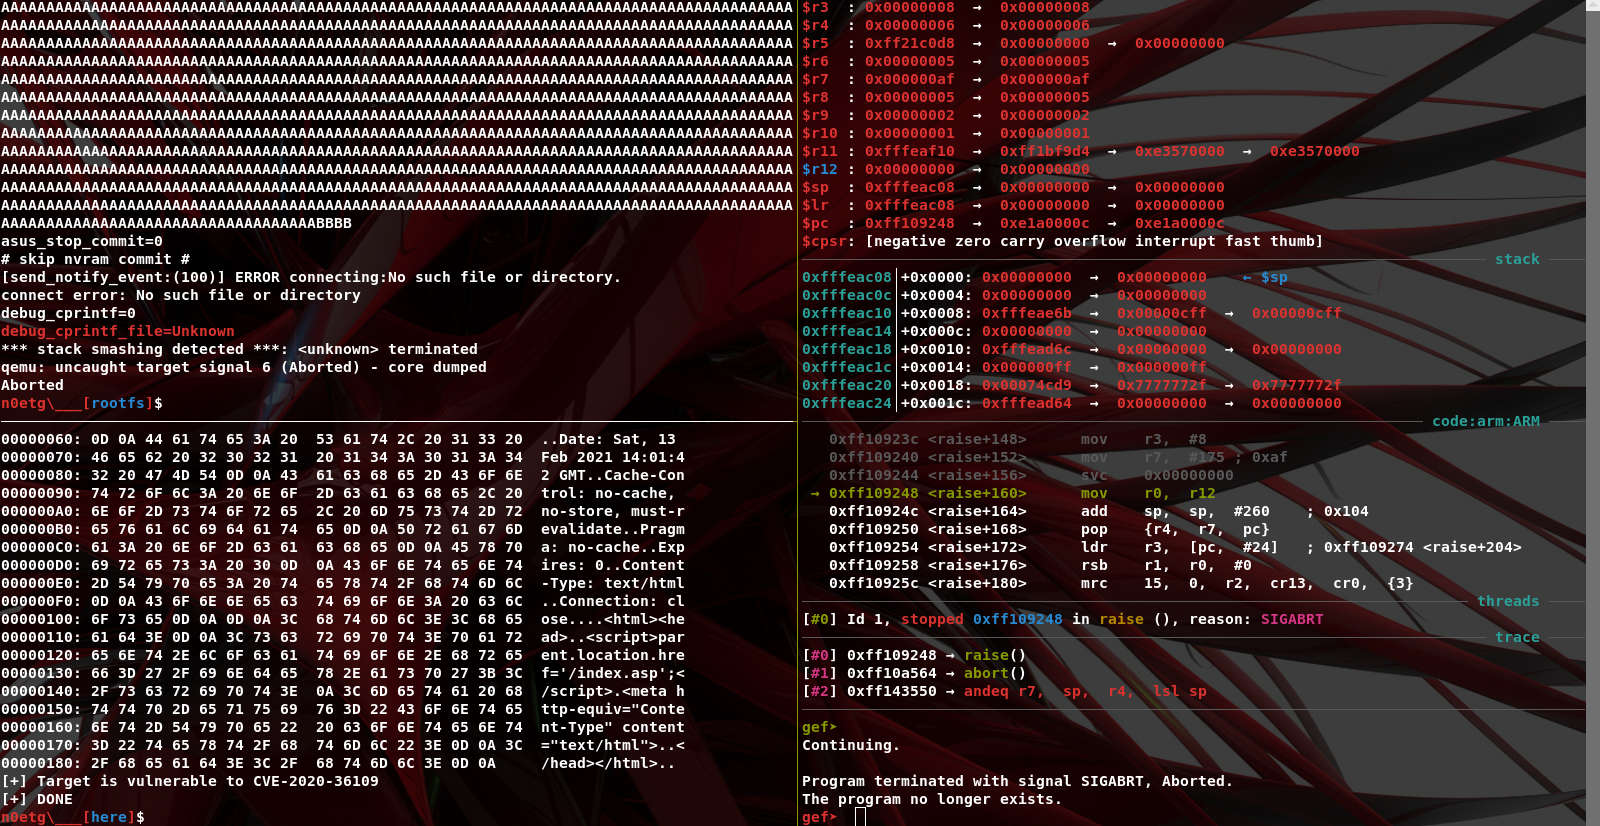 sunn1day/cve-2020-36109-poc
CVE-2020-36109 PoC causing DoS
 mellow-hype/cve-2023-33476
Exploits for a heap overflow in MiniDLNA <=1.3.2 (CVE-2023-33476)
 alexandre-bartel/cve-2019-12594
This is a PoC for CVE-2019-12594, a vulnerability in DOSBox 0.74-2.