
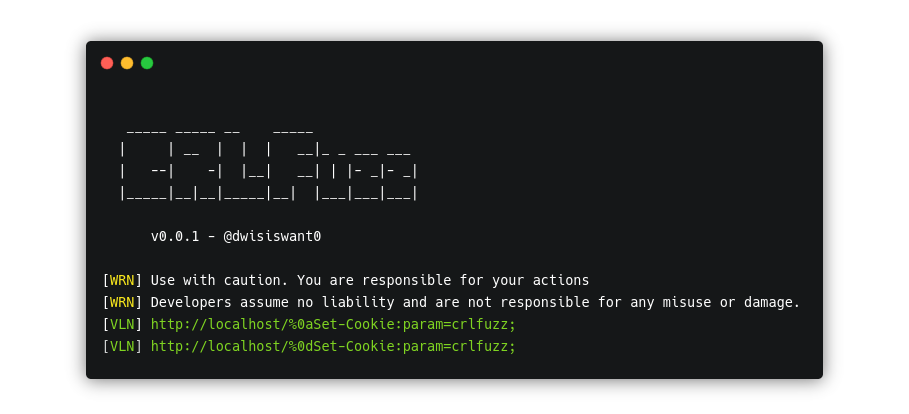
crlfuzz
 dwisiswant0/crlfuzz
A fast tool to scan CRLF vulnerability written in Go
fuzzingvulnerability-scannersweb-security
dwisiswant0/crlfuzzA fast tool to scan CRLF vulnerability written in Go
 fcavallarin/htcap
htcap is a web application scanner able to crawl single page application (SPA) recursively by intercepting ajax calls and DOM changes.
 jaeles-project/jaeles-signatures
Default signature for Jaeles Scanner
 dwisiswant0/ppfuzz
A fast tool to scan client-side prototype pollution vulnerability written in Rust. 🦀
 damian89/extended-ssrf-search
Smart ssrf scanner using different methods like parameter brute forcing in post and get...
 v4ltonn/cve-2026-42530
Scanner PoC for CVE-2026-42530 -- nginx 1.31.0-1.31.1 HTTP/3 QPACK encoder stream Use-After-Free (CVSS 9.2)
 kiralab/text4shell-scan
A fully automated, accurate, and extensive scanner for finding text4shell RCE CVE-2022-42889
 rk-000/log4j_scan_advance
A fully automated, accurate, and extensive scanner for finding log4j RCE CVE-2021-44228
 jack0we/cve-2024-6387
Proof-of-concept exploit for CVE-2024-6387, a remote code execution vulnerability in OpenSSH server, demonstrating exploitation techniques for…
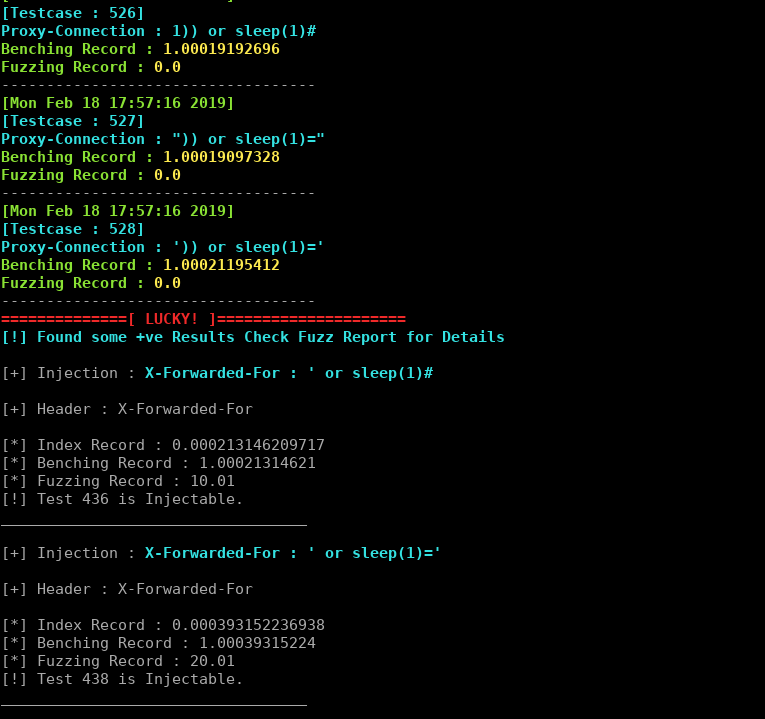 johntroony/blisqy
Version 0.2 - Exploit Time-based blind-SQL injection in HTTP-Headers (MySQL/MariaDB).
 vitaliy-grigoriev/protocol-analyzer
Fuzz testing framework for network protocols.
 cao-wuhui/cve-2025-69720
Advisory for CVE-2025-69720: stack-based buffer overflow in GNU ncurses infocmp (CWE-121)
 13m0n4de/pngcheck-vulns
A repository of proof-of-concept files demonstrating disclosed and patched vulnerabilities in pngcheck (2.4.0 - 3.0.1), including CVE-2020-27818,…
 xmendez/wfuzz
Modular web fuzzer for automated security testing. Injects payloads into any HTTP request field to discover vulnerabilities, brute-force parameters,…
 danmcinerney/xsscrapy
XSS spider - 66/66 wavsep XSS detected
 devanshbatham/openredirex
A fuzzer for detecting open redirect vulnerabilities
 lc/theftfuzzer
TheftFuzzer is a tool that fuzzes Cross-Origin Resource Sharing implementations for common misconfigurations.