smugglefuzz
 moopinger/smugglefuzz
A rapid HTTP downgrade smuggling scanner written in Go.
api-security-testingfuzzingpenetration-testing+3
moopinger/smugglefuzzA rapid HTTP downgrade smuggling scanner written in Go.
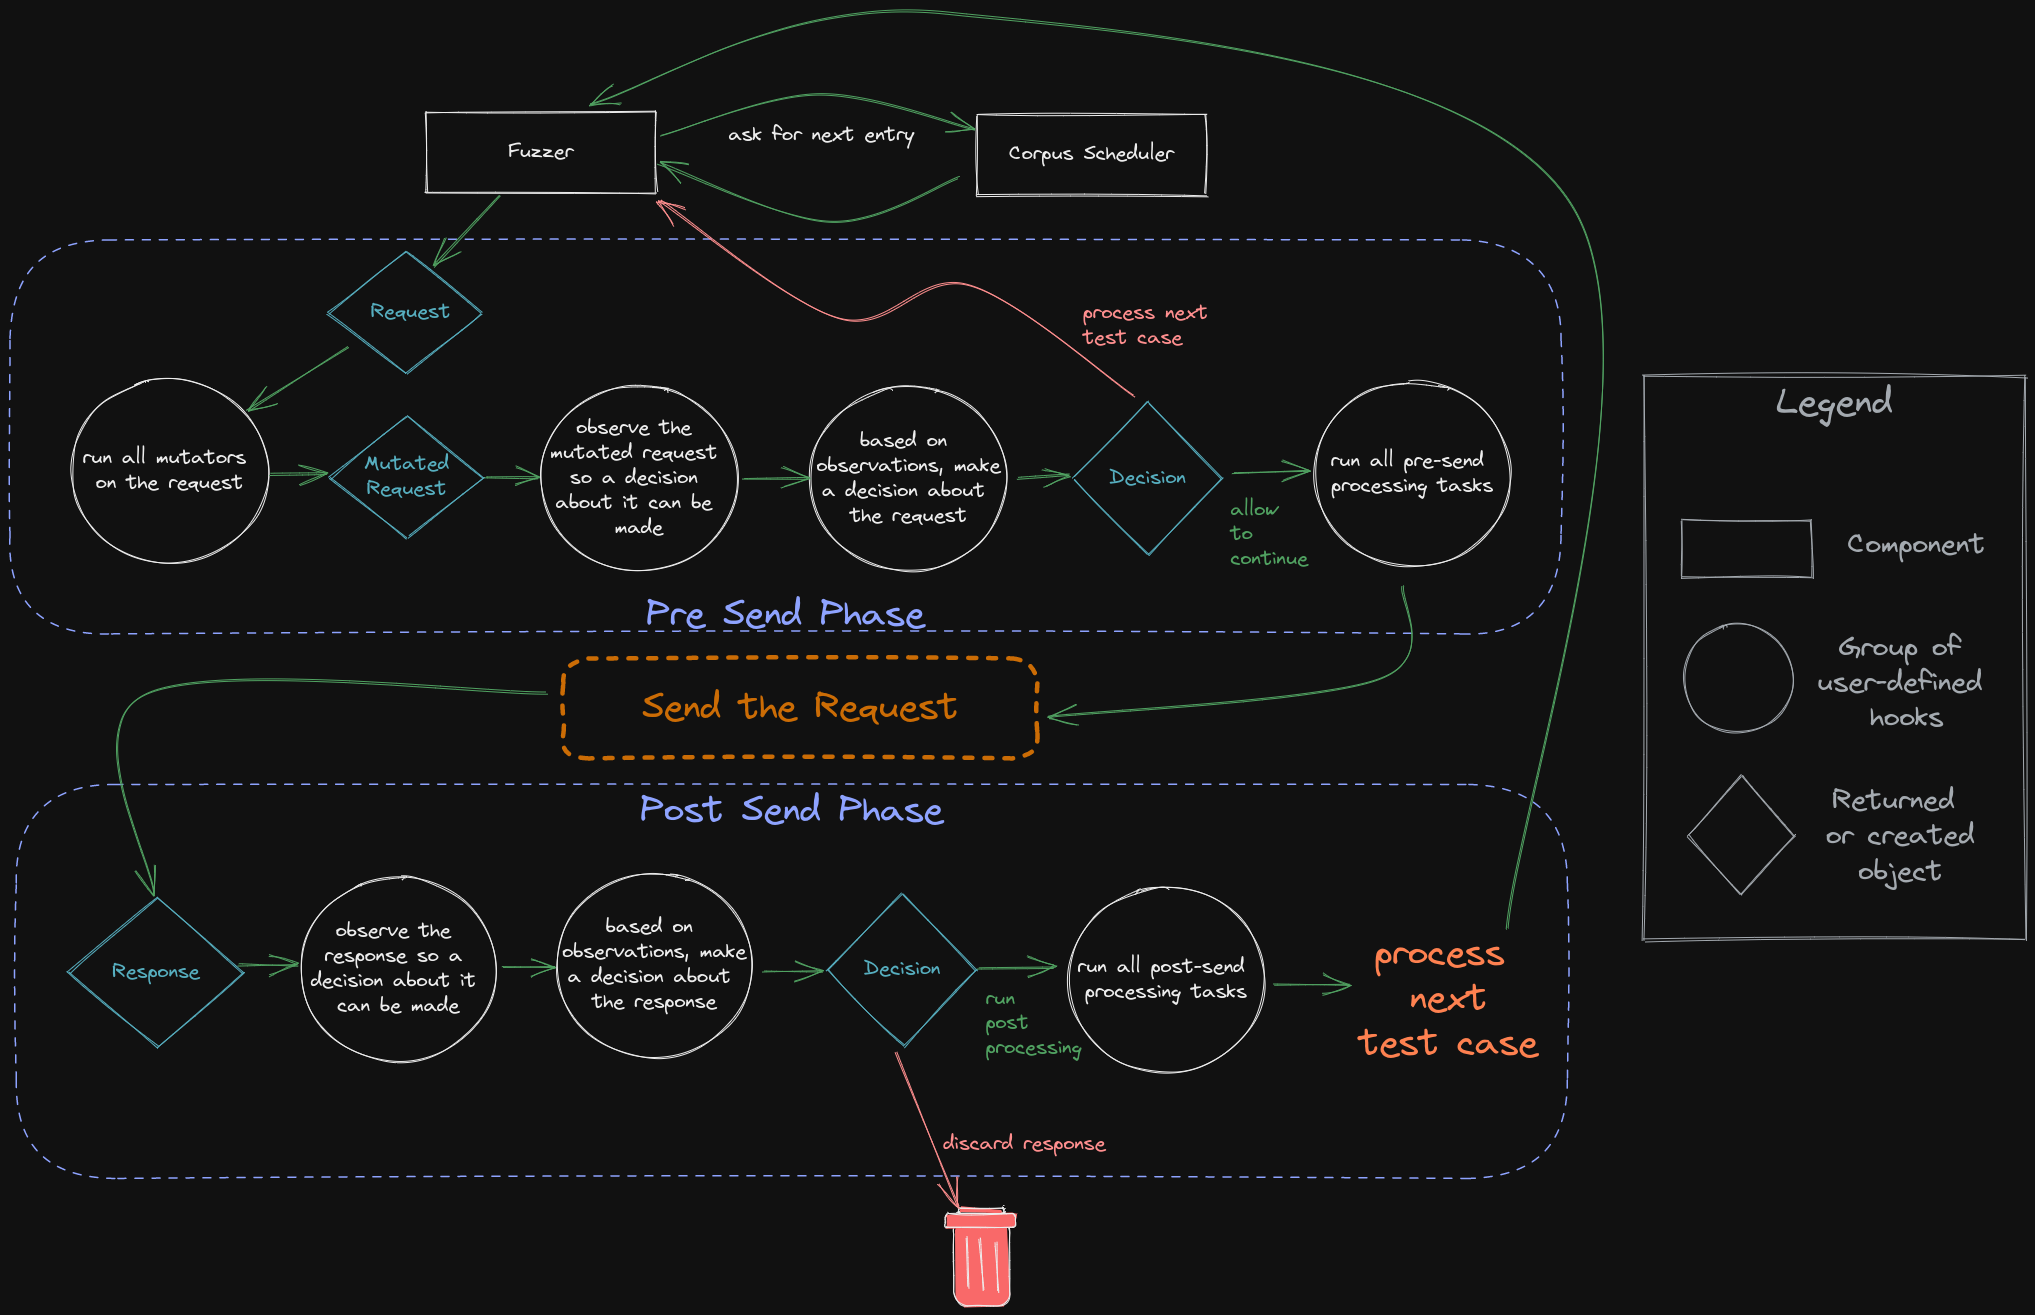 epi052/feroxfuzz
Build structure-aware black-box HTTP fuzzers in Rust with composable mutators, schedulers, observers, deciders, and processors for custom web and API…
 hackinglz/maps_scanner
MAPS cloud scanner and response parser for Microsoft Defender research.
 raz0r/burp-radamsa
Radamsa fuzzer extension for Burp Suite
 d0ge/websocketturbointruder
Burp Suite extension for fuzzing WebSocket messages with custom Python code, supporting multiple engines, HTTP middleware routing, and response…
 0xmarik/aresius
Native HTTP/HTTPS interception proxy for penetration testers and bug bounty hunters with live request tampering, request replay, high-speed fuzzing,…
 bogdanticu88/ratrace
A lightweight CLI tool for systematically detecting and exploiting race conditions in web applications, APIs, and modern services.
 omar2535/graphqler
☸The first ever dependency-aware GraphQL API testing tool!