

API-Wordlist
 net-hunter121/api-wordlist
Curated wordlists of API function names, verbs, and nouns for fuzzing web application endpoints with Burp Suite Intruder.
api-security-testingcurated-resourcesfuzzing+3
254
net-hunter121/api-wordlistCurated wordlists of API function names, verbs, and nouns for fuzzing web application endpoints with Burp Suite Intruder.
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and pentesting toolkit for the terminal built for humans and AI agents alike.
 nicholasaleks/crackql
GraphQL penetration testing tool that exploits weak rate limits and cost analysis to brute-force credentials, bypass 2FA, enumerate users, and fuzz…
 moopinger/smugglefuzz
A rapid HTTP downgrade smuggling scanner written in Go.
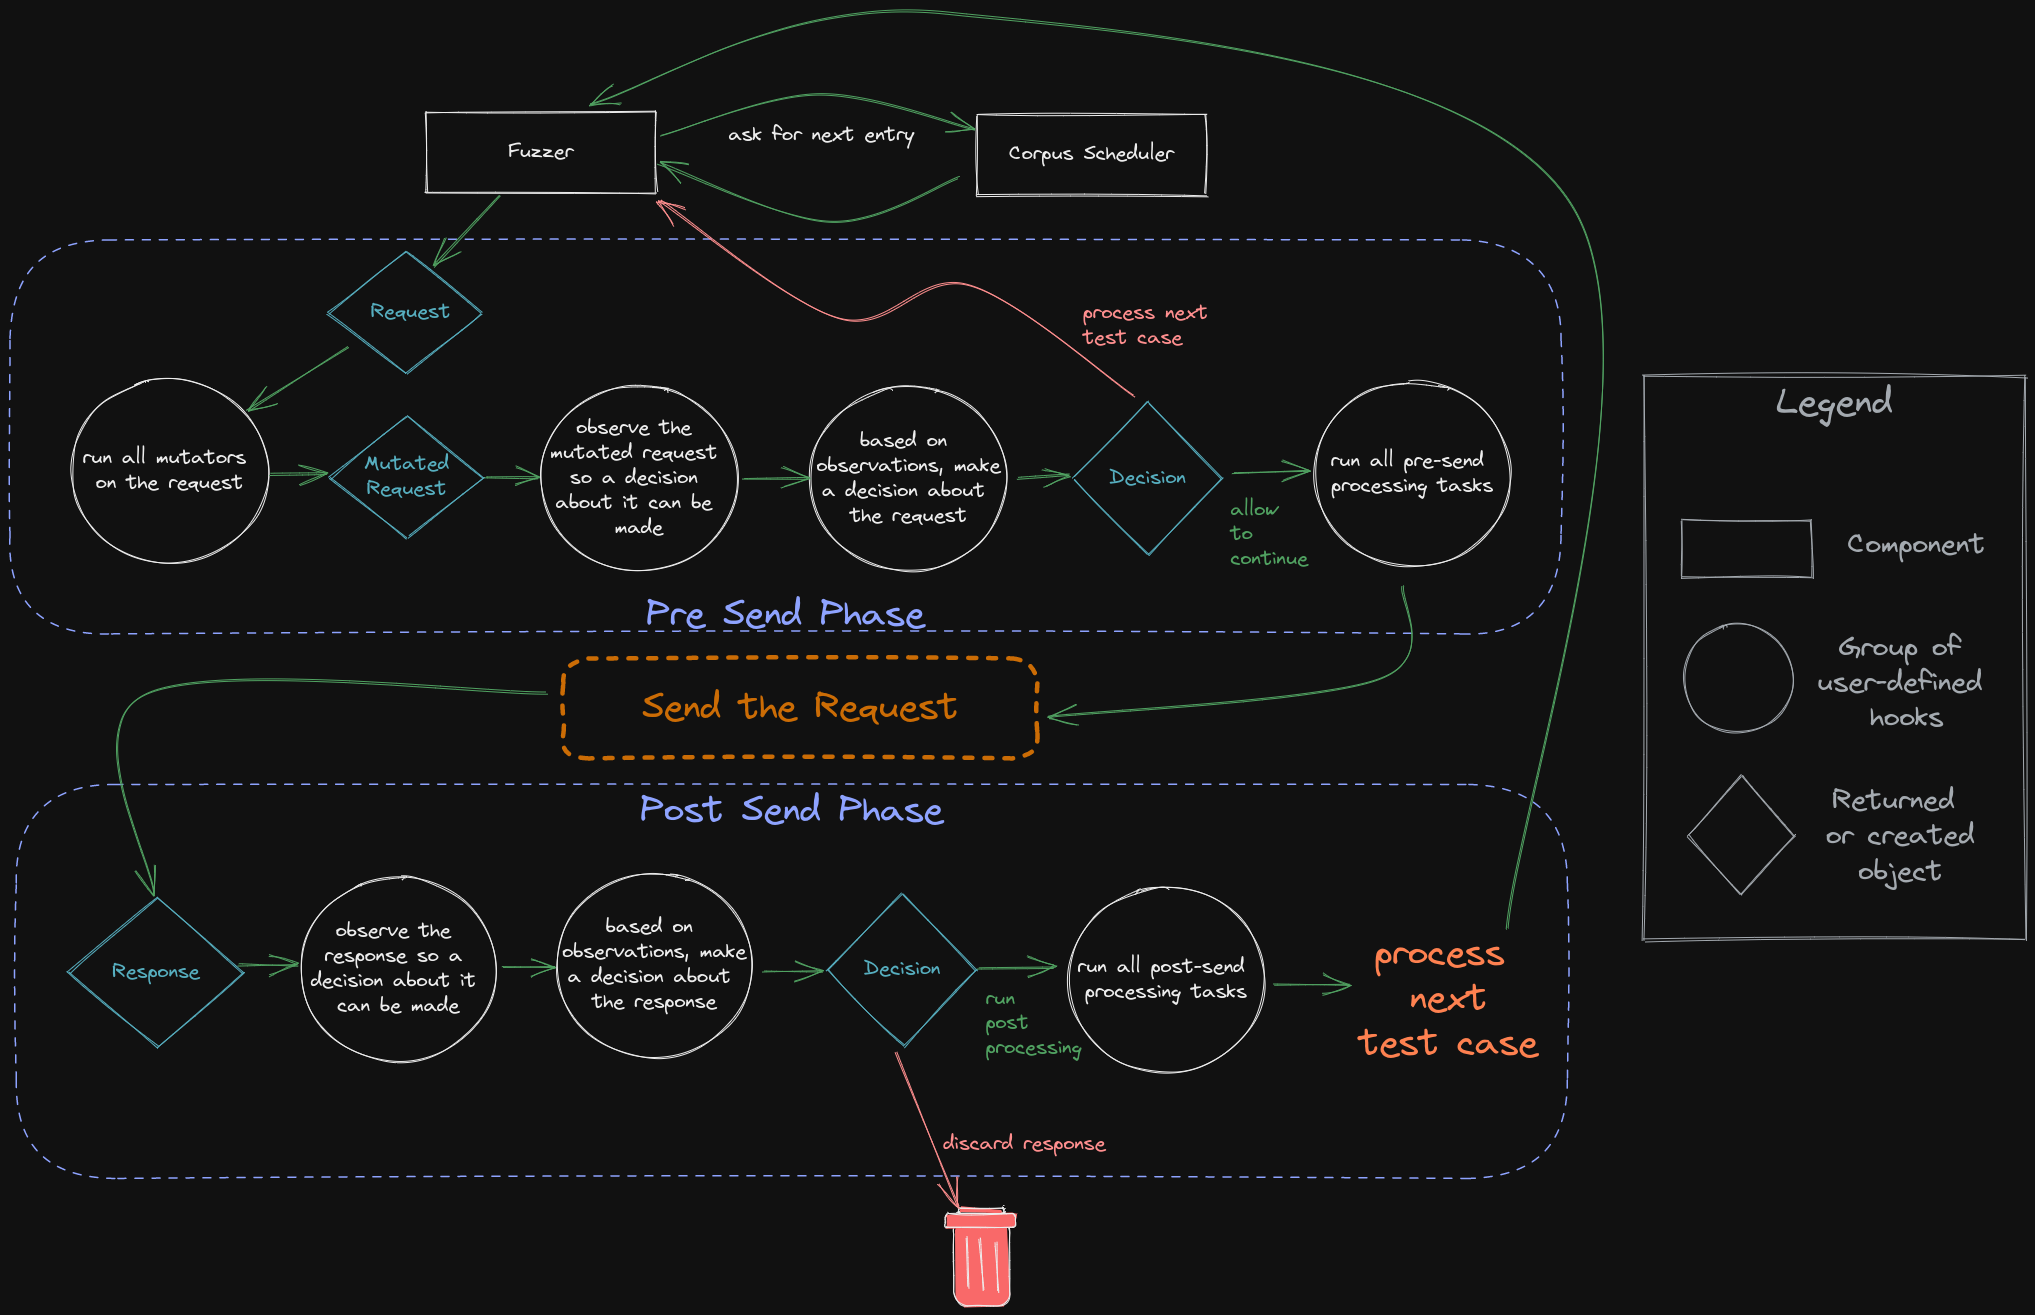 epi052/feroxfuzz
Build structure-aware black-box HTTP fuzzers in Rust with composable mutators, schedulers, observers, deciders, and processors for custom web and API…
 mda2av/http11probe
An open testing platform that probes HTTP/1.1 servers against RFC 9110/9112 requirements, smuggling vectors, and malformed input handling. Add your…
 hackinglz/maps_scanner
MAPS cloud scanner and response parser for Microsoft Defender research.
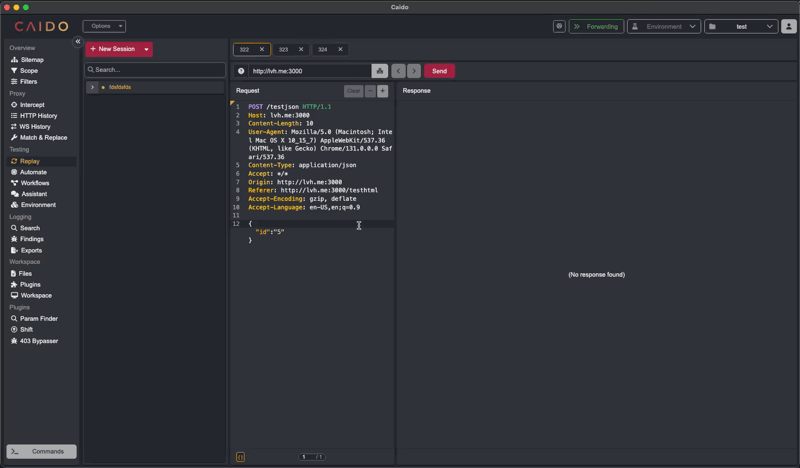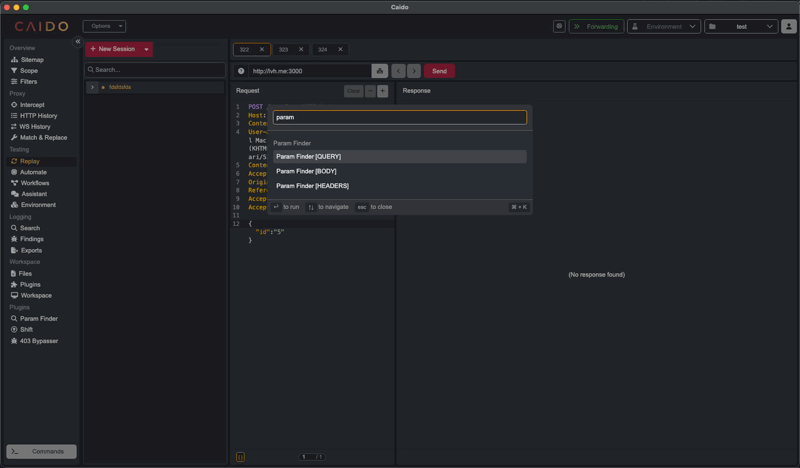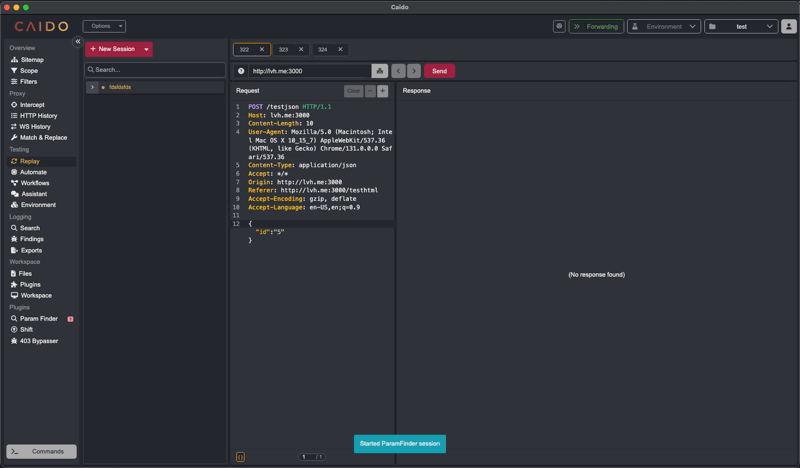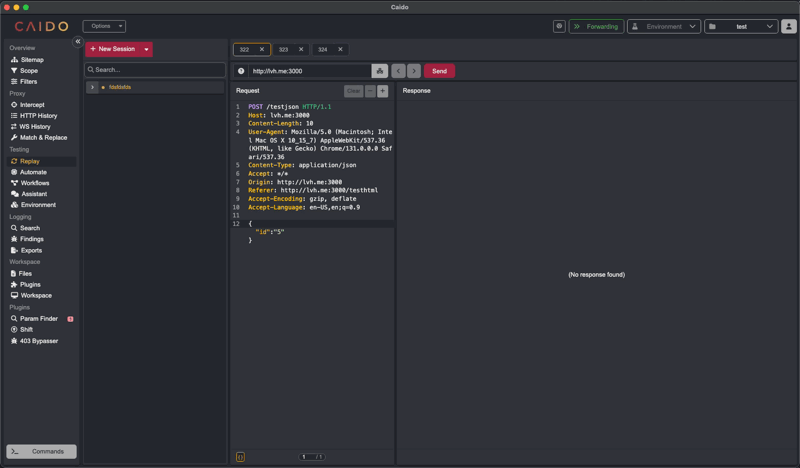 caido-community/paramfinder
Discover hidden parameters in Caido
 raz0r/burp-radamsa
Radamsa fuzzer extension for Burp Suite
 d0ge/websocketturbointruder
Burp Suite extension for fuzzing WebSocket messages with custom Python code, supporting multiple engines, HTTP middleware routing, and response…
 0xmarik/aresius
Native HTTP/HTTPS interception proxy for penetration testers and bug bounty hunters with live request tampering, request replay, high-speed fuzzing,…
 bogdanticu88/ratrace
A lightweight CLI tool for systematically detecting and exploiting race conditions in web applications, APIs, and modern services.
 omar2535/graphqler
☸The first ever dependency-aware GraphQL API testing tool!
 functori/dev/gaia
Global API Integrity Assessor
 openstack-archive/syntribos
Python API security testing tool from OpenStack Security Group
 andreafioraldi/frida-fuzzer
This experimetal fuzzer is meant to be used for API in-memory fuzzing.