
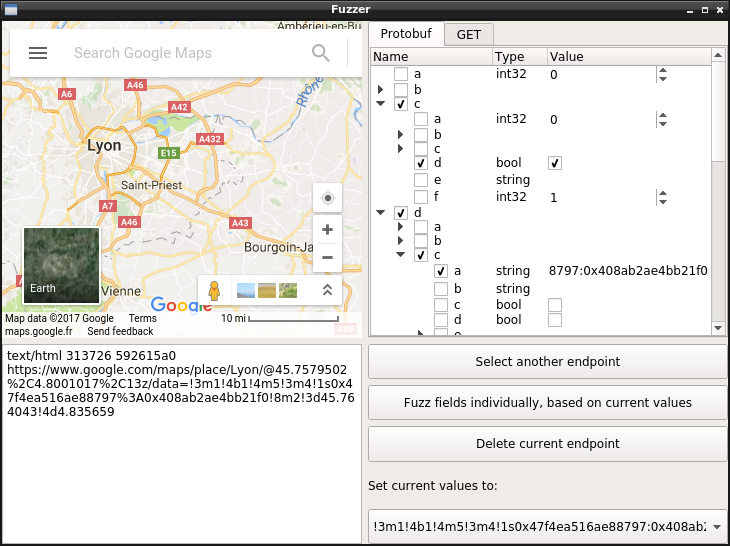
pbtk
 marin-m/pbtk
A toolset for reverse engineering and fuzzing Protobuf-based apps
android-securitybinary-analysisdynamic-analysis-sandboxing+5
marin-m/pbtkA toolset for reverse engineering and fuzzing Protobuf-based apps
 sunblaze-ucb/exploitgym
ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
 0xinfection/tidos-framework
The Offensive Manual Web Application Penetration Testing Framework.
 p0dalirius/coercer
A python script to automatically coerce a Windows server to authenticate on an arbitrary machine through 12 methods.
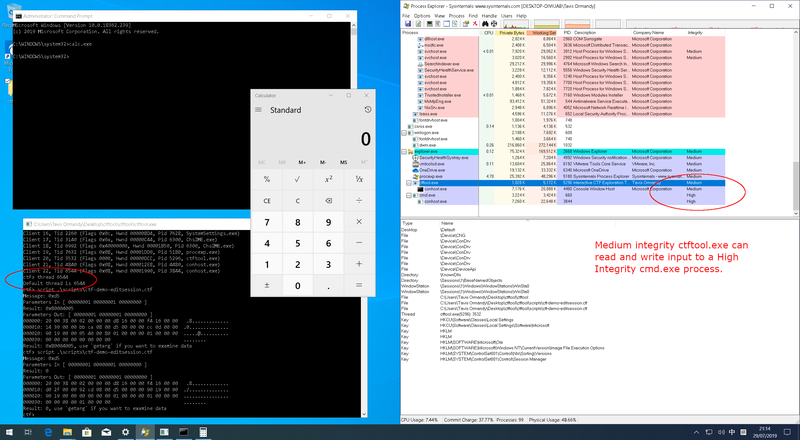 taviso/ctftool
Interactive CTF Exploration Tool
 asciimoo/exrex
Irregular methods on regular expressions

 programa-stic/barf-project
BARF : A multiplatform open source Binary Analysis and Reverse engineering Framework
 bahaabdelwahed/killshot
A Penetration Testing Framework, Information gathering tool & Website Vulnerability Scanner
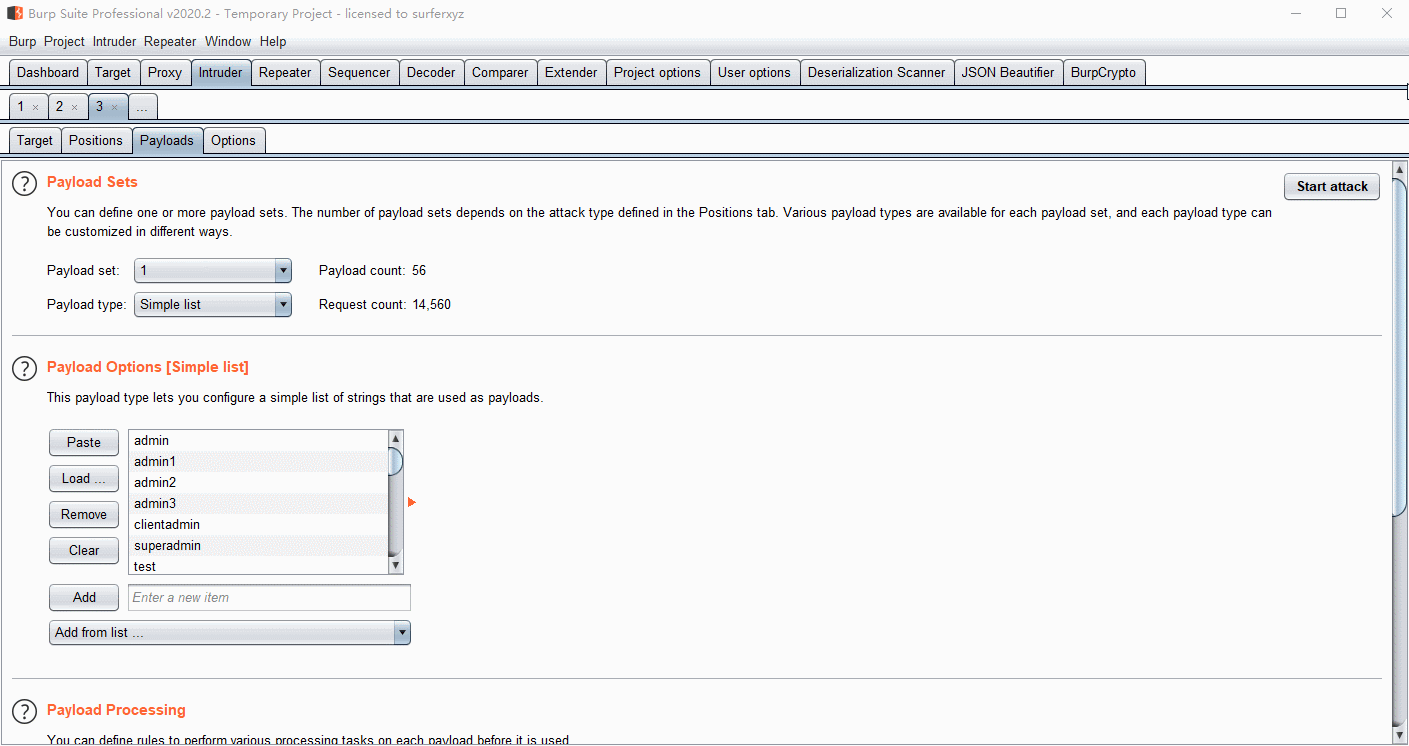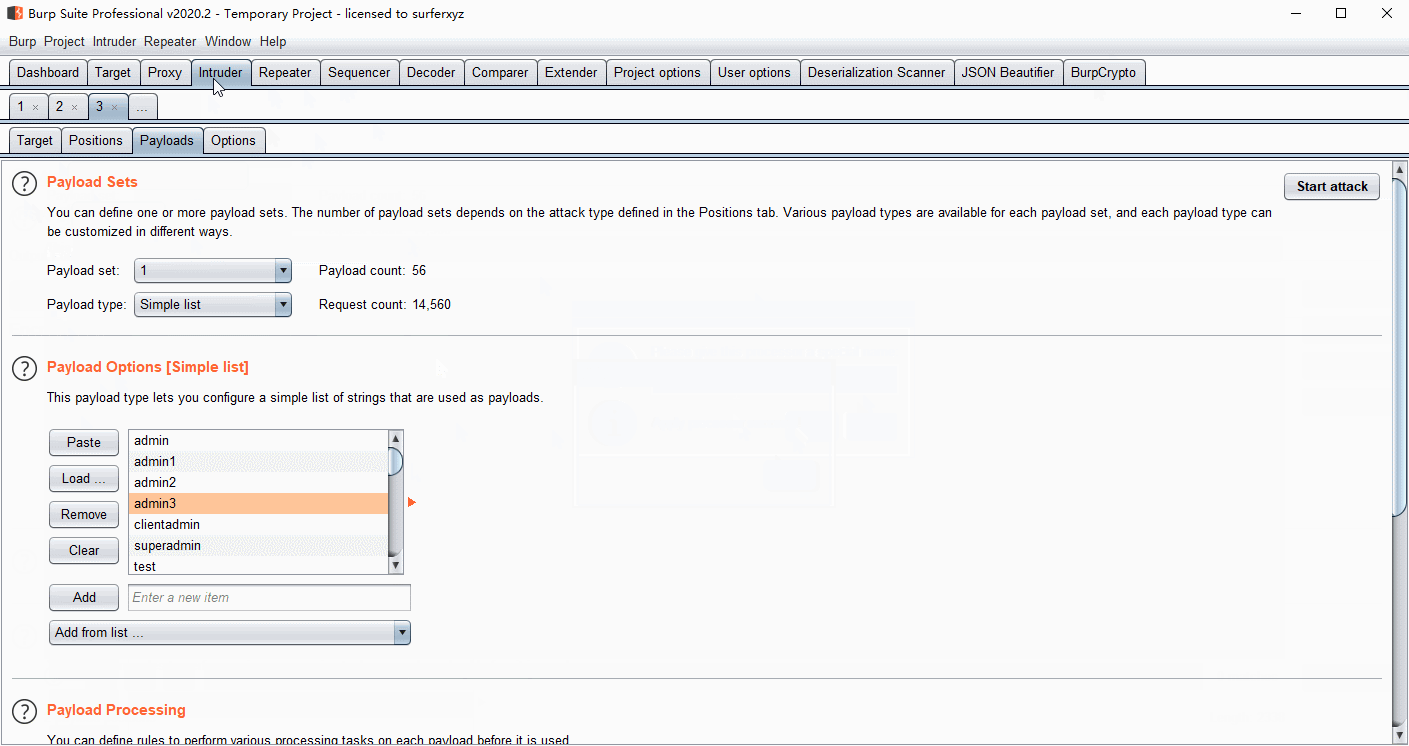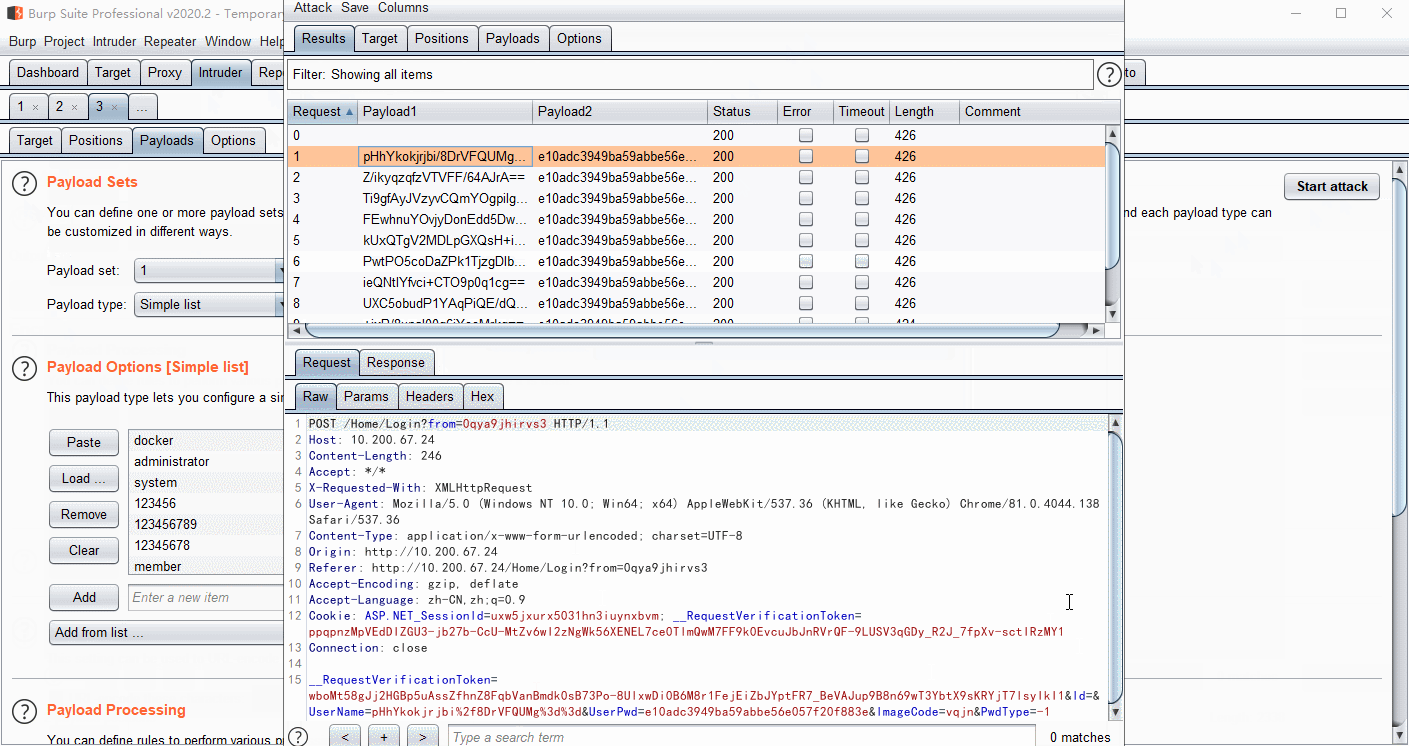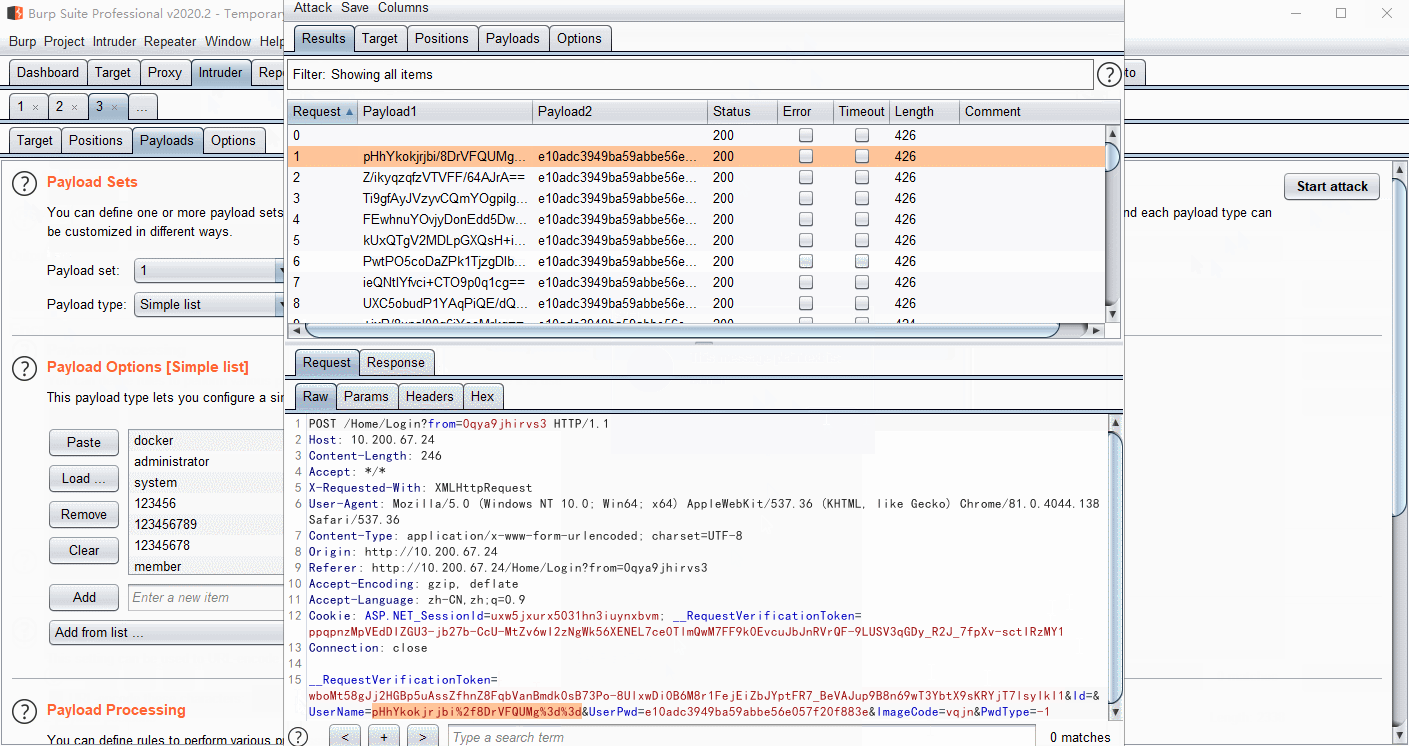 whwlsfb/burpcrypto
BurpSuite plugin for encrypting payloads with AES, RSA, DES, or custom JS code, enabling automated decryption of front-end encrypted traffic during…
 overspace-labs/caa
BurpSuite plugin for HTTP packet analysis and fuzzing dictionary generation. Extracts parameters, paths, and files from requests, counts frequency,…
 x3omdax/penbox
PenBox - A Penetration Testing Framework - The Tool With All The Tools , The Hacker's Repo
 openrce/paimei
A reverse engineering framework written in Python.
 kagancapar/cve-2022-29072
7-Zip through 21.07 on Windows allows privilege escalation and command execution when a file with the .7z extension is dragged to the Help>Contents…
 0xacb/recollapse
Black-box regex fuzzing tool that generates payloads to bypass input validations, discover normalizations, and evade WAFs in web applications.
 kmkz/exploits
Original CVEs, exploit PoCs, and security advisories with detailed vulnerability chains, privilege escalation, and container escape techniques for…