
BootStomp
 ucsb-seclab/bootstomp
BootStomp: a bootloader vulnerability finder
android-securitybinary-analysisexploitation+3
ucsb-seclab/bootstompBootStomp: a bootloader vulnerability finder
 parallelbeings/cve-2019-14079
USB device fuzzing on Android Phone
 devrodt2/cve-2026-28609-matroska-pcm-oob
Proof-of-concept and instrumented reproduction harness for CVE-2026-28609, an out-of-bounds write in Android's MatroskaExtractor reachable via a…
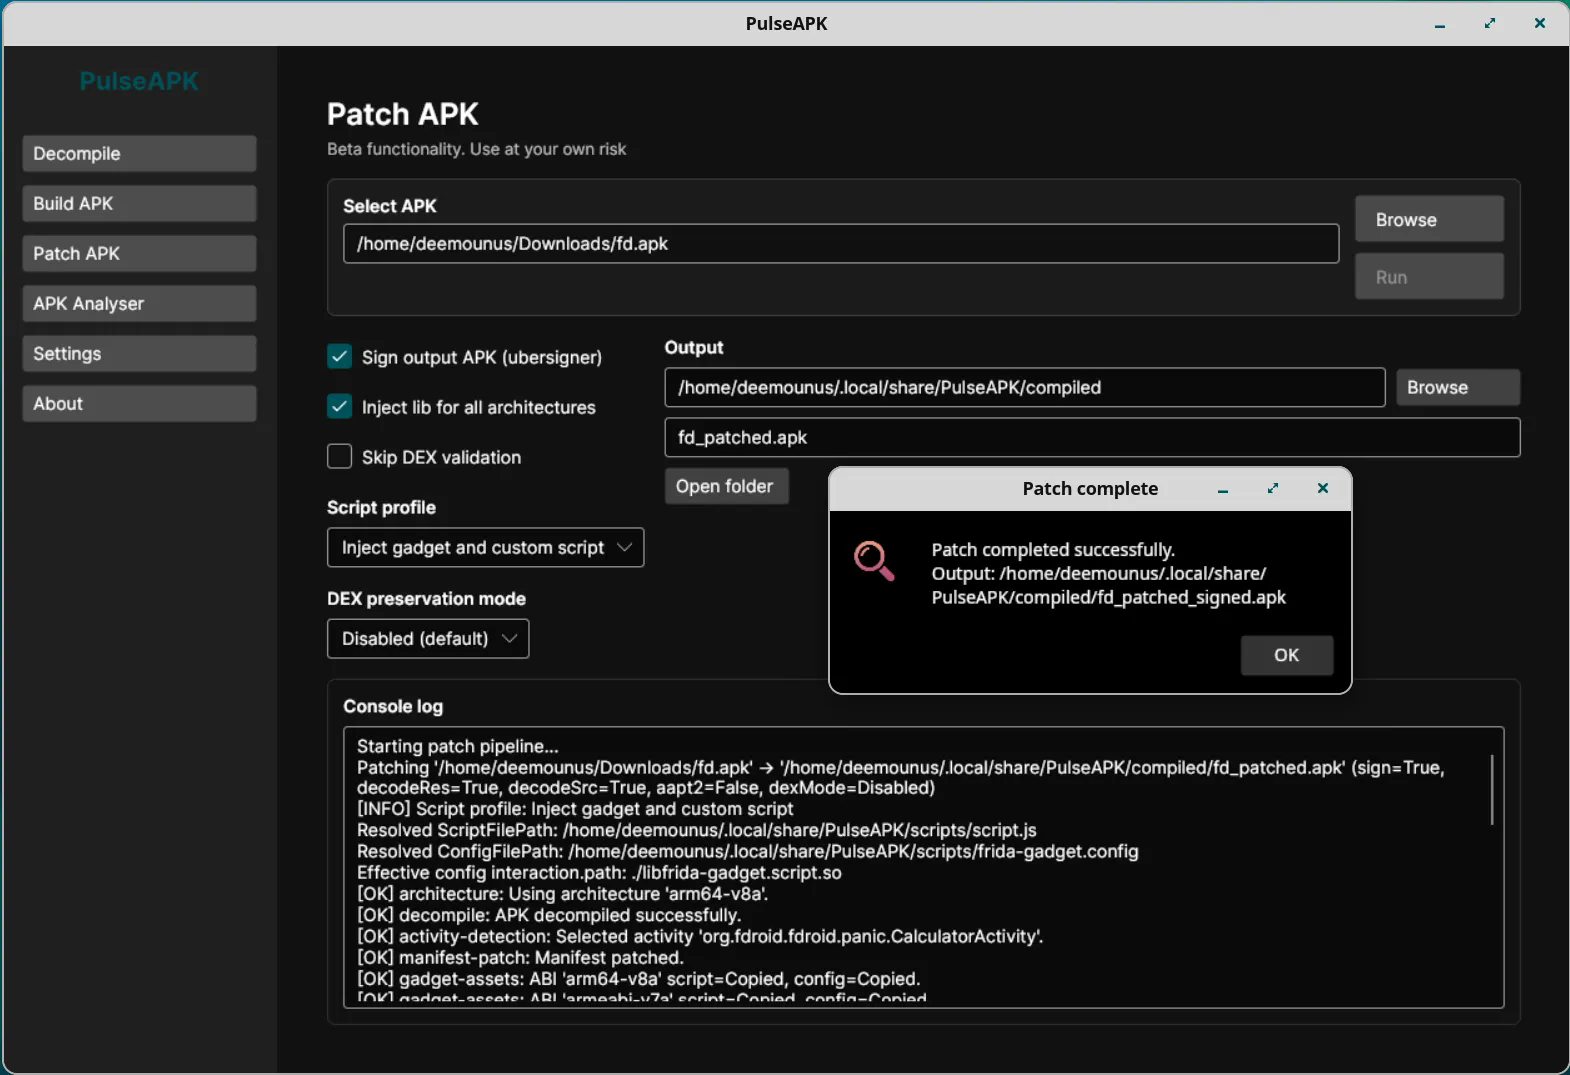 deemoun/pulseapk-core
PulseAPK Core: Cross-Platform tool for working with APK files: Decompilation, Analysis, Building
 flankerhqd/cve-2015-6620-poc
POC for CVE-2015-6620, AMessage unmarshal arbitrary write
 cleov2/debuggable-app-exploit
CVE-2024-31317 Debuggable App Exploit
 boredpentester/abl_rop
Experimenting with CVE-2022-20120 (Pixel Bootloader / ABL) using Unicorn, derived from eShard's emulator at…
 r3n3r0/cve-2026-27280
In-depth analysis and proof-of-concept for CVE-2026-27280, an out-of-bounds write in Adobe DNG SDK's dng_render_task::ProcessArea, reachable via…
 zx41r/awesome-reverse-engineering-and-malware-analysis
A verified map of reverse engineering and malware analysis. Disassemblers, unpacking, exploit dev, fuzzing, DFIR, and the deep-cut writeups other…
 vmoranv/jshookmcp
A search-first, profile-aware reverse-engineering workspace for AI agents — 735 tools across 36 domains in one MCP server.
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 aflplusplus/libafl
Advanced Fuzzing Library - Slot your Fuzzer together in Rust! Scales across cores and machines. For Windows, Android, MacOS, Linux, no_std, ...
 googleprojectzero/jackalope
Binary, coverage-guided fuzzer for Windows, macOS, Linux and Android
 abrarkhan/external_sonivox_cve-2024-23709
Proof-of-concept for CVE-2024-23709, an out-of-bounds write vulnerability in Android's Sonivox audio synthesis library, demonstrating exploitation on…
 pazhanivelmani/webp_android10_r33_cve-2023-1999
Proof-of-concept exploit for CVE-2023-1999 targeting the WebP codec library on Android 10 (r33). Demonstrates a heap buffer overflow vulnerability in…
 qilingframework/qiling
A True Instrumentable Binary Emulation Framework