
e9patch
 gjduck/e9patch
A powerful static binary rewriting tool
binary-analysisbinary-exploitationfuzzing+1
gjduck/e9patchA powerful static binary rewriting tool
 aflplusplus/libafl
Advanced Fuzzing Library - Slot your Fuzzer together in Rust! Scales across cores and machines. For Windows, Android, MacOS, Linux, no_std, ...
 emrekybs/draculaos
Dracula OS is a Linux operating system meticulously designed for OSINT (Open Source Intelligence) and Cyber Intelligence missions.
 bobfuzzer/cve-2019-18885
Proof-of-concept for a null pointer dereference in the Linux kernel BTRFS filesystem (CVE-2019-18885), including a crafted image, reproduction steps,…
 0vercl0k/wtf
Distributed, code-coverage guided snapshot-based fuzzer for user and kernel-mode targets on Windows and Linux, with emulator and hypervisor backends.
 fysac/cve-2019-20326
Heap buffer overflow in GNOME gThumb and Linux Mint Pix
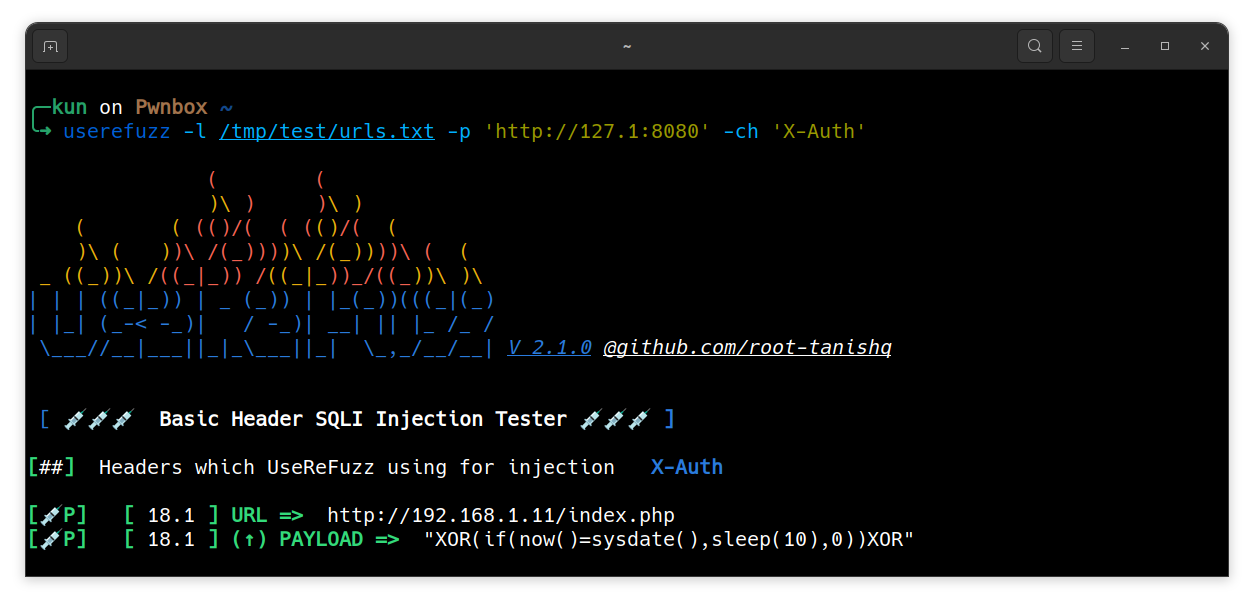 root-tanishq/userefuzz
User-Agent , X-Forwarded-For and Referer SQLI Fuzzer
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 ww9210/cve-2017-7374
Proof-of-concept exploit for CVE-2017-7374, triggering a vulnerability in ext4 filesystem encryption via crafted directory operations on Linux.
 microsoft/restler-fuzzer
RESTler is the first stateful REST API fuzzing tool for automatically testing cloud services through their REST APIs and finding security and…
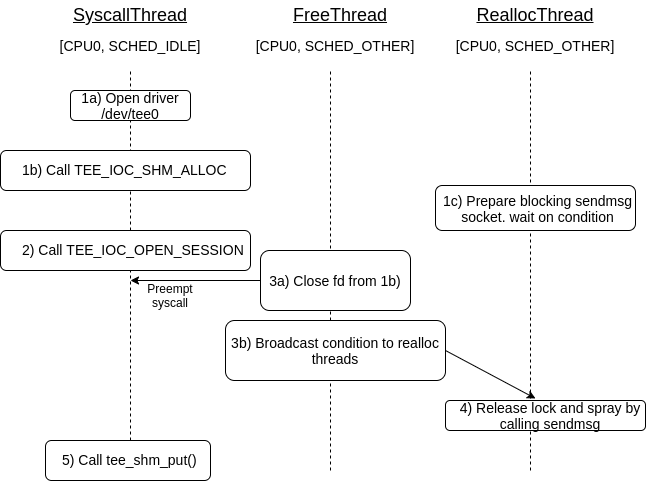 pjlantz/optee-qemu
Environment with vulnerable kernel for exploitation of the TEE driver (CVE-2021-44733)
 erikdervishi03/cve-2026-31024
Proof of Concept (PoC) for a stack-based buffer overflow in Steghide 0.5.1. Demonstrates how long file paths trigger a crash (DoS) and leak sensitive…
 cao-wuhui/cve-2025-69720
Advisory for CVE-2025-69720: stack-based buffer overflow in GNU ncurses infocmp (CWE-121)
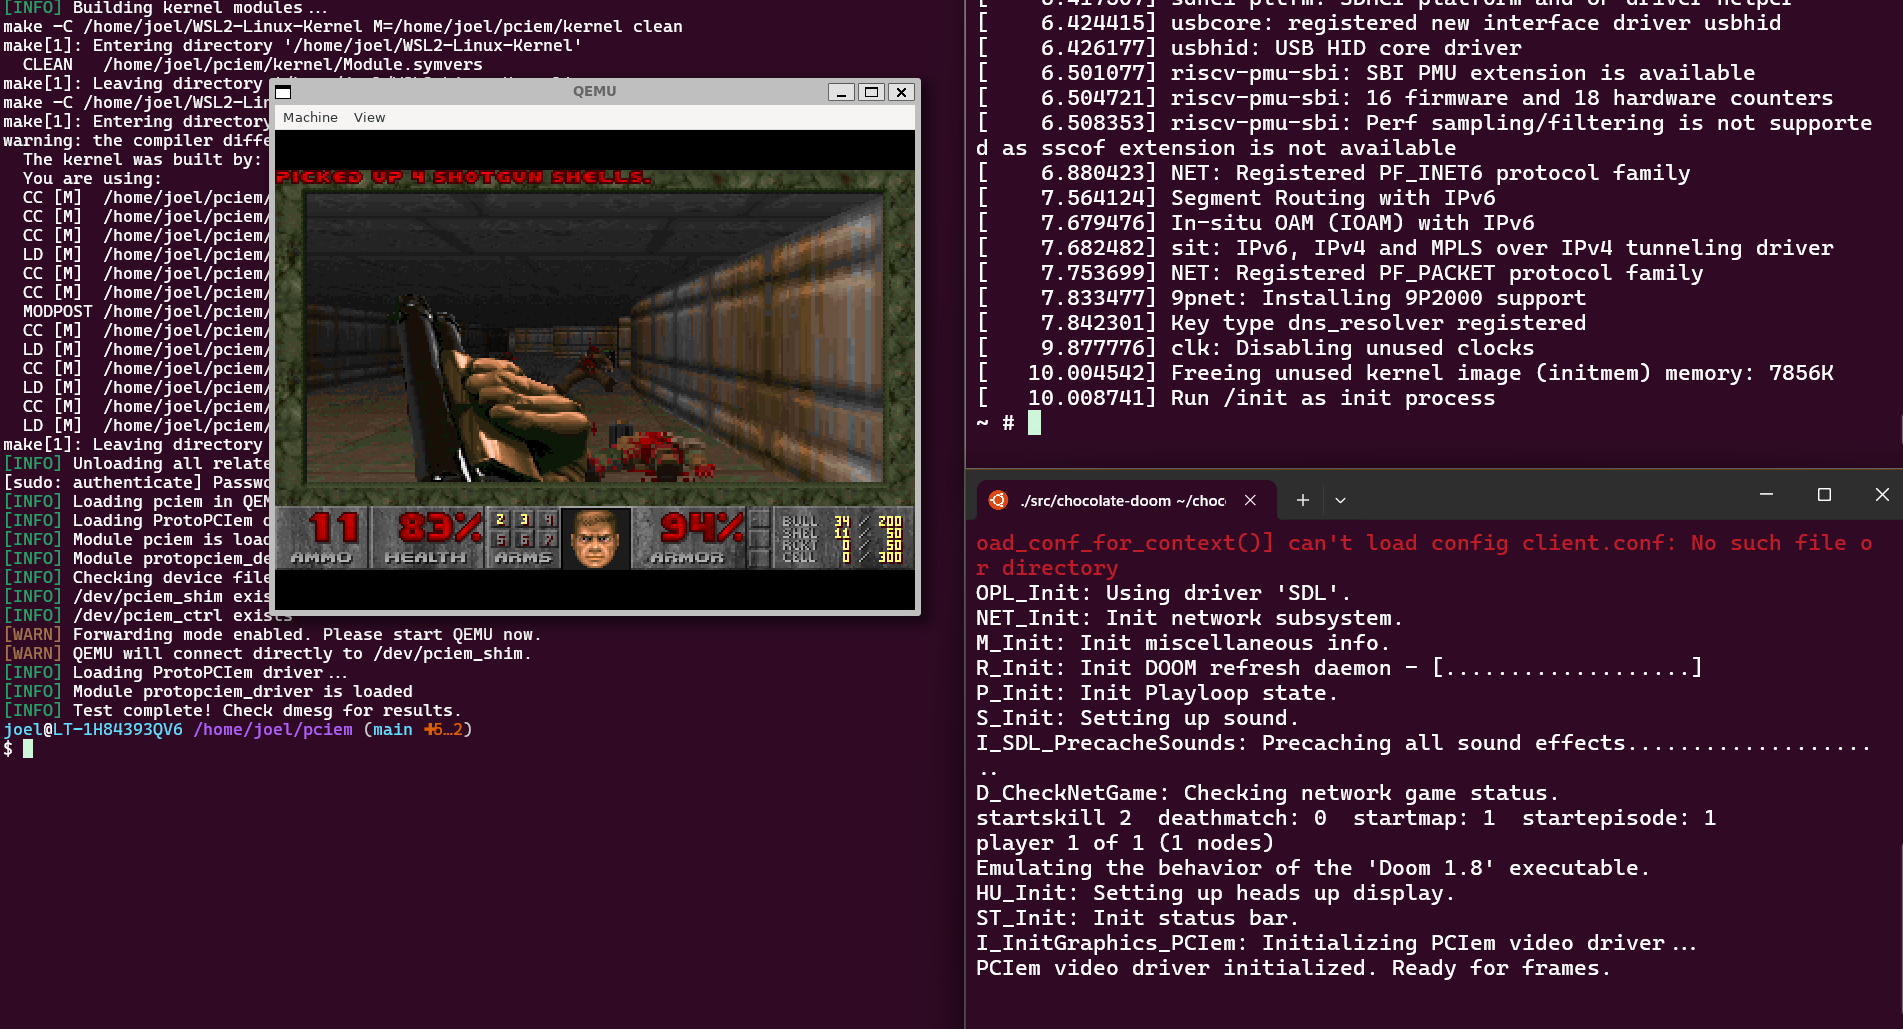 cakehonolulu/pciem
A Linux framework to enable userspace-defined "Virtual" PCIe card shims to enable in-host PCIe card driver development.
 mxmssh/drafl
AFL + DynamoRIO = fuzzing binaries with no source code on Linux
 foxirain/linux-kernel-codex-harness
Evidence-driven Linux kernel vulnerability research harness used in the investigation of CVE-2026-31720
 abubakar-shahid/cve-2024-36886
Academic research on N-Day Linux kernel vulnerabilities, analyzing CVE-2024-36886 in the TIPC networking subsystem, lifecycle, impact, and mitigation…