external_expact_AOSP10_r33_CVE-2022-25314

C library for parsing XML, providing stream-oriented parsing with handler registration, supporting UTF-16 encoding, and including a reference manual.

C library for parsing XML, providing stream-oriented parsing with handler registration, supporting UTF-16 encoding, and including a reference manual.

CVE-2017-9608 analysis


C library for parsing XML, patched for CVE-2022-25315, providing stream-oriented XML parsing with handlers for efficient document processing.


General-purpose data compression library implementing the zlib, deflate, and gzip formats, with thread-safe functions and cross-platform build…

Private end-to-end sanitizer reproduction package for six GDCM findings

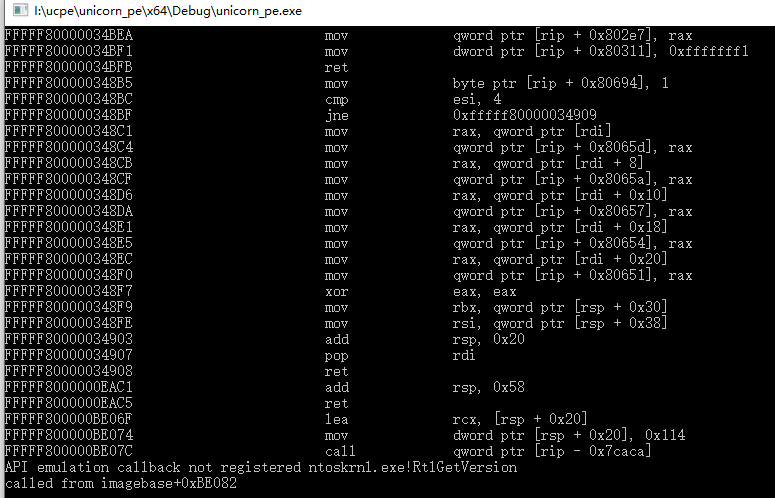
Emulates Windows PE execution using Unicorn engine for malware analysis, unpacking packed binaries, and decrypting VMProtect strings and imports.

Exhaustive differential validation of all 4.3B AArch64 instruction encodings.


Symbolic execution tool

Static Binary Instrumentation tool for Windows x64 executables

Standalone PoC for CVE-2026-90782: status-clobbering NULL dereference in S2OPC alloc_notification_message_items() (DataChange fails, Event succeeds)

Proof of concept for CVE-2021-24086, a NULL dereference in tcpip.sys triggered remotely.

Runtime libc function auditor that detects file access race conditions and symlink vulnerabilities by hooking filesystem syscalls via LD_PRELOAD,…