

SSTImap
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
code-analysiscommand-and-controldynamic-code-analysis+6
vladko312/sstimapAutomatic SSTI detection tool with interactive interface
 owasp/offat
Automated API security testing tool that generates tests from OpenAPI specs, fuzzes inputs, and checks for OWASP API Top 10 vulnerabilities including…
 trailofbits/manticore
Symbolic execution tool
 zeze-zeze/ioctlance
A tool that is used to hunt vulnerabilities in x64 WDM drivers
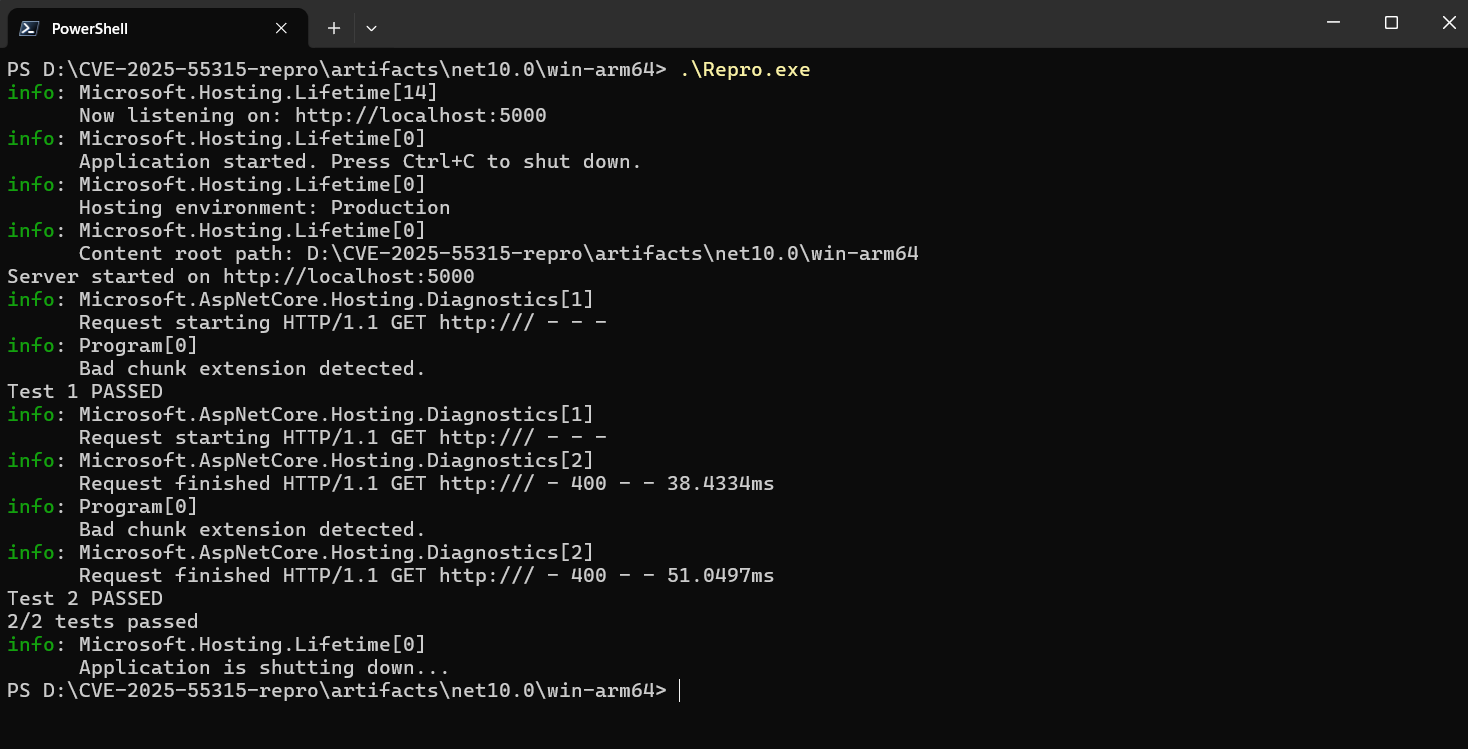 sirredbeard/cve-2025-55315-repro
Tool that reproduces CVE-2025-55315 in ASP.NET Core.
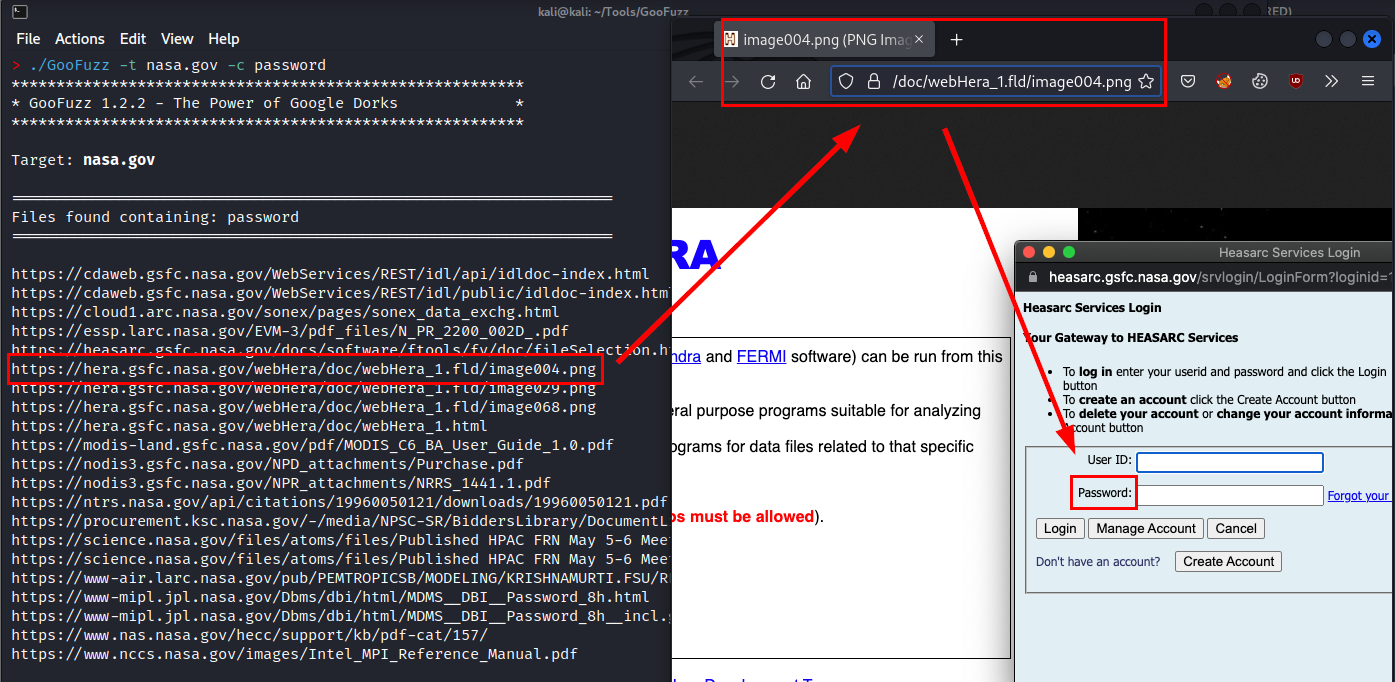 m3n0sd0n4ld/goofuzz
Bash-based fuzzing tool that leverages Google Dorking for stealthy enumeration of directories, files, subdomains, and parameters without direct…
 asciimoo/exrex
Irregular methods on regular expressions
 0xacb/recollapse
Black-box regex fuzzing tool that generates payloads to bypass input validations, discover normalizations, and evade WAFs in web applications.
 s0md3v/arjun
HTTP parameter discovery tool that finds valid query parameters for URL endpoints using a large dictionary, supporting GET/POST/JSON/XML requests,…
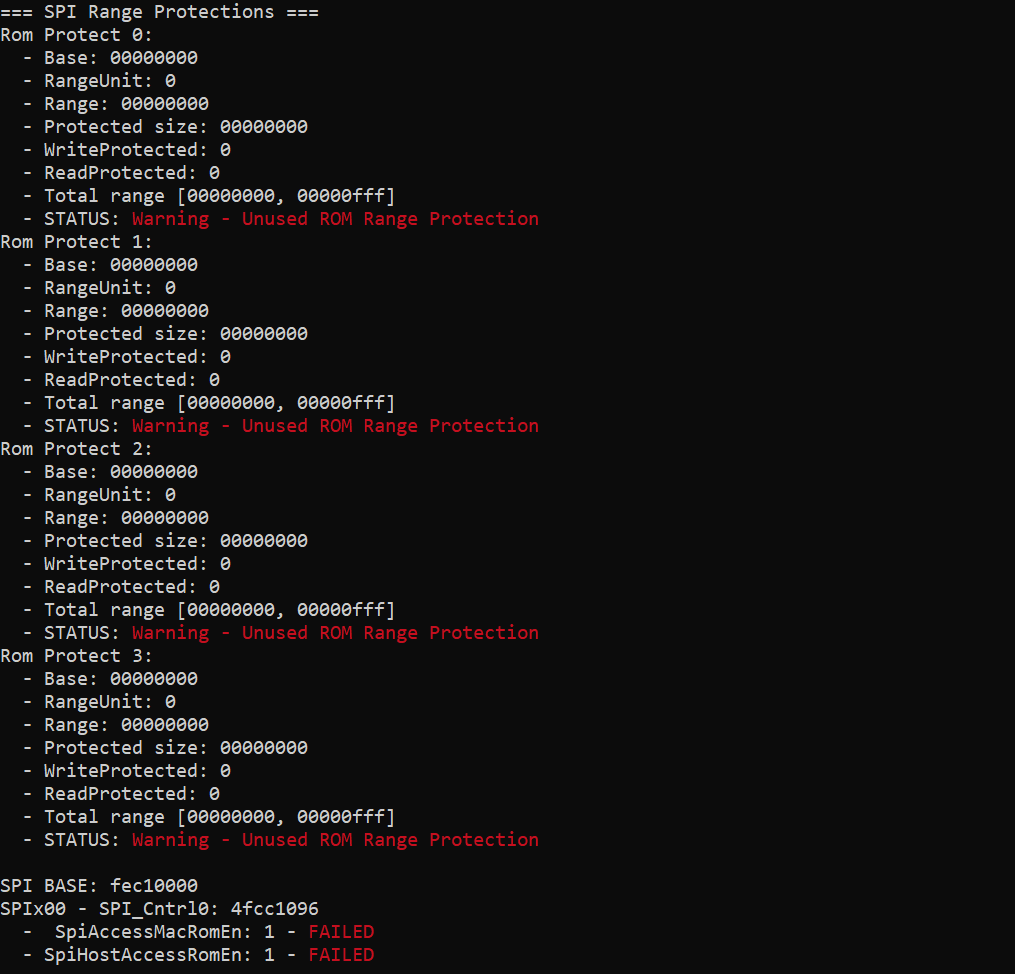 ioactive/platbox
Platform security assessment tool for dumping and analyzing UEFI/SMM registers, PCI config space, physical memory, SPI flash, and S3 bootscripts with…
 pwnwriter/kanha
🦚 A web-app pentesting suite written in rust .
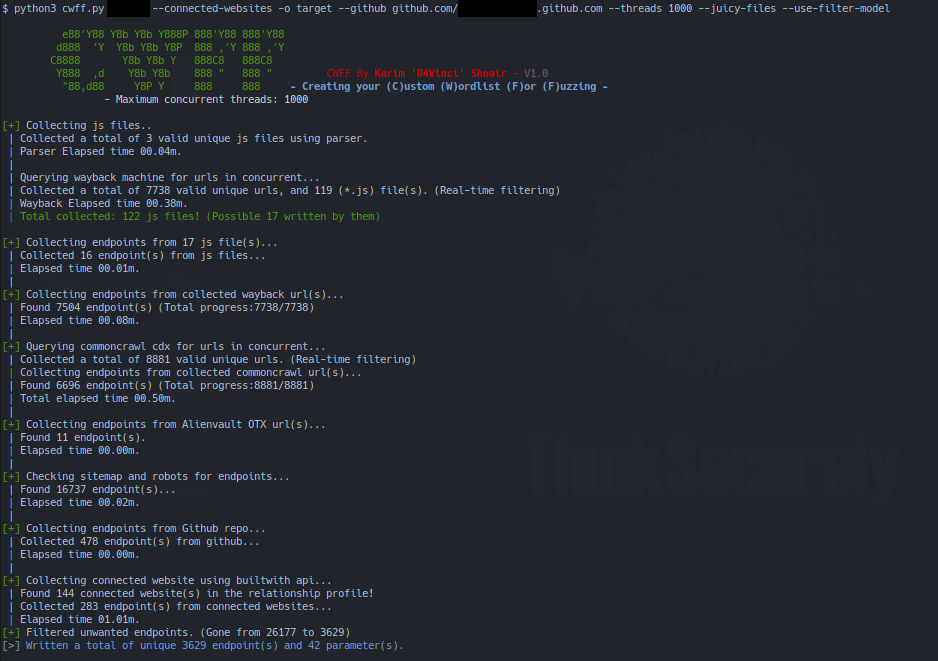 d4vinci/cwff
Create your Custom Wordlist For Fuzzing
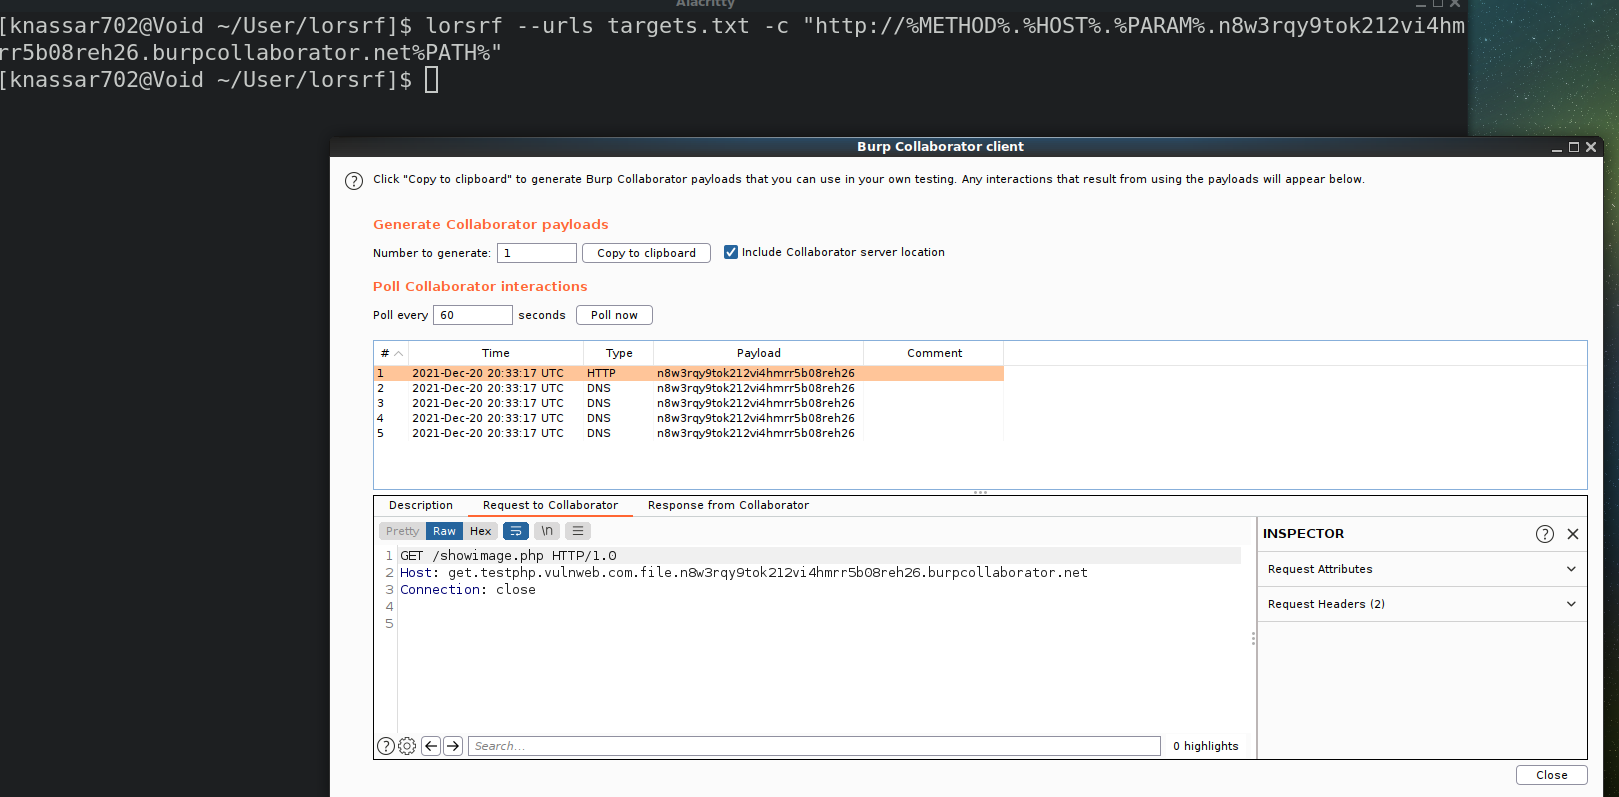 mindpatch/lorsrf
Fast CLI tool to find the parameters that can be used to find SSRF or Out-of-band resource load :artificial_satellite: :crab:
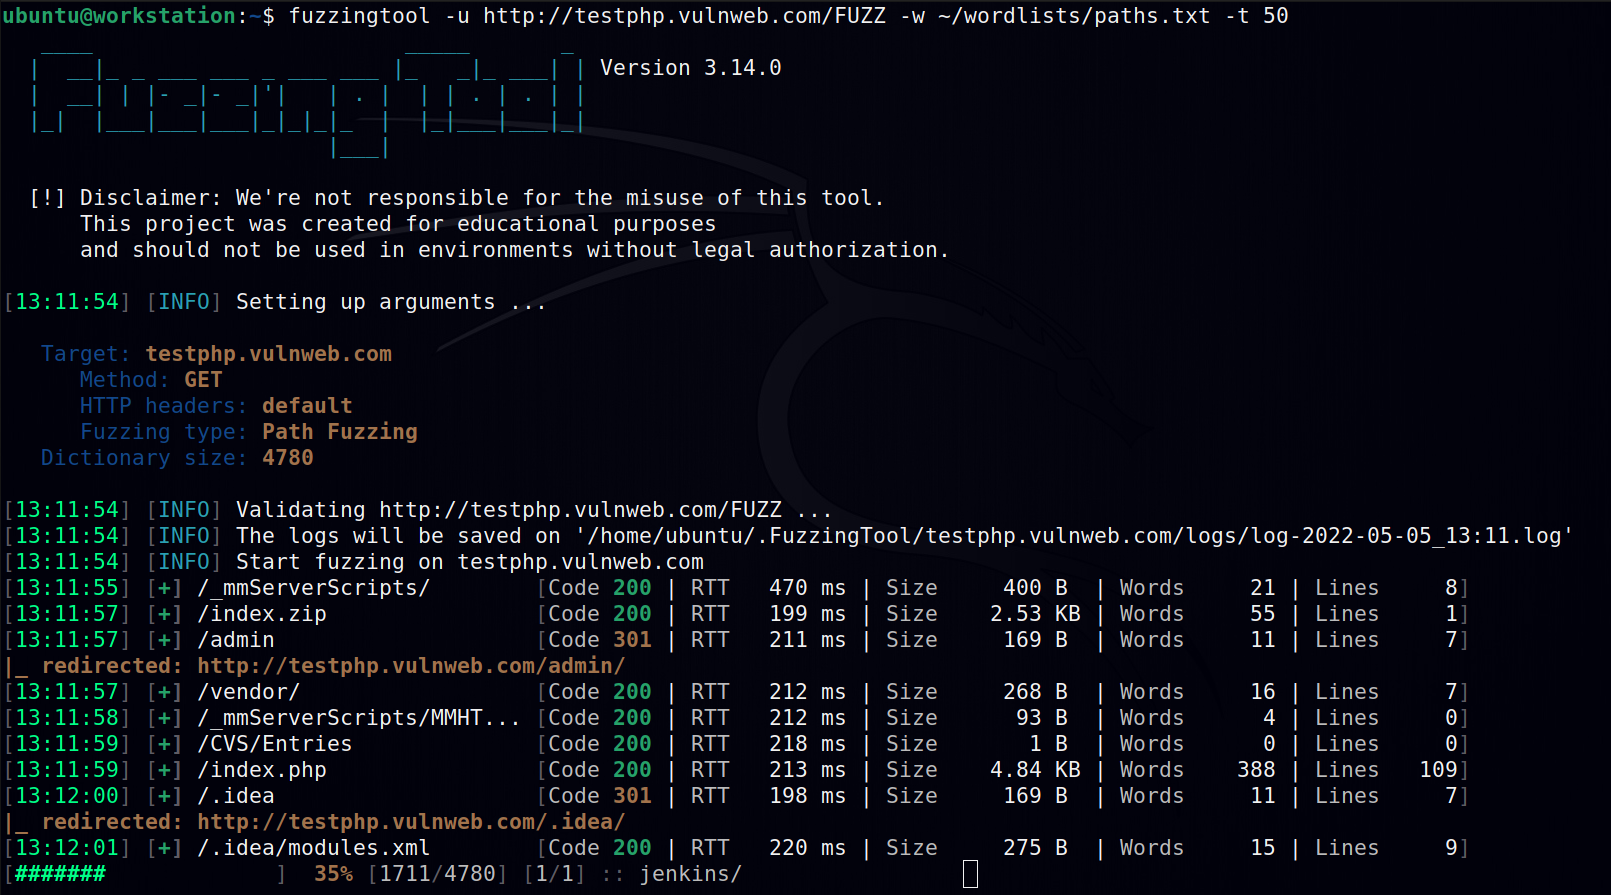 nescau-ufla/fuzzingtool
Software for fuzzing, used on web application pentestings.
 trinadh465/external_zlib_cve-2022-37434
General-purpose data compression library implementing the zlib, deflate, and gzip formats, with thread-safe functions and cross-platform build…
 musana/fuzzuli
Domain-aware URL fuzzer that dynamically generates wordlists to discover exposed backup and sensitive files on web servers.
 nicholasaleks/crackql
GraphQL penetration testing tool that exploits weak rate limits and cost analysis to brute-force credentials, bypass 2FA, enumerate users, and fuzz…
 rapiddns/afuzz
Automated web path fuzzing tool that detects hidden directories, files, and endpoints using intelligent language detection, blacklist/whitelist…