

pentest-mcp
 dmontgomery40/pentest-mcp
NOT for educational purposes: An MCP server for professional penetration testers including STDIO/HTTP/SSE support, nmap, go/dirbuster, nikto, JtR,…
exploitationfuzzingnetwork-mapping+8
150
dmontgomery40/pentest-mcpNOT for educational purposes: An MCP server for professional penetration testers including STDIO/HTTP/SSE support, nmap, go/dirbuster, nikto, JtR,…
 yuatemycat/superghidra
Python toolkit accelerating Ghidra with a cached daemon, ARM64 P-code lifting, Z3 equivalence proofs, GPU-accelerated scanning, binary diffing, and…
 marin-m/pbtk
A toolset for reverse engineering and fuzzing Protobuf-based apps
 google/syzkaller
Unsupervised coverage-guided kernel fuzzer for Linux and major OS kernels; automatically discovers security vulnerabilities through intelligent…
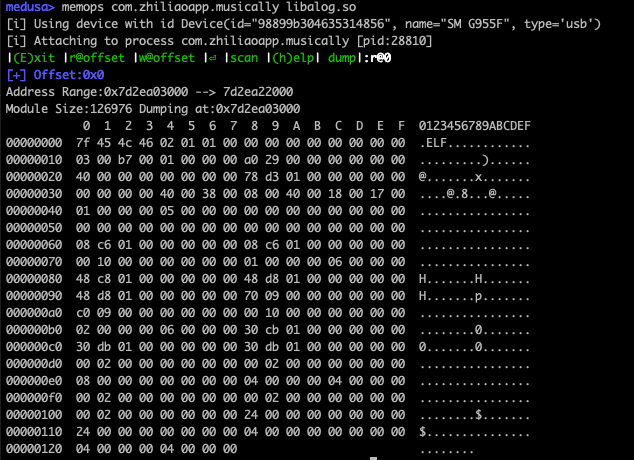 ch0pin/medusa
Mobile Edge-Dynamic Unified Security Analysis
 reversenseorg/dexcalibur
[Official] Android reverse engineering tool focused on dynamic instrumentation automation leveraging Frida. It disassembles dex, analyzes it…
 firerpa/lamda
Android Full-Stack Device Control Platform: WebRTC/H.264 remote desktop, UI/OCR/image-matching automation, one-click MITM, built-in Frida,…
 devrodt2/cve-2026-28609-matroska-pcm-oob
Proof-of-concept and instrumented reproduction harness for CVE-2026-28609, an out-of-bounds write in Android's MatroskaExtractor reachable via a…
 r3n3r0/cve-2026-27280
In-depth analysis and proof-of-concept for CVE-2026-27280, an out-of-bounds write in Adobe DNG SDK's dng_render_task::ProcessArea, reachable via…
 0xinfection/logmepwn
A fully automated, reliable, super-fast, scanning and validation toolkit for the Log4J RCE CVE-2021-44228 vulnerability.
 sharif-bot-cmd/quantum-silicon-core-loader
Executes at the silicon boundary
 robertcprice/ncpu
Research runtime for differentiable neural computers, GPU-based CPU emulation, and program synthesis. Features neural ALU, constant-time crypto, JEPA…
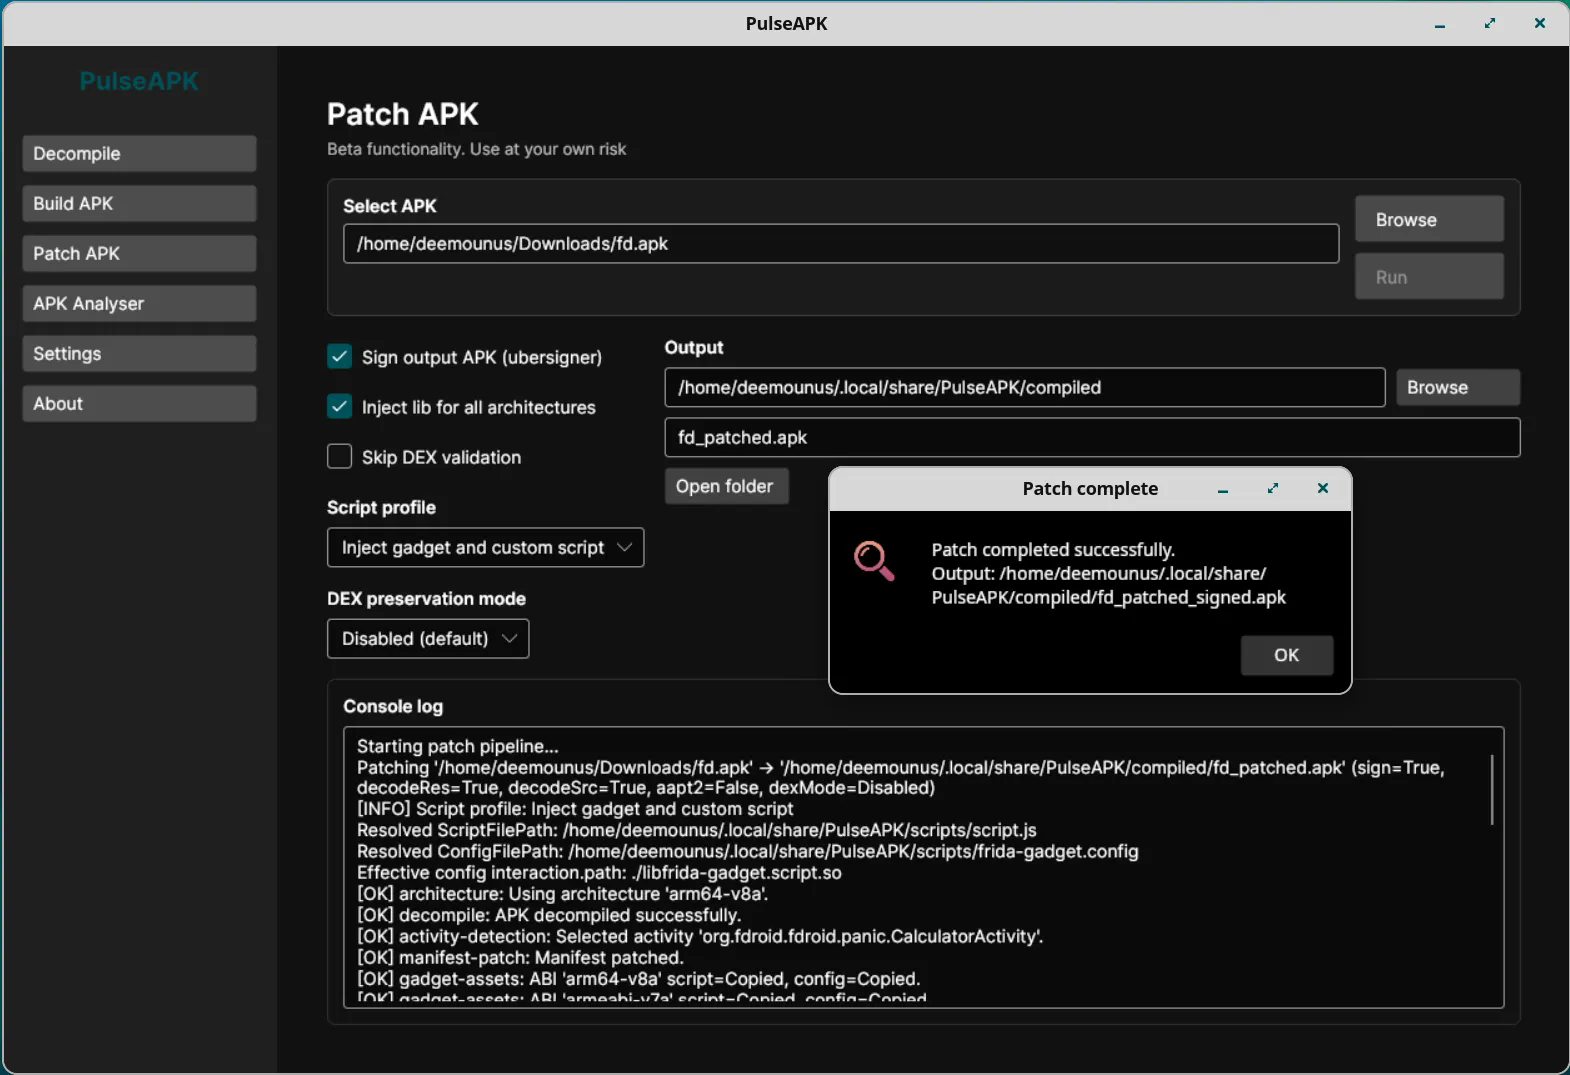 deemoun/pulseapk-core
PulseAPK Core: Cross-Platform tool for working with APK files: Decompilation, Analysis, Building
 m0bilesecurity/rms-runtime-mobile-security
Runtime Mobile Security (RMS) 📱🔥 - is a powerful web interface that helps you to manipulate Android and iOS Apps at Runtime
 0xbbdd/cve-2026-33317
Proof-of-concept for CVE-2026-33317, an out-of-bounds write in OP-TEE PKCS#11 TA, demonstrating Secure World heap corruption via a malformed…
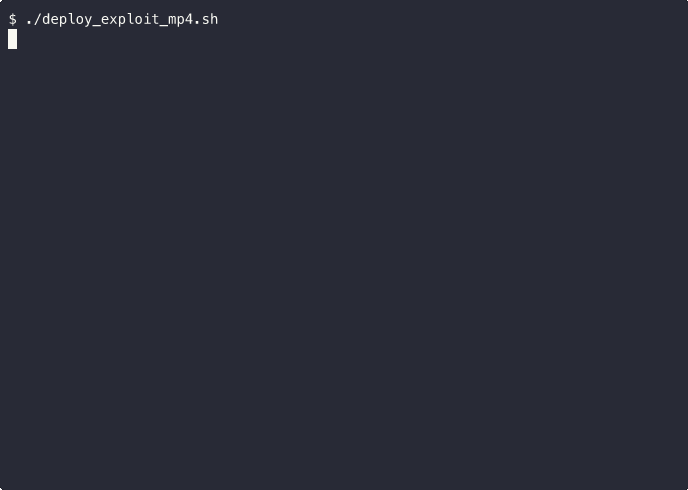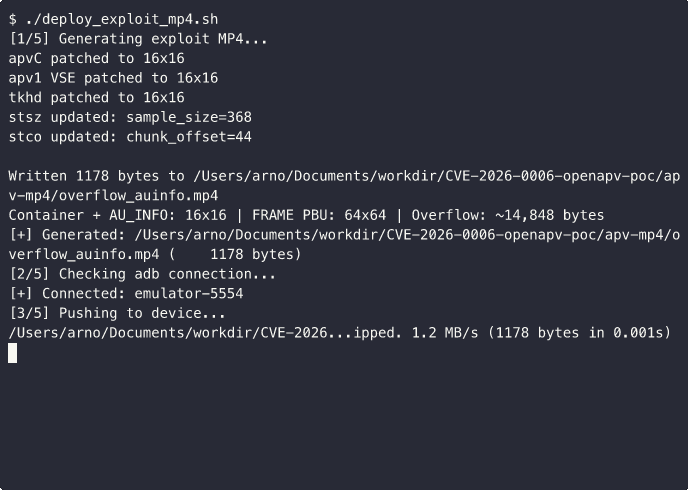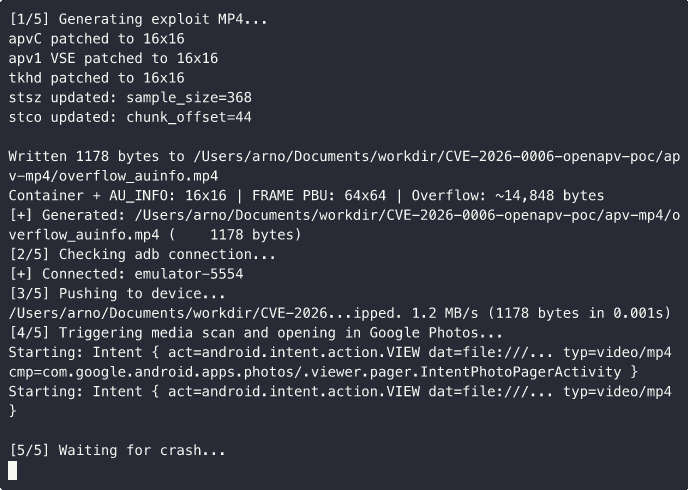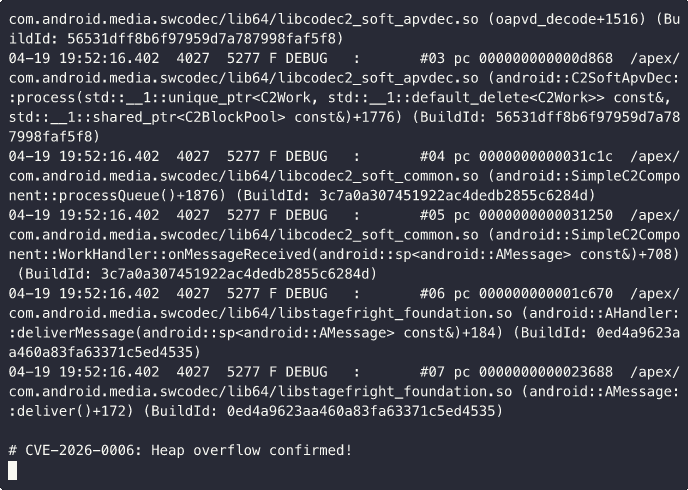 mobilehackinglab/cve-2026-0006-openapv-poc
CVE-2026-0006: Heap buffer overflow PoC for libopenapv (Android APV codec) - CVSS 9.8
 0xbbdd/cve-2022-46152
CVE-2022-46152: Improper Validation of Array Index in the `cleanup_shm_refs' function.
 cleov2/debuggable-app-exploit
CVE-2024-31317 Debuggable App Exploit