

 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
 bishopfox/joro
A collaborative web exploitation framework.
 jvbotelho/cve-2026-69243-poc-aiohttp-smuggling
Reproduces aiohttp CWE-444 request smuggling via rejected WebSocket upgrades, with Python/Rust payloads and Docker lab demonstrating proxy…
 fraunhofer-aisec/gallia
Extendable pentesting framework for automotive UDS interfaces, enabling reproducible scans, diagnostic trouble code reading, and post-processing via…
 agampreet-singh/redroot
RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…
 bahaabdelwahed/killshot
A Penetration Testing Framework, Information gathering tool & Website Vulnerability Scanner
 grp-ops/react2shell
Lightweight scanner and Nuclei templates for identifying React and Next.js deserialization RCEs (CVE-2025-55182 / CVE-2025-66478).
 0xacb/recollapse
Black-box regex fuzzing tool that generates payloads to bypass input validations, discover normalizations, and evade WAFs in web applications.
 jesusprubio/bluebox
A collection of exploits for different VoIP products.
 domienschepers/wifi-framework
Wi-Fi Framework for creating proof-of-concepts, automated experiments, test suites, fuzzers, and more.
 pedrib/poc
Advisories, proof of concept files and exploits that have been made public by @pedrib.
 shipcod3/cantot
quick and dirty canbus h4xing framework
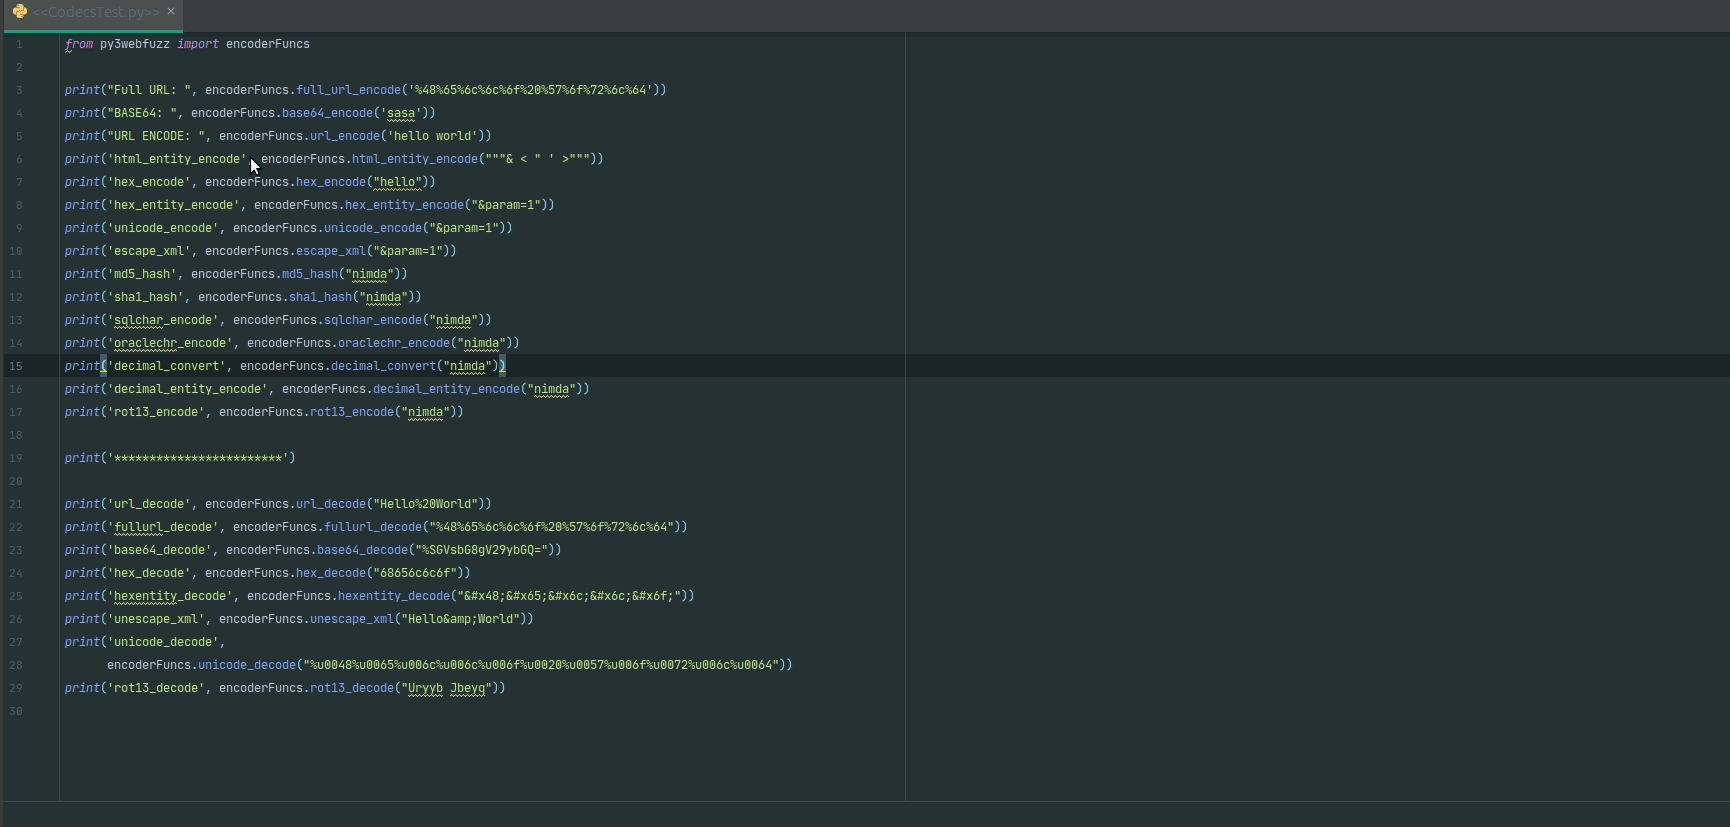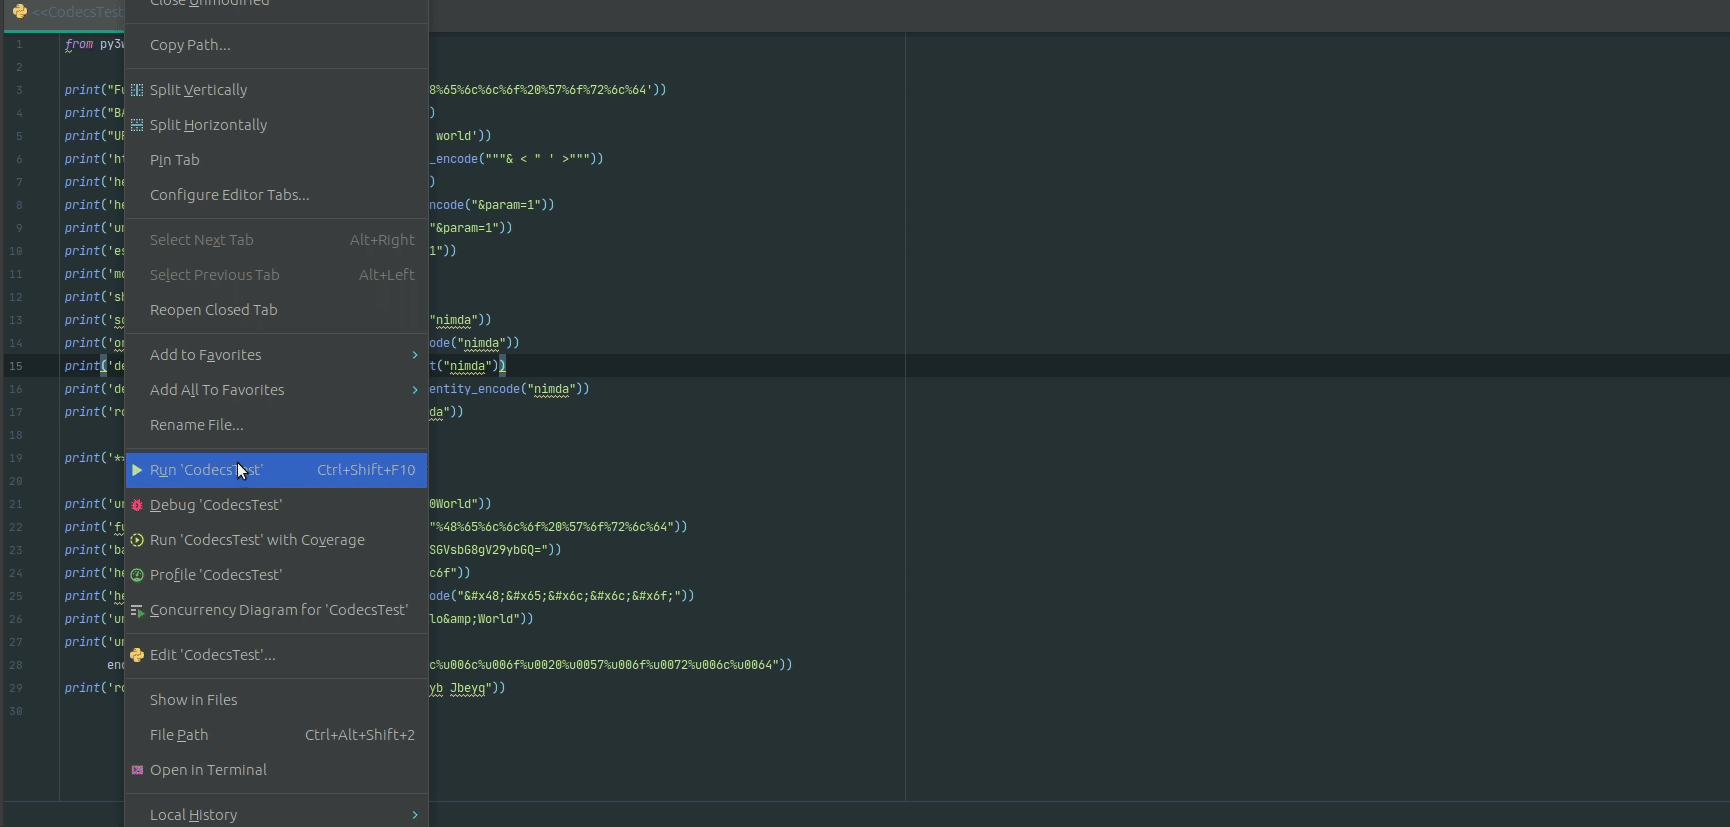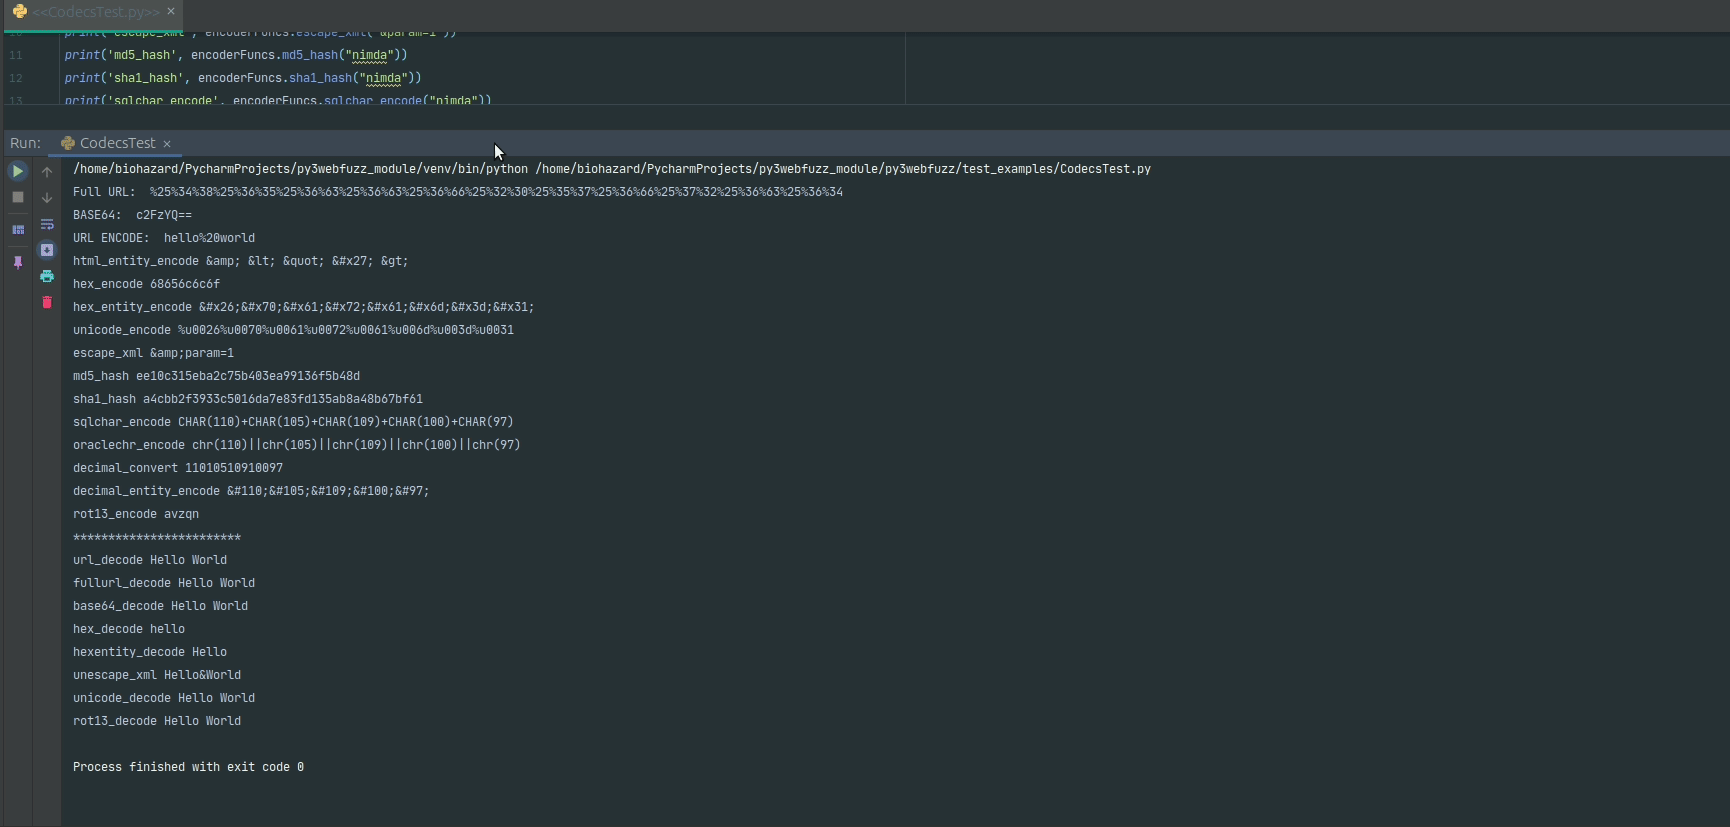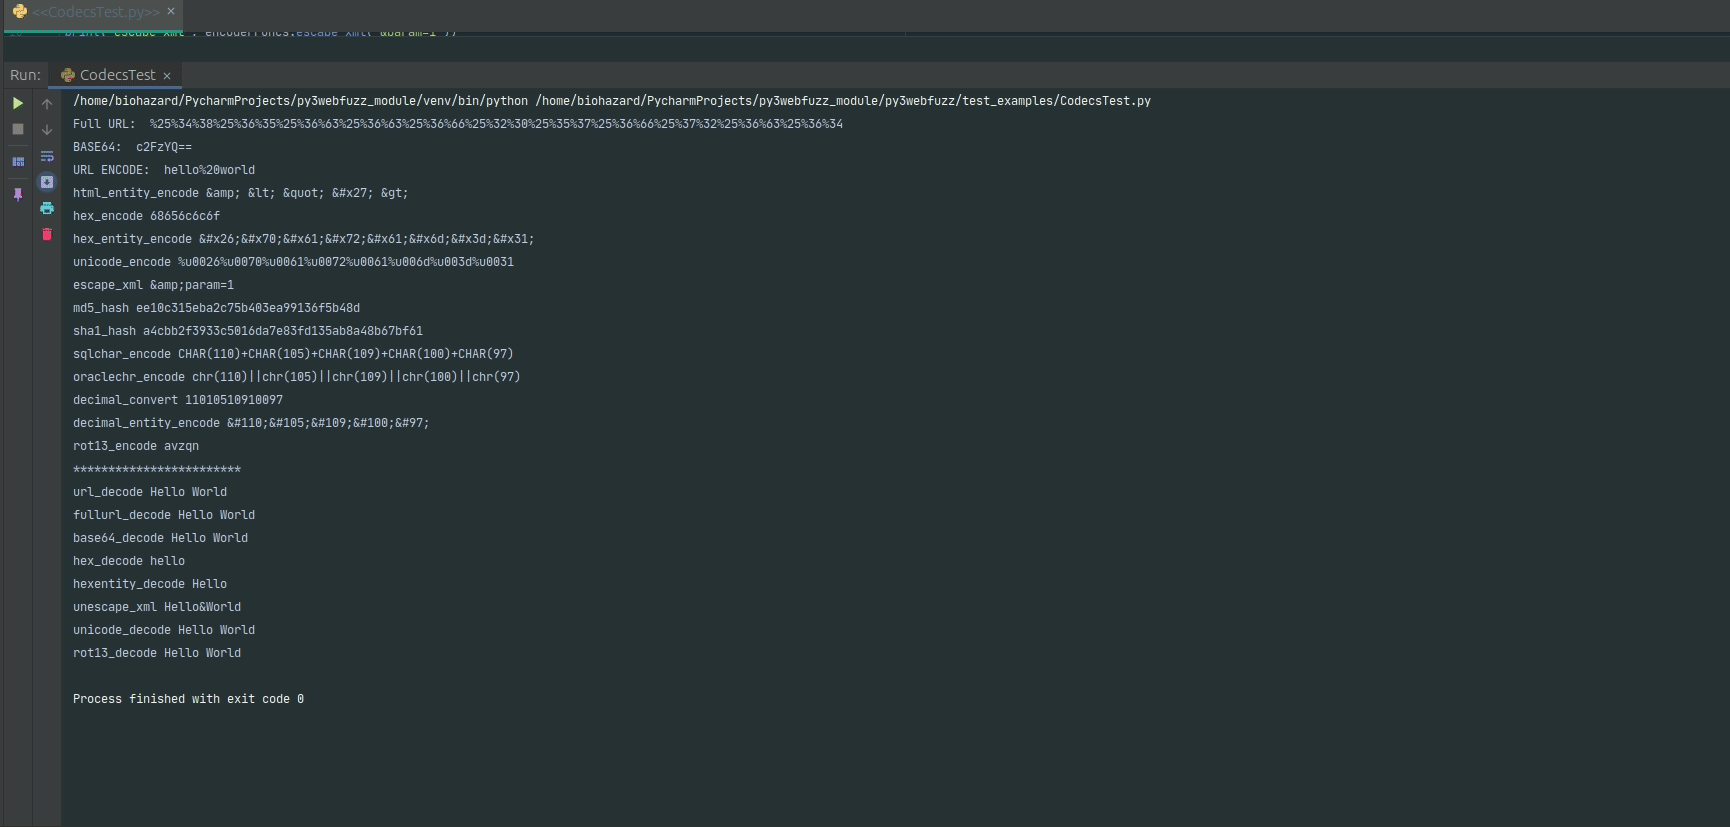 jangelesg/py3webfuzz
A Python3 module to assist in fuzzing web applications
 dark-lbp/isf
ISF(Industrial Control System Exploitation Framework),a exploitation framework based on Python
 seungsoo-lee/delta
PROJECT DELTA: SDN SECURITY EVALUATION FRAMEWORK
 malqr/malqr.github.io
MalQR is a collection of malicious QR Codes and Barcodes you can use to test the security of your scanners.
 luisfontes19/xxexploiter
Tool to help exploit XXE vulnerabilities