fuzz4bounty
 0xpugal/fuzz4bounty
1337 Wordlists for Bug Bounty Hunting
curated-resourcesfuzzinginformation-gathering+2
0xpugal/fuzz4bounty1337 Wordlists for Bug Bounty Hunting
 mycode83/godirb
Fast and easy-to-use directory brute-forcer written in Go.
 puppetm4ster/koyane-framework
Modular wordlist generation, editing, analysis, and discovery toolkit for password cracking, fuzzing, and ethical security testing. Supports…
 xmendez/wfuzz
Modular web fuzzer for automated security testing. Injects payloads into any HTTP request field to discover vulnerabilities, brute-force parameters,…
 postmodern/wordlist.rb
A Ruby library and CLI for generating and working with wordlists.
 ivan-sincek/forbidden
Bypass 4xx HTTP response status codes and more. The tool is based on Python Requests, PycURL, and HTTP Client.
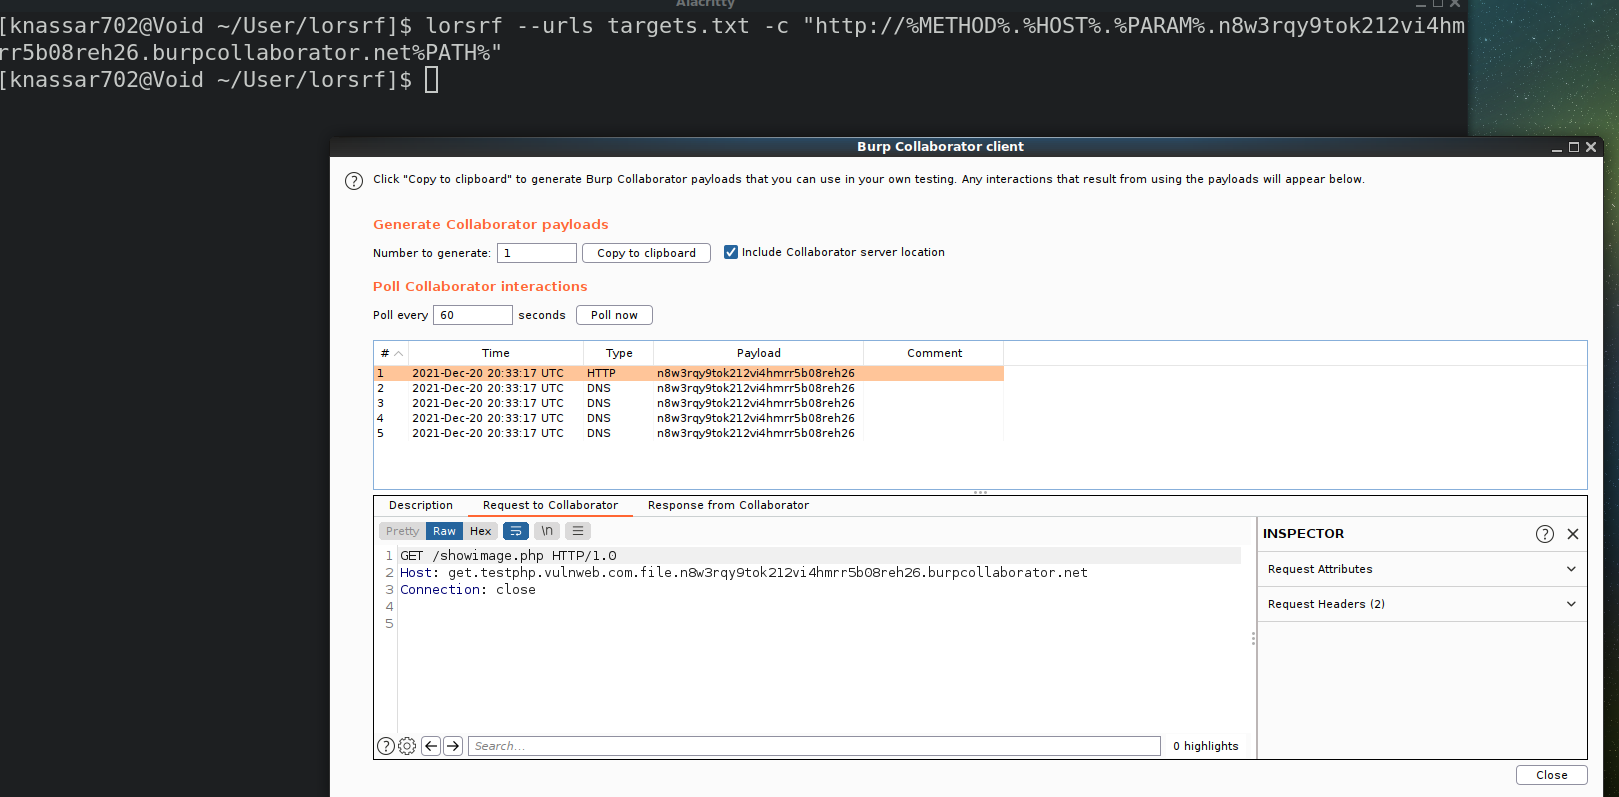 mindpatch/lorsrf
Fast CLI tool to find the parameters that can be used to find SSRF or Out-of-band resource load :artificial_satellite: :crab:
 ghosttroops/scan4all
Official repository vuls Scan: 15000+PoCs; 23 kinds of application password crack; 7000+Web fingerprints; 146 protocols and 90000+ rules Port…
 nicholasaleks/crackql
GraphQL penetration testing tool that exploits weak rate limits and cost analysis to brute-force credentials, bypass 2FA, enumerate users, and fuzz…
 hakaioffsec/navgix
Multi-threaded Go tool to detect nginx alias traversal vulnerabilities using heuristic and brute-force techniques for identifying vulnerable…
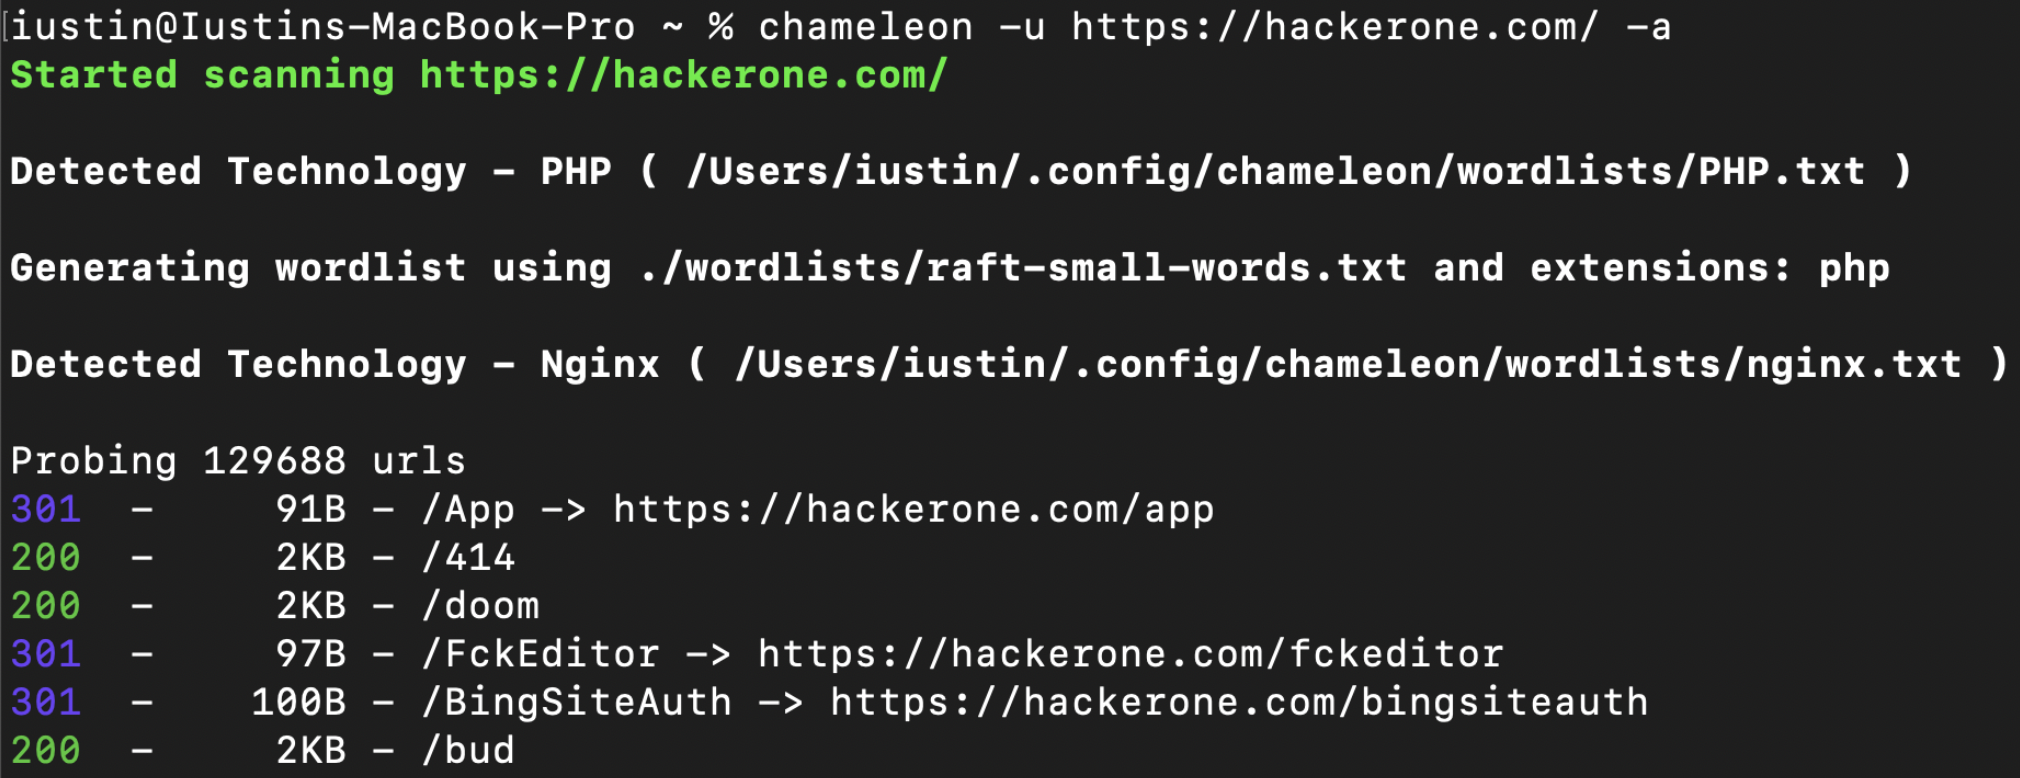 iustin24/chameleon
Technology-aware web content discovery scanner: detects Wappalyzer fingerprints, adapts wordlists/extensions, and performs fast directory bruteforce…
 henshin/filebuster
An extremely fast and flexible web fuzzer
 bo0om/parampampam
Brute-force tool for discovering hidden GET and POST parameters in web applications, supporting custom wordlists and concurrent requests.
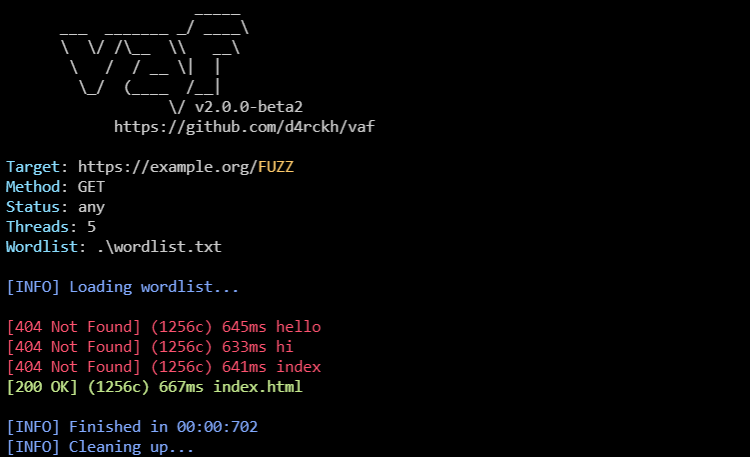 andreiverse/vaf
Multi-threaded web fuzzer for URL path, HTTP header, and POST data brute-forcing with proxy support, status code filtering, and reflexive content…
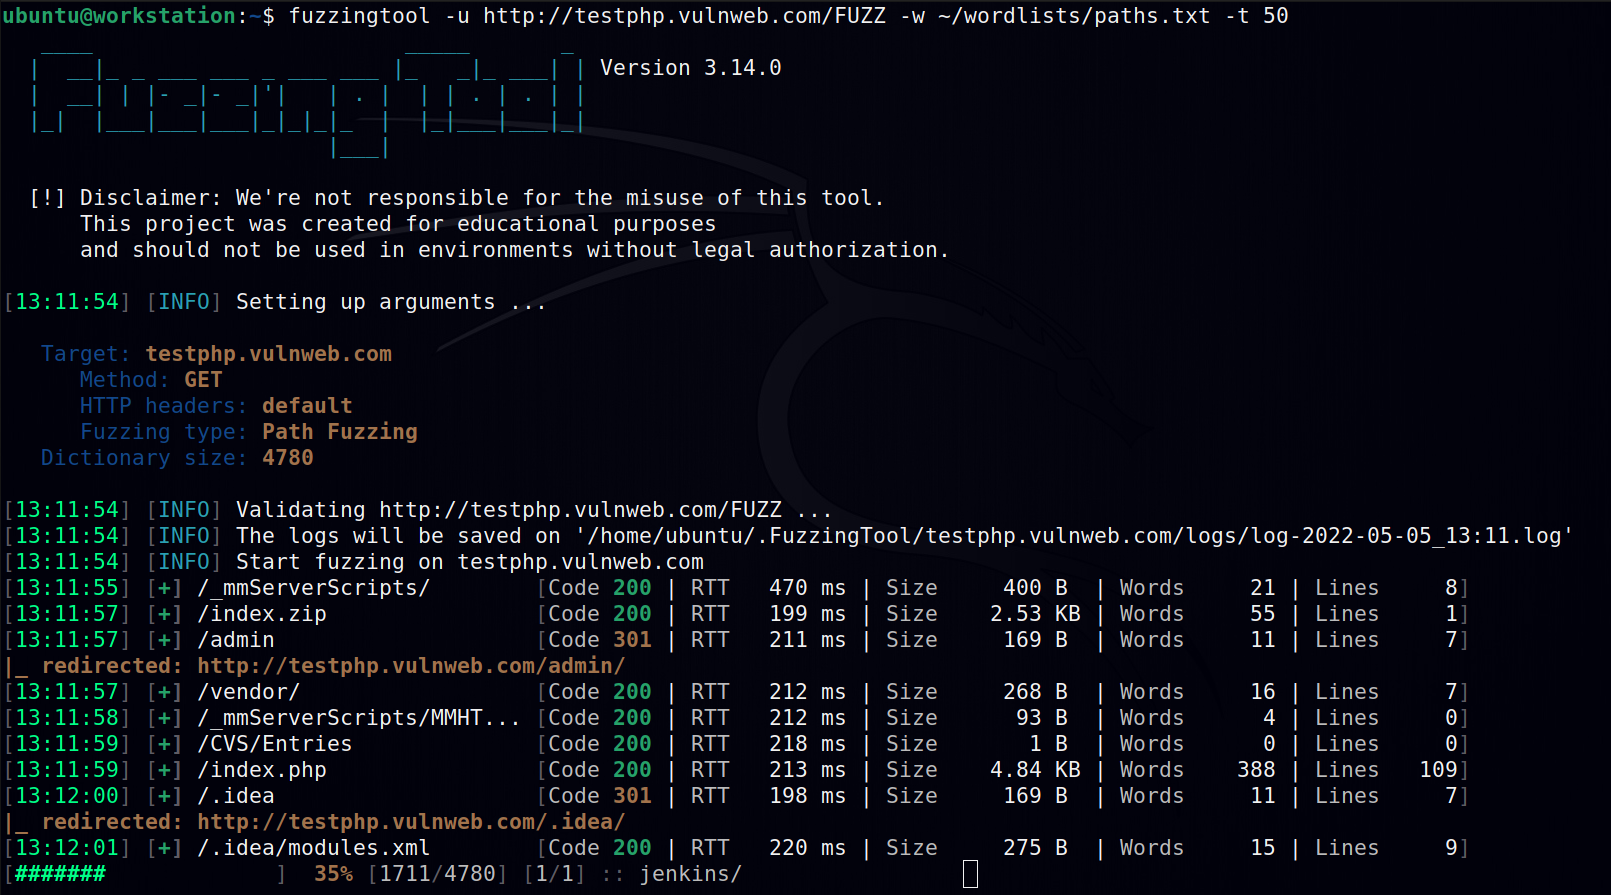 nescau-ufla/fuzzingtool
Software for fuzzing, used on web application pentestings.
 cytopia/urlbuster
Powerful mutable web directory fuzzer to bruteforce existing and/or hidden files or directories.