
unleashed-firmware
Custom firmware for Flipper Zero enabling Sub-GHz radio, NFC/RFID emulation, infrared, and BadUSB attack features for hardware security testing.

Custom firmware for Flipper Zero enabling Sub-GHz radio, NFC/RFID emulation, infrared, and BadUSB attack features for hardware security testing.

High-speed Burp Suite extension for sending large volumes of HTTP requests with a custom stack, Python-based attack configuration, and advanced…

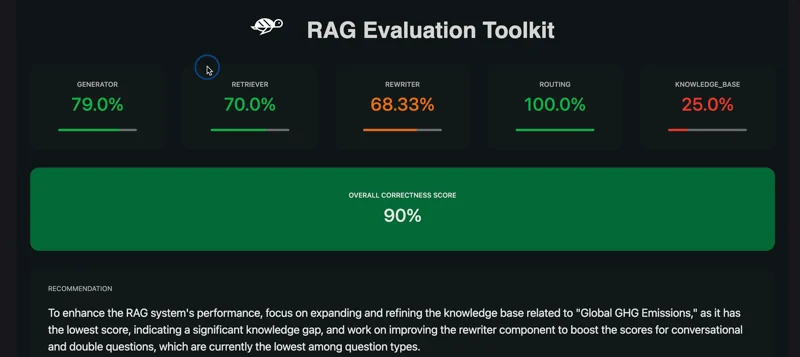
🐢 Open-Source Evaluation & Testing library for LLM Agents

LLM security testing framework for detecting prompt injection, jailbreaks, and adversarial attacks — 190+ probes, 28 providers, single Go binary

WiFi Penetration Testing & Auditing Tool

SIP Security Assessment Framework for VoIP Pentesters. Presented at DEFCON, BlackHat & Offzone.

ESP32DIV is a multi-purpose wireless offensive and defensive toolkit powered by an ESP32

Automatically find and execute fault injection attacks

Burp Suite extension for API security testing with 15 attack types, 108+ payloads, intelligent fuzzing, BOLA/IDOR detection, AI integration, and…

Validates and exploits VMware ESXi SFCB authentication bypass (CVE-2021-21994) via a probe/fuzz harness, enabling unauthenticated CIM-XML enumeration.

WAFNinja is a tool which contains two functions to attack Web Application Firewalls.

A full-featured open-source Wi-Fi fuzzer

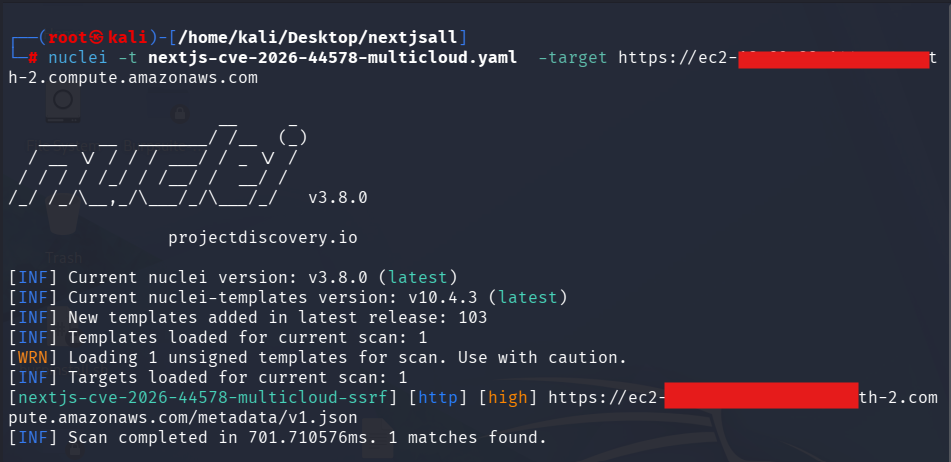
Nuclei templates for detecting CVE-2026-44578 (Next.js WebSocket Upgrade SSRF) with multi-cloud metadata validation, Next.js fingerprinting, and…

Security research and technical analysis of CVE-2025-5548, a buffer overflow vulnerability affecting FreeFloat FTP Server 1.0. This repository…


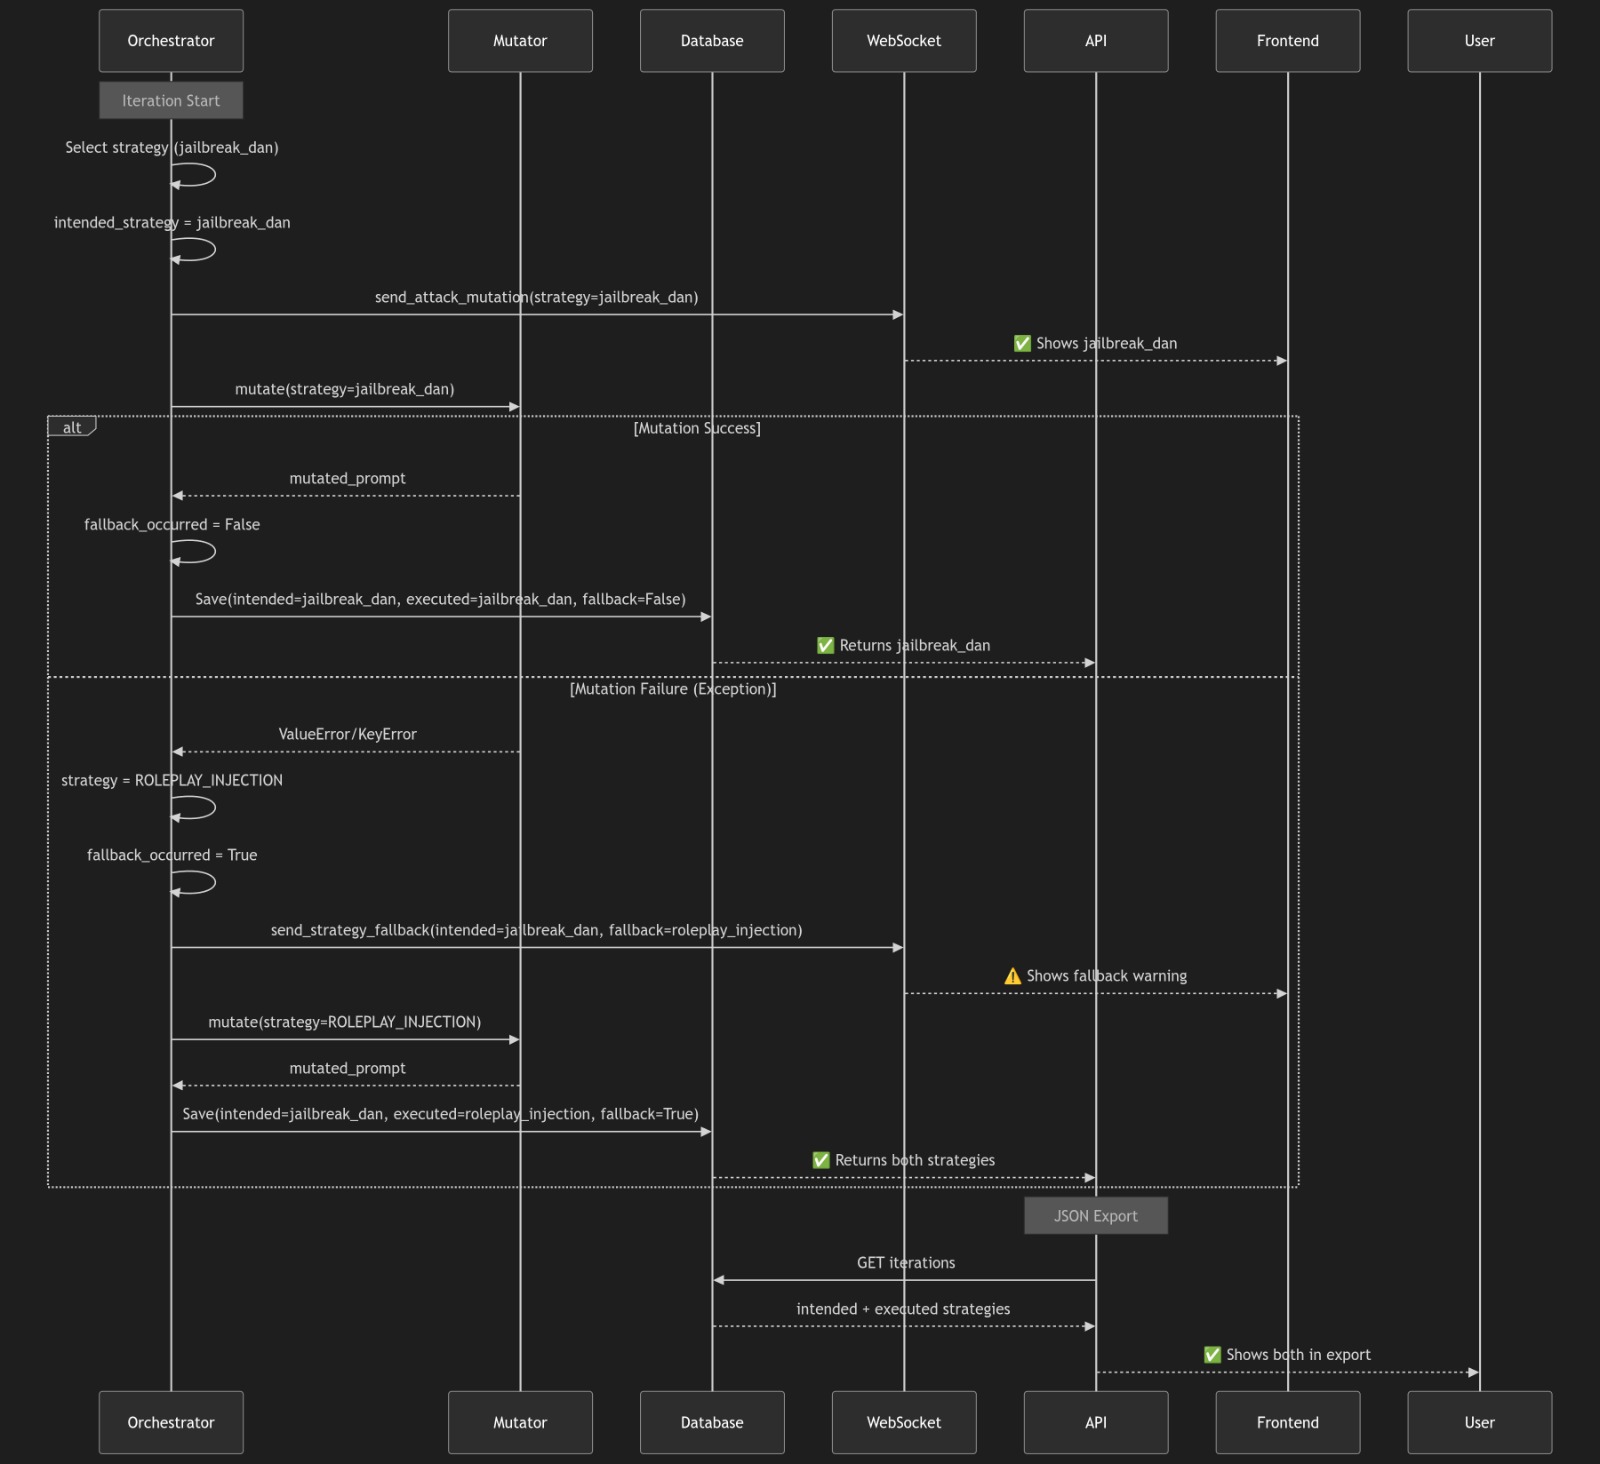
CEREBRO-RED v2: Advanced LLM Red Team Research Platform with PAIR Algorithm and LLM-as-a-Judge Evaluation

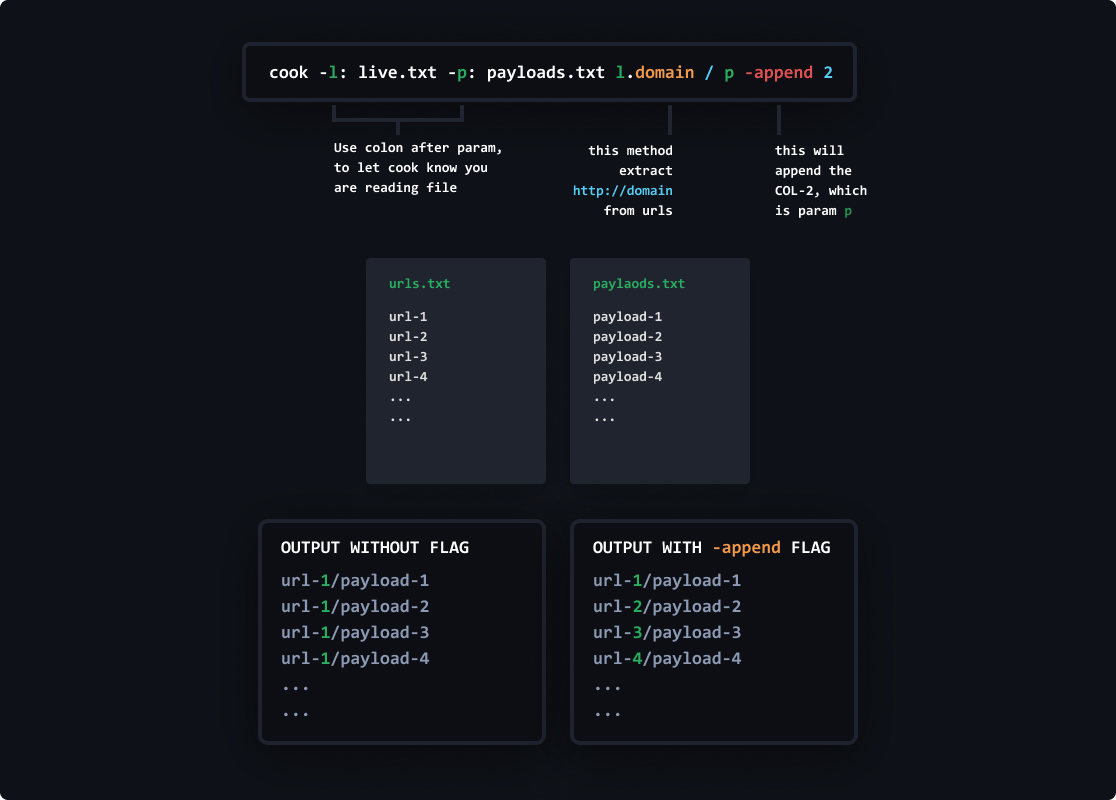
A wordlist framework to fullfill your kinks with your wordlists. For security researchers, bug bounty and hackers.

针对JWT渗透开发的漏洞验证/密钥爆破工具,针对CVE-2015-9235/空白密钥/未验证签名攻击/CVE-2016-10555/CVE-2018-0114/CVE-2020-28042的结果生成用于FUZZ,也可使用字典/字符枚举(包括JJWT)的方式进行爆破(JWT Crack)