

caeruleus
 praetorian-inc/caeruleus
Single Go binary for Bluetooth Low Energy security testing on Linux/BlueZ: scan, enumerate GATT, read/write/notify, fuzz characteristics, and run…
bluetooth-securityfuzzinghardware-iot-security+8
56
praetorian-inc/caeruleusSingle Go binary for Bluetooth Low Energy security testing on Linux/BlueZ: scan, enumerate GATT, read/write/notify, fuzz characteristics, and run…
 piratesshield/apiharvester
The one shot API attacker tool - finds the API url from the given root simulate the automated attacks
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 rix4uni/wordlist
Curated collection of custom wordlists for fuzzing, DNS enumeration, parameter discovery, and default credentials, plus a Go generator for nuclei…
 vighnesh91/omnisec-hex
Browser-local security monorepo with six modules for mobile APK/IPA triage, client-side DAST fuzzing, OSINT directories, offline AI threat scoring,…
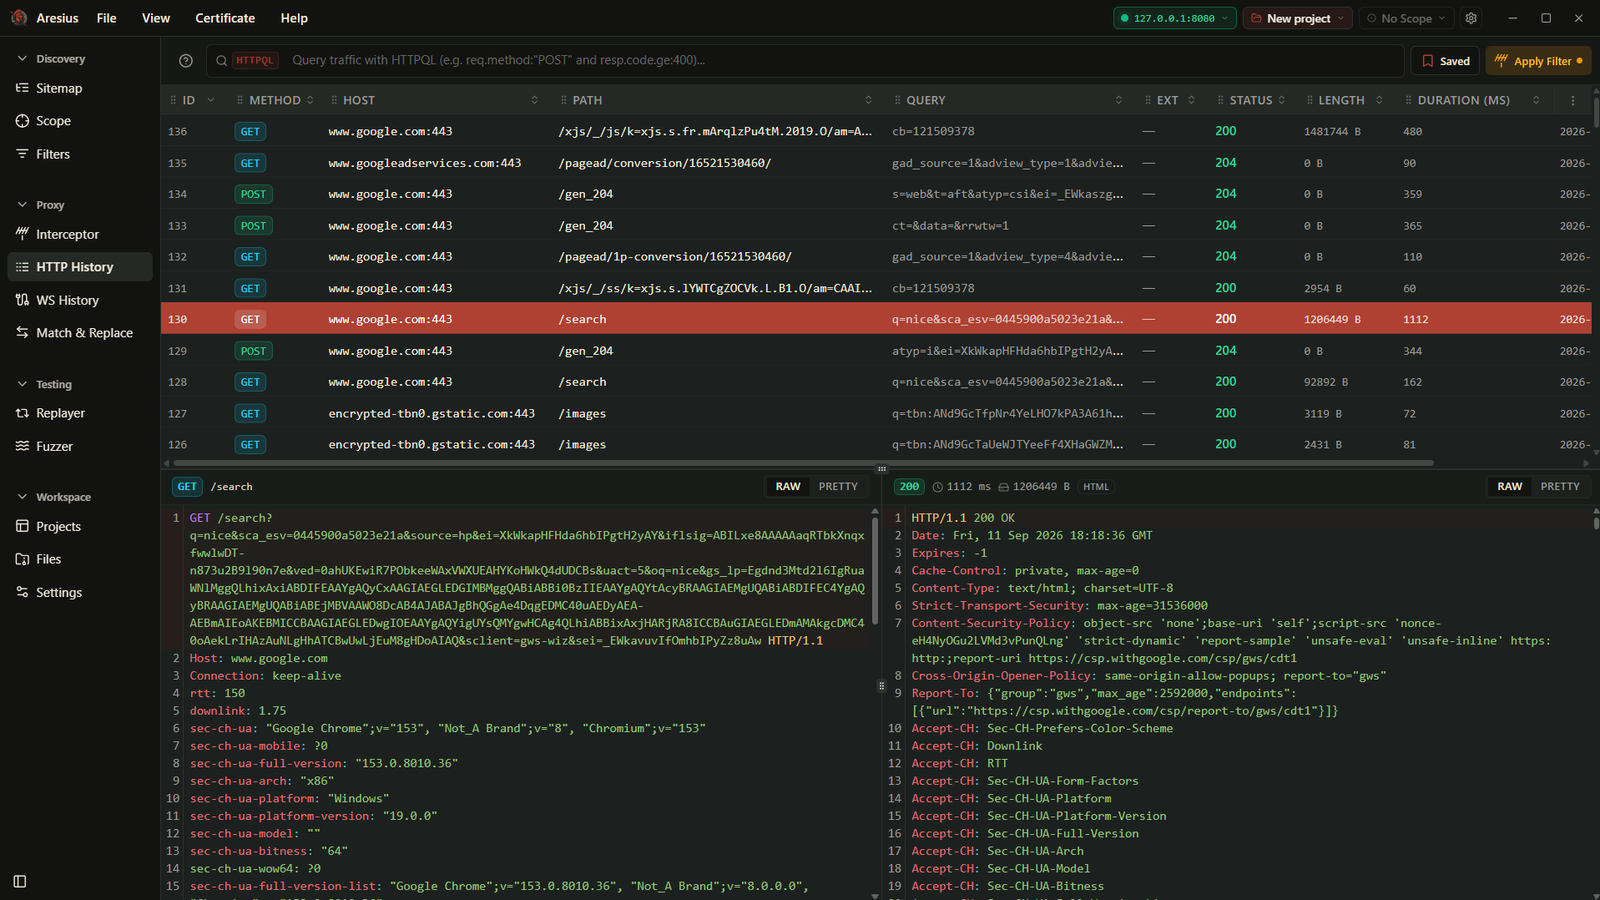 0xmarik/aresius
Native HTTP/HTTPS interception proxy for penetration testers and bug bounty hunters with live request tampering, request replay, high-speed fuzzing,…
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and hacking & pentesting toolkit for the terminal.
 mycode83/godirb
Fast and easy-to-use directory brute-forcer written in Go.
 ericmtzmtz/pwnproxy
An open, local-first security testing platform for pentesters, AI agents, CI/CD pipelines, and teams.
 hslatman/awesome-industrial-control-system-security
A curated list of resources related to Industrial Control System (ICS) security.
 wapiti-scanner/wapiti
Web vulnerability scanner written in Python3
 dozermx/argus
Multi-phase reconnaissance and attack-surface scanner that maps domains, IPs, ASNs, cloud assets, and CVEs into a knowledge graph with CVSS scoring…
 wattocyber/bug-bounty-library
Curated bug-bounty methodology library with runbooks, recon/fuzz playbooks, checklists, and CLI helpers for target scoping, cert enumeration, and…
 mreza-en/cve-2021-21994_poc
Validates and exploits VMware ESXi SFCB authentication bypass (CVE-2021-21994) via a probe/fuzz harness, enabling unauthenticated CIM-XML enumeration.
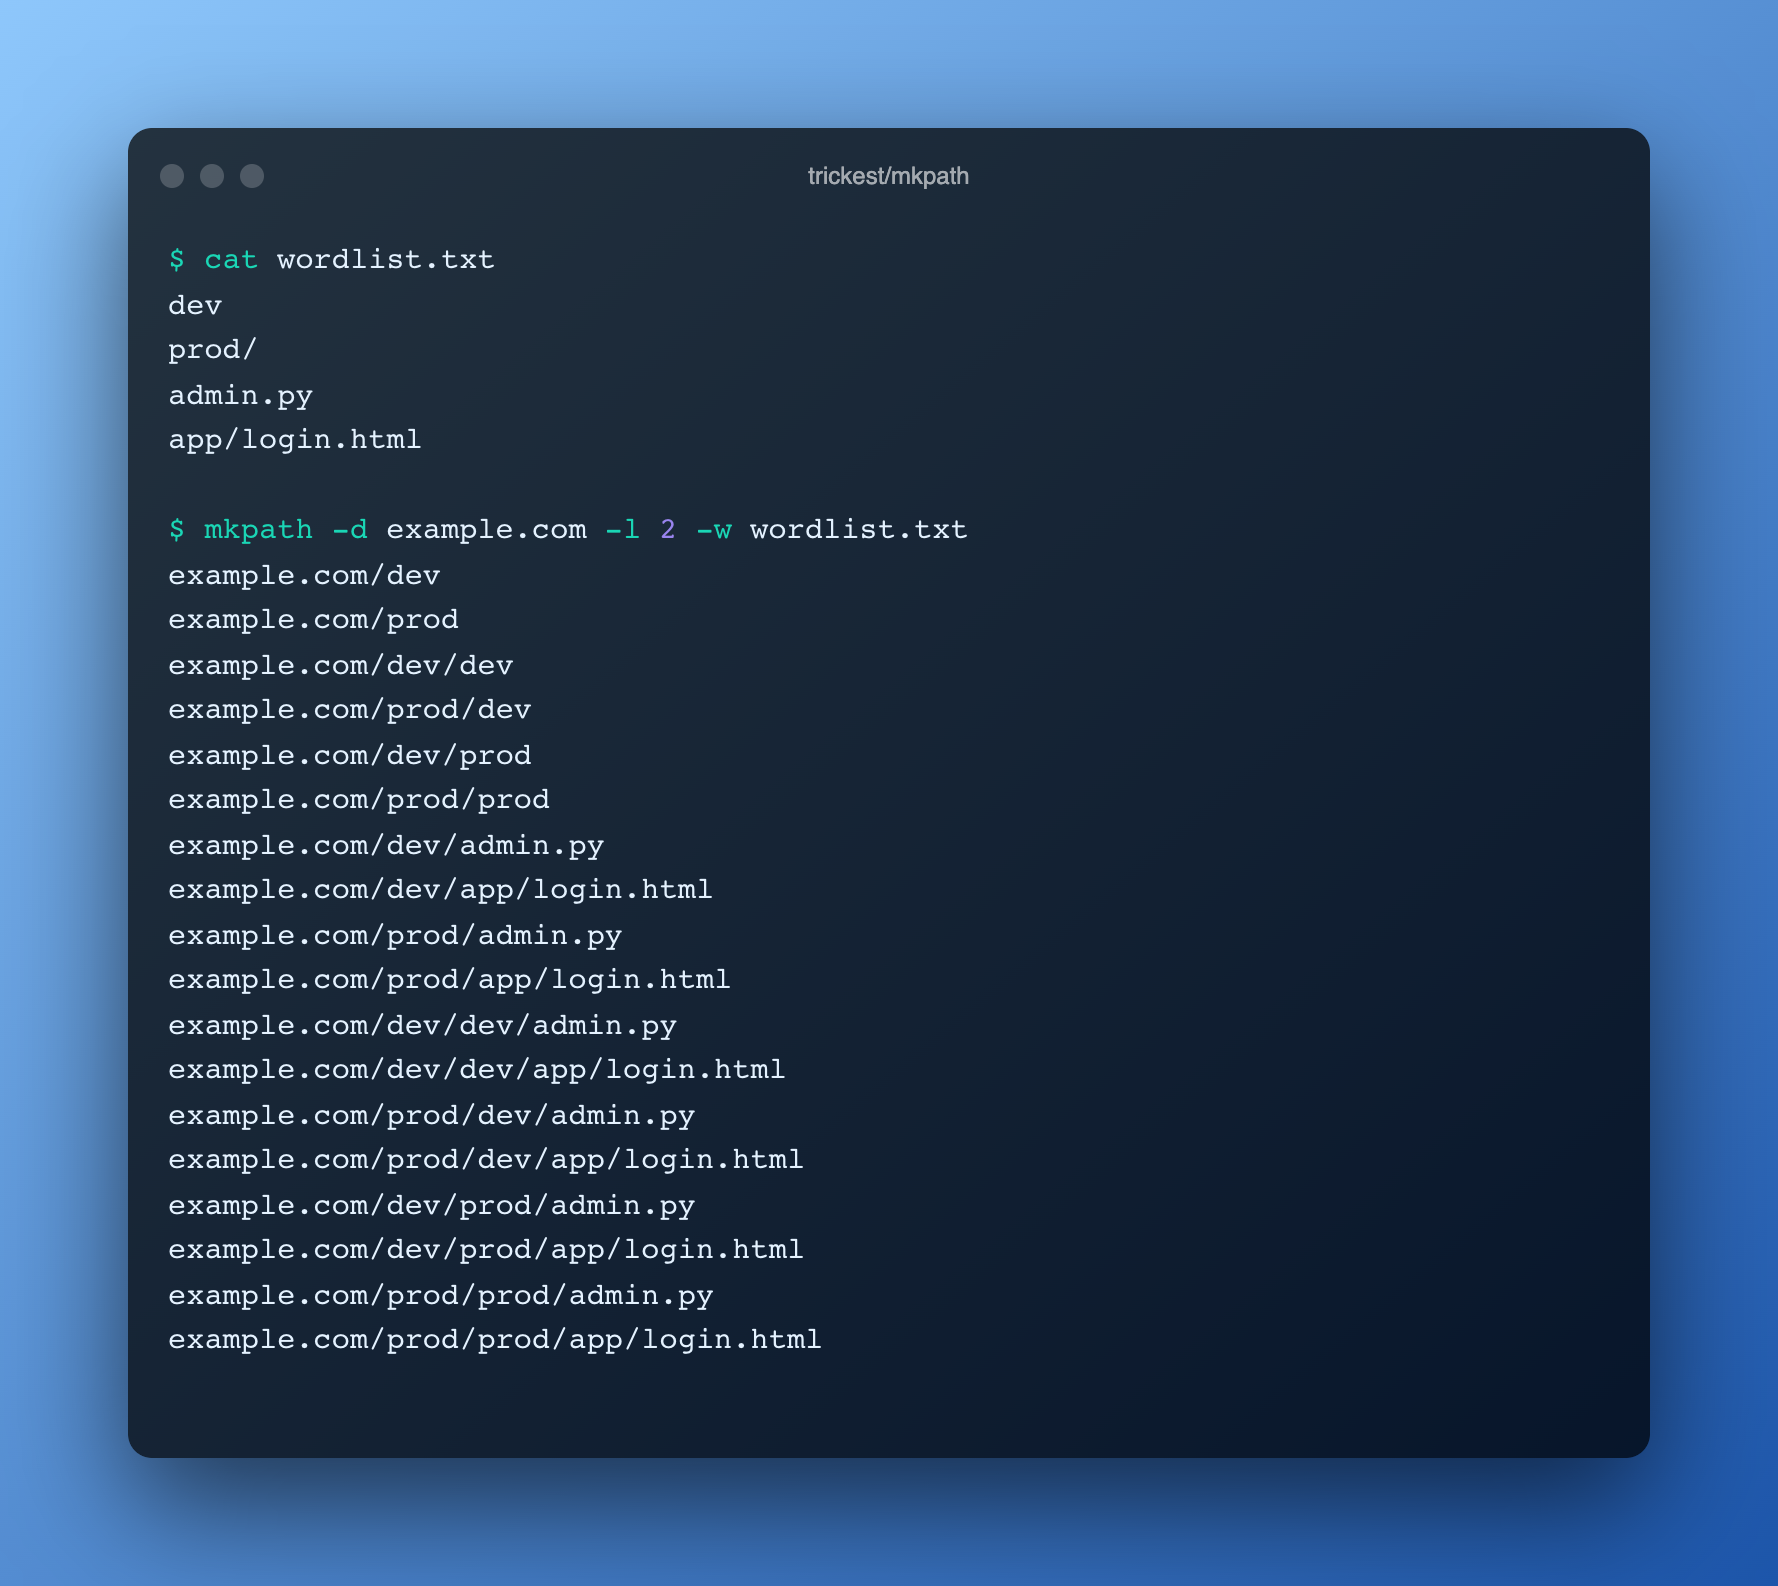 trickest/mkpath
Make URL path combinations using a wordlist
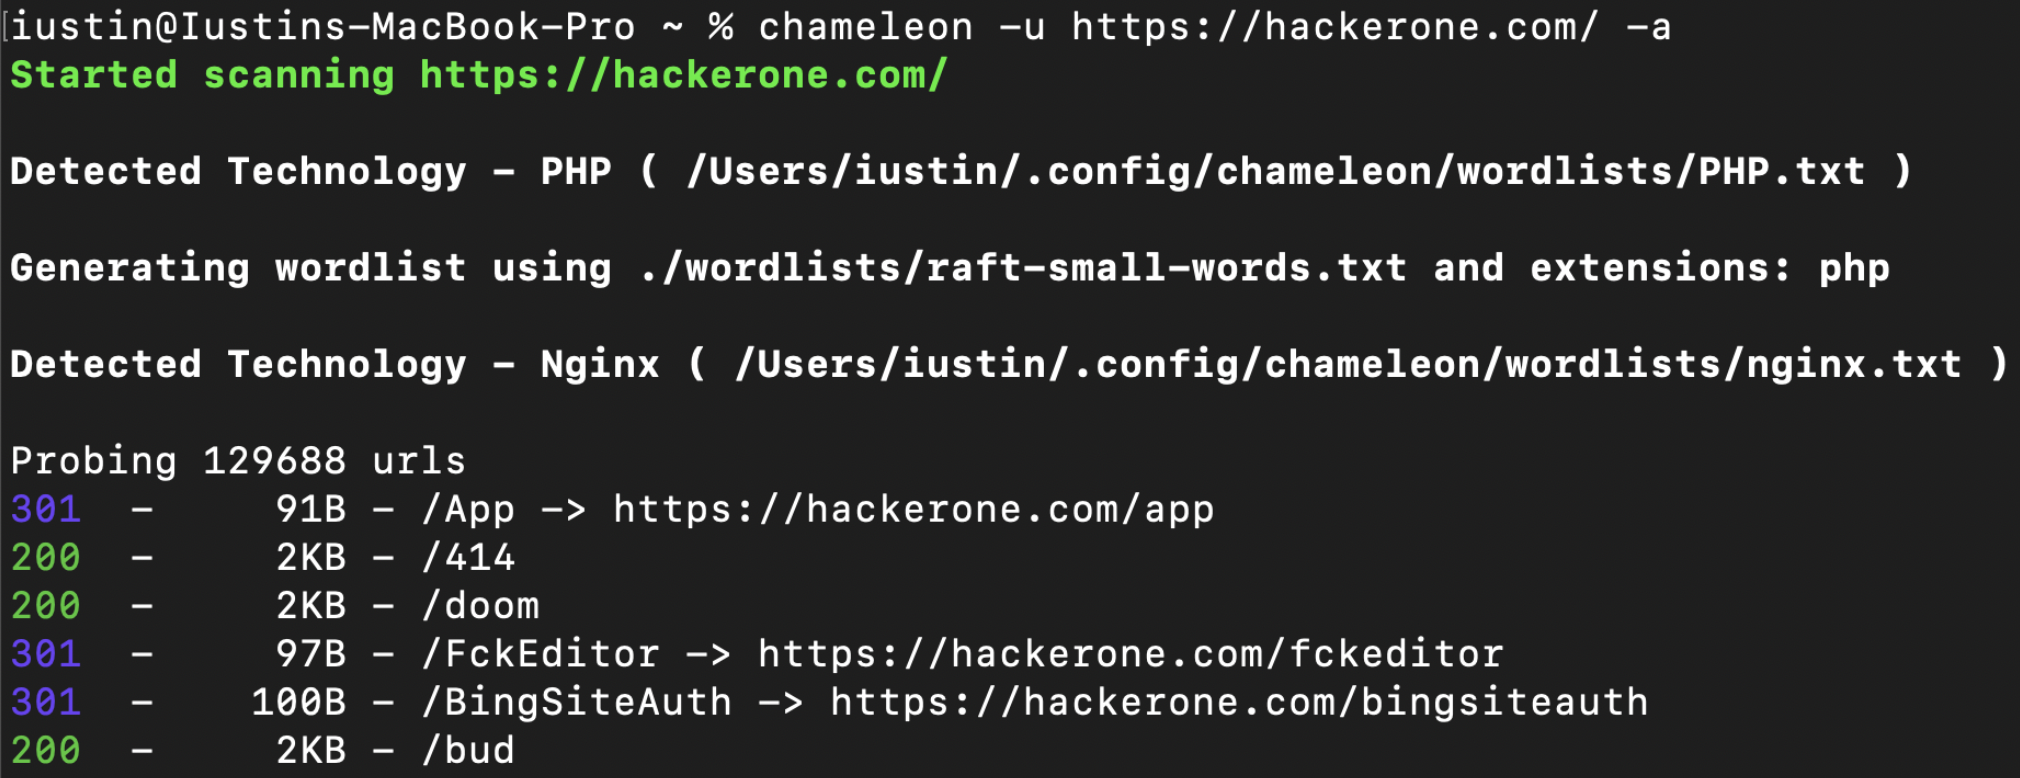 iustin24/chameleon
Technology-aware web content discovery scanner: detects Wappalyzer fingerprints, adapts wordlists/extensions, and performs fast directory bruteforce…