

http-terminator
 portswigger/http-terminator
AI-assisted research pipeline that extracts HTTP desync techniques, generates malformed request test-cases, validates them via Burp, and confirms…
ai-securityexploitationfuzzing+8
120
portswigger/http-terminatorAI-assisted research pipeline that extracts HTTP desync techniques, generates malformed request test-cases, validates them via Burp, and confirms…
 kabiri-labs/rcekit
RCE detection and confirmation toolkit that tests URLs or captured HTTP requests for command injection, SSTI, blind and OOB paths, returning tiered…
 mohammadalimehri/cve-2021-44790-lab
Dockerized Apache mod_lua lab with a Python PoC reproducing the CVE-2021-44790 multipart boundary buffer overflow for local defensive testing and…
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and hacking & pentesting toolkit for the terminal.
 12lie20/cve-2026-23918-test
This repository contains a Proof of Concept (PoC) demonstrating the Double Free vulnerability (CVE-2026-23918) in Apache HTTP Server 2.4.66…
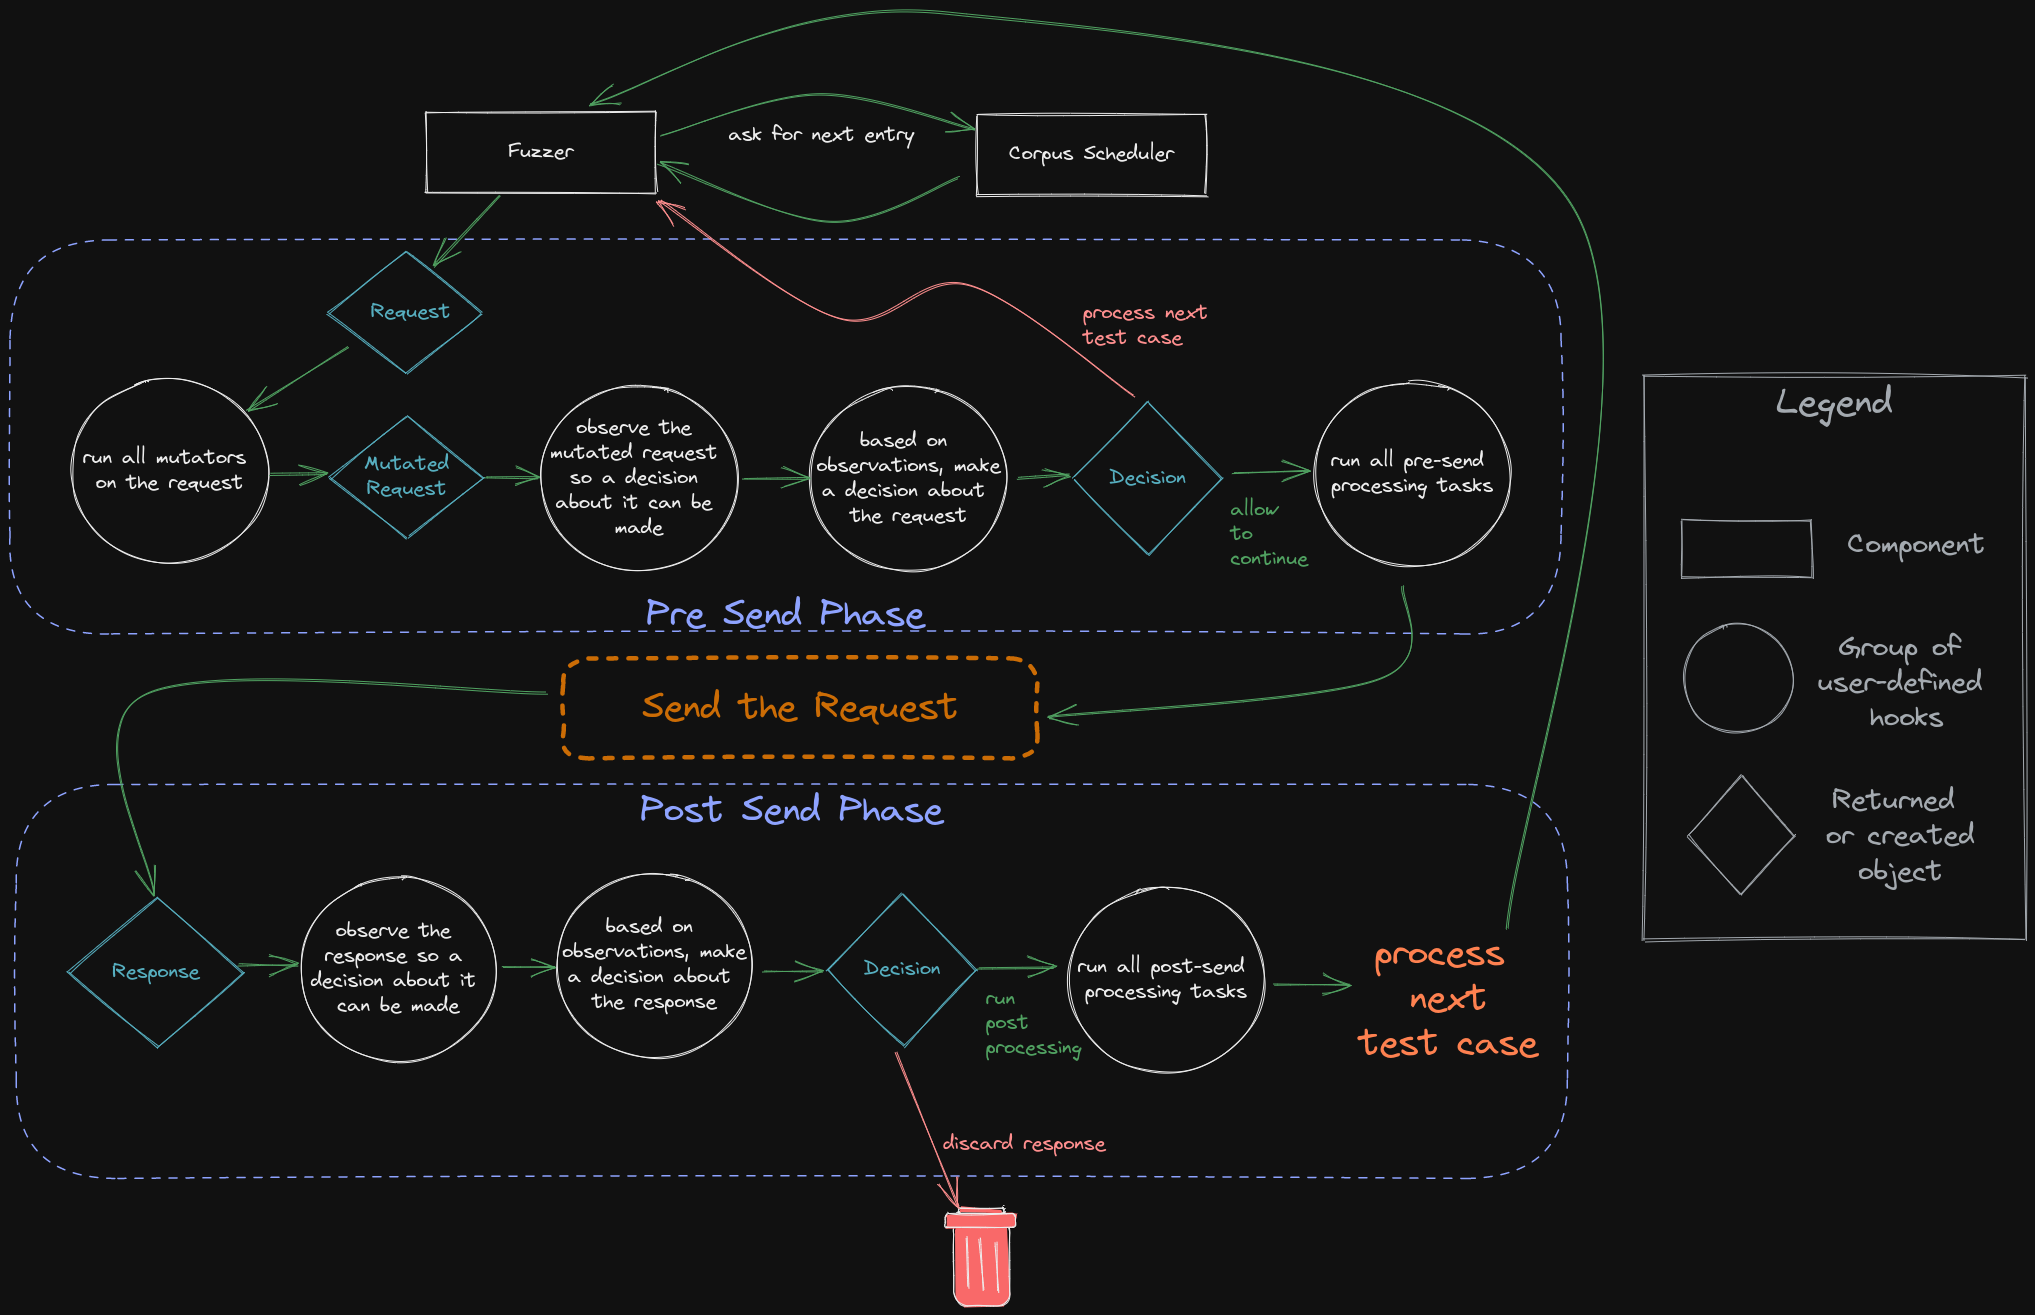 epi052/feroxfuzz
Build structure-aware black-box HTTP fuzzers in Rust with composable mutators, schedulers, observers, deciders, and processors for custom web and API…
 xnl-h4ck3r/auto-repeater
Automated HTTP Request Repeating With Burp Suite
 narfindustries/http-garden
Differential testing framework for HTTP implementations
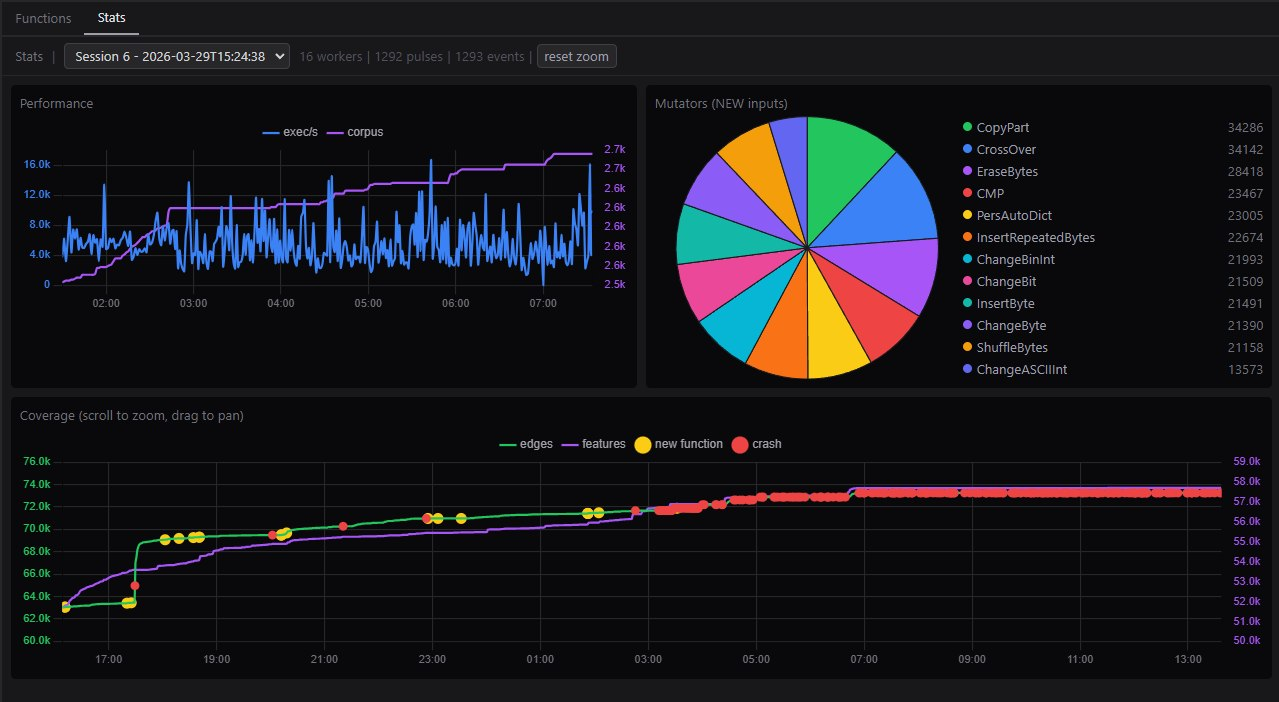 0xbigshaq/apatchy
Fuzzing Framework for Modules in Apache HTTPD Server
 cappricio-securities/crlfi-scanner
CRLFISCANNER is a lightweight and powerful CLI tool designed for bug bounty hunters and penetration testers to automatically detect CRLF injection…
 r3dxpl0it/rtspserver-code-execution-vulnerability
RTSPServer Code Execution Vulnerability CVE-2018-4013
 scheibling/py-log4shellscanner
Scanner for the Log4j vulnerability dubbed Log4Shell (CVE-2021-44228)
 quantumworld-dpdns-io/cve-2026-42945
Full CVE-2026-42945 research repository with heap buffer overflow analysis, RCE exploit (heap spray + Feng Shui), detection scripts, and patching…
 liaoziqi-gzfls/cve-2026-42945
CVE-2026-42945 Nginx Rift
 sirredbeard/cve-2025-60876
Behavior-preserving fix for CVE-2025-60876 HTTP header injection in BusyBox wget, with proof-of-concept, percent-encoding patch, and upstream…
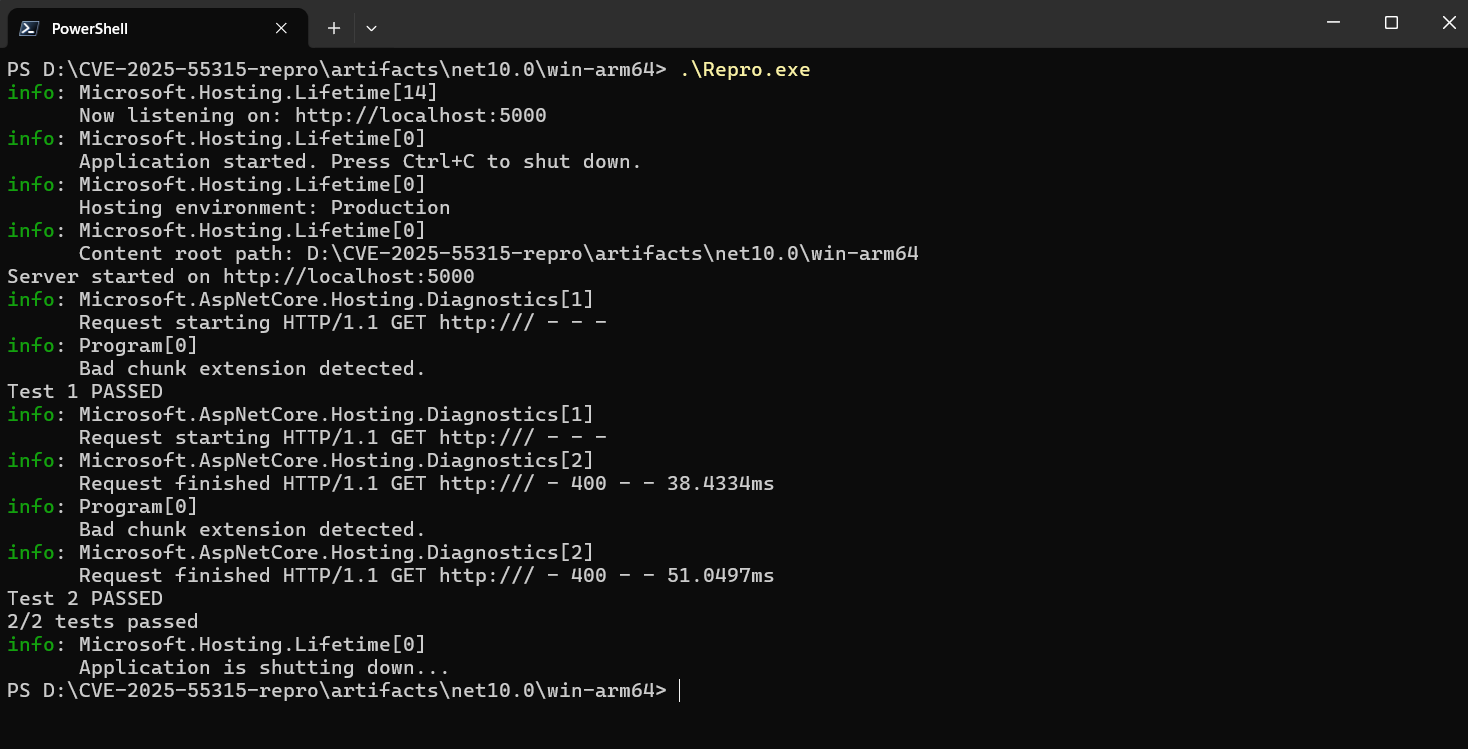 sirredbeard/cve-2025-55315-repro
Tool that reproduces CVE-2025-55315 in ASP.NET Core.
 starrynightsecurity/cve-2025-54574-squid-heap-buffer-overflow
Vulnerability Found on Squid Proxy.
 soltanali0/cve-2024-40725
exploit CVE-2024-40725 (Apache httpd) with