
CVE-2026-55781-poc
 nt2dev/cve-2026-55781-poc
Unbounded memory allocation in NanaZip's UFS handler via an attacker-controlled `fs_bsize` field.
exploitationfuzzingpapers-research+1
2
nt2dev/cve-2026-55781-pocUnbounded memory allocation in NanaZip's UFS handler via an attacker-controlled `fs_bsize` field.
 portswigger/http-terminator
AI-assisted research pipeline that extracts HTTP desync techniques, generates malformed request test-cases, validates them via Burp, and confirms…
 devrodt2/cve-2026-28609-matroska-pcm-oob
Proof-of-concept and instrumented reproduction harness for CVE-2026-28609, an out-of-bounds write in Android's MatroskaExtractor reachable via a…
 aftermathlabs/discord-crasher
Some bugs found via binary instrumentation and fuzzing
 ivanesk315/cve-2026-42533
Docker lab reproducing CVE-2026-42533, a pre-auth nginx heap overflow and info leak via two-pass capture clobbering, with PoC scripts and patched…
 isukasanuj/cve-2026-85769
Proof-of-concept exploit for CVE-2026-85769, a heap out-of-bounds read in libtpms TPM 2.0 state deserialization, demonstrating denial of service via…
 r3n3r0/cve-2026-27280
In-depth analysis and proof-of-concept for CVE-2026-27280, an out-of-bounds write in Adobe DNG SDK's dng_render_task::ProcessArea, reachable via…
 slayerkkkk/cve-2025-46817-poc
C-based exploit for CVE-2025-46817, a Redis integer overflow vulnerability, enabling crash detection and potential RCE via Lua unpack() payload.
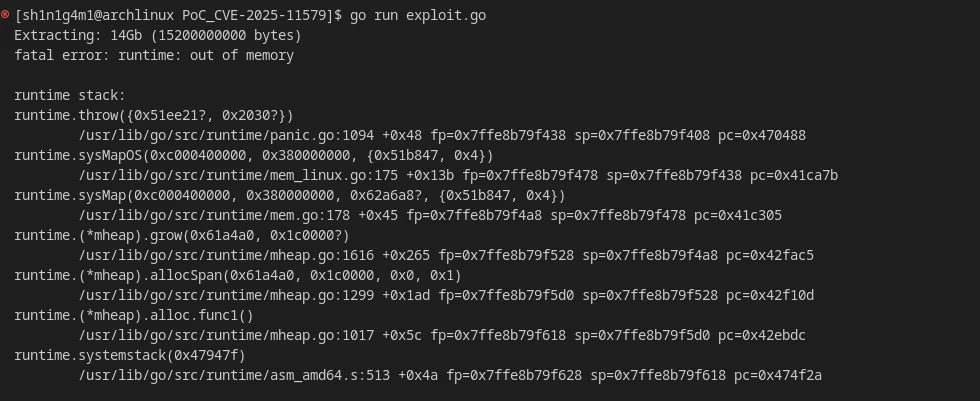 shinigami-777/poc_cve-2025-11579
Proof-of-concept exploit for CVE-2025-11579, a denial-of-service vulnerability in rardecode that triggers an out-of-memory crash via a crafted RAR…
 jfrog/jfrog-cve-2023-43786-libx11_dos
Proof-of-concept for CVE-2023-43786, a libX11 integer overflow causing infinite loop DoS. Demonstrates triggering the vulnerability via sxpm with a…
 dwisiswant0/cve-2025-46819
Proof-of-concept exploit for CVE-2025-46819, a Redis Lua long-string delimiter out-of-bounds read, demonstrating a crash via malformed input.
 cyhe50/cve-2025-54874-poc
Proof-of-concept demonstrating a memory leak in OpenJPEG 2.5.1 via crafted JP2 files, triggering opj_read_header failure and heap leak, with valgrind…
 johanneslks/cve-2026-32945
PJSIP DNS Compression Pointer Heap OOB Read (Remote DoS)
 dshankle/vlc_cve-2021-25801_analysis
Technical analysis of CVE-2021-25801 in VLC's AVI parser, demonstrating an out-of-bounds read via crafted sub-index chunks and providing a…
 0xbbdd/cve-2026-33317
Proof-of-concept for CVE-2026-33317, an out-of-bounds write in OP-TEE PKCS#11 TA, demonstrating Secure World heap corruption via a malformed…
 mreza-en/cve-2021-21994_poc
Validates and exploits VMware ESXi SFCB authentication bypass (CVE-2021-21994) via a probe/fuzz harness, enabling unauthenticated CIM-XML enumeration.
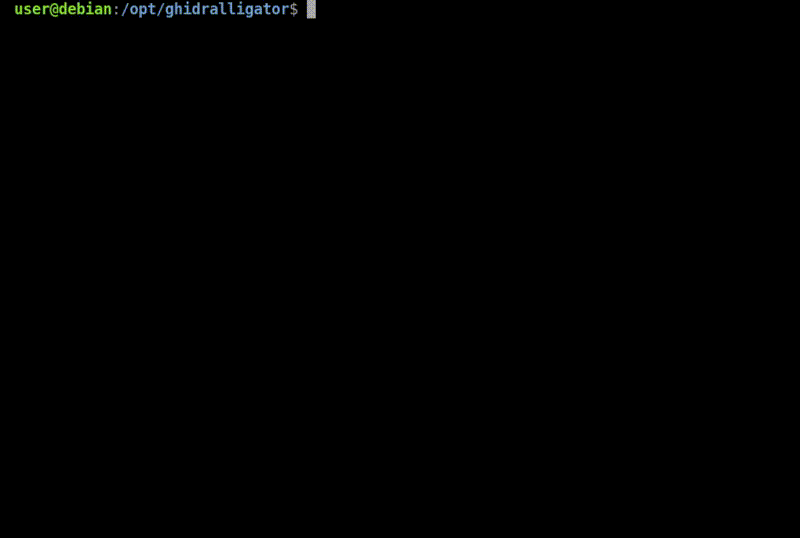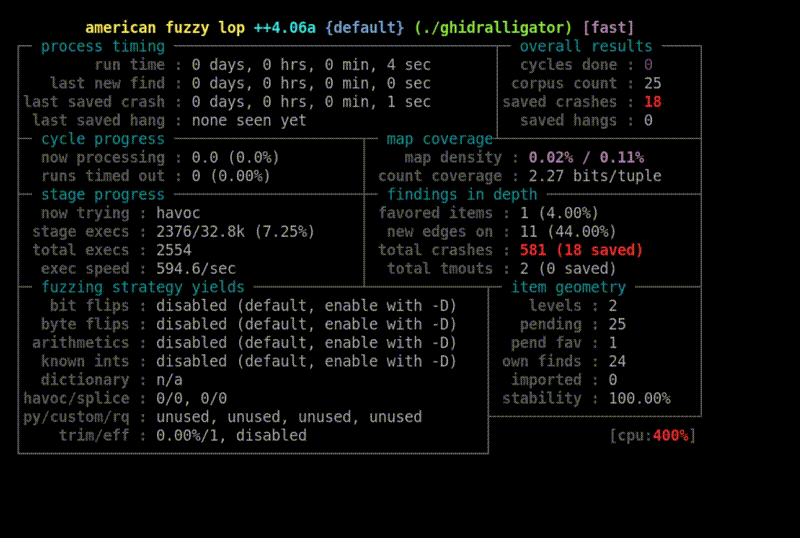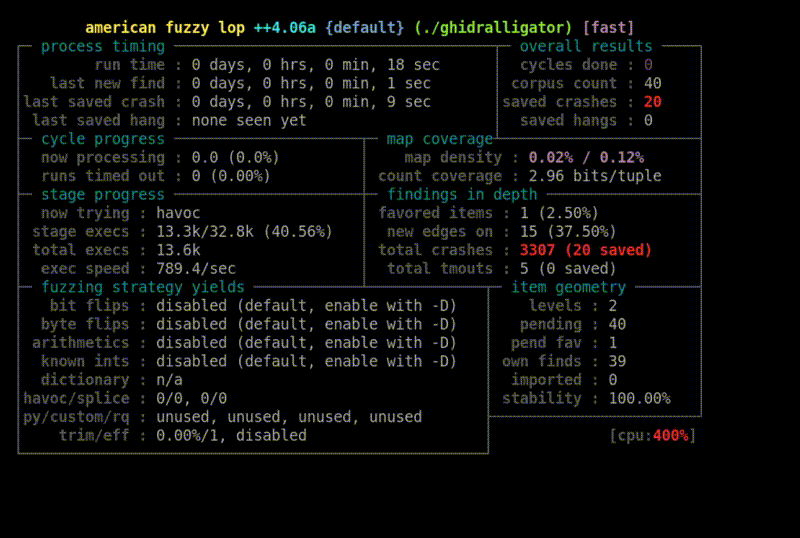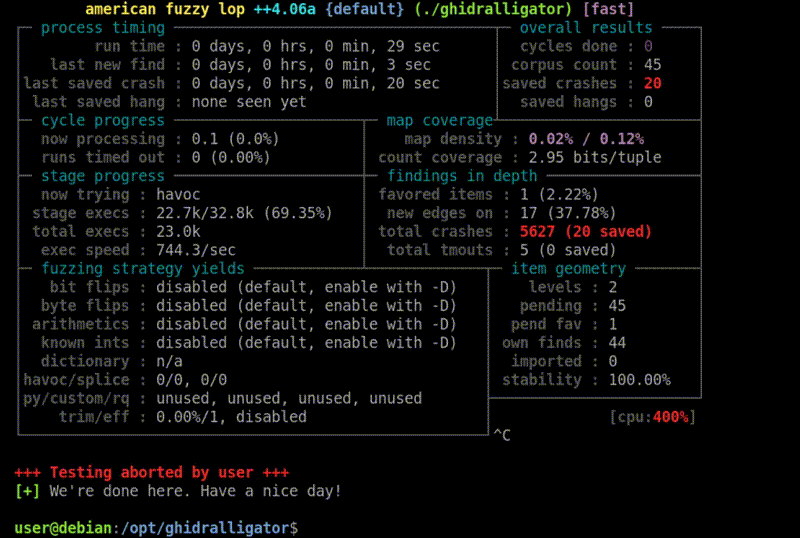 airbus-cyber/ghidralligator
Multi-architecture pcode emulator using Ghidra/Sleigh for AFL++ fuzzing of binaries, firmware, and embedded targets; detects memory-corruption bugs…
 google/oss-fuzz-gen
LLM powered fuzzing via OSS-Fuzz.