
log4j-fuzzer
 mr-vill4in/log4j-fuzzer
Automated scanner for CVE-2021-44228 (Log4Shell) that tests single or multiple web targets for the vulnerability using remote callback servers.
exploitationfuzzingpenetration-testing+2
3
mr-vill4in/log4j-fuzzerAutomated scanner for CVE-2021-44228 (Log4Shell) that tests single or multiple web targets for the vulnerability using remote callback servers.
 manishkanyal/log4j-scanner
A Log4j vulnerability scanner is used to identify the CVE-2021-44228 and CVE_2021_45046
 xnl-h4ck3r/auto-repeater
Automated HTTP Request Repeating With Burp Suite
 soltanali0/cve-2024-40725
exploit CVE-2024-40725 (Apache httpd) with
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
 kiralab/text4shell-scan
A fully automated, accurate, and extensive scanner for finding text4shell RCE CVE-2022-42889
 juanschallibaum/cve-2024-38473-nuclei-template
Nuclei template to detect Apache servers vulnerable to CVE-2024-38473
 freefv/cve-2020-6308-mass-exploiter
Mass exploiter for CVE-2020-6308 with multi-worker support, enabling automated exploitation of vulnerable SAP NetWeaver systems.
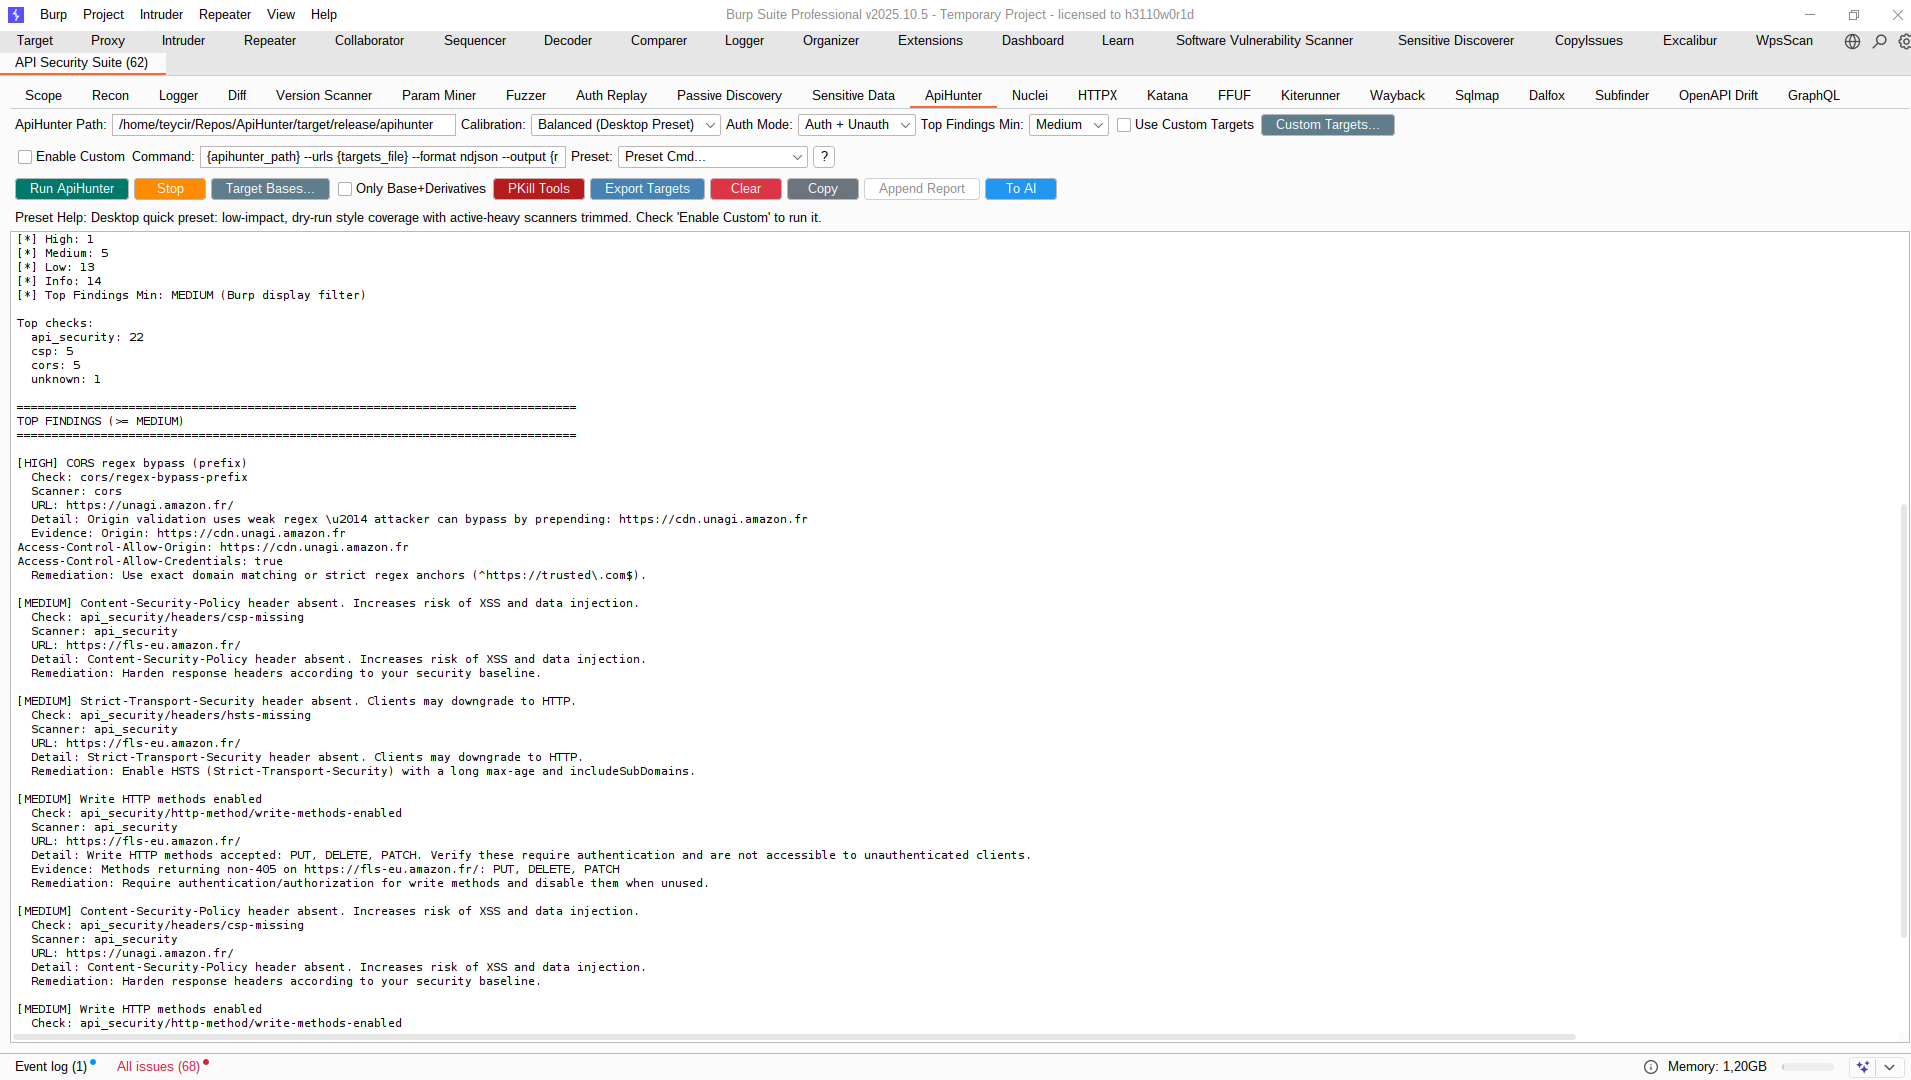 teycir/burpapisecuritysuite
Burp Suite extension for API security testing with 15 attack types, 108+ payloads, intelligent fuzzing, BOLA/IDOR detection, AI integration, and…
 bogdanticu88/ratrace
A lightweight CLI tool for systematically detecting and exploiting race conditions in web applications, APIs, and modern services.
 416rehman/deepzero
Find zero-days while you sleep. DeepZero is an automated vulnerability research framework that parses, decompiles, and analyzes thousands of Windows…
 hellsender01/llmmap
Automated prompt injection testing framework for LLM-integrated applications with dual-LLM architecture.
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
 fcavallarin/htcap
htcap is a web application scanner able to crawl single page application (SPA) recursively by intercepting ajax calls and DOM changes.
 xmendez/wfuzz
Modular web fuzzer for automated security testing. Injects payloads into any HTTP request field to discover vulnerabilities, brute-force parameters,…
 vitaliy-grigoriev/protocol-analyzer
Fuzz testing framework for network protocols.
 damian89/extended-ssrf-search
Smart ssrf scanner using different methods like parameter brute forcing in post and get...
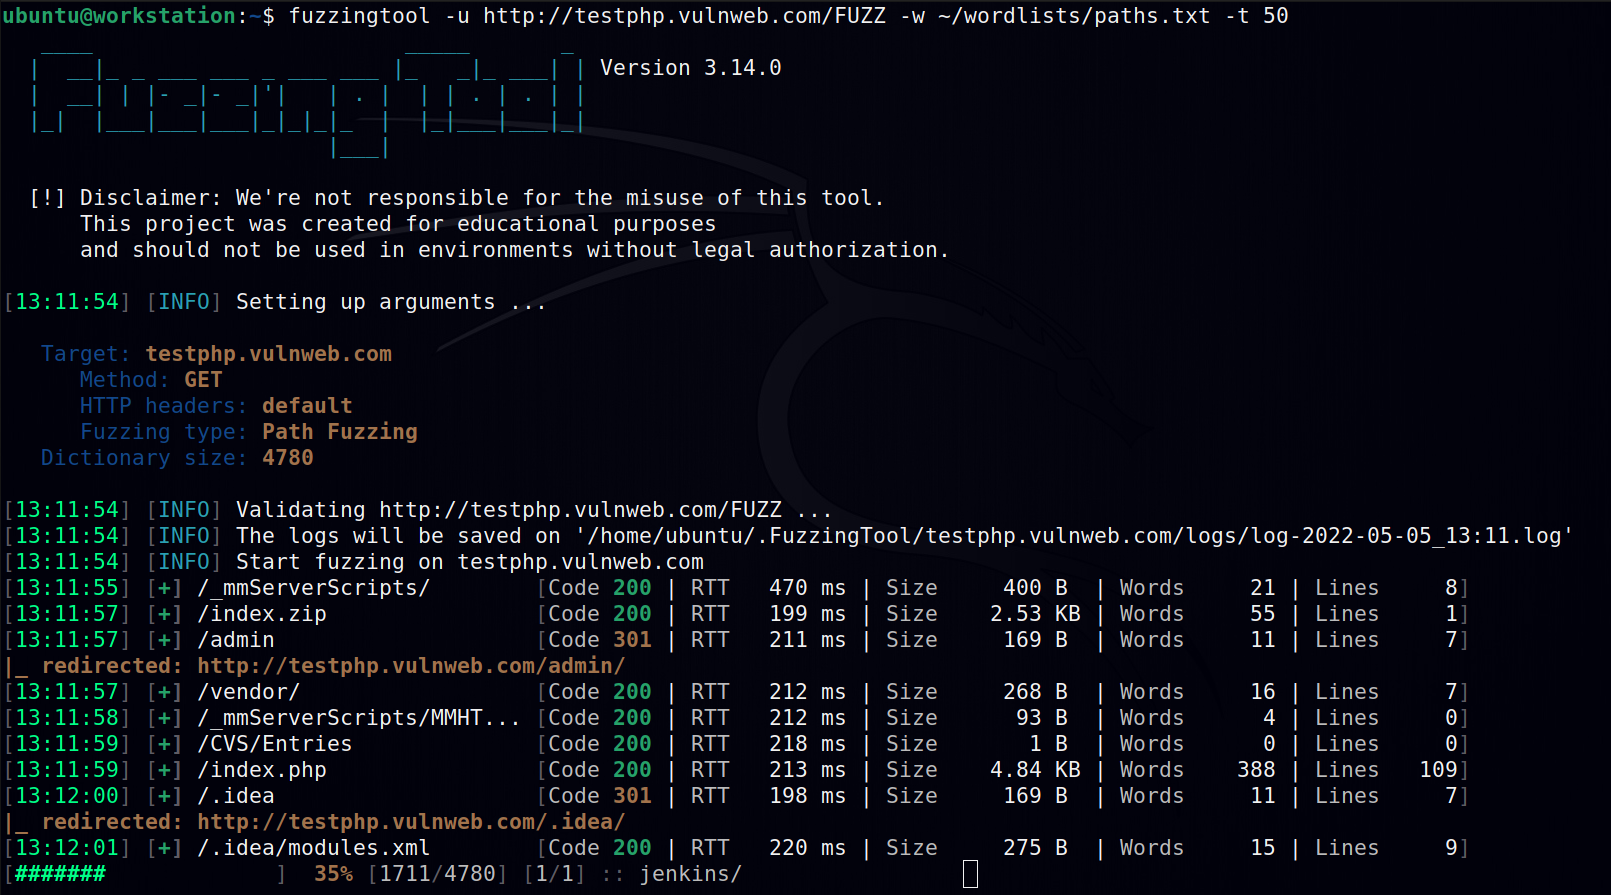 nescau-ufla/fuzzingtool
Software for fuzzing, used on web application pentestings.