
giskard-oss
 giskard-ai/giskard-oss
🐢 Open-Source Evaluation & Testing library for LLM Agents
adversarial-attackai-securityfuzzing+3
giskard-ai/giskard-oss🐢 Open-Source Evaluation & Testing library for LLM Agents
 darkflippers/unleashed-firmware
Custom firmware for Flipper Zero enabling Sub-GHz radio, NFC/RFID emulation, infrared, and BadUSB attack features for hardware security testing.
 mreza-en/cve-2021-21994_poc
Validates and exploits VMware ESXi SFCB authentication bypass (CVE-2021-21994) via a probe/fuzz harness, enabling unauthenticated CIM-XML enumeration.
 z-bool/venom-jwt
针对JWT渗透开发的漏洞验证/密钥爆破工具,针对CVE-2015-9235/空白密钥/未验证签名攻击/CVE-2016-10555/CVE-2018-0114/CVE-2020-28042的结果生成用于FUZZ,也可使用字典/字符枚举(包括JJWT)的方式进行爆破(JWT Crack)
 prikalel/django-xss-example
This repo reproduce xss attack on django 4.0.1 (see CVE-2022-22818)
 mk017-hk/cve-2025-5548
Security research and technical analysis of CVE-2025-5548, a buffer overflow vulnerability affecting FreeFloat FTP Server 1.0. This repository…
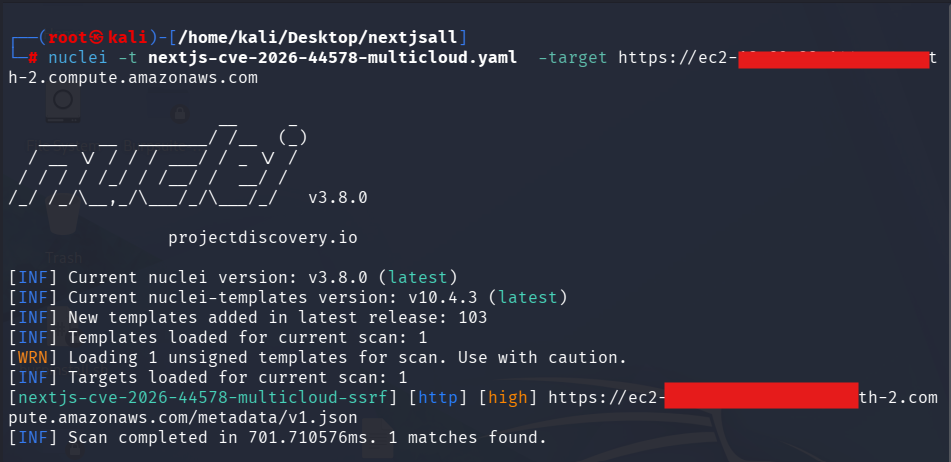 love07oj/nextjs-cve-2026-44578
Nuclei templates for detecting CVE-2026-44578 (Next.js WebSocket Upgrade SSRF) with multi-cloud metadata validation, Next.js fingerprinting, and…
 santokum/cve-2020-25478--asus-rt-ac87u-tftp-is-vulnerable-to-denial-of-service-dos-attack
ASUS RT-AC87U TFTP is vulnerable to Denial of Service(DoS) attack
 foospidy/payloads
Git All the Payloads! A collection of web attack payloads.
 cifertech/esp32-div
ESP32DIV is a multi-purpose wireless offensive and defensive toolkit powered by an ESP32
 syaifulandy/cve-2024-38475
CVE-2024-38475 Scanner using FFUF + Seclists
 geeoon/fault-injection-finder
Automatically find and execute fault injection attacks
 kagancapar/cve-2022-29072
7-Zip through 21.07 on Windows allows privilege escalation and command execution when a file with the .7z extension is dragged to the Help>Contents…
 gogo2464/cve-2024-5124
Exploit for CVE-2024-5124 targeting ChuanhuChatGPT via TLS timing side-channel attack. Uses tlsfuzzer to perform character-by-character credential…
 abrewer251/cve-2024-38475_sonicboom_apache_url_traversal_poc
Proof-of-concept scanner for CVE-2024-38475 (SonicBoom) Apache URL traversal. Automates TLS negotiation, directory scanning, traversal verification,…
 teycir/burpapisecuritysuite
Burp Suite extension for API security testing with 15 attack types, 108+ payloads, intelligent fuzzing, BOLA/IDOR detection, AI integration, and…