

ESP32-DIV
 cifertech/esp32-div
ESP32DIV is a multi-purpose wireless offensive and defensive toolkit powered by an ESP32
bluetooth-securityeducationembedded-systems-security+8
4.2k
cifertech/esp32-divESP32DIV is a multi-purpose wireless offensive and defensive toolkit powered by an ESP32
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 dozermx/argus
Multi-phase reconnaissance and attack-surface scanner that maps domains, IPs, ASNs, cloud assets, and CVEs into a knowledge graph with CVSS scoring…
 portswigger/splitting-the-email-atom
Research materials and tooling for exploiting email address parser discrepancies to bypass access controls, including fuzzers, Hackvertor tags, CSS…
 x3omdax/penbox
PenBox - A Penetration Testing Framework - The Tool With All The Tools , The Hacker's Repo
 popclom/cve-2025-5548
Step-by-step guide to exploit a buffer overflow in FreeFloat FTP Server using Python fuzzing, Immunity Debugger with mona.py, and IDA Free for binary…
 foospidy/payloads
Git All the Payloads! A collection of web attack payloads.
 rfidtool/esp-rfid-tool
A tool for logging data/testing devices with a Wiegand Interface. Can be used to create a portable RFID reader or installed directly into an existing…
 trailofbits/manticore
Symbolic execution tool
 ya551n3/bug-bounty-wordlists
Curated collection of wordlists for bug bounty hunting, covering directories, subdomains, parameters, usernames, passwords, and web fuzzing payloads.
 airbus-seclab/gustave
GUSTAVE is a fuzzing platform for embedded OS kernels. It is based on QEMU and AFL (and all of its forkserver siblings). It allows to fuzz OS kernels…
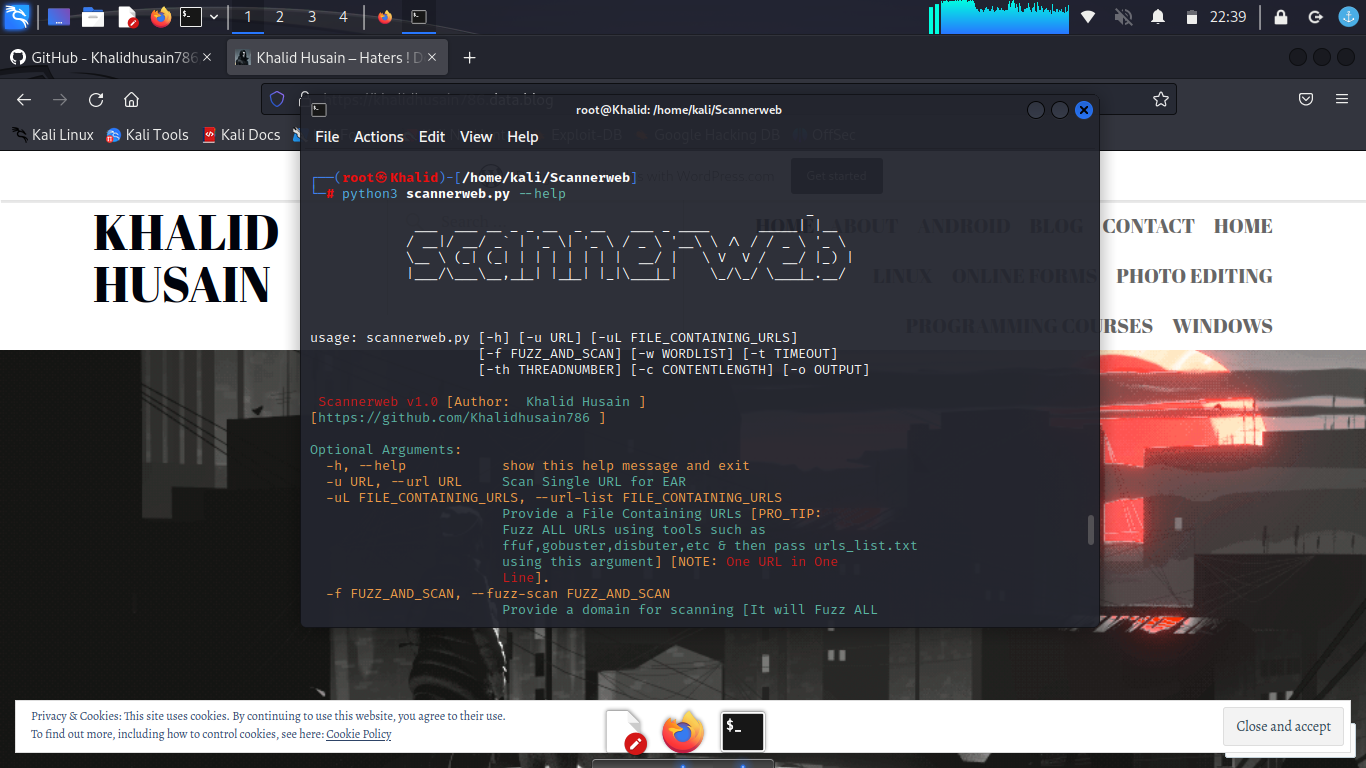 khalidhusain786/scannerweb
Python3 vulnerability scanner that fuzzes all URLs of a target website and scans them for web vulnerabilities, with optional GoBuster integration for…
 alphaseclab/all-my-collection-repos
All Security Resource Collections Repos That I Published.
 nathan-luevano/silica
Exhaustive differential validation of all 4.3B AArch64 instruction encodings.
 asciimoo/exrex
Irregular methods on regular expressions
 hycqaq/logitech-g-cloud-ghostlock-cve-2026-43499
罗技云掌机 · GhostLock CVE-2026-43499 root 尝试
 bw3ll/sharem
SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…