
 henshin/filebuster
An extremely fast and flexible web fuzzer
 google/boringssl
Fork of OpenSSL implementing TLS, cryptographic primitives, and X.509 certificate handling for use in Chrome and Android, with no API/ABI…
 ghosttroops/scan4all
Official repository vuls Scan: 15000+PoCs; 23 kinds of application password crack; 7000+Web fingerprints; 146 protocols and 90000+ rules Port…
 yolkfull/cve-2026-52910-poc
Race reproducer and stress toolkit for CVE-2026-52910, a Linux kernel use-after-free in reuseport cBPF selector programs, with dmesg and leak checks.
 hardik05/damn_vulnerable_c_program
An example C program which contains vulnerable code for common types of vulnerabilities. It can be used to show fuzzing concepts.
 terribledactyl/cve-2025-55891
Proof-of-concept for CVE-2025-55891: heap corruption in TIFFCP.EXE via malformed TIFF file, triggering segmentation fault during LZW decompression in…
 malqr/malqr.github.io
MalQR is a collection of malicious QR Codes and Barcodes you can use to test the security of your scanners.
 trailofbits/trailmark
Build and query a graph database representation of source code
 tno-s3/wuppiefuzz
A coverage-guided REST API fuzzer developed on top of LibAFL
 trailofbits/testing-handbook
Trail of Bits Testing Handbook - appsec.guide
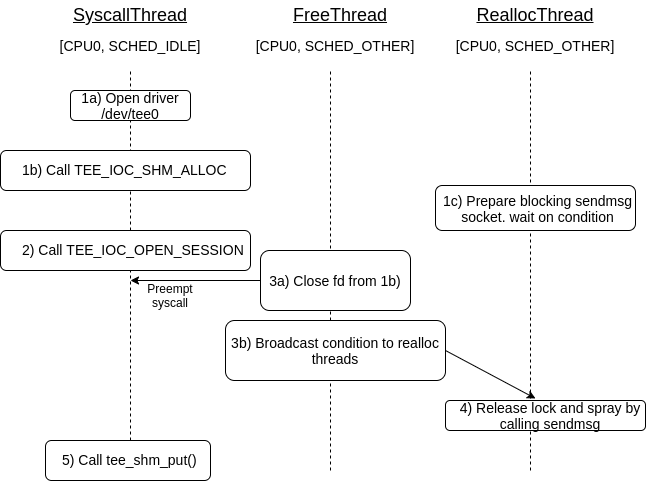 pjlantz/optee-qemu
Environment with vulnerable kernel for exploitation of the TEE driver (CVE-2021-44733)
 dukptkey/cve-2020-9273
Analysis and exploitation of an use-after-free in ProFTPd
 nevesnunes/z80-sans
OpenType font that disassembles Z80 instructions
 nccgroup/nobex
nOBEX allows emulating the PBAP, MAP, and HFP profiles to test vehicle infotainment systems and similar devices using these profiles
 webraybtl/cve-2022-1068
Modbus Slave缓冲区溢出漏洞CVE-2022-1068分析与复现
 phantomn/virtualbox_cve-2019-2525-cve-2019-2548
Proof-of-concept exploits for VirtualBox guest-to-host escape vulnerabilities CVE-2019-2525 and CVE-2019-2548, with a Python library for HGCM…
 acen28/cve-2026-26399-disclosure
Disclosure of a stack-based use-after-return vulnerability in Arduino_Core_STM32, detailing technical root cause, affected versions, and fix, with…