unleashed-firmware
Custom firmware for Flipper Zero enabling Sub-GHz radio, NFC/RFID emulation, infrared, and BadUSB attack features for hardware security testing.

Custom firmware for Flipper Zero enabling Sub-GHz radio, NFC/RFID emulation, infrared, and BadUSB attack features for hardware security testing.

Modern WiFi auditing library for ESP32 using advanced 802.11 techniques. Captures WPA/WPA2/WPA3 handshakes via PMKID extraction and CSA injection…

CANToolz - framework for black-box CAN network analysis

Predatory ESP32 Firmware

Snapshot-based coverage-guided windows kernel fuzzer

Python-based exploit development framework with payloads, encoders, and connect-back servers, focused on MIPS CPU architecture but designed for…

Disclosure of Accfly camera vulnerabilities: CVE-2020-25782, CVE-2020-25783, CVE-2020-25784, CVE-2020-25785.

PoC exploit for CVE-2018-18778: arbitrary file read in mini_httpd 1.29 via empty Host header, affecting IoT devices from Huawei, Zyxel, and others.

CANToolz - Black-box CAN network analysis framework

Standalone proof of concept for CVE-2026-86547, a NULL pointer dereference in mrubyc op_enter() through 4.0.0.

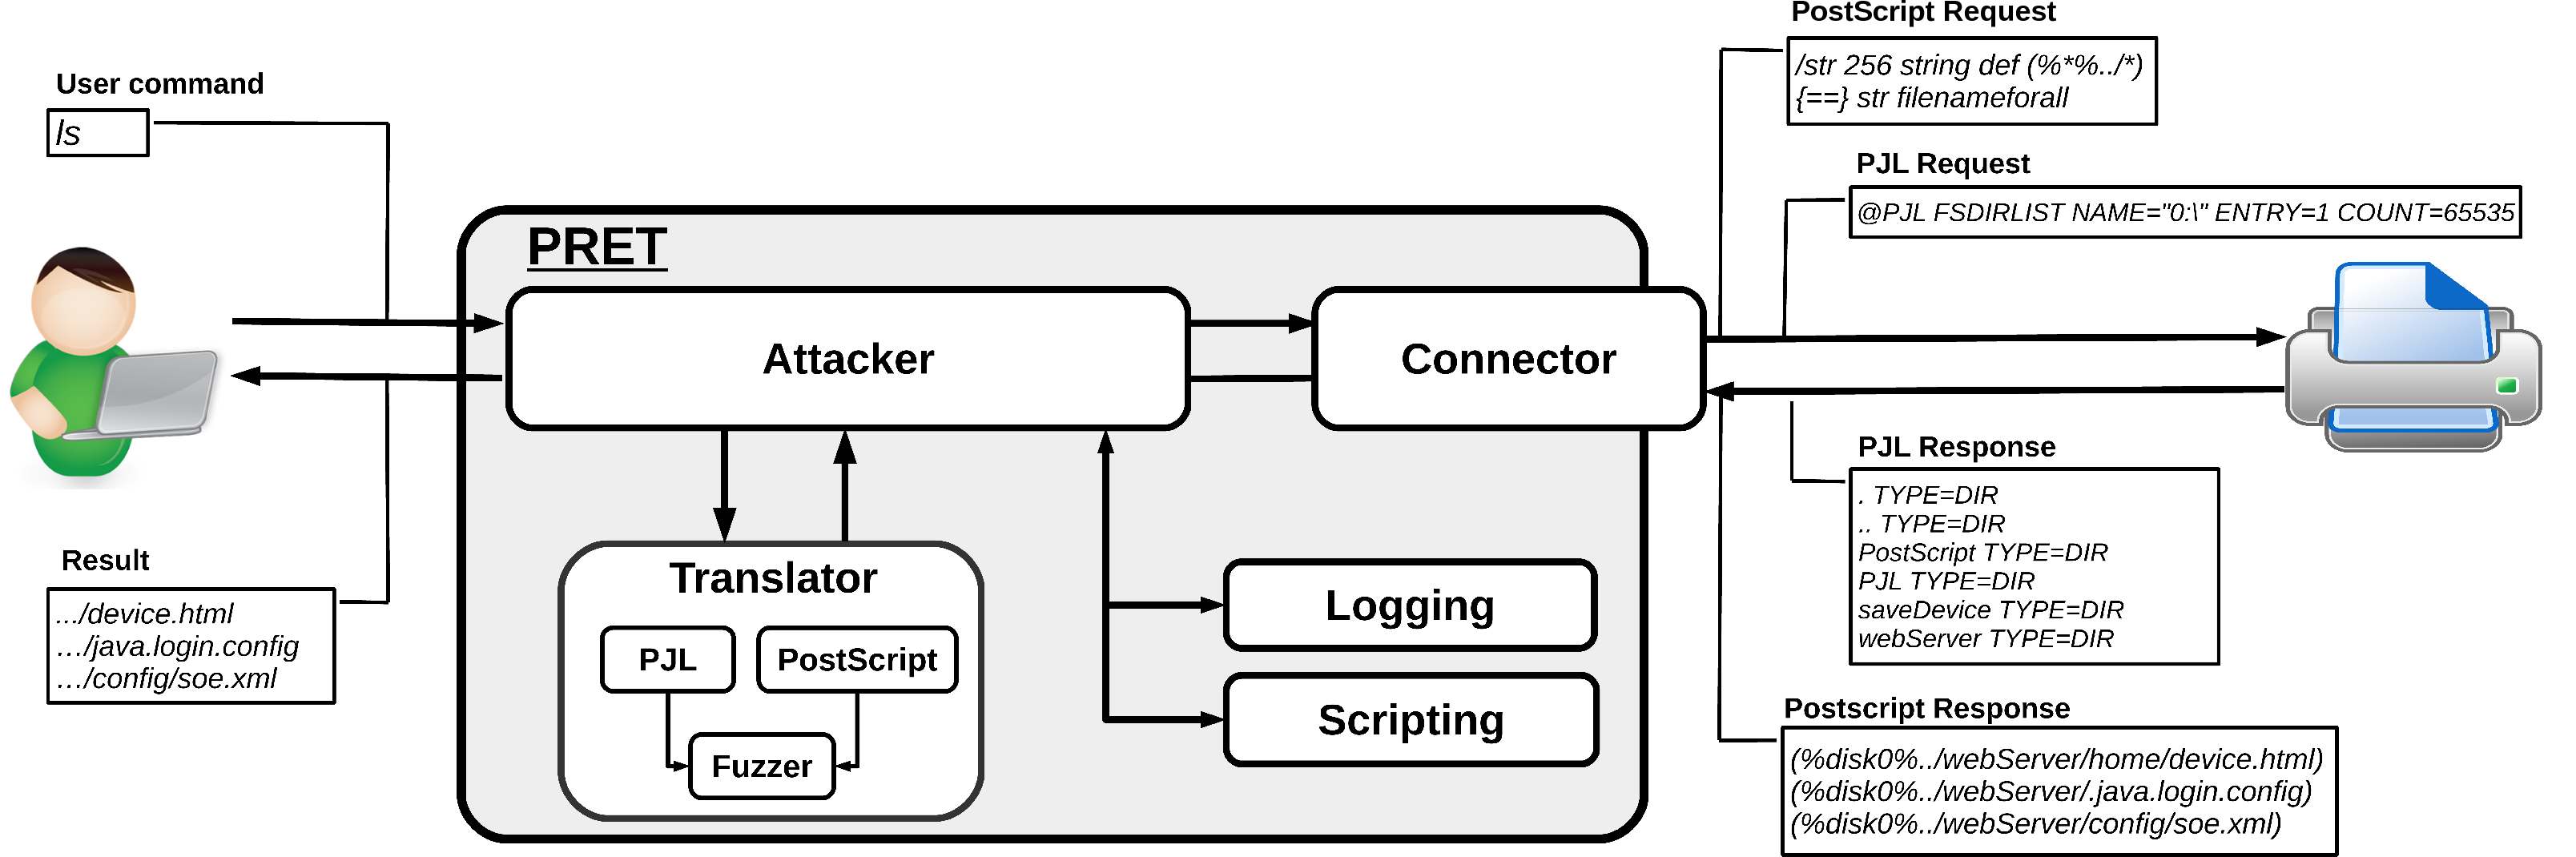
Printer Exploitation Toolkit - The tool that made dumpster diving obsolete.

GUSTAVE is a fuzzing platform for embedded OS kernels. It is based on QEMU and AFL (and all of its forkserver siblings). It allows to fuzz OS kernels…

A tool for logging data/testing devices with a Wiegand Interface. Can be used to create a portable RFID reader or installed directly into an existing…

Real-time GPS signal simulator for bladeRF

⭐⭐ Join us at SNIA SDC for the SMB3 IO Lab (September 28 - October 1, 2026), see upcoming Interoperability Events

Automated Application Generation for Stack Overflow Types on Wireless Routers

EDID (Enhanced Display Identification Data) Fuzzer

Proof-of-concept exploit for CVE-2026-85769, a heap out-of-bounds read in libtpms TPM 2.0 state deserialization, demonstrating denial of service via…