

APIHarvester
 piratesshield/apiharvester
The one shot API attacker tool - finds the API url from the given root simulate the automated attacks
api-securityapi-security-testingcrawler+9
35
piratesshield/apiharvesterThe one shot API attacker tool - finds the API url from the given root simulate the automated attacks
 firerpa/lamda
Android Full-Stack Device Control Platform: WebRTC/H.264 remote desktop, UI/OCR/image-matching automation, one-click MITM, built-in Frida,…
 danielmiessler/seclists
Curated collection of wordlists for security assessments, including usernames, passwords, URLs, fuzzing payloads, and sensitive data patterns for…
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 pennacle-security/summit
Open-source web security testing platform: proxy, scanner and fuzzer in one CLI. By Pennacle Security.
 vmoranv/jshookmcp
A search-first, profile-aware reverse-engineering workspace for AI agents — 735 tools across 36 domains in one MCP server.
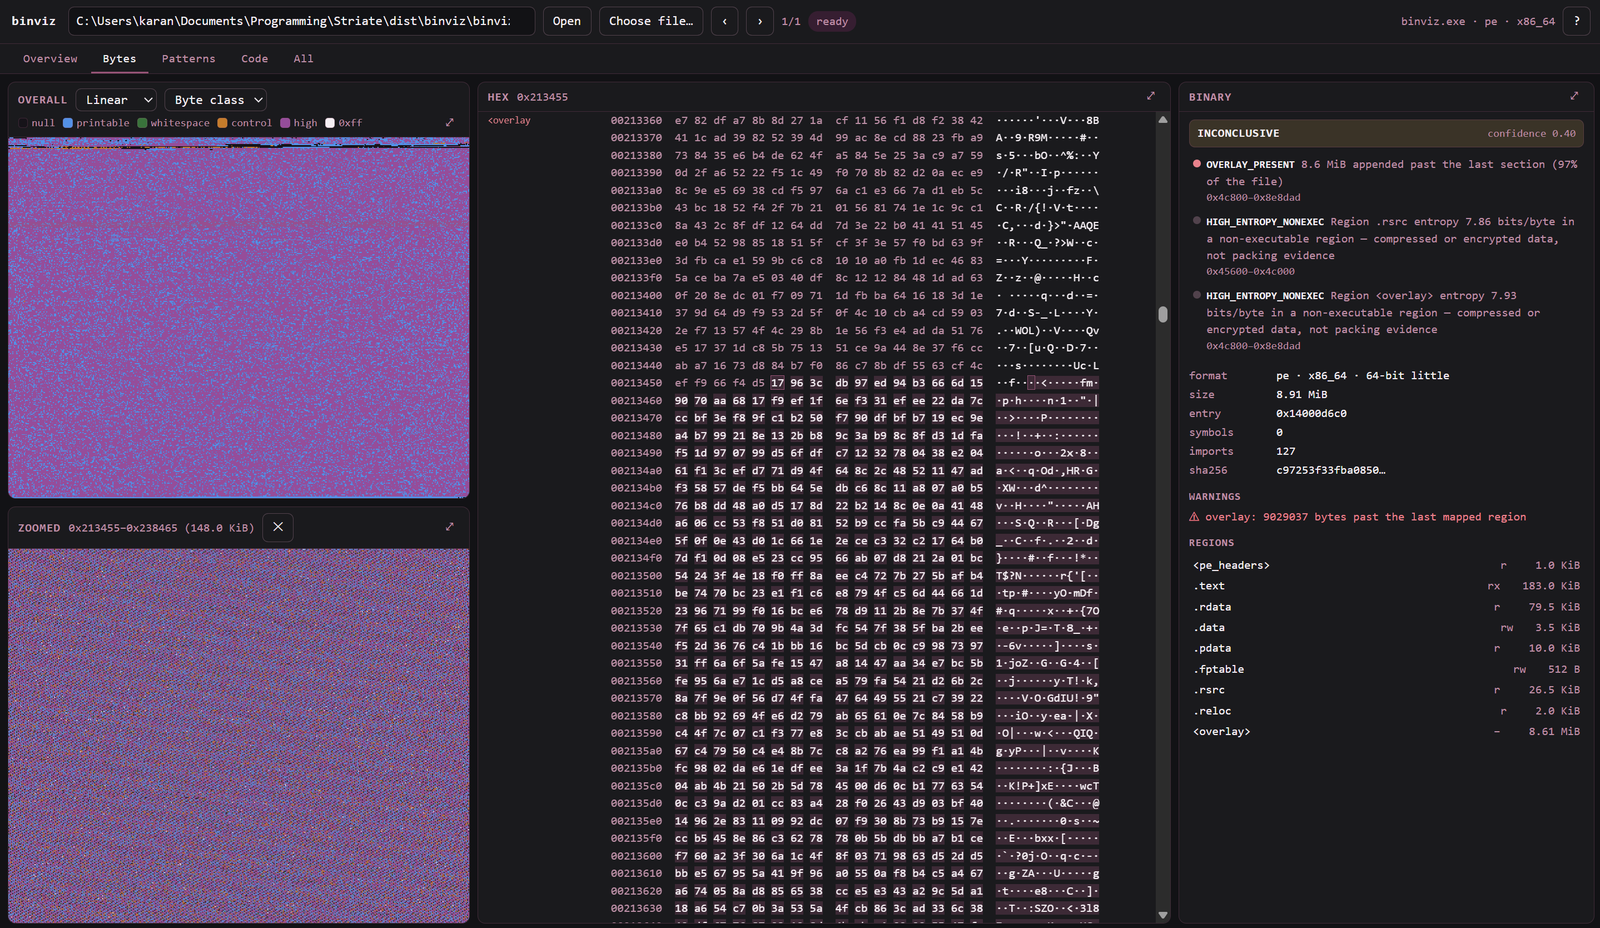 karankantaria/binviz
Binary visualiser and triage tool — entropy, byte-class and Hilbert surfaces, dot plots and control-flow graphs over one shared address-space model.
 bethington/ghidra-mcp
MCP server bridging Ghidra's reverse engineering with AI tools: 256 tools for decompilation, P-code emulation, live debugging, data flow analysis,…
 scheibling/py-log4shellscanner
Scanner for the Log4j vulnerability dubbed Log4Shell (CVE-2021-44228)
 xuehuolll/cve-2026-109618-109619-audit
CVE-2026-109618/109619 — PHP session.upload_progress pre-auth RCE. Exploit research: remote ASLR chain, PoC & patch analysis.
 gal-nagli/shockwave-oss
Curated collection of bug bounty tips, one-liners, and automation workflows for recon, fuzzing, and web exploitation, with private nuclei templates…
 agampreet-singh/redroot
RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…
 sneakynachos/cve-2026-85048-the-gpu-died
Reproducer and technical analysis for CVE-2026-85048, a Chrome viz surface use-after-free in the GPU process, with ASAN unit tests and browser…
 rat5ak/cve-2026-41285-openbsd-v6daemons-go-brrr
One IPv6 ND option with length zero. One missing check. Daemon walks backward and lives in the loop. Reported to OpenBSD, fixed, CVE assigned.
 ffmancera/pentesting-multitool
Different utility scripts for pentesting and hacking.
 nexxus67/cve-2010-1938
A simple Python script to test an off-by-one vulnerability in the OPIE library (CVE-2010-1938). This vulnerability affects certain FTP servers and…
 halcy0nic/cve-2023-40296
Proof of Concept for CVE-2023-40296
 bogdanticu88/ratrace
A lightweight CLI tool for systematically detecting and exploiting race conditions in web applications, APIs, and modern services.