
wtf
 0vercl0k/wtf
Distributed, code-coverage guided snapshot-based fuzzer for user and kernel-mode targets on Windows and Linux, with emulator and hypervisor backends.
binary-analysisdynamic-analysis-sandboxingexploitation+2
1.8k
0vercl0k/wtfDistributed, code-coverage guided snapshot-based fuzzer for user and kernel-mode targets on Windows and Linux, with emulator and hypervisor backends.
 microsoft/windowsprotocoltestsuites
⭐⭐ Join us at SNIA SDC for the SMB3 IO Lab (September 28 - October 1, 2026), see upcoming Interoperability Events
 microsoft/onefuzz
A self-hosted Fuzzing-As-A-Service platform
 hackinglz/maps_scanner
MAPS cloud scanner and response parser for Microsoft Defender research.
 0vercl0k/cve-2021-24086
Proof of concept for CVE-2021-24086, a NULL dereference in tcpip.sys triggered remotely.
 microsoft/restler-fuzzer
RESTler is the first stateful REST API fuzzing tool for automatically testing cloud services through their REST APIs and finding security and…
 0neb1n/cve-2020-16947
Proof-of-concept exploit for CVE-2020-16947, a Microsoft Outlook RCE triggered by malformed HTML content leading to a heap buffer overflow and remote…
 personnumber3377/dns_client_fuzzing
Fuzzing the Microsoft Windows DNS client library. Inspired by CVE-2026-41096.
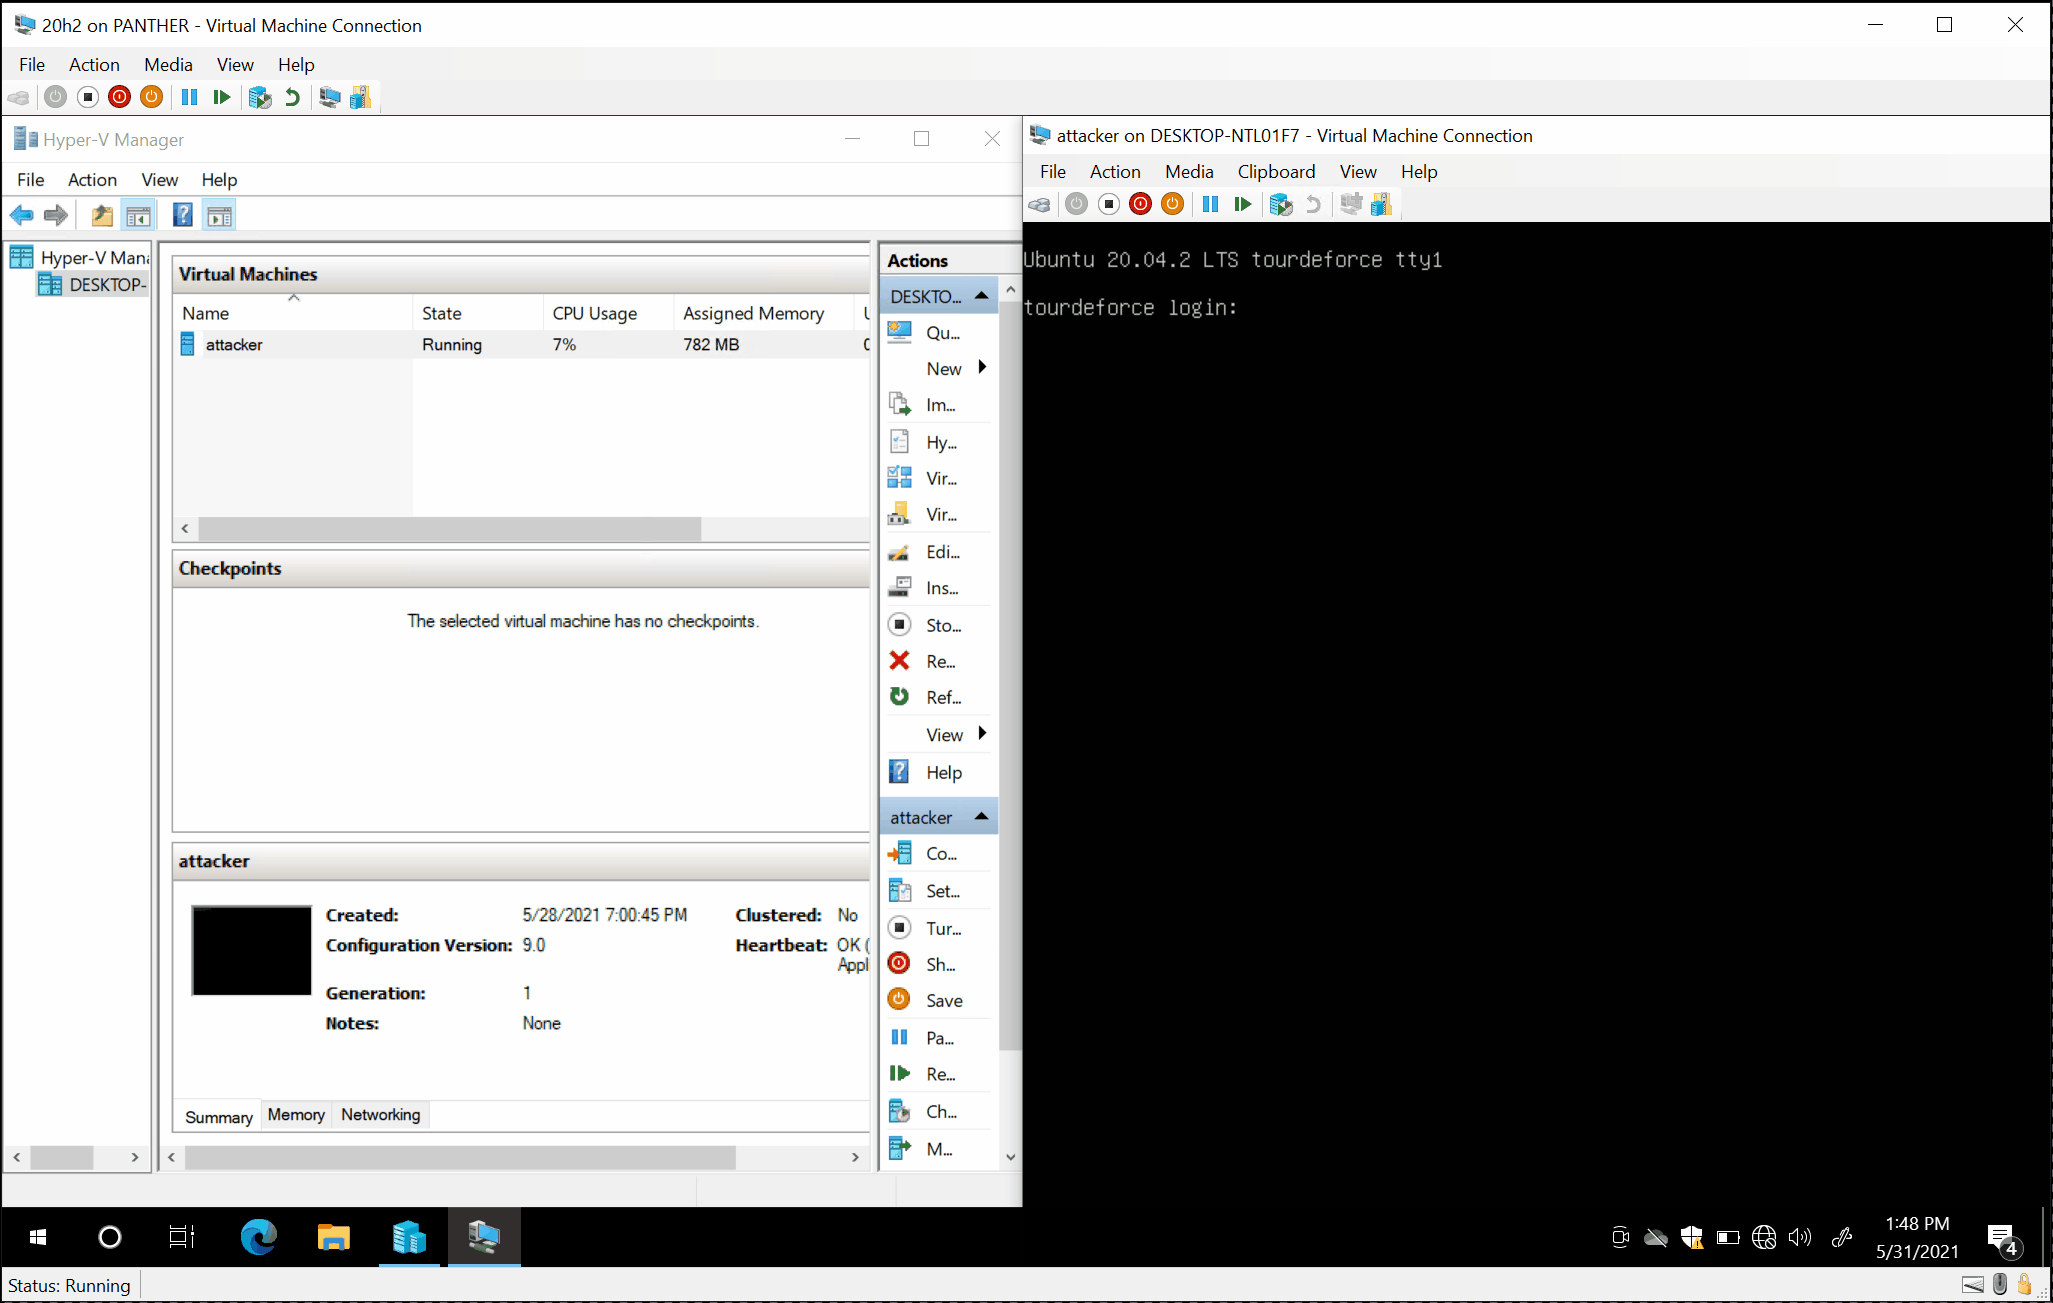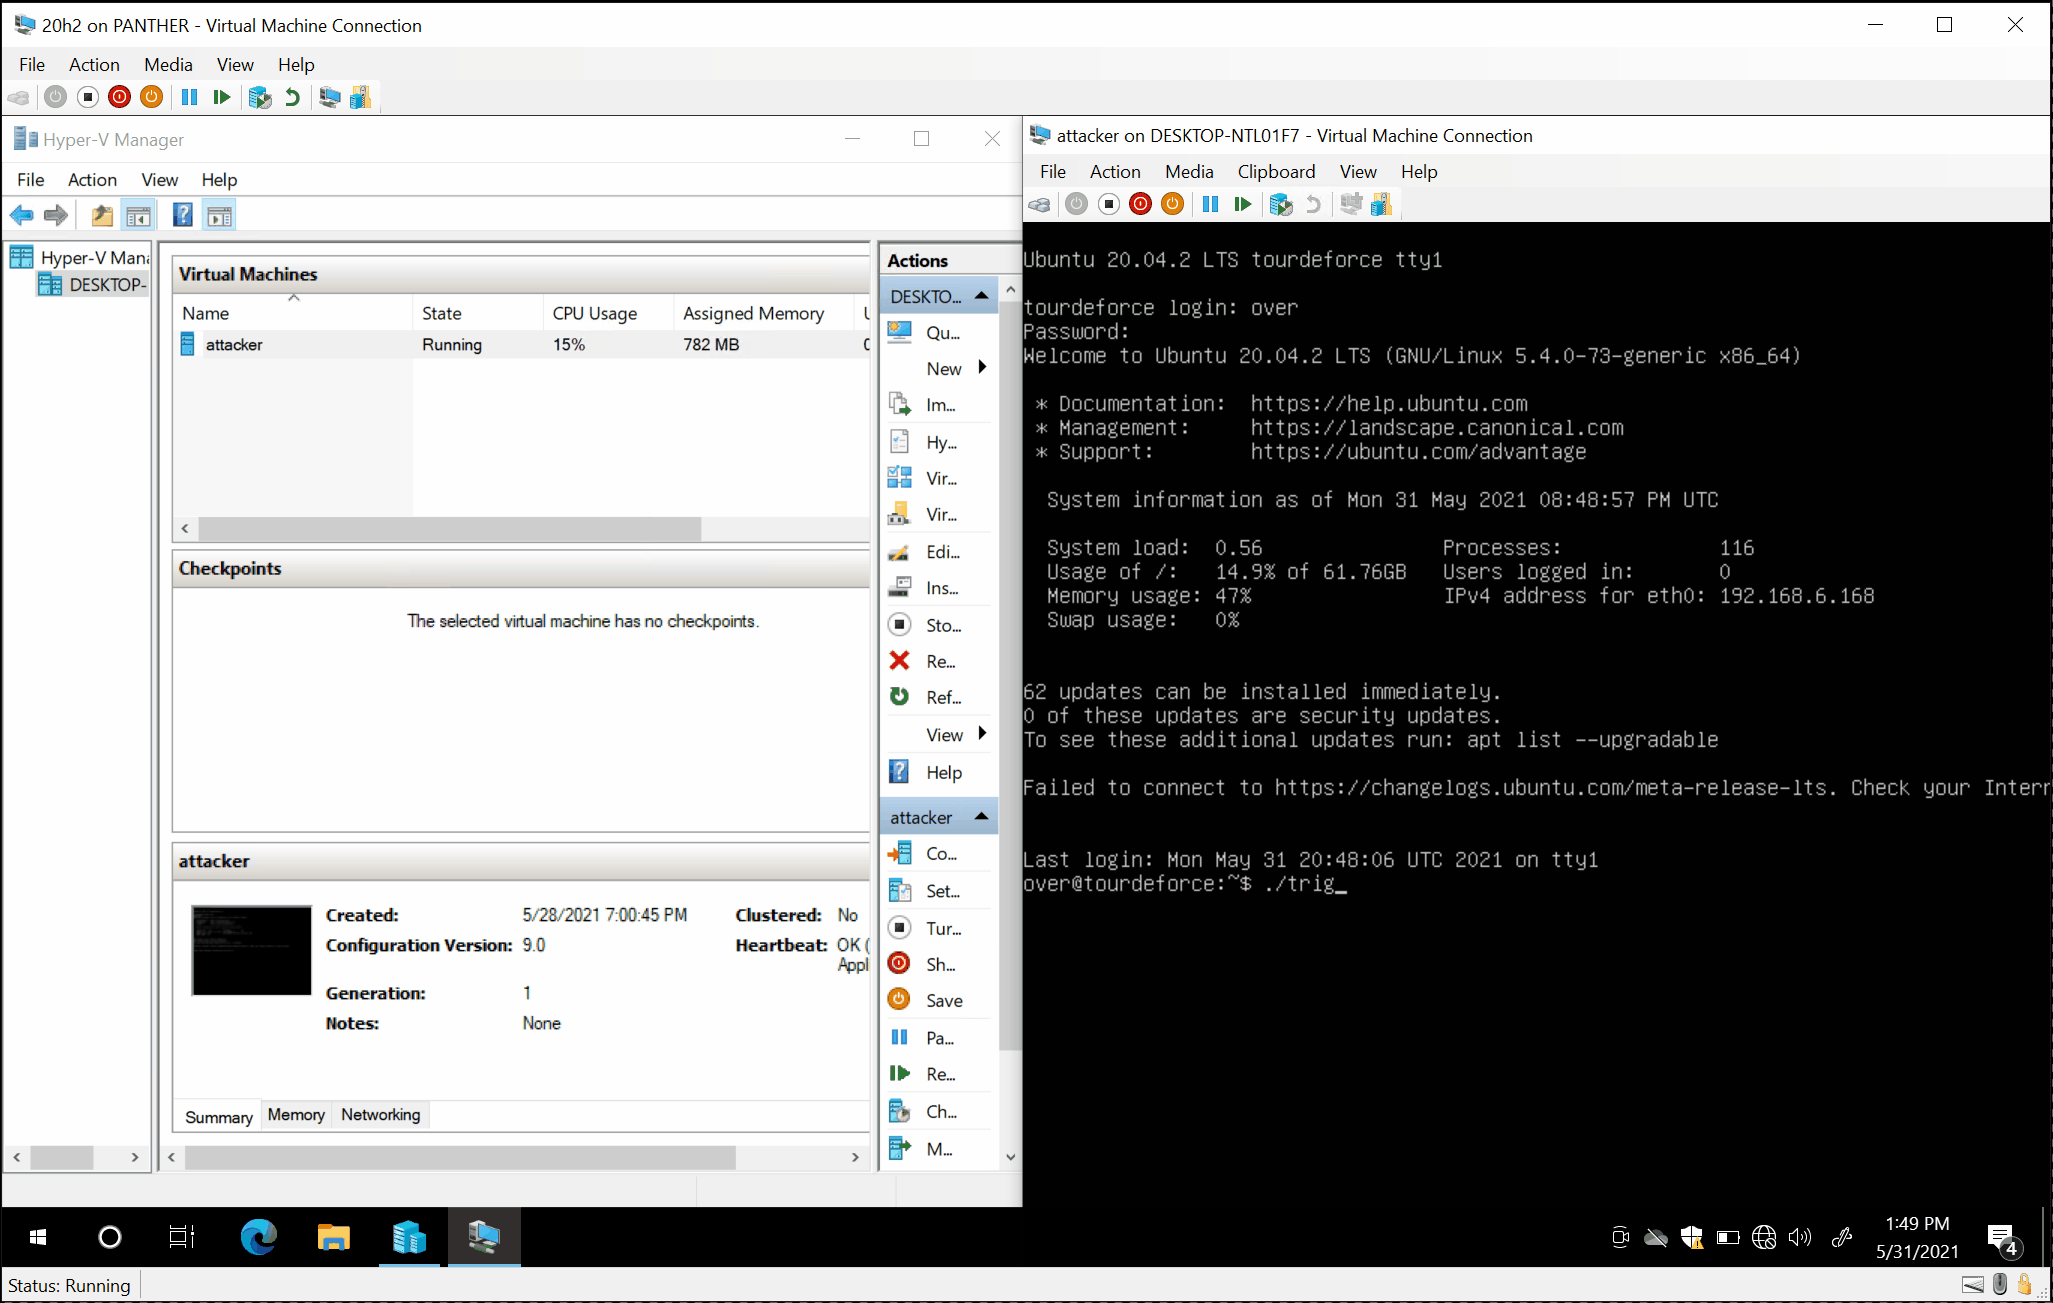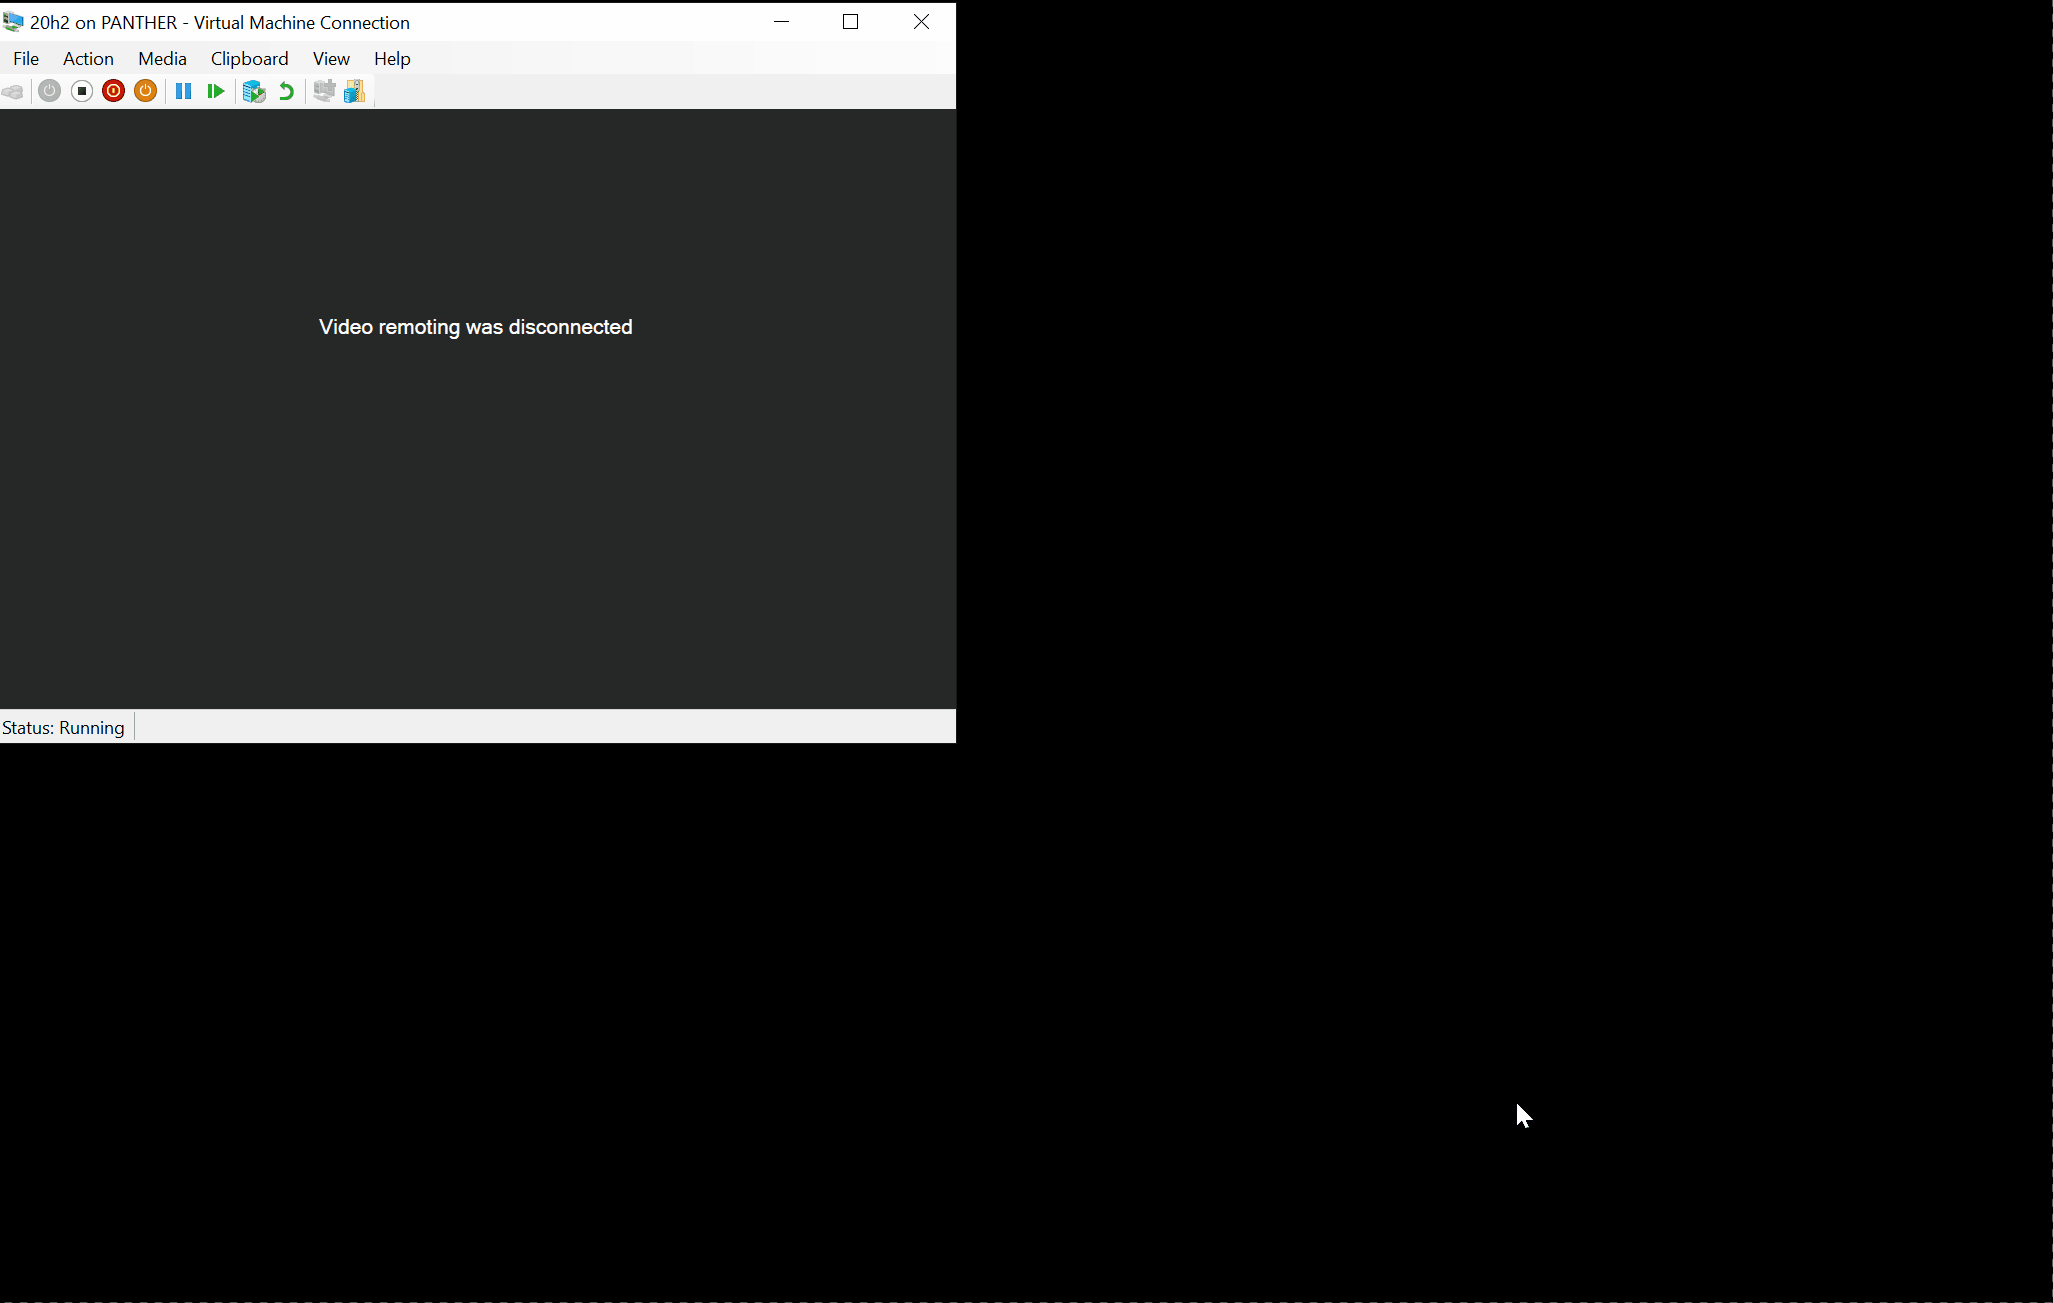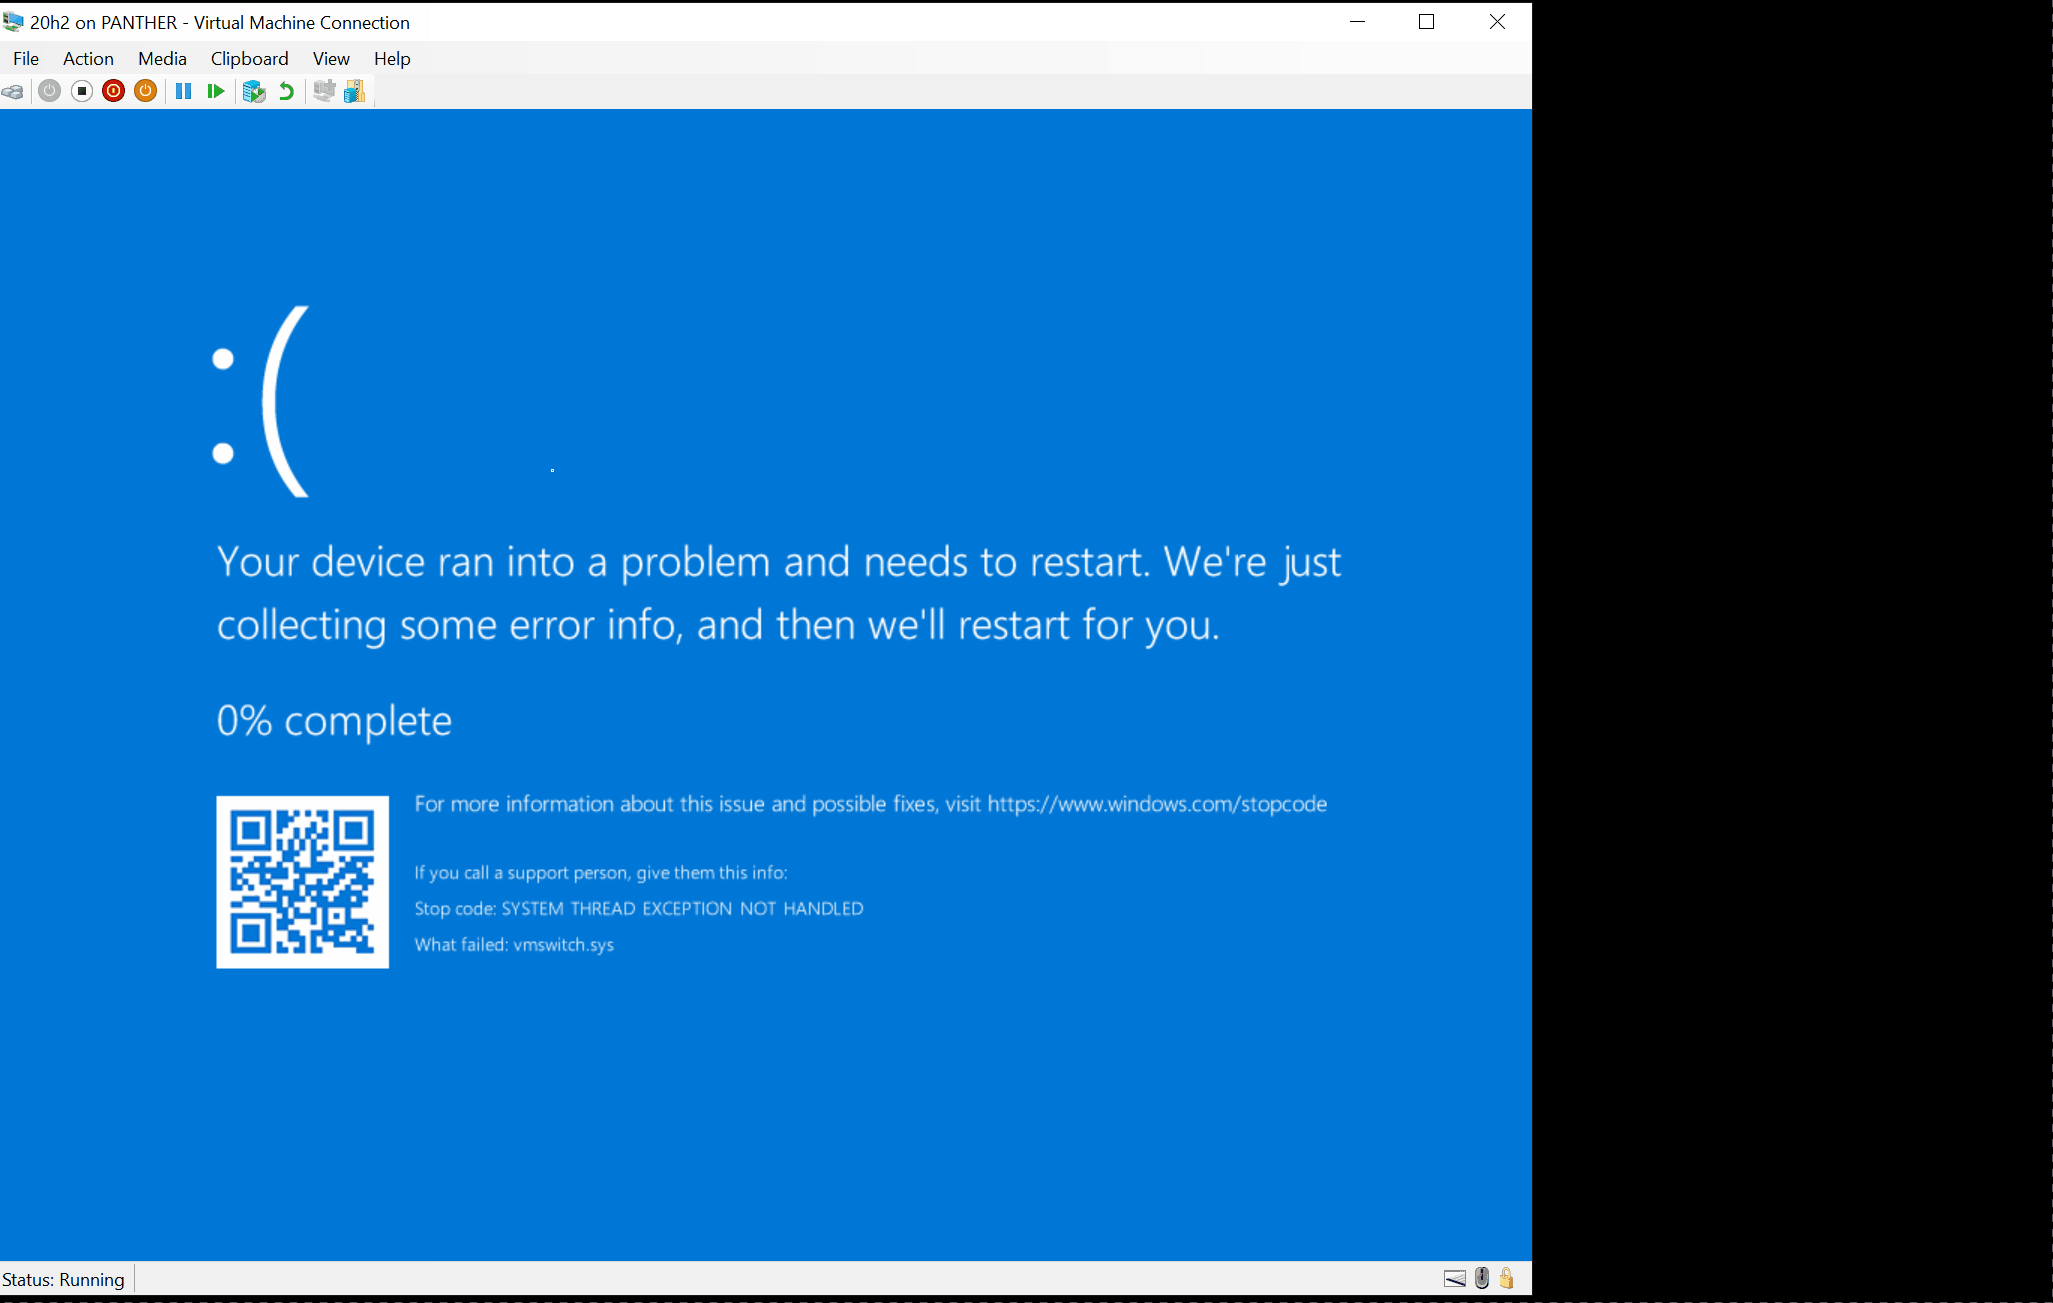 0vercl0k/cve-2021-28476
PoC for CVE-2021-28476 a guest-to-host "Hyper-V Remote Code Execution Vulnerability" in vmswitch.sys.
 malwareman007/cve-2022-26937
POC Of CVE-2022-26937
 hyunjungg/cve-2025-62821
Microsoft HEIF Extension (msheif_store.dll) OOB-read