

yakit
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
command-and-controlexploit-frameworksfuzzing+9
7.7k
yaklang/yakitAll-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
 jiangsir404/poc-s
POC-T强化版本 POC-S , 用于红蓝对抗中快速验证Web应用漏洞, 对功能进行强化以及脚本进行分类添加,自带dnslog等, 平台补充来自vulhub靶机及其他开源项目的高可用POC

 0xacb/recollapse
Black-box regex fuzzing tool that generates payloads to bypass input validations, discover normalizations, and evade WAFs in web applications.
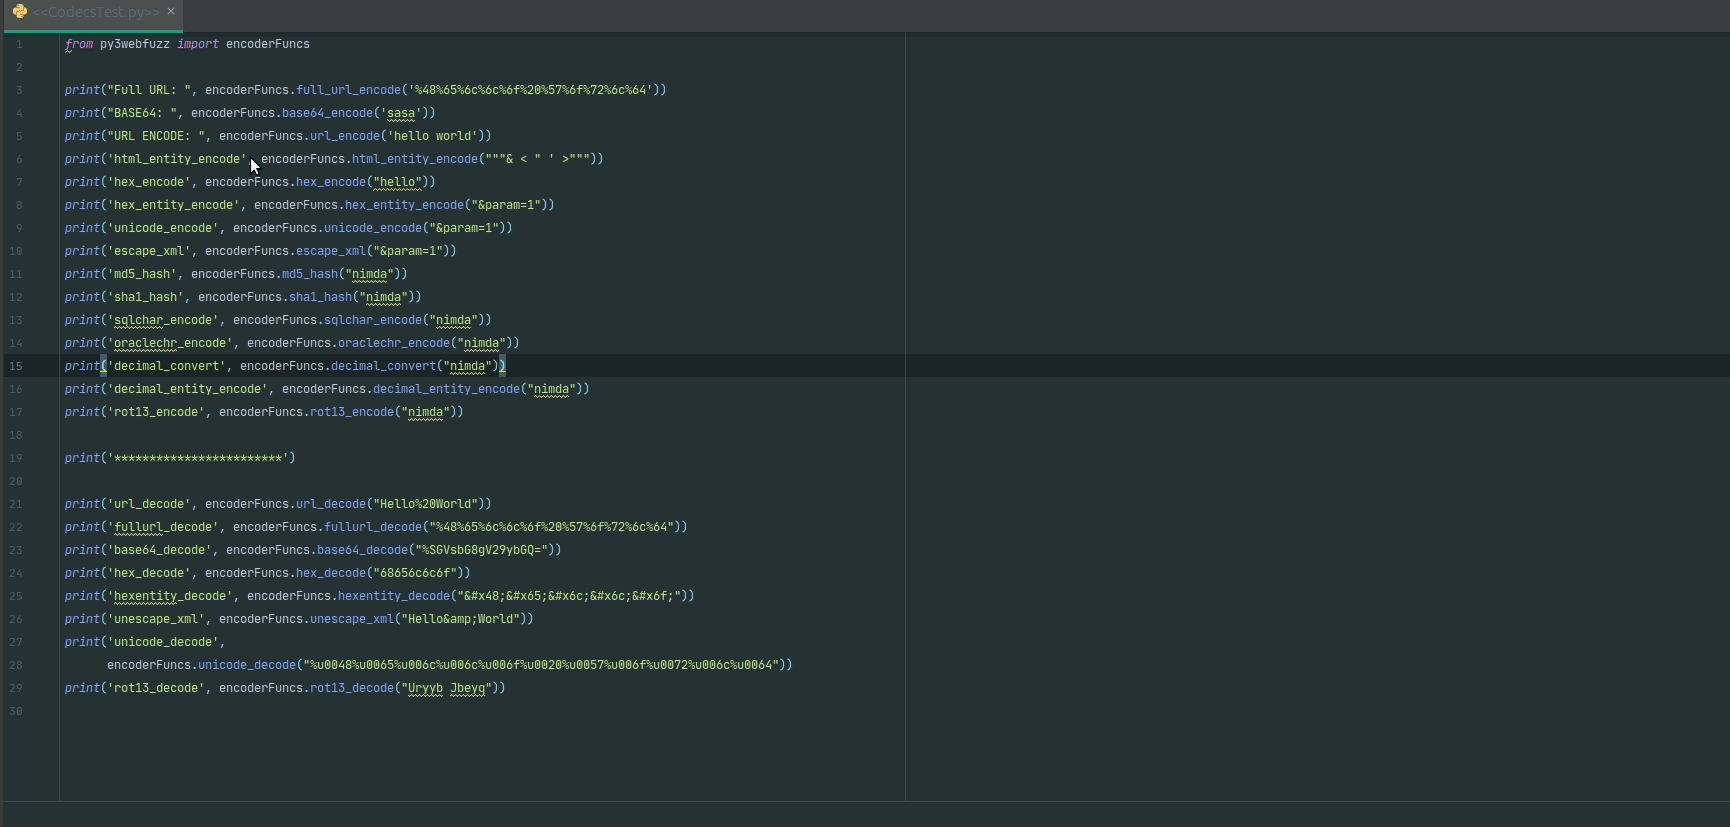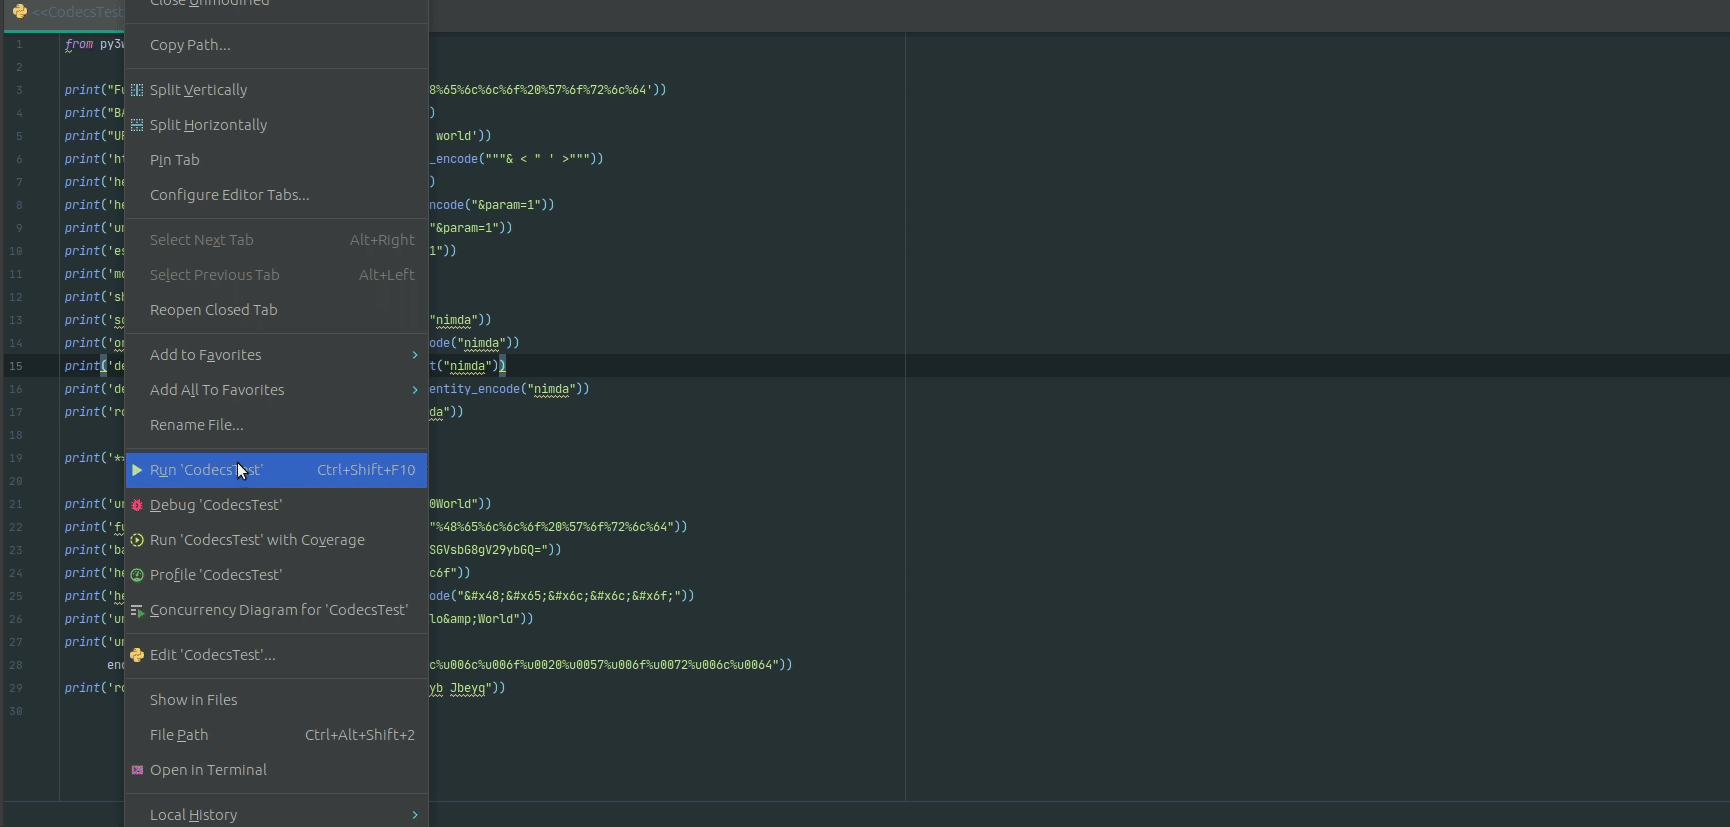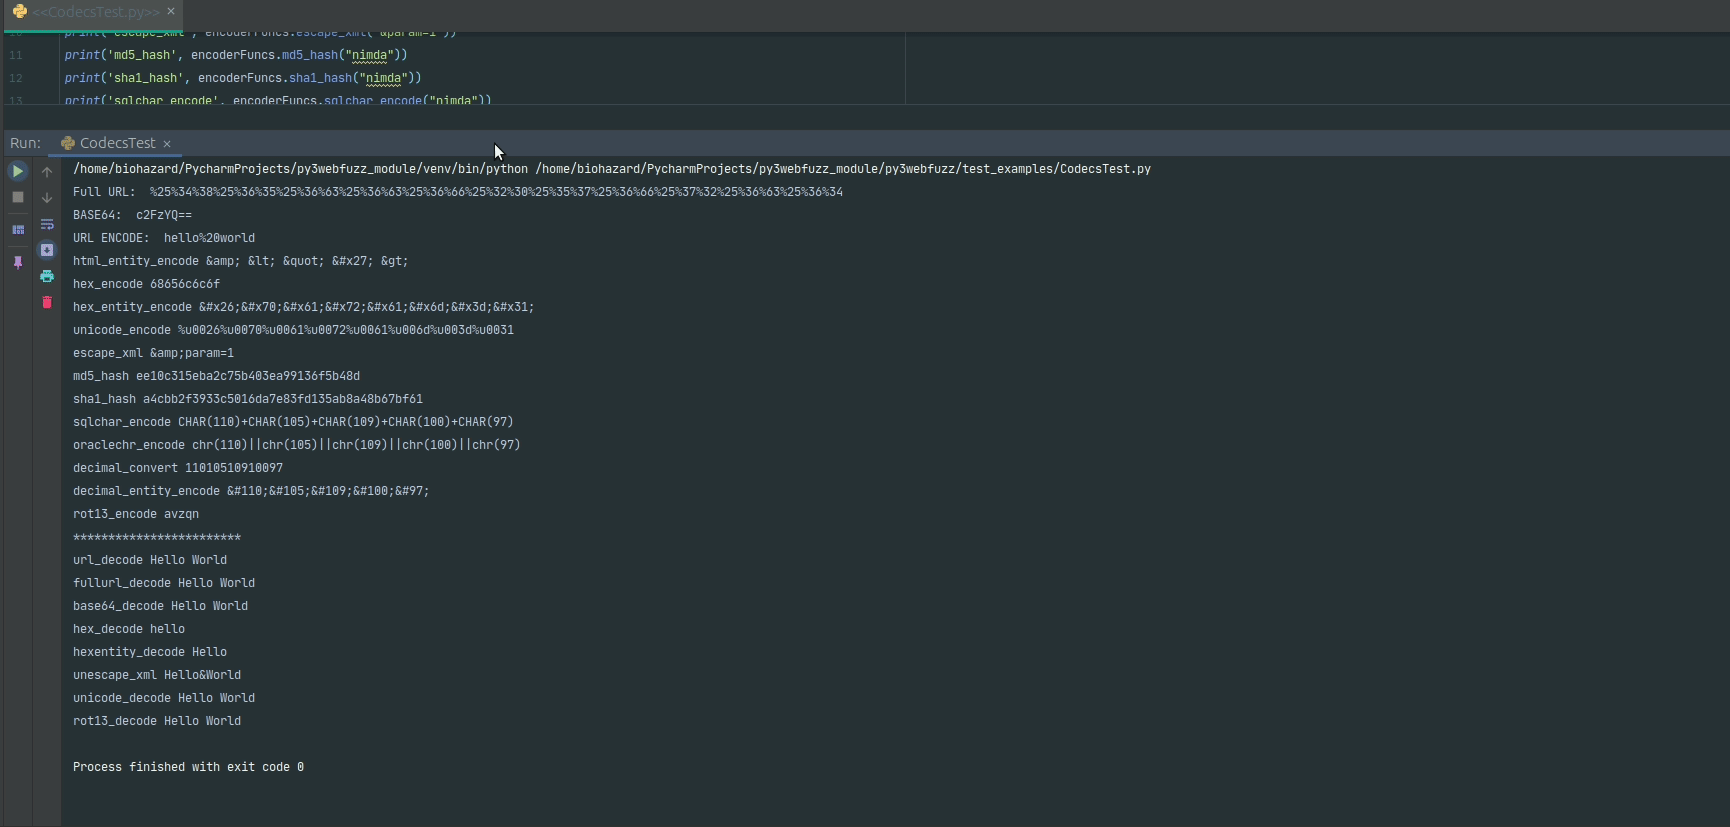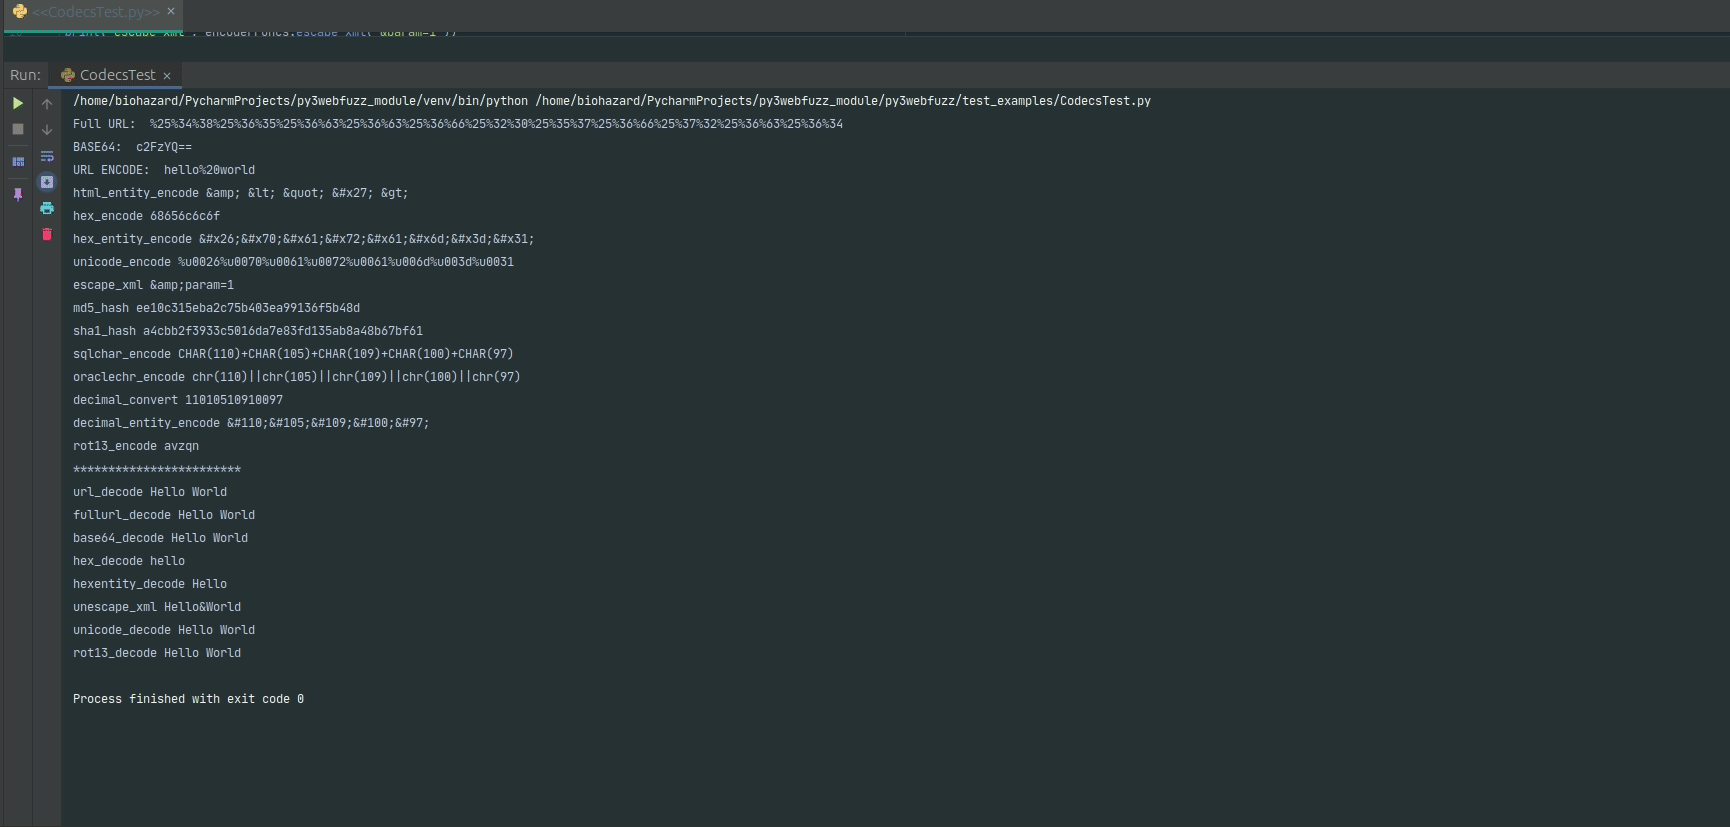 jangelesg/py3webfuzz
A Python3 module to assist in fuzzing web applications
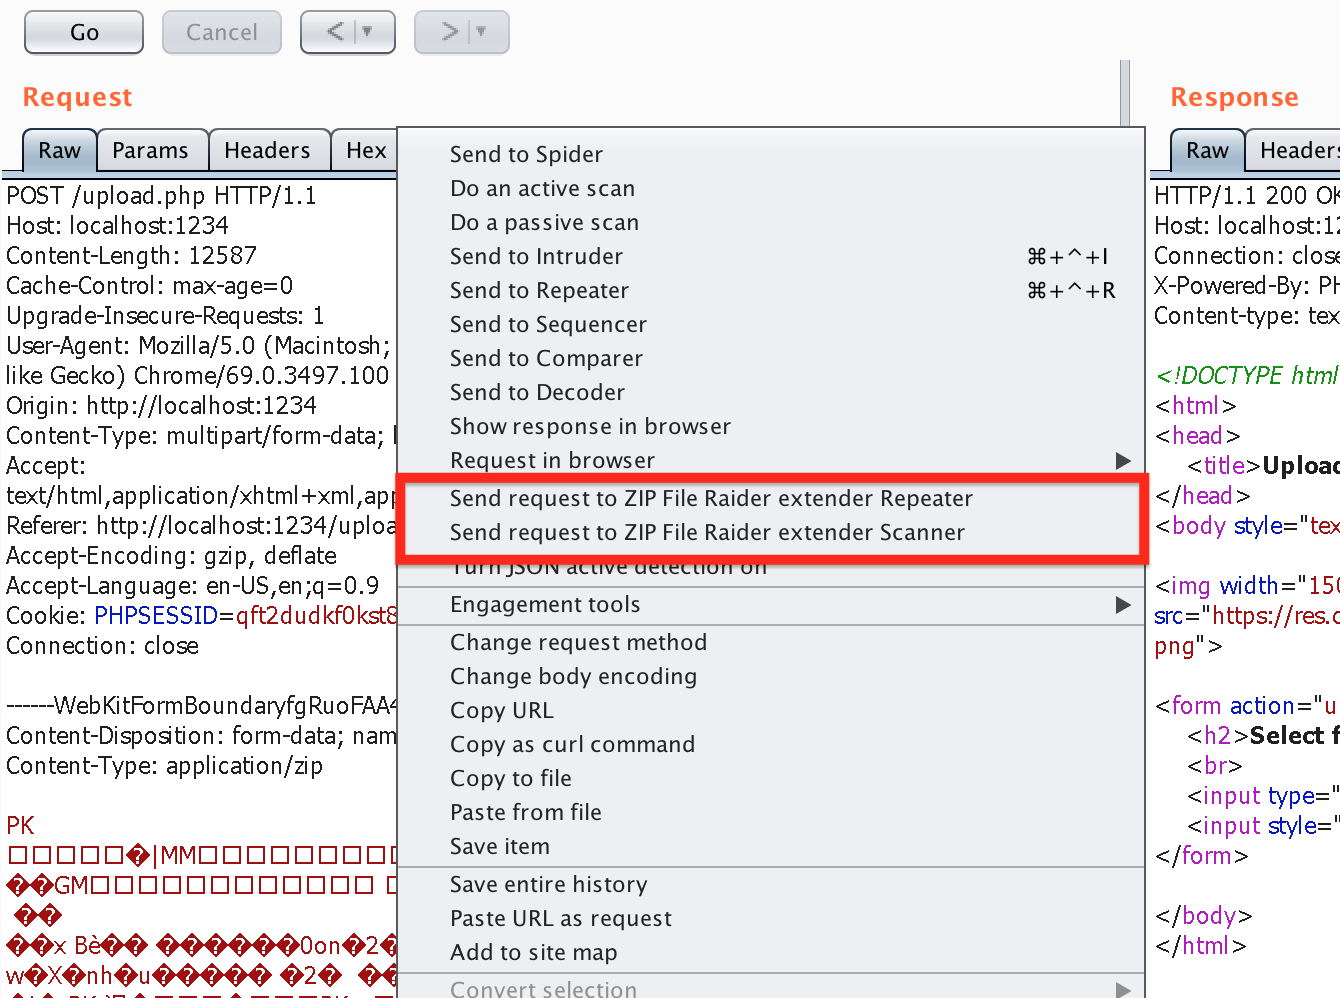 destine21/zipfileraider
ZIP File Raider - Burp Extension for ZIP File Payload Testing
 bishopfox/joro
A collaborative web exploitation framework.
 dark-lbp/isf
ISF(Industrial Control System Exploitation Framework),a exploitation framework based on Python
 domienschepers/wifi-framework
Wi-Fi Framework for creating proof-of-concepts, automated experiments, test suites, fuzzers, and more.
 bahaabdelwahed/killshot
A Penetration Testing Framework, Information gathering tool & Website Vulnerability Scanner
 fraunhofer-aisec/gallia
Extendable pentesting framework for automotive UDS interfaces, enabling reproducible scans, diagnostic trouble code reading, and post-processing via…
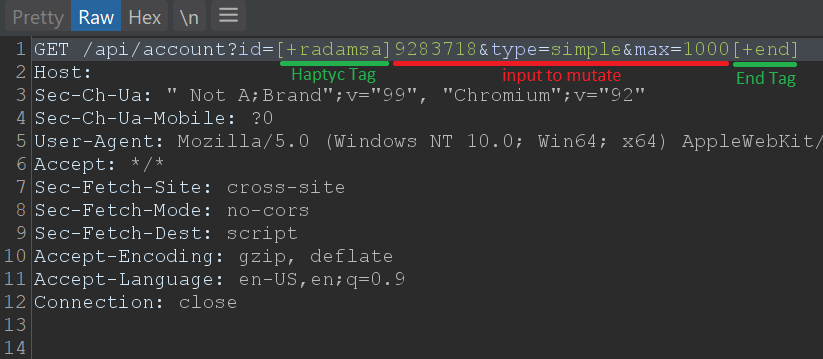 defparam/haptyc
Python library for Turbo Intruder that adds payload position support and Sniper/Clusterbomb/Pitchfork attack types with tag-based test generation for…
 luisfontes19/xxexploiter
Tool to help exploit XXE vulnerabilities
 nytrorst/xssfuzzer
XSS Fuzzer is a tool which generates XSS payloads based on user-defined vectors and fuzzing lists.
 agampreet-singh/redroot
RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…
 jvbotelho/cve-2026-69243-poc-aiohttp-smuggling
Reproduces aiohttp CWE-444 request smuggling via rejected WebSocket upgrades, with Python/Rust payloads and Docker lab demonstrating proxy…
 fozavci/viproy-voipkit
VIPROY - VoIP Pen-Test Kit for Metasploit Framework