

LLMMap
 hellsender01/llmmap
Automated prompt injection testing framework for LLM-integrated applications with dual-LLM architecture.
ai-securityapi-security-testingdynamic-analysis-sandboxing+6
205
hellsender01/llmmapAutomated prompt injection testing framework for LLM-integrated applications with dual-LLM architecture.
 danmcinerney/xsscrapy
XSS spider - 66/66 wavsep XSS detected
 anonmoty/xxstrike
XSStrike based XSS scanner with custom features. Detects XSS vulnerabilities in web applications.
 0xacb/recollapse
Black-box regex fuzzing tool that generates payloads to bypass input validations, discover normalizations, and evade WAFs in web applications.
 scheibling/py-log4shellscanner
Scanner for the Log4j vulnerability dubbed Log4Shell (CVE-2021-44228)
 tismayil/fastfuz-chrome-ext
Chrome extension for fast web fuzzing to discover hidden files and directories during penetration testing and vulnerability analysis.
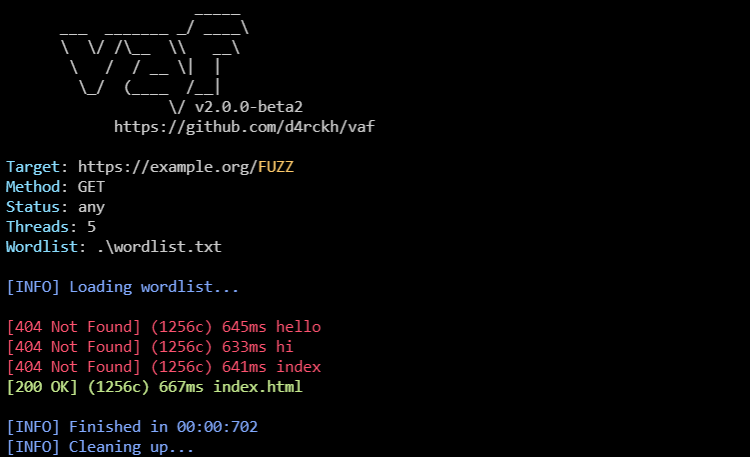 andreiverse/vaf
Multi-threaded web fuzzer for URL path, HTTP header, and POST data brute-forcing with proxy support, status code filtering, and reflexive content…
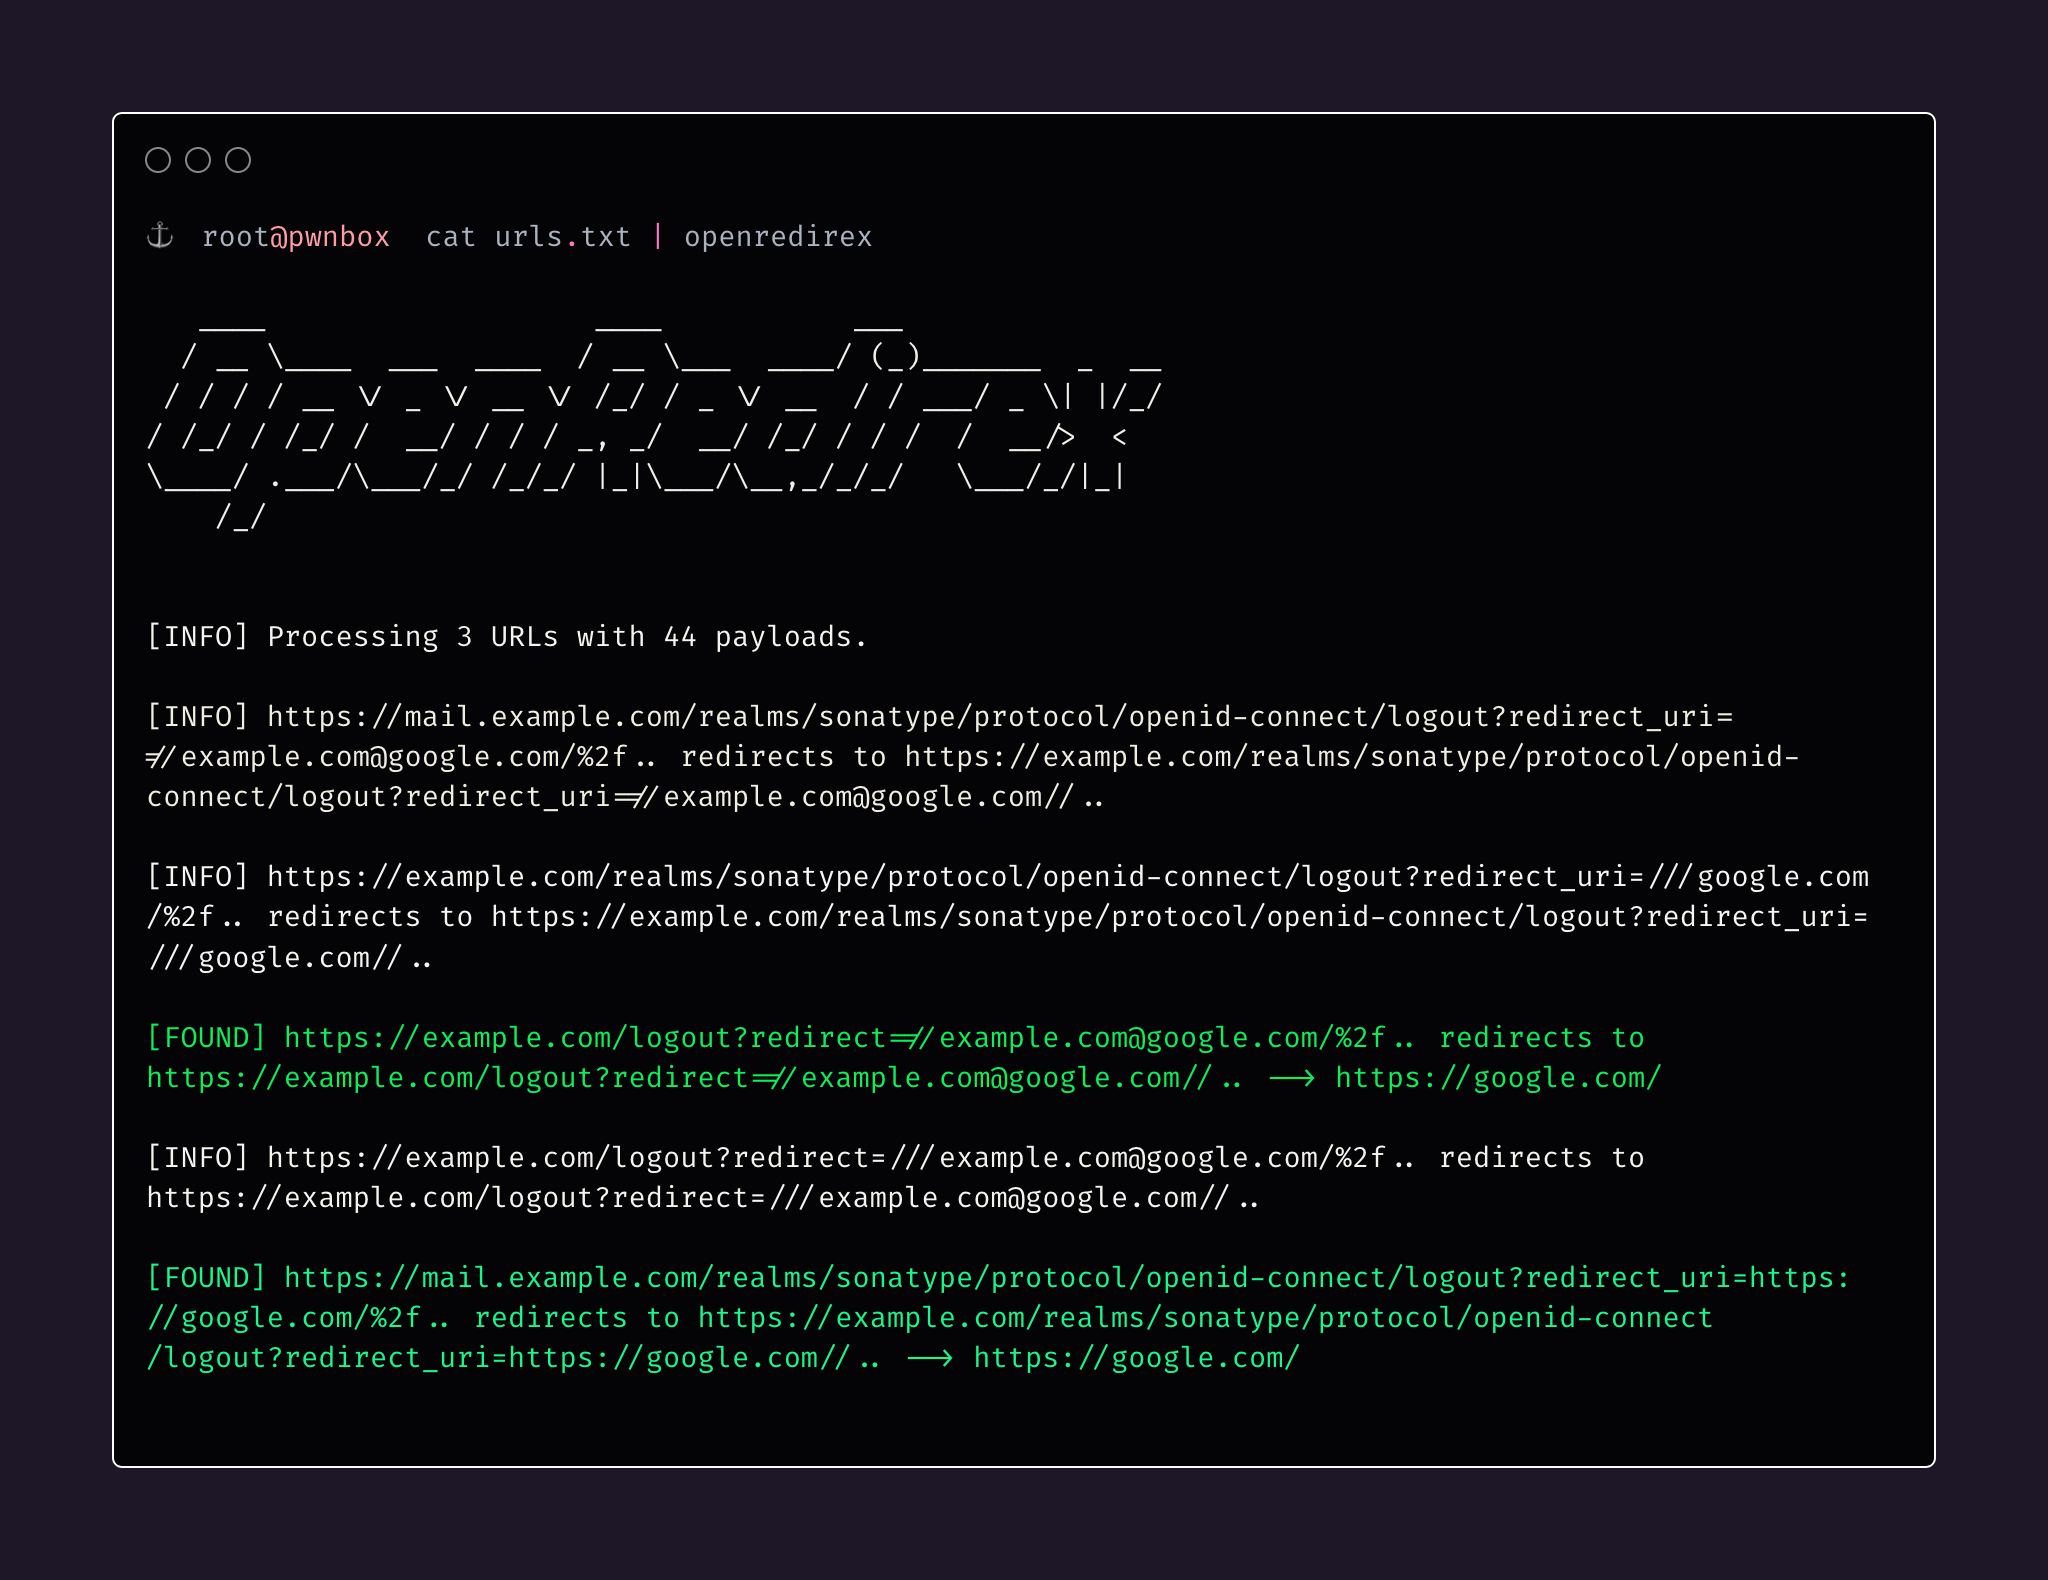 devanshbatham/openredirex
A fuzzer for detecting open redirect vulnerabilities
 jaeles-project/jaeles-signatures
Default signature for Jaeles Scanner
 v4ltonn/cve-2026-42530
Scanner PoC for CVE-2026-42530 -- nginx 1.31.0-1.31.1 HTTP/3 QPACK encoder stream Use-After-Free (CVSS 9.2)
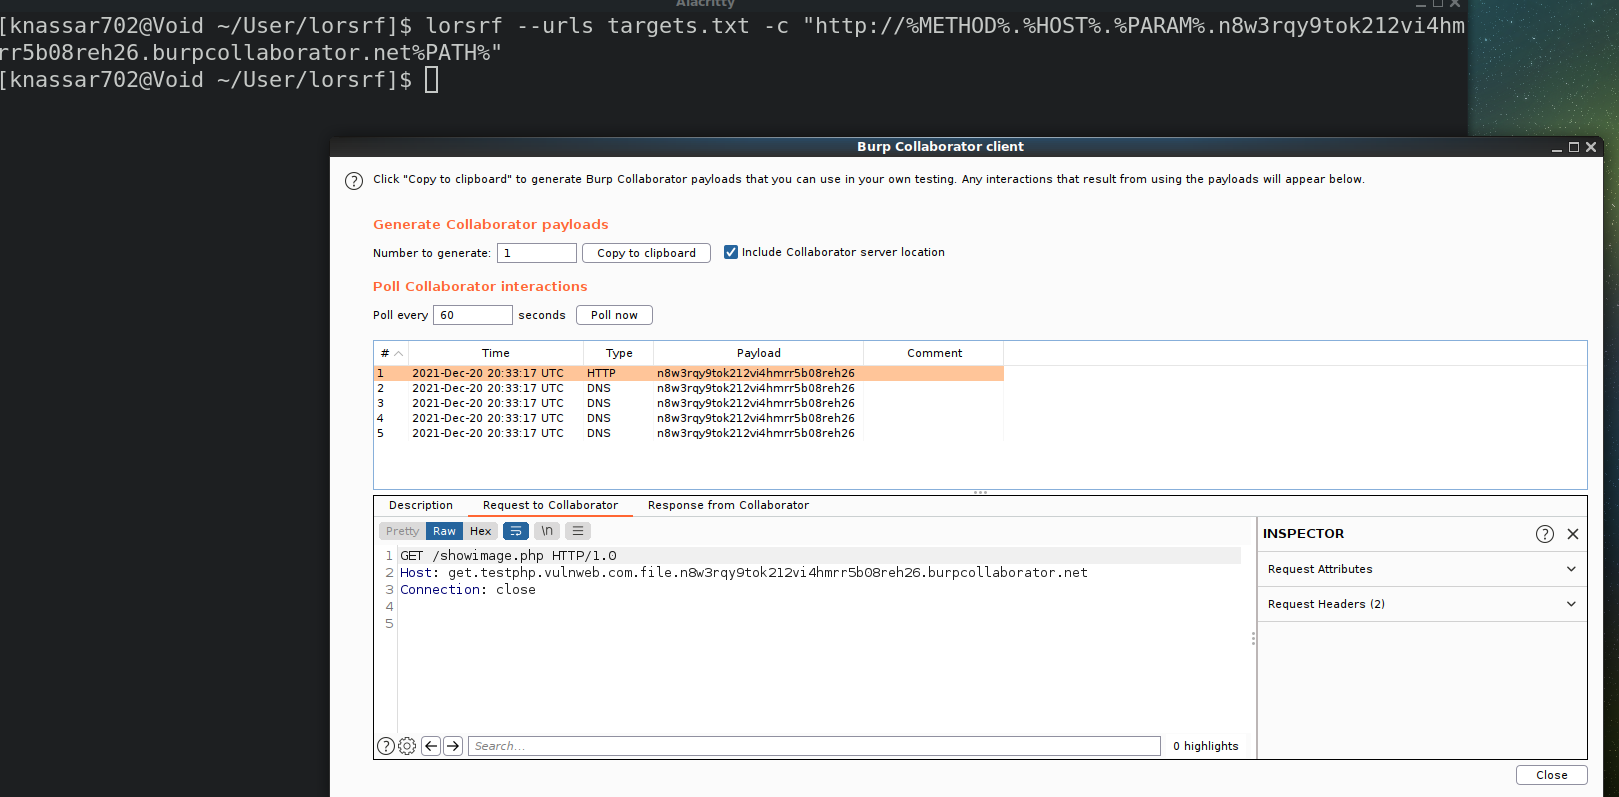 mindpatch/lorsrf
Fast CLI tool to find the parameters that can be used to find SSRF or Out-of-band resource load :artificial_satellite: :crab:
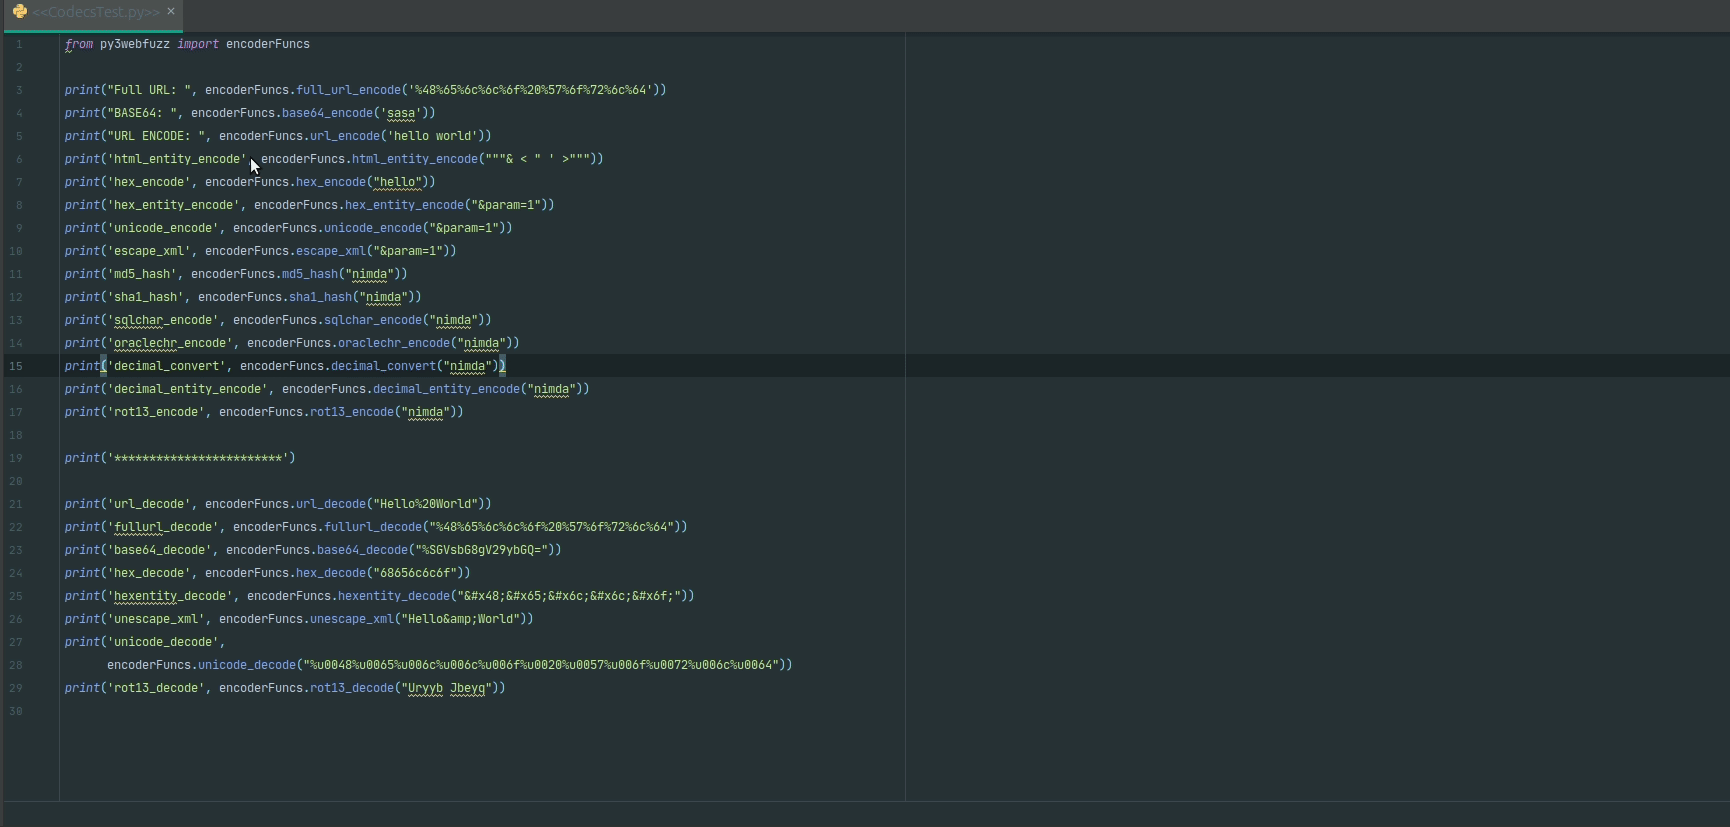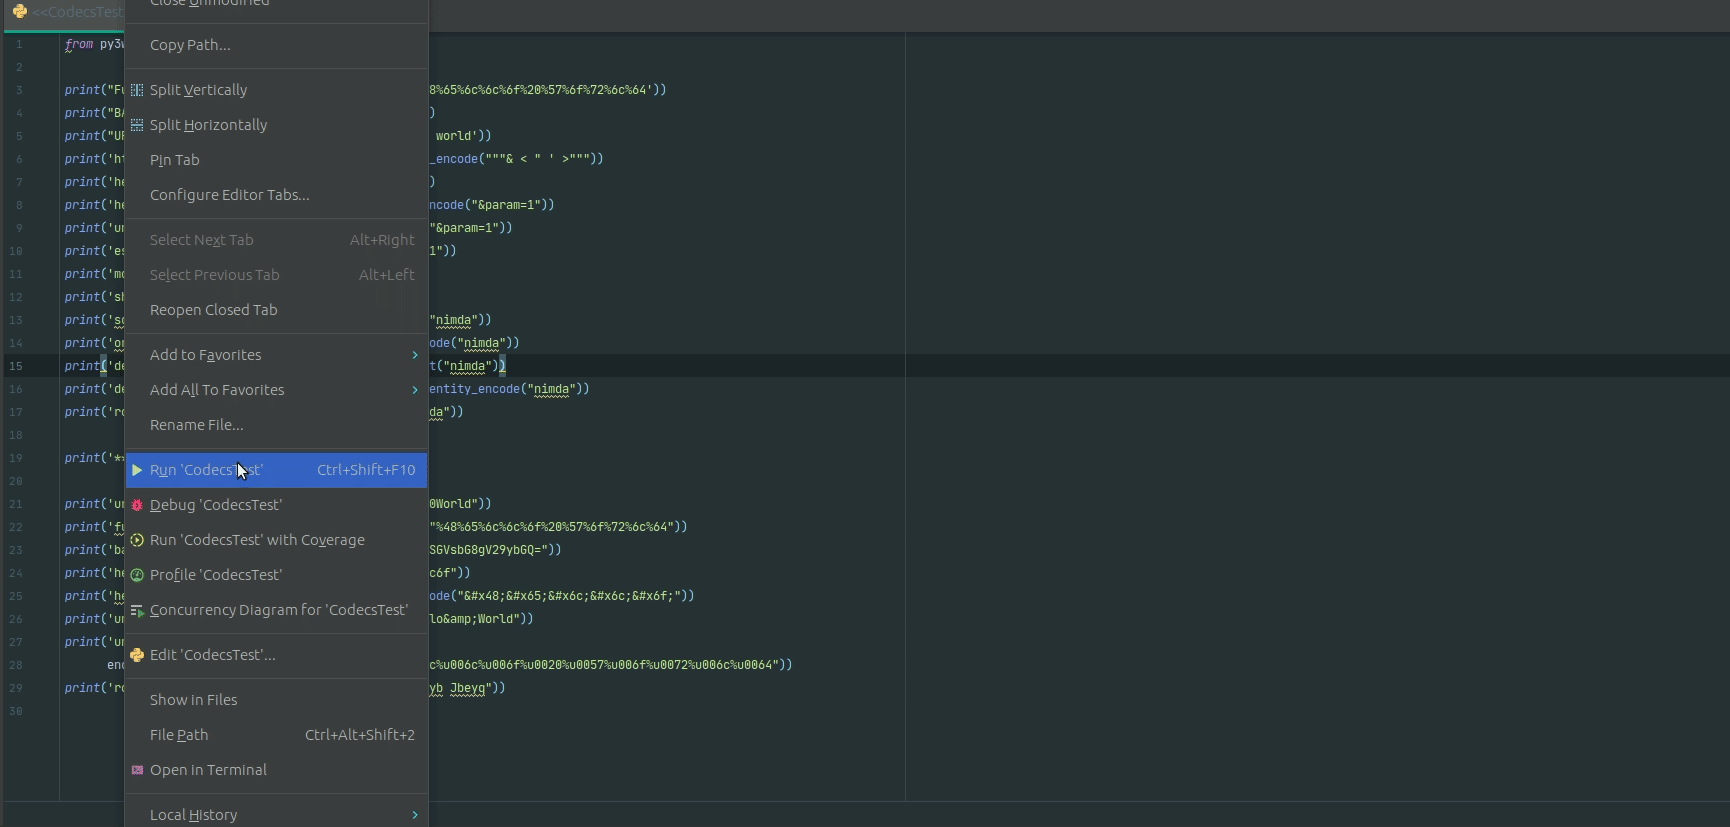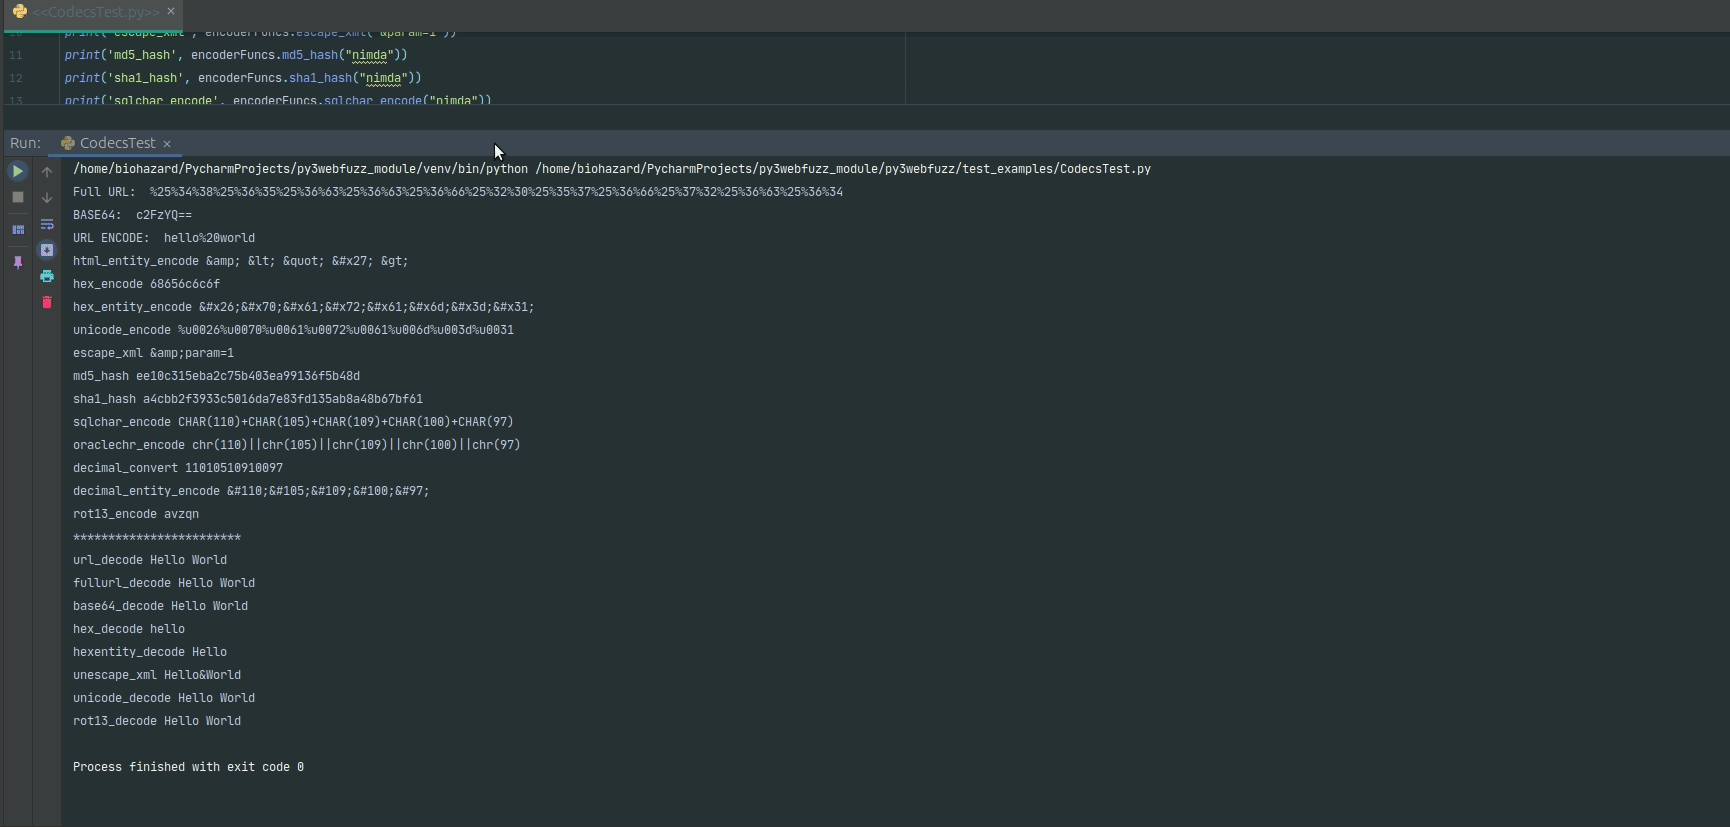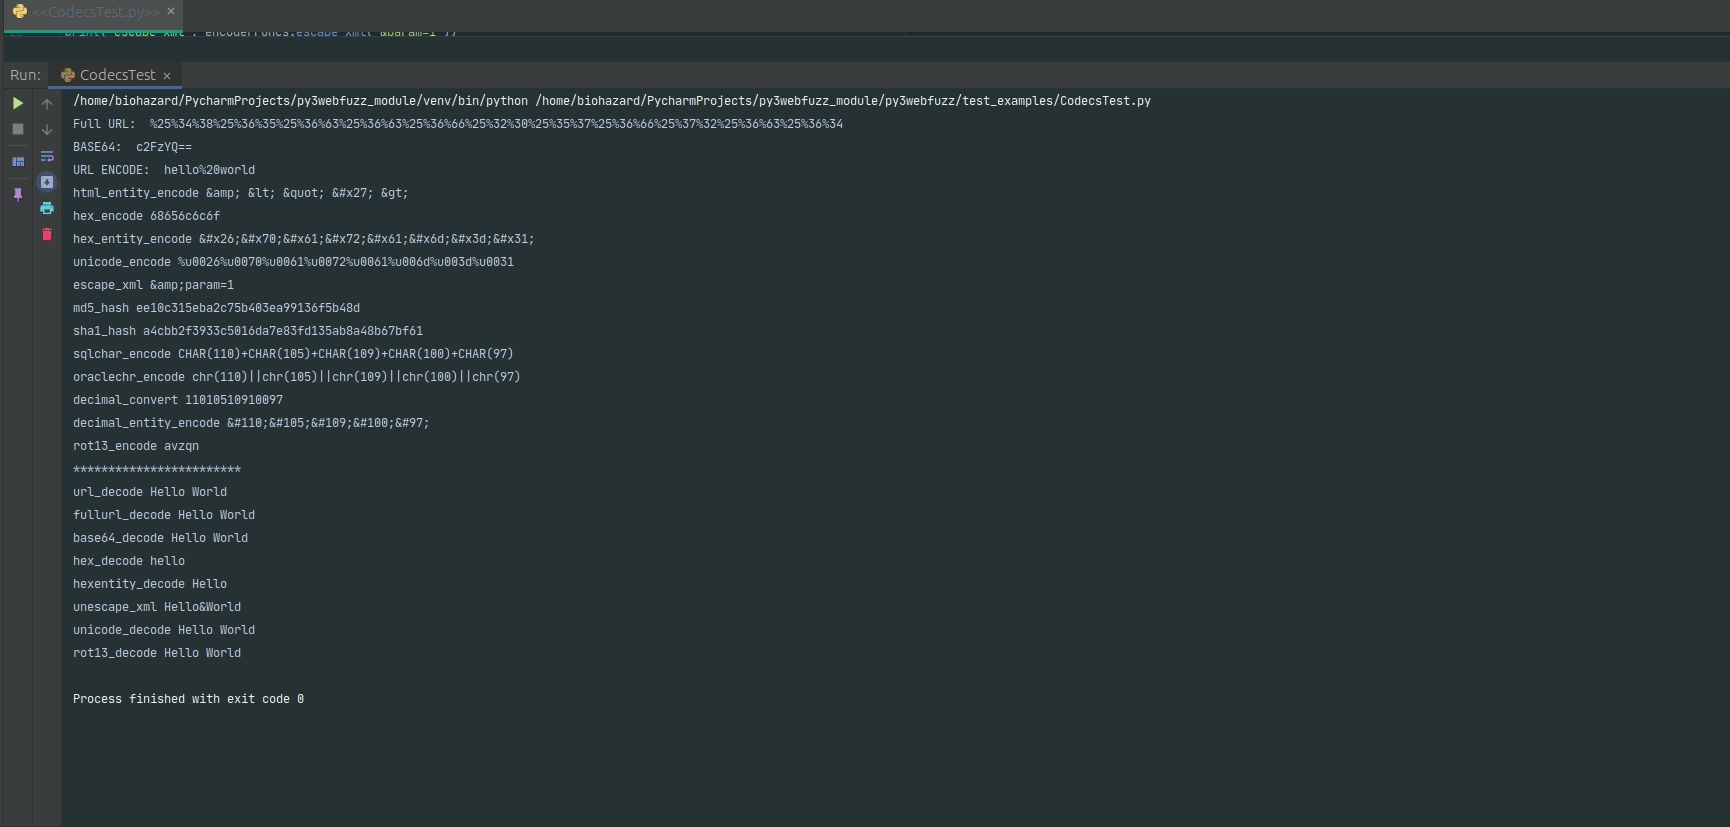 jangelesg/py3webfuzz
A Python3 module to assist in fuzzing web applications
 06-ux/cve-2026-9256-poc
CVE-2026-9256 Nginx heap buffer overflow POC
 michenriksen/jdam
A structure-aware JSON fuzzer
 jakabakos/cve-2017-9096-itext-xxe
Proof-of-concept exploit for CVE-2017-9096 demonstrating XML External Entity (XXE) injection in iText PDF library via malicious XMP metadata and form…
 ethicalhackingplayground/crlfmap
CRLFMap is a tool to find HTTP Splitting vulnerabilities
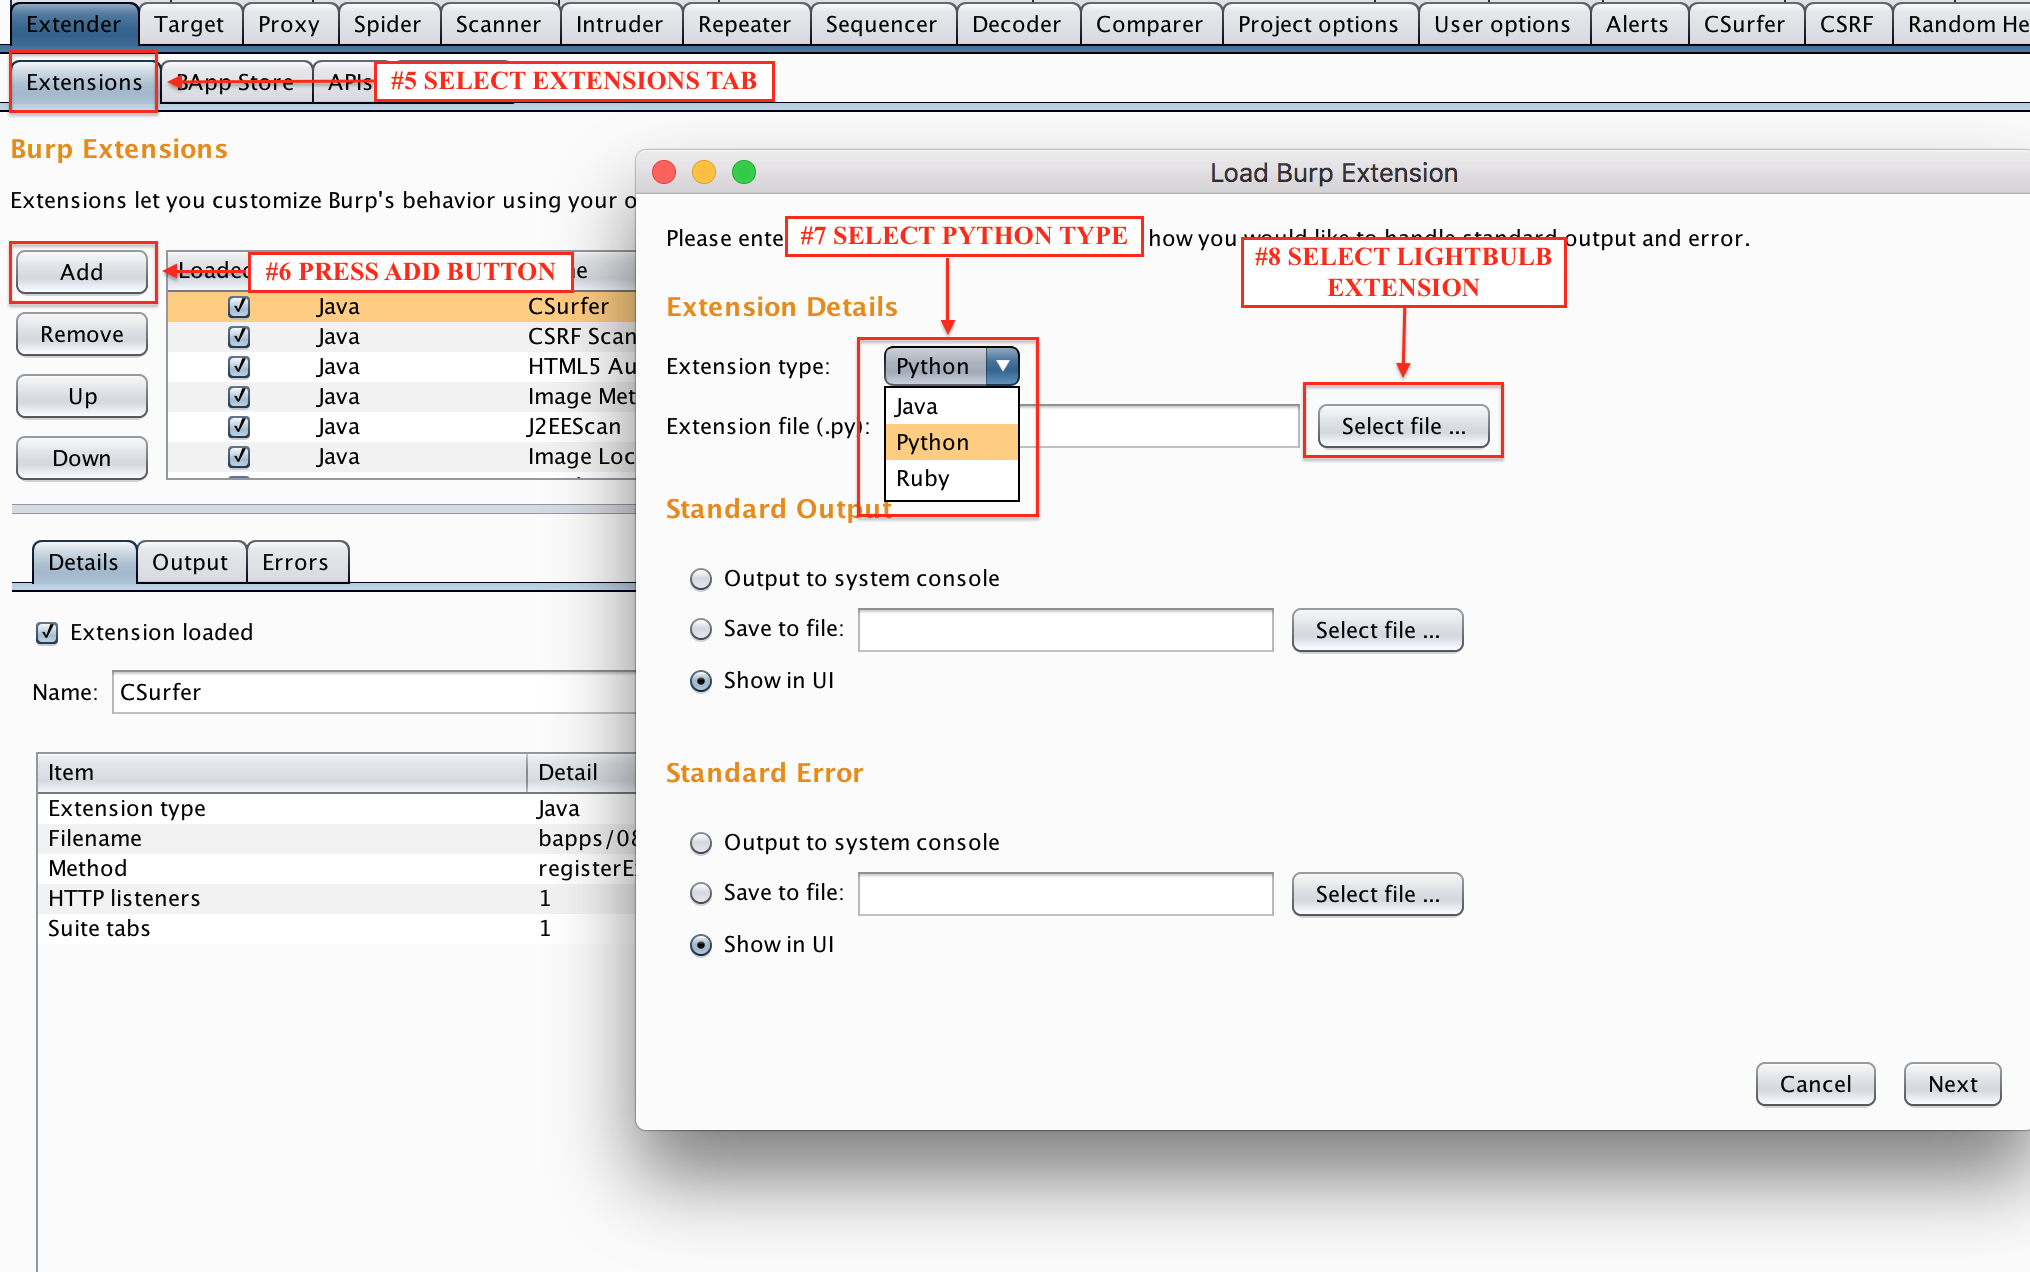 lightbulb-framework/lightbulb-framework
Tools for auditing WAFS
 brahmstaedt/libxml2-exploit
An example exploit for CVE-2017-7376