

wireshark
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
bluetooth-securitydata-exfiltrationdigital-forensics+11
9.9k
wireshark/wiresharkCapture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
 wireshark/wireshark
Wireshark's official code repository. You can keep the releases coming by donating at https://wiresharkfoundation.org/donate/.
 rjbhide/wireshark-forensics-plugin
Wireshark plugin that correlates network traffic with threat intelligence, asset tags, and vulnerability data to accelerate forensic analysis of PCAP…
 proxymanapp/tcpviewer
The best-in-class macOS app to See every packet clearly on your Mac. Alternative to Wireshark
 microsoft/etl2pcapng
Utility that converts an .etl file containing a Windows network packet capture into .pcapng format.
 kirkdjohnson/wireshark
Downloaded a packet capture (.pcapng) file from malware-traffic-analysis.net which was an example of an attempted attack against a webserver using…
 kubeshark/kubeshark
eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…
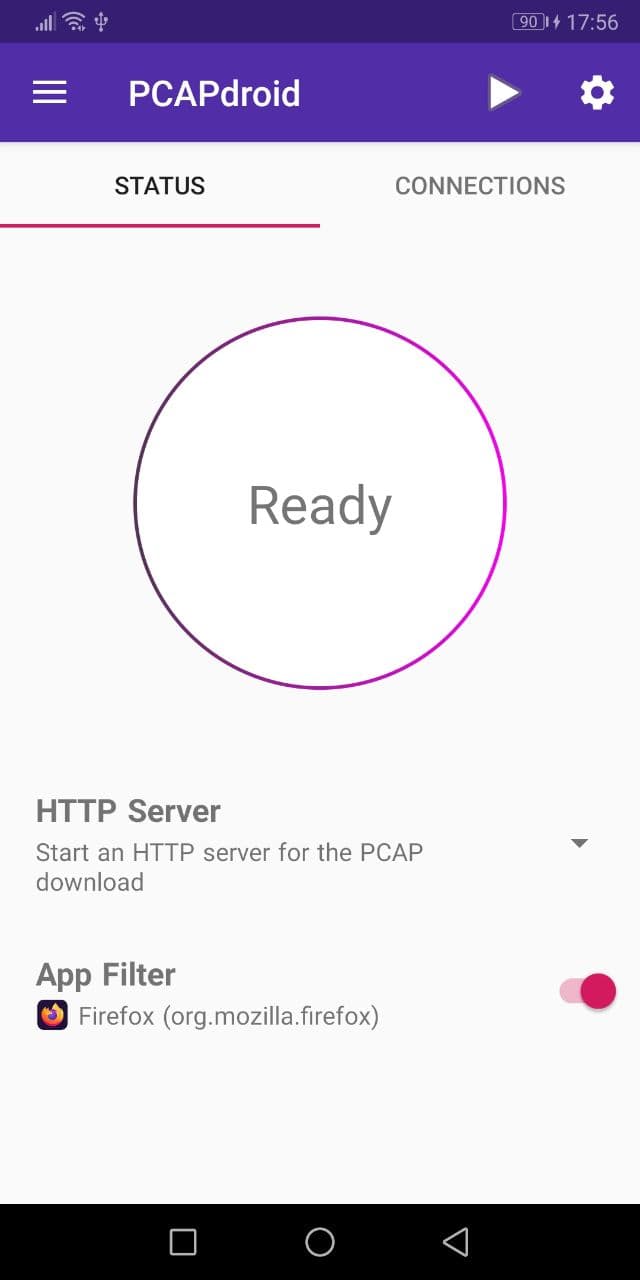 emanuele-f/pcapdroid
No-root network monitor, firewall and PCAP dumper for Android
 kiminewt/pyshark
Python wrapper for tshark, allowing python packet parsing using wireshark dissectors
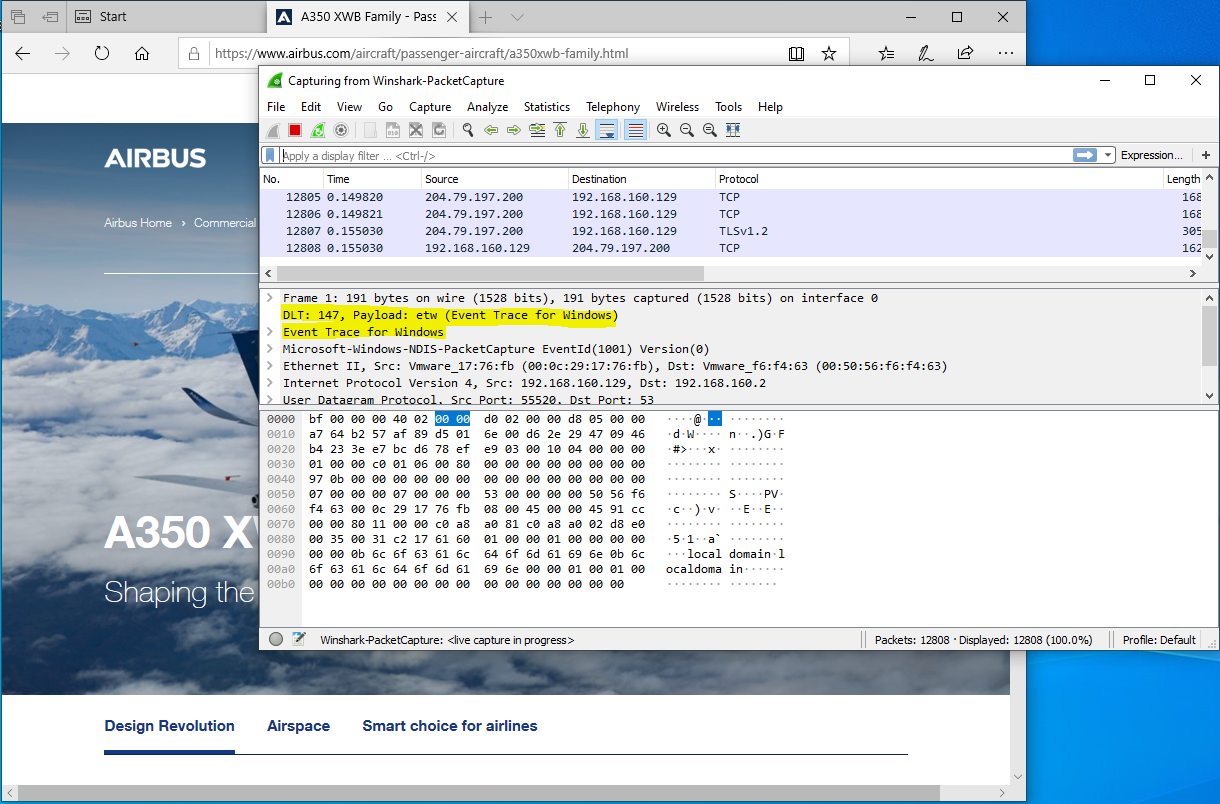 airbus-cert/winshark
A wireshark plugin to instrument ETW
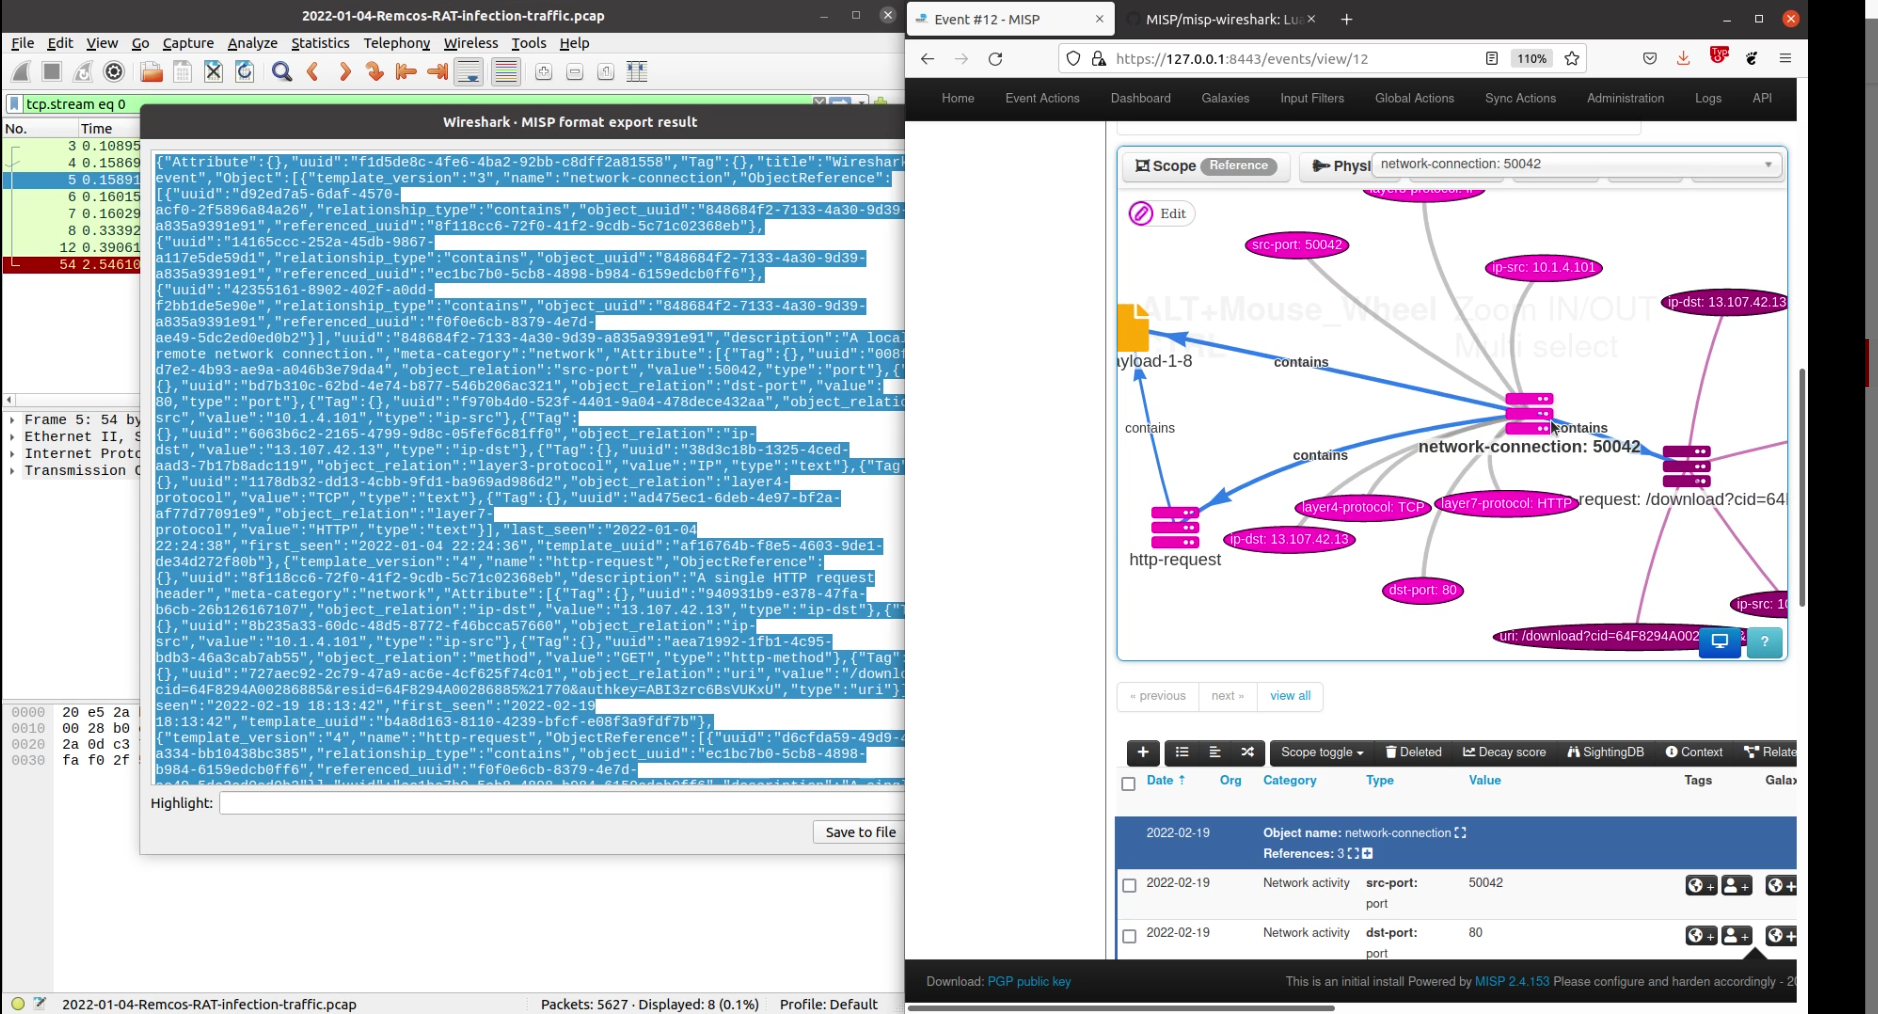 misp/misp-wireshark
Lua plugin to extract data from Wireshark and convert it into MISP format
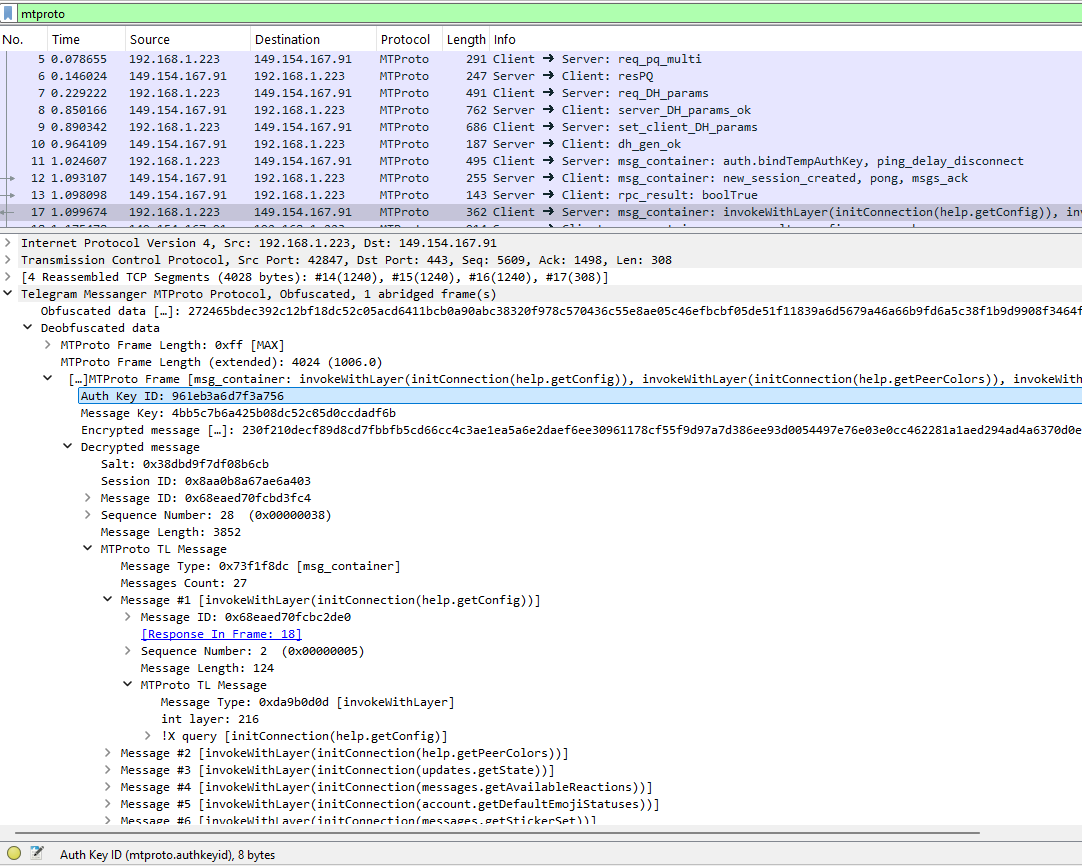 tomer8007/mtproto-dissector
Wireshark plugin for dissecting the Telegram protocol
 emrekybs/bryobio
It was developed to speed up the processes of SOC Analysts during analysis
 infobyte/wiremax
Lua-based Wireshark postdissector that decrypts and parses Ubiquiti AirMAX/RouterBoard 802.11 vendor IEs into filterable fields.
 w00t3k/awesome-cellular-hacking
Awesome-Cellular-Hacking
 weirdmachine64/sharkmcp
A swiss-knife MCP server for analysing PCAP files
 emrekybs/bluefish
Automation tool designed to simplify the analysis of PCAP (Packet Capture) files