
passivedns
 gamelinux/passivedns
A network sniffer that logs all DNS server replies for use in a passive DNS setup
dns-analysisforensicsincident-response+3
1.7k15 days ago
gamelinux/passivednsA network sniffer that logs all DNS server replies for use in a passive DNS setup
 jpr5/ngrep
ngrep is like GNU grep applied to the network layer. It's a PCAP-based tool that allows you to specify an extended regular or hexadecimal expression…
 mlgualtieri/ntlmrawunhide
NTLMRawUnhide.py is a Python3 script designed to parse network packet capture files and extract NTLMv2 hashes in a crackable format. The following…
 thomasareed/pict
Modular incident response toolkit for collecting forensic data from potentially infected macOS endpoints, capturing browser artifacts, persistence…
 emrekybs/bryobio
It was developed to speed up the processes of SOC Analysts during analysis
 arkime/arkime
Arkime is an open source, large scale, full packet capturing, indexing, and database system.
 proxymanapp/tcpviewer
The best-in-class macOS app to See every packet clearly on your Mac. Alternative to Wireshark
 s0md3v/orbit
Blockchain Transactions Investigation Tool
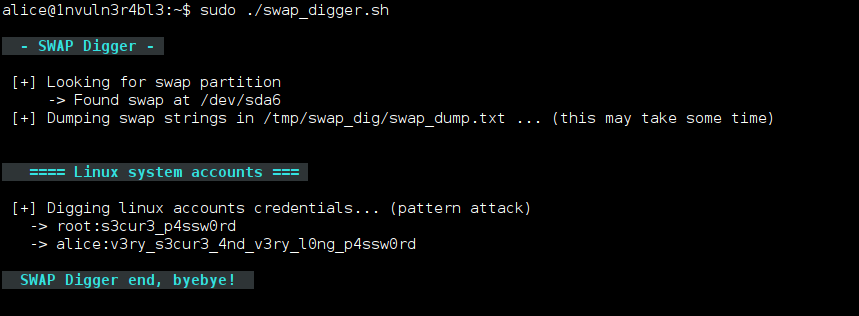 sevagas/swap_digger
Automates Linux swap analysis to extract user credentials, web form data, WiFi keys, and HTTP authentication during post-exploitation or forensic…
 invoke-ir/ace
Automated, Collection, and Enrichment Platform
 logisek/baconsampler
Sniffs outbound traffic for suspicious, beacon-like callbacks, because if it keeps coming back on schedule, it's probably not breakfast.
 sjzar/chatlog
chat log tool, easily use your own chat data. 聊天记录工具,轻松使用自己的聊天数据
 ssrajadh/sentrysearch
Semantic search over videos using Gemini Embedding 2 or Qwen3-VL.
 idescriptor/idescriptor
privacy-first, open-source and free idevice management tool written in Rust and Qt
 elevenpaths/foca
Tool to find metadata and hidden information in the documents.
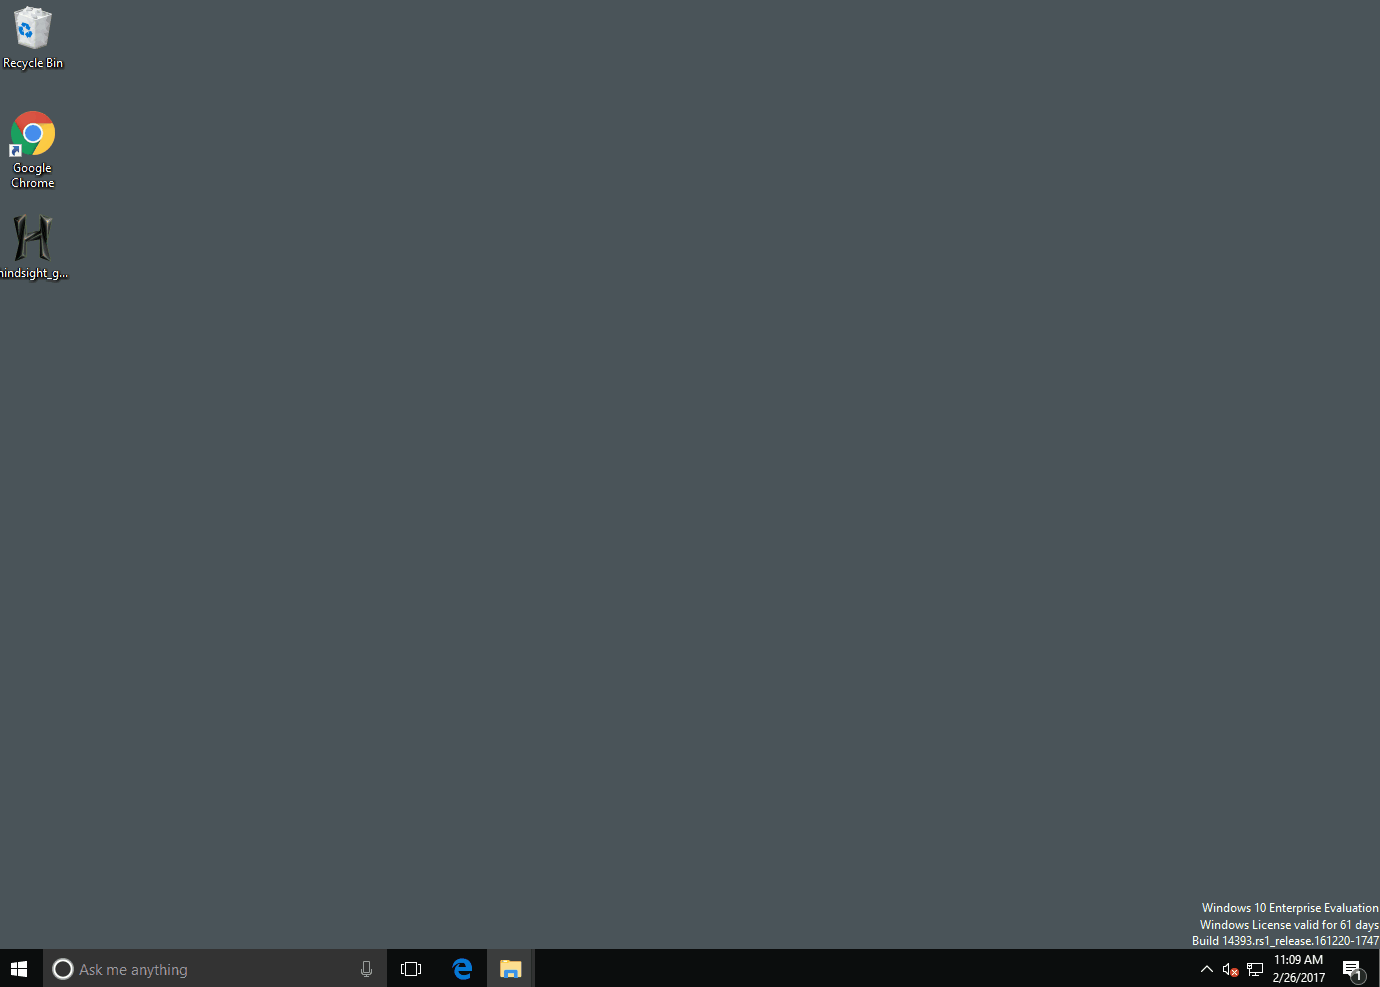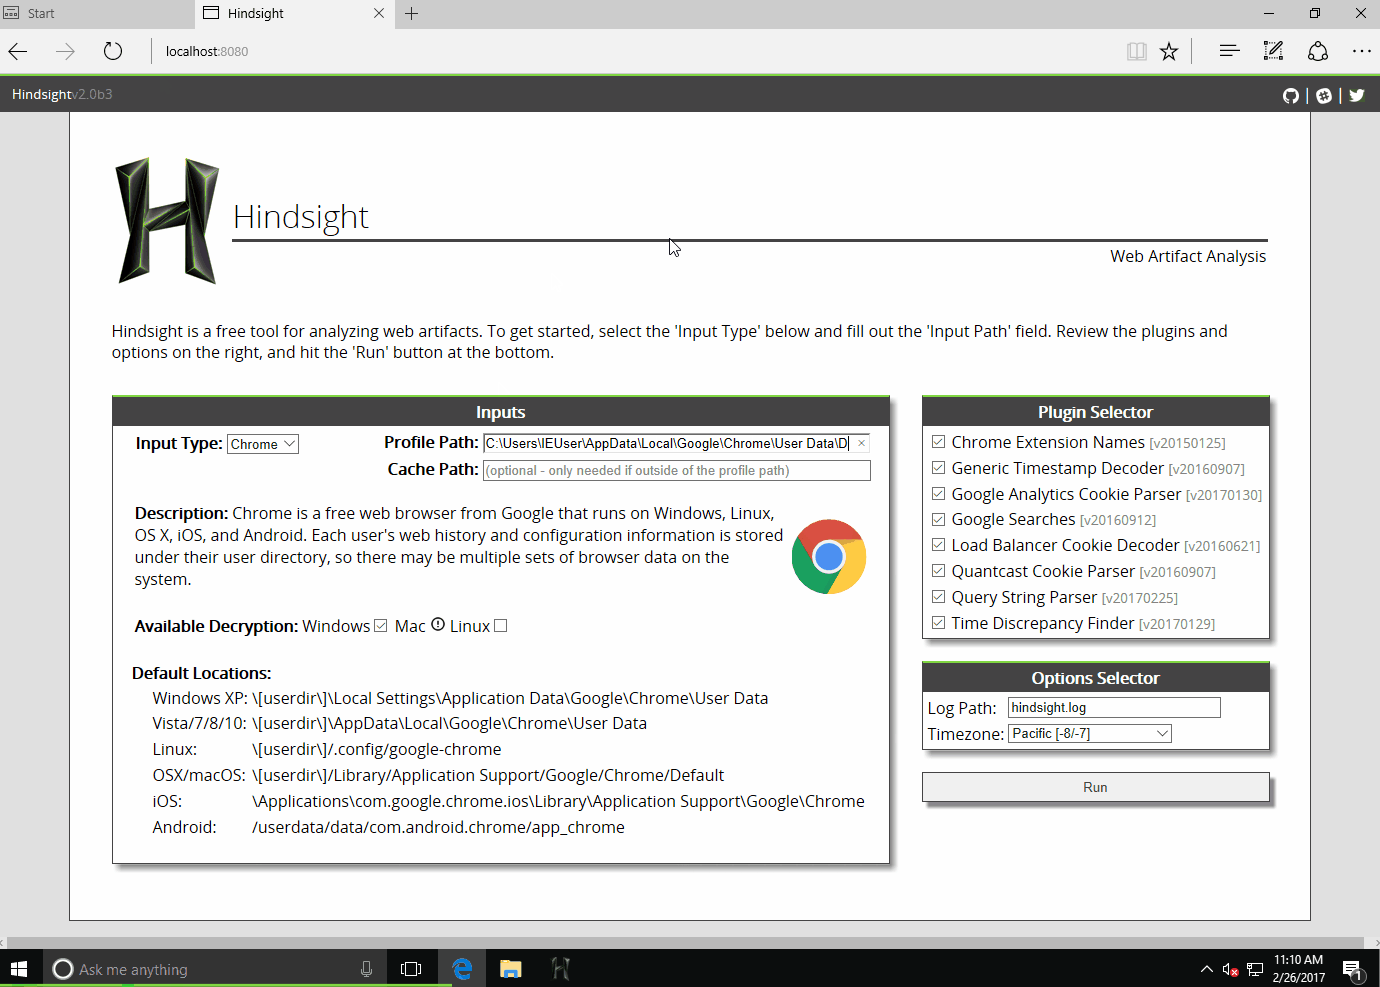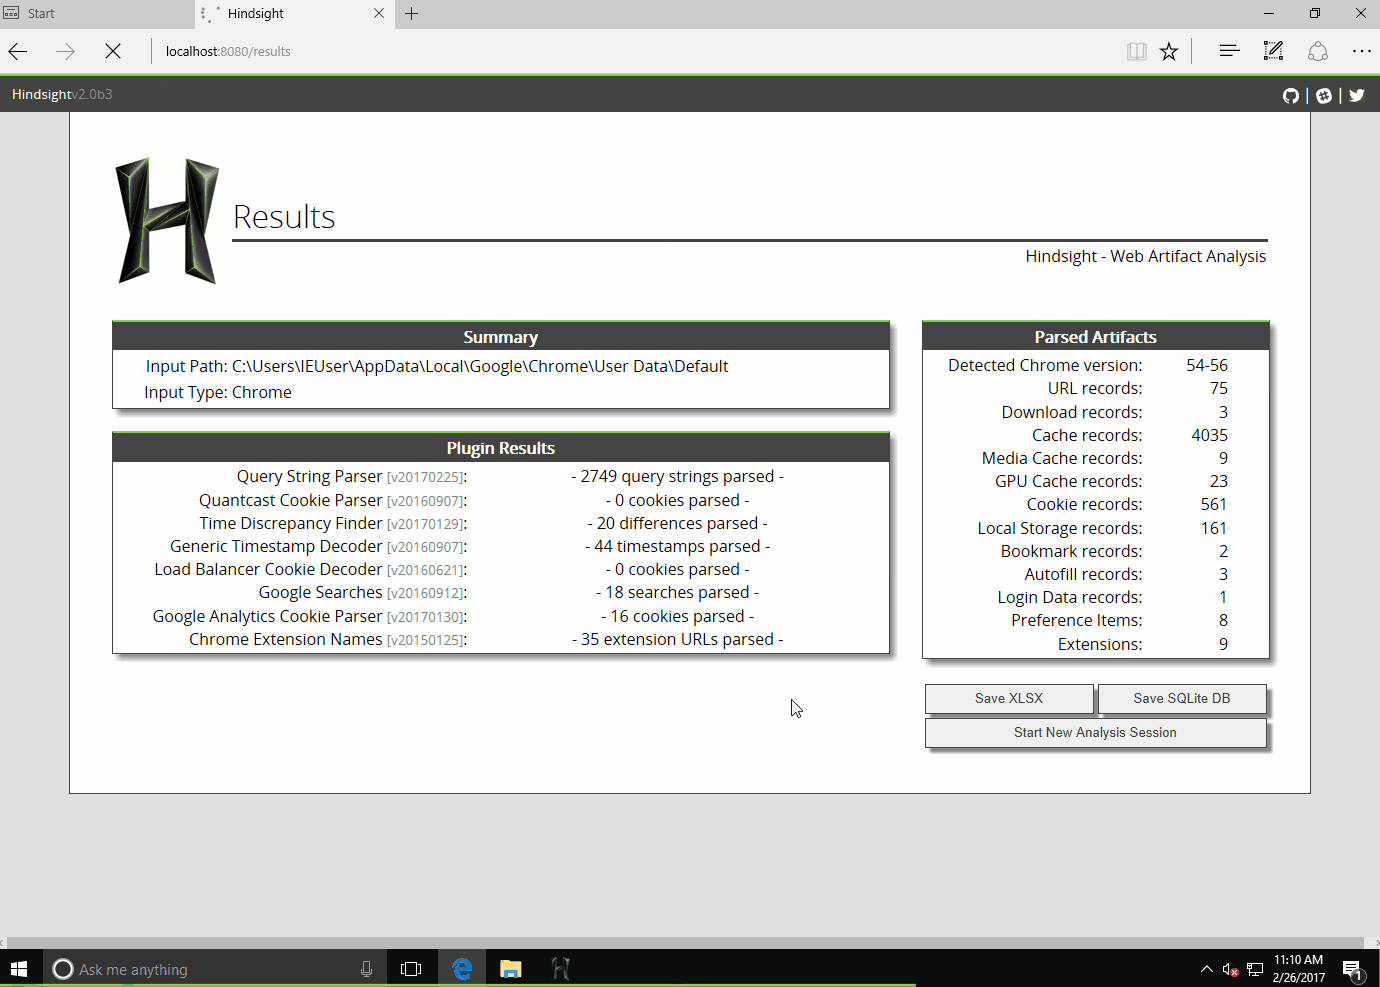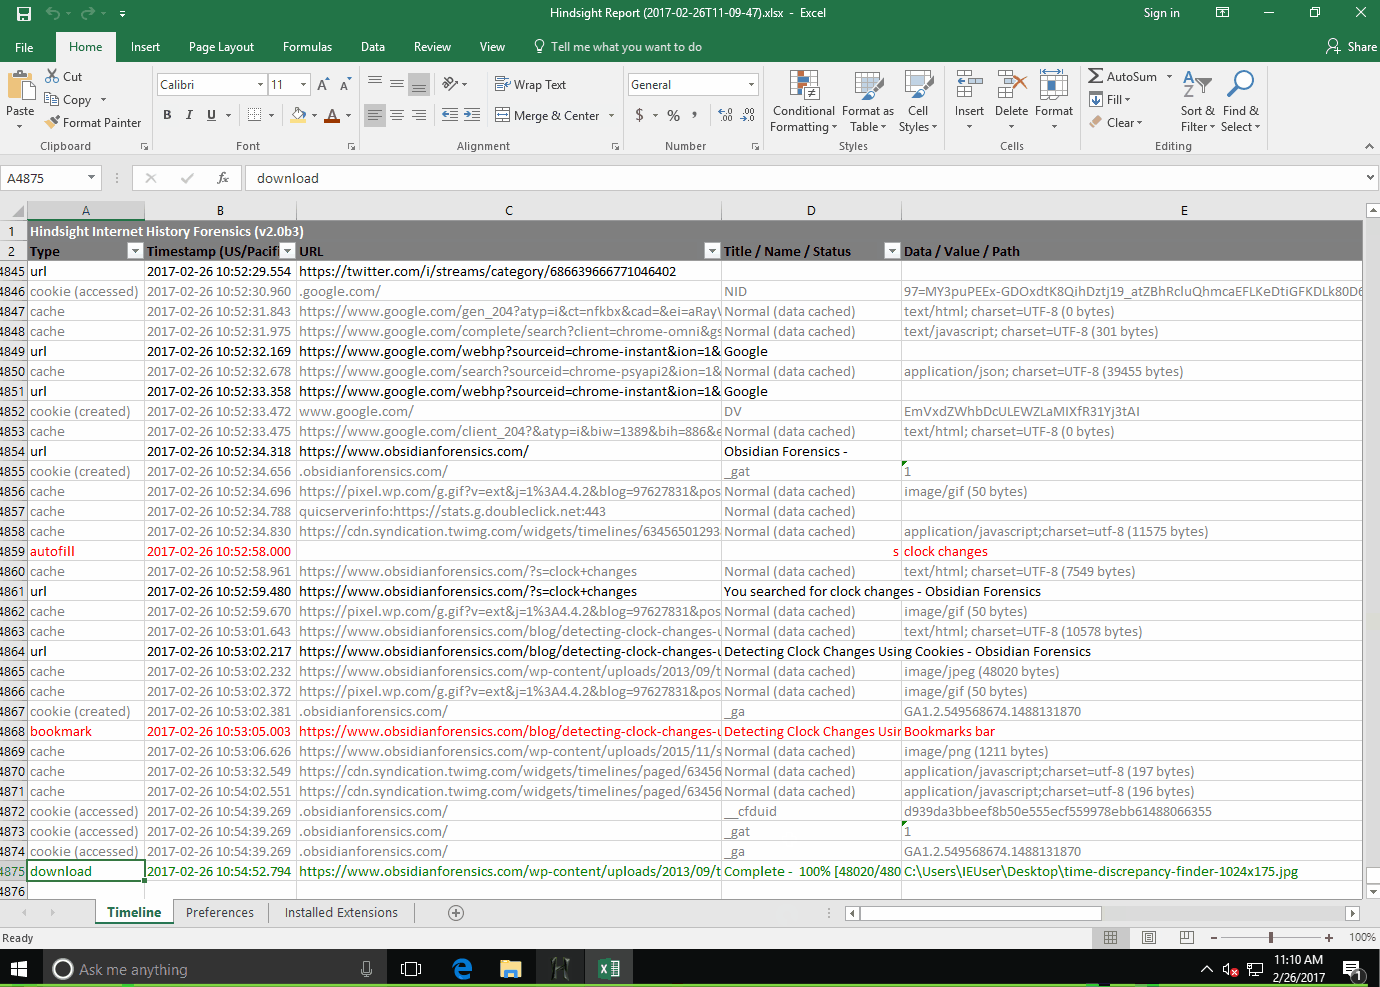 ryandfir/hindsight
Browser forensics tool for Google Chrome, other Chromium-based browsers, and Mozilla Firefox
 amnestytech/investigations
Indicators of Compromise from Amnesty International's cyber investigations
 lgandx/pcredz
This tool extracts Credit card numbers, NTLM(DCE-RPC, HTTP, SQL, LDAP, etc), Kerberos (AS-REQ Pre-Auth etype 23), HTTP Basic, SNMP, POP, SMTP, FTP,…