
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
62 results
packetsifterTool preview

packetsifterTool

GitHubpacketsifter/packetsiftertool

PacketSifter is a tool/script that is designed to aid analysts in sifting through a packet capture (pcap) to find noteworthy traffic. Packetsifter…
defensive-toolsdigital-forensicsforensics+5
93
5 years ago
RootQuest-CTF-Box-Multi-Stage-Exploitation-VM preview

RootQuest-CTF-Box-Multi-Stage-Exploitation-VM

GitHubthieveshkar/rootquest-ctf-box-multi-stage-exploitation-vm

Custom vulnerable VM (Ubuntu 14.04) designed for teaching multi-stage penetration testing. Features 10 interconnected challenges across Forensics,…
binary-exploitationcryptographyctf+7
11 months ago
dumpscan preview
Archived

dumpscan

GitHubdaddycocoaman/dumpscan

Finding secrets in kernel and user memory
cryptographydigital-forensicsencryption-decryption-tools+4
1183 years ago
Meerkat preview

Meerkat

GitHubtonyphipps/meerkat

A collection of PowerShell modules designed for artifact gathering and reconnaisance of Windows-based endpoints.
digital-forensicsforensicsincident-response+2
4821 year ago
MasterParser preview

MasterParser

GitHubsecurityjoes/masterparser

MasterParser is a powerful DFIR tool designed for analyzing and parsing Linux logs
digital-forensicseducationforensics+3
7618 months ago
analyzeMFT preview

analyzeMFT

GitHubrowingdude/analyzemft

analyzeMFT.py is designed to fully parse the MFT file from an NTFS filesystem and present the results as accurately as possible in multiple formats.
data-recoverydigital-forensicsdisk-forensics+1
5331 year ago
NTLMRawUnHide preview

NTLMRawUnHide

GitHubmlgualtieri/ntlmrawunhide

NTLMRawUnhide.py is a Python3 script designed to parse network packet capture files and extract NTLMv2 hashes in a crackable format. The following…
forensicsinformation-gatheringnetwork-security+2
3932 years ago
artifacts-kit preview

artifacts-kit

GitHubforrest-orr/artifacts-kit

Pseudo-malicious usermode memory artifact generator kit designed to easily mimic the footprints left by real malware on an infected Windows OS.
exploitationforensicsmalware-analysis+5
2282 years ago
IG-Detective preview

IG-Detective

GitHubshredzwho/ig-detective

OSINT tool researched and designed to hunt down IG handles

educationfingerprint-spoofingforensics+7
1581 month ago
pegasus-neo preview

pegasus-neo

GitHubsobri3195/pegasus-neo

PEGASUS-NEO is a comprehensive penetration testing framework designed for security professionals and ethical hackers. It combines multiple security…
exploitationforensicsosint+9
1287 months ago
LiMEaide preview

LiMEaide

GitHubkd8bny/limeaide

A python application designed to remotely dump RAM of a Linux client and create a volatility profile for later analysis on your local host.

digital-forensicsforensicsmemory-forensics
1577 years ago
ForensicMiner preview

ForensicMiner

GitHubsecurityjoes/forensicminer

A really good DFIR automation for collecting and analyzing evidence designed for cybersecurity professionals.
digital-forensicsdisk-forensicsforensics+2
1651 year ago
DraculaOS preview

DraculaOS

GitHubemrekybs/draculaos

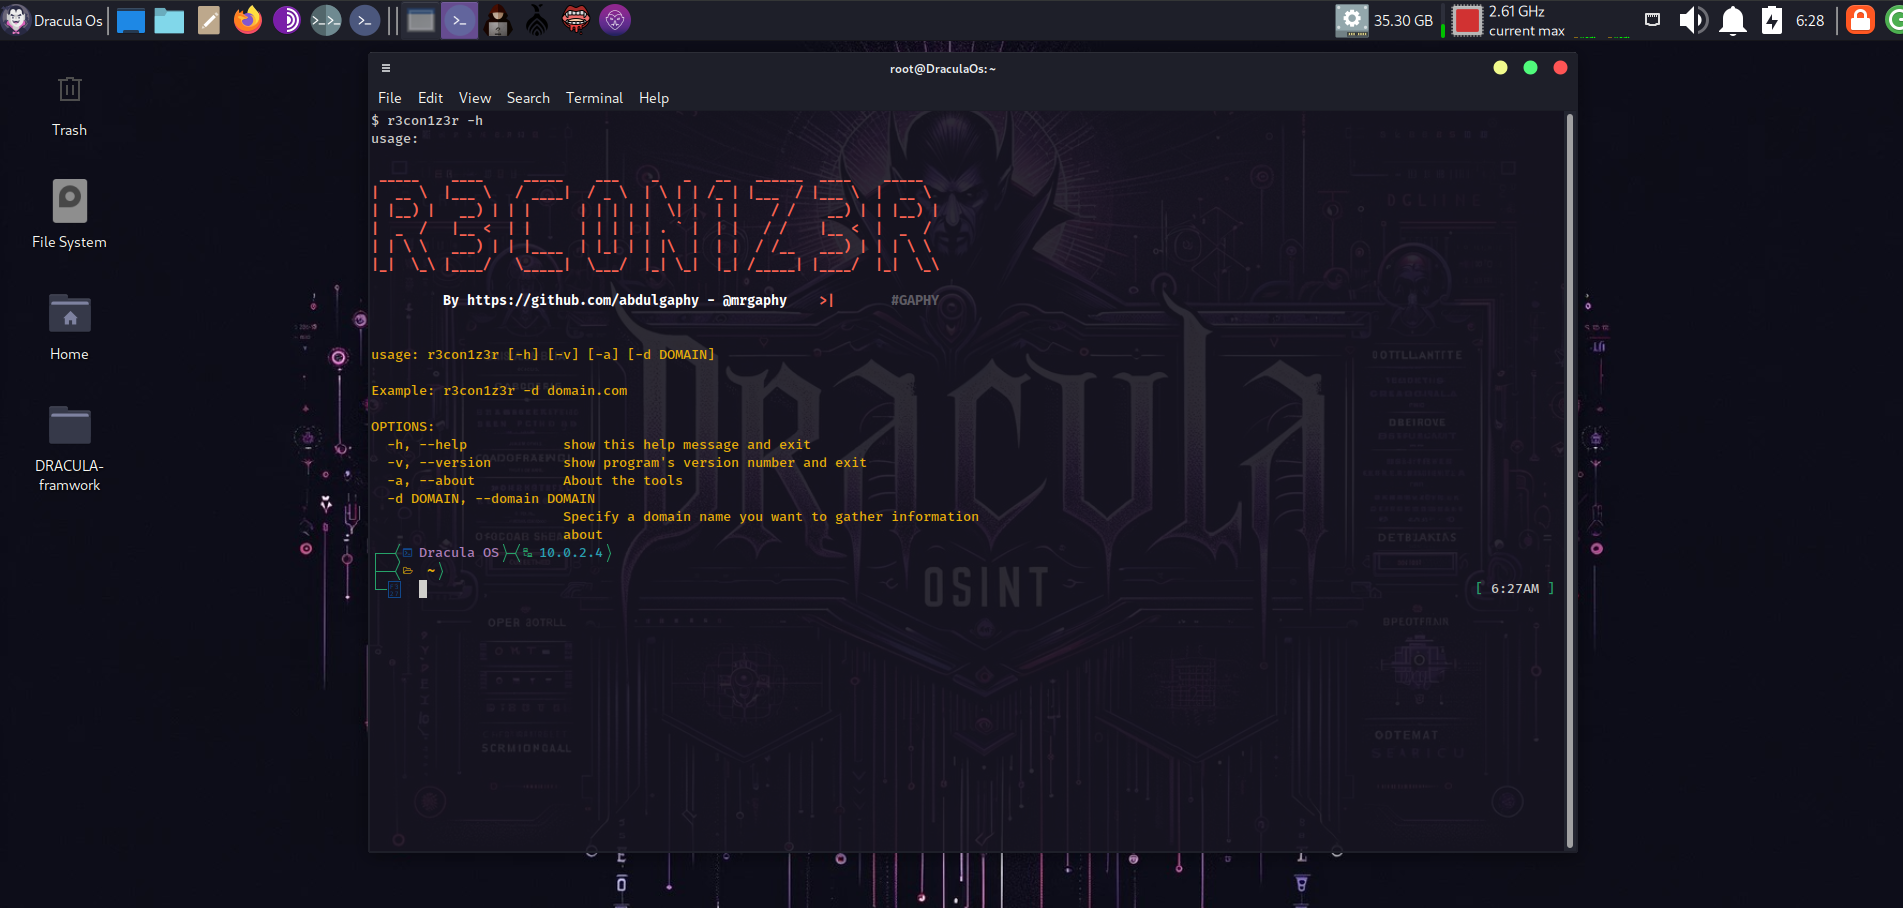
Dracula OS is a Linux operating system meticulously designed for OSINT (Open Source Intelligence) and Cyber ​​Intelligence missions.

curated-resourceseducationemail-harvesting+9
9710 months ago
BlueFish preview

BlueFish

GitHubemrekybs/bluefish

Automation tool designed to simplify the analysis of PCAP (Packet Capture) files
forensicsincident-responseinformation-gathering+2
206 months ago
challenges preview

challenges

GitHubstar-sg/challenges

Christmas-themed CTF Advent Calendar with 12 structured challenges across binary exploitation, cryptography, reverse engineering, forensics, OSINT,…
binary-exploitationcryptographyctf+6
248 months ago
Ivanti-Connect-Secure-Logs-Parser preview

Ivanti-Connect-Secure-Logs-Parser

GitHubhexastrike/ivanti-connect-secure-logs-parser

A Python script for examining Ivanti Secure Connect (ICS) event logs, designed to support investigations into vulnerabilities CVE-2025-0282,…

digital-forensicsforensicsincident-response+3
51 year ago
MagicArch preview

MagicArch

GitLabmagicbytes/magicarch

MagicArch is a comprehensive post-installation script built with Ansible, designed to transform a basic Arch Linux installation into a fully equipped…
exploit-frameworksforensicsinformation-gathering+8
22 years ago
CyberSources preview

CyberSources

GitHubbst04/cybersources

A curated list of cybersecurity tools and resources.

cryptographyctfcurated-resources+8
2.4k14 days ago
Previous1234Next