
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
495 results
halogen preview
Archived

halogen

GitHubtarget/halogen

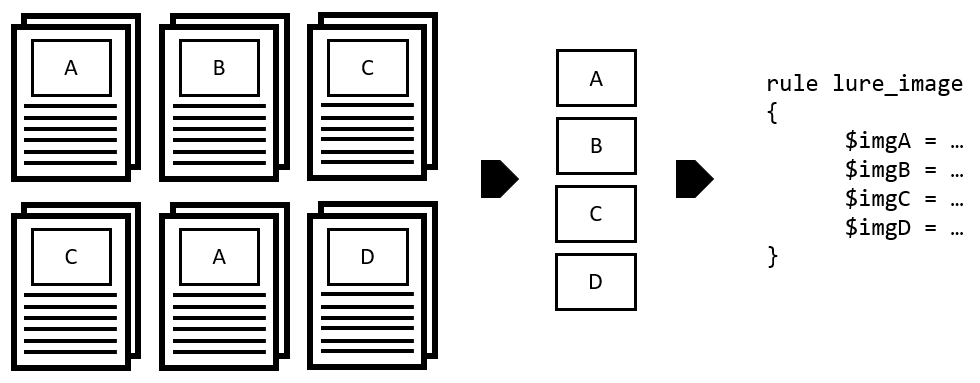
Automatically create YARA rules from malicious documents.

forensicsincident-responsemalware-analysis+2
210
4 years ago
CitrixNetscalerAnalysis preview

CitrixNetscalerAnalysis

GitHubl4r1k/citrixnetscaleranalysis

🔬 Jupyter notebook to help automate some of the forensic analysis related to Citrix Netscalers compromised via CVE-2019-19781
curated-resourcesdigital-forensicseducation+5
6 years ago
rip_raw preview
Archived

rip_raw

GitHubcado-security/rip_raw

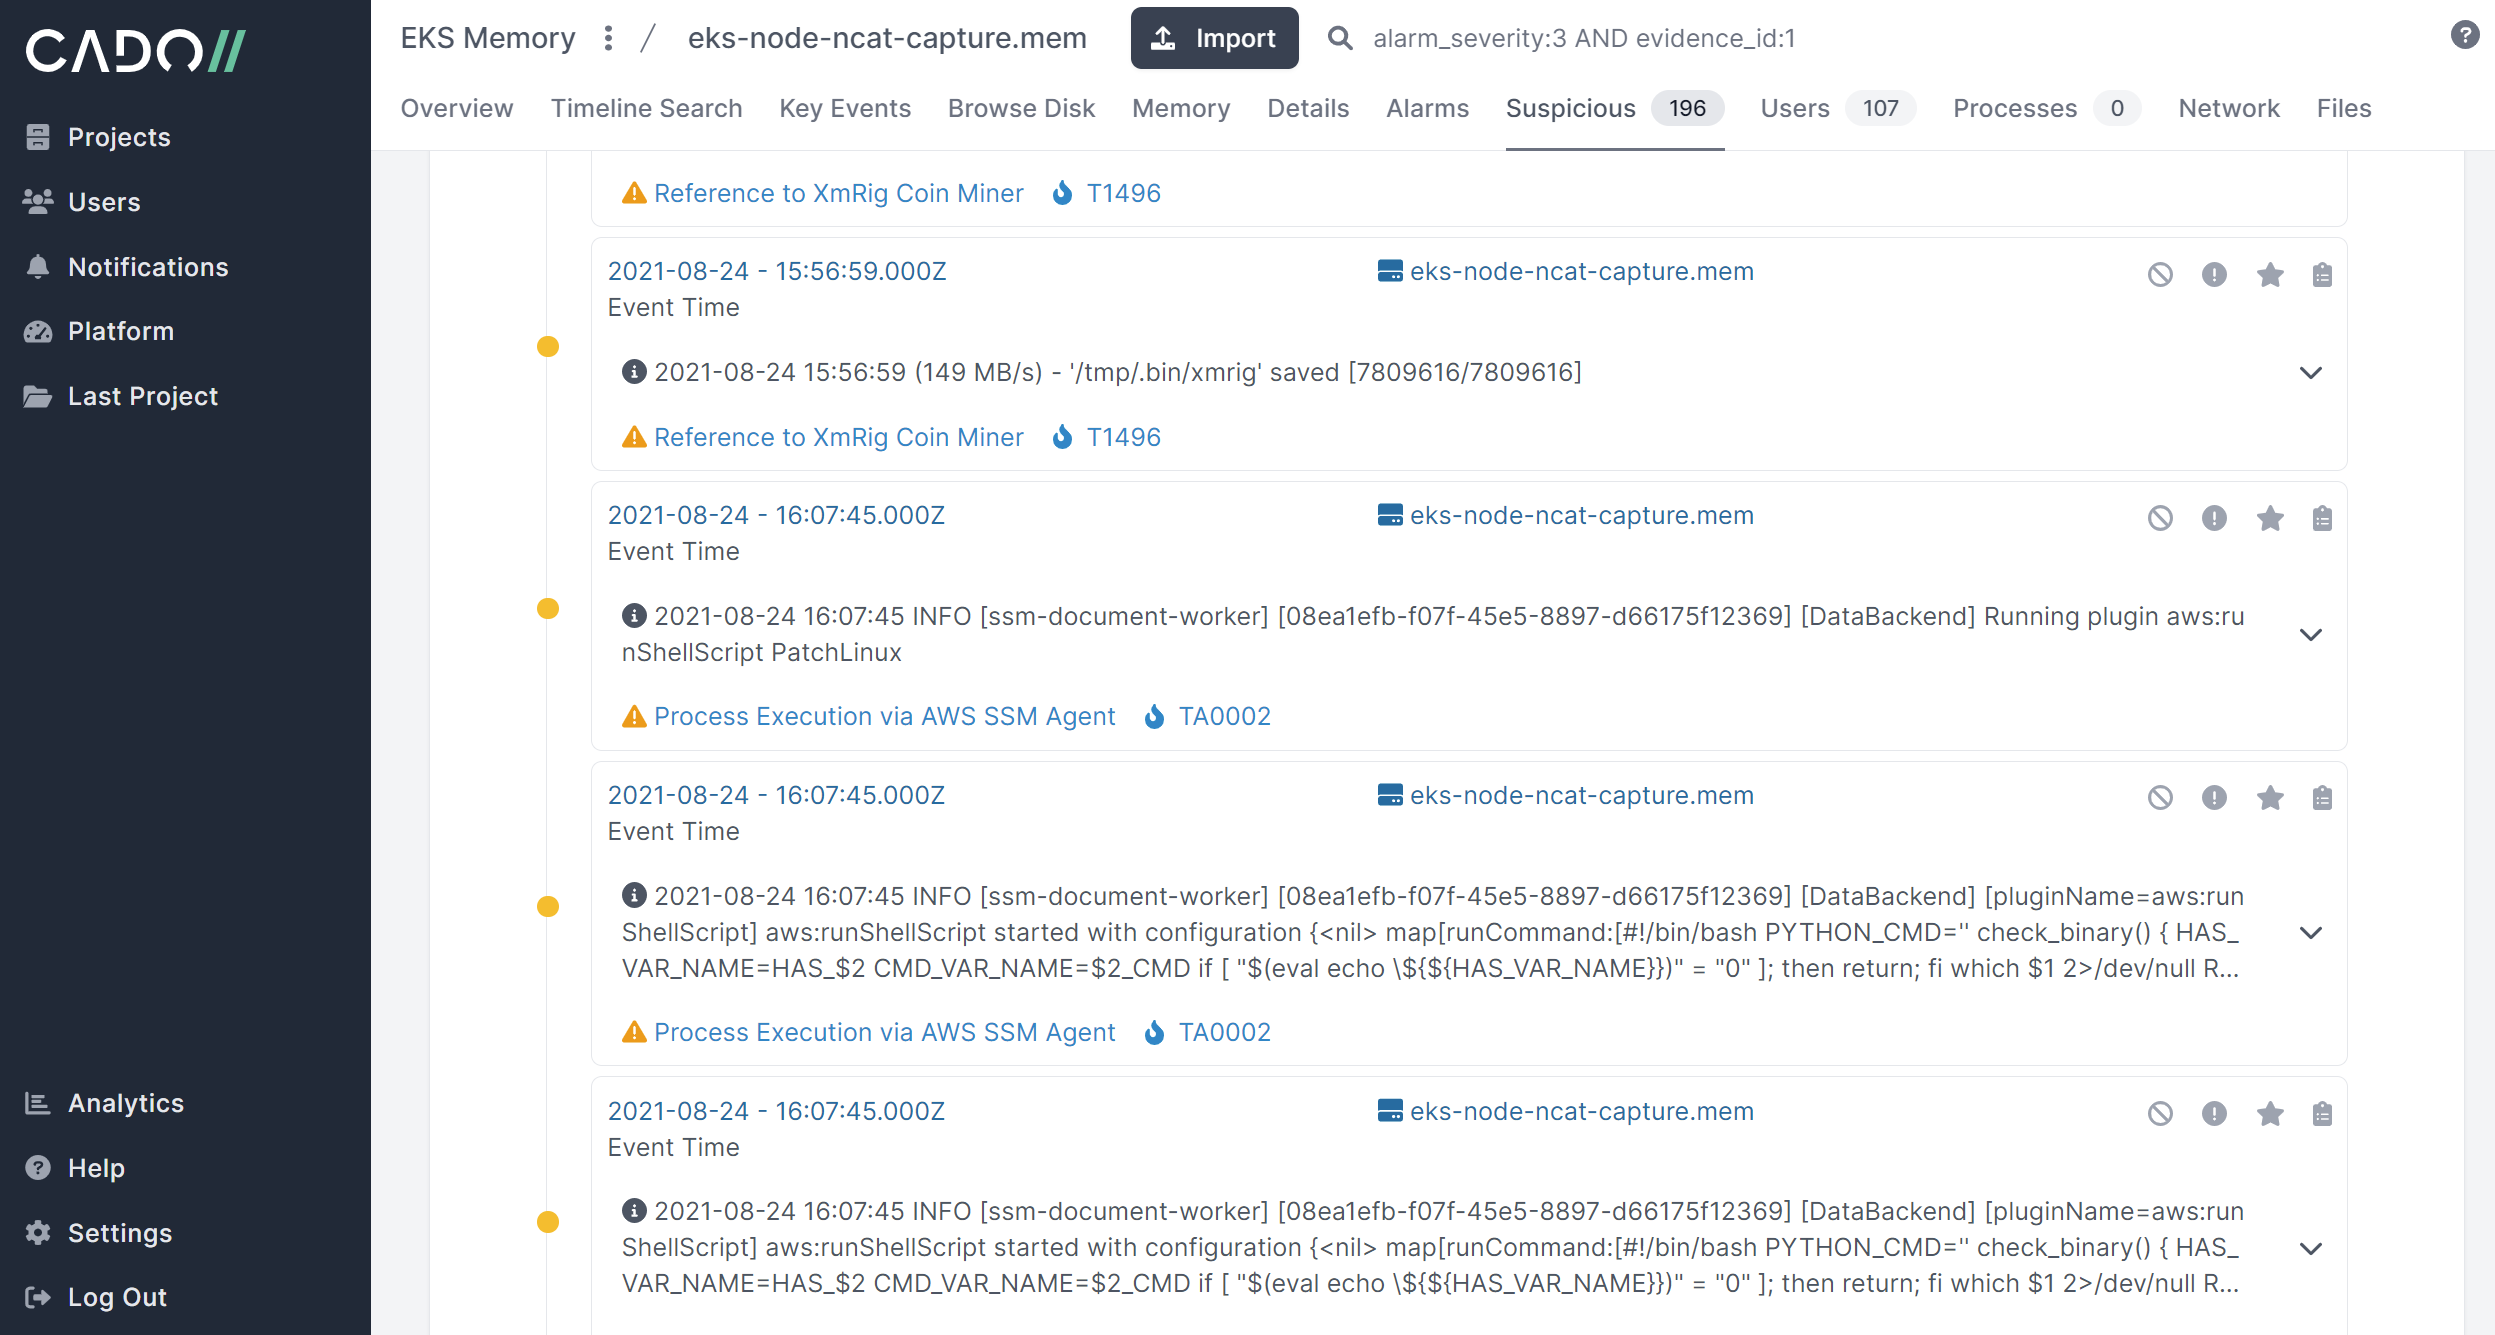
Rip Raw is a small tool to analyse the memory of compromised Linux systems.
data-recoverydigital-forensicsforensics+3
1334 years ago
androidqf preview

androidqf

GitHubmvt-project/androidqf

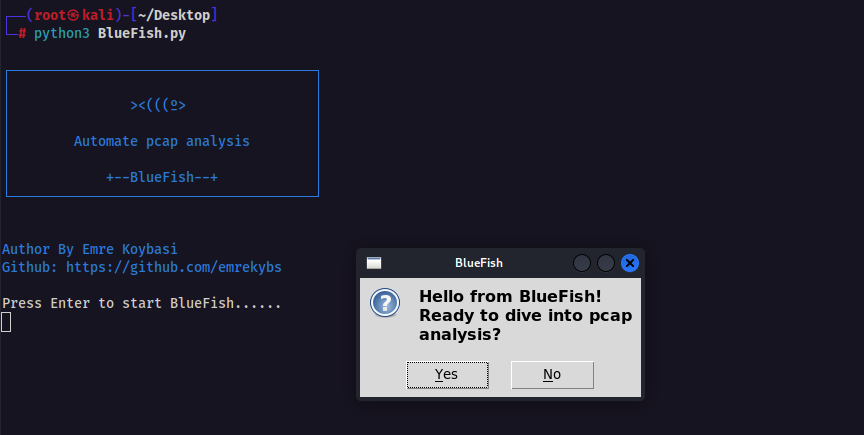
androidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…
android-securitydata-recoverydigital-forensics+4
27314 days ago
BlueFish preview

BlueFish

GitHubemrekybs/bluefish

Automation tool designed to simplify the analysis of PCAP (Packet Capture) files
forensicsincident-responseinformation-gathering+2
205 months ago
LEAF preview

LEAF

GitHubalex-cart/leaf

Linux Evidence Acquisition Framework

digital-forensicsdisk-forensicsforensics+5
1211 year ago
malpedia-flossed preview

malpedia-flossed

GitHubmalpedia/malpedia-flossed

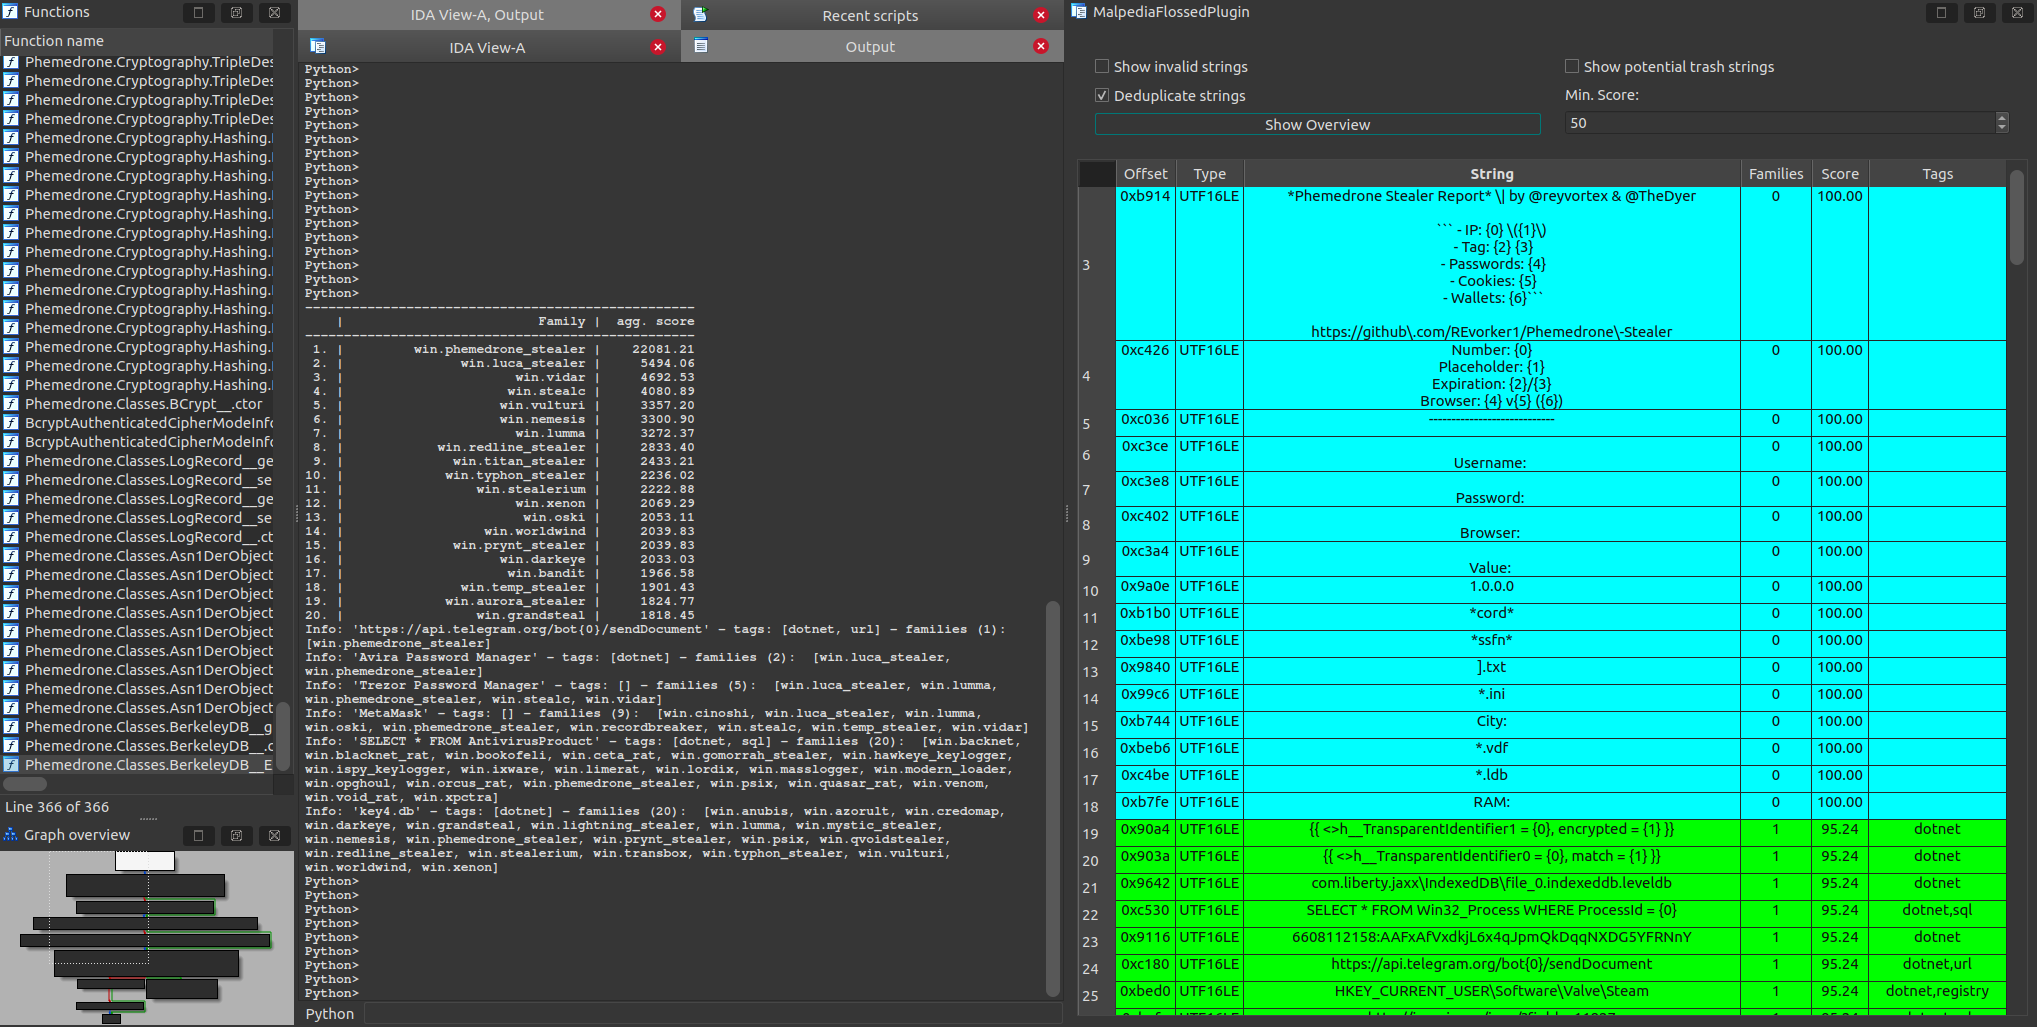
FLARE floss applied to all unpacked+dumped samples in Malpedia, pre-processed for further use.

binary-analysiscurated-resourcesdynamic-analysis-sandboxing+8
838 months ago
mailMeta preview

mailMeta

GitHubgr33nm0nk2802/mailmeta

An forensics tool to help aid in the investigation of spoofed emails based off the email headers.
digital-forensicsemail-securityforensics+2
1755 years ago
cve_2023_38831_scanner preview

cve_2023_38831_scanner

GitHubyezzfusl/cve_2023_38831_scanner

This Python application scans for the CVE-2023-38831 vulnerability in WinRAR.
dynamic-analysis-sandboxingeducationexploitation+5
11 year ago
noia preview

noia

GitHub0x742/noia

Web-based tool for browsing mobile application sandboxes, previewing SQLite databases and binary files, and downloading app data via Frida…
android-securitydynamic-analysis-sandboxingforensics+3
1275 years ago
imaginaryC2 preview

imaginaryC2

GitHubfelixweyne/imaginaryc2

Imaginary C2 is a python tool which aims to help in the behavioral (network) analysis of malware. Imaginary C2 hosts a HTTP server which captures…
command-and-controldigital-forensicsdynamic-analysis-sandboxing+5
4463 years ago
packetStrider preview

packetStrider

GitHubbenjeems/packetstrider

A network packet forensics tool for SSH

anomaly-detectionforensicsintrusion-detection+5
2556 years ago
caronte preview

caronte

GitHubeciavatta/caronte

A tool to analyze the network flow during attack/defence Capture the Flag competitions
ctfforensicsnetwork-forensics+1
6514 years ago
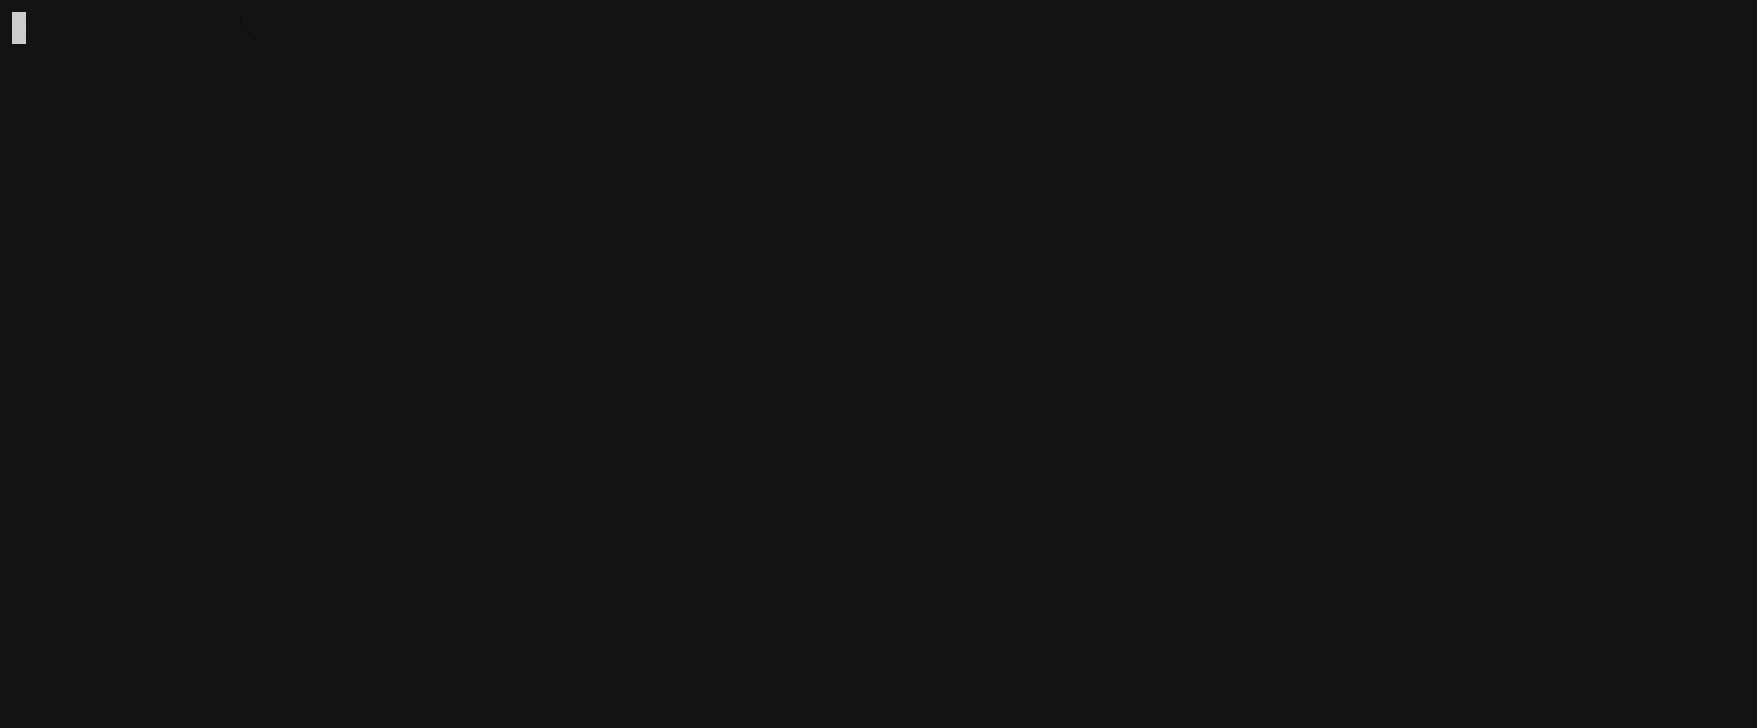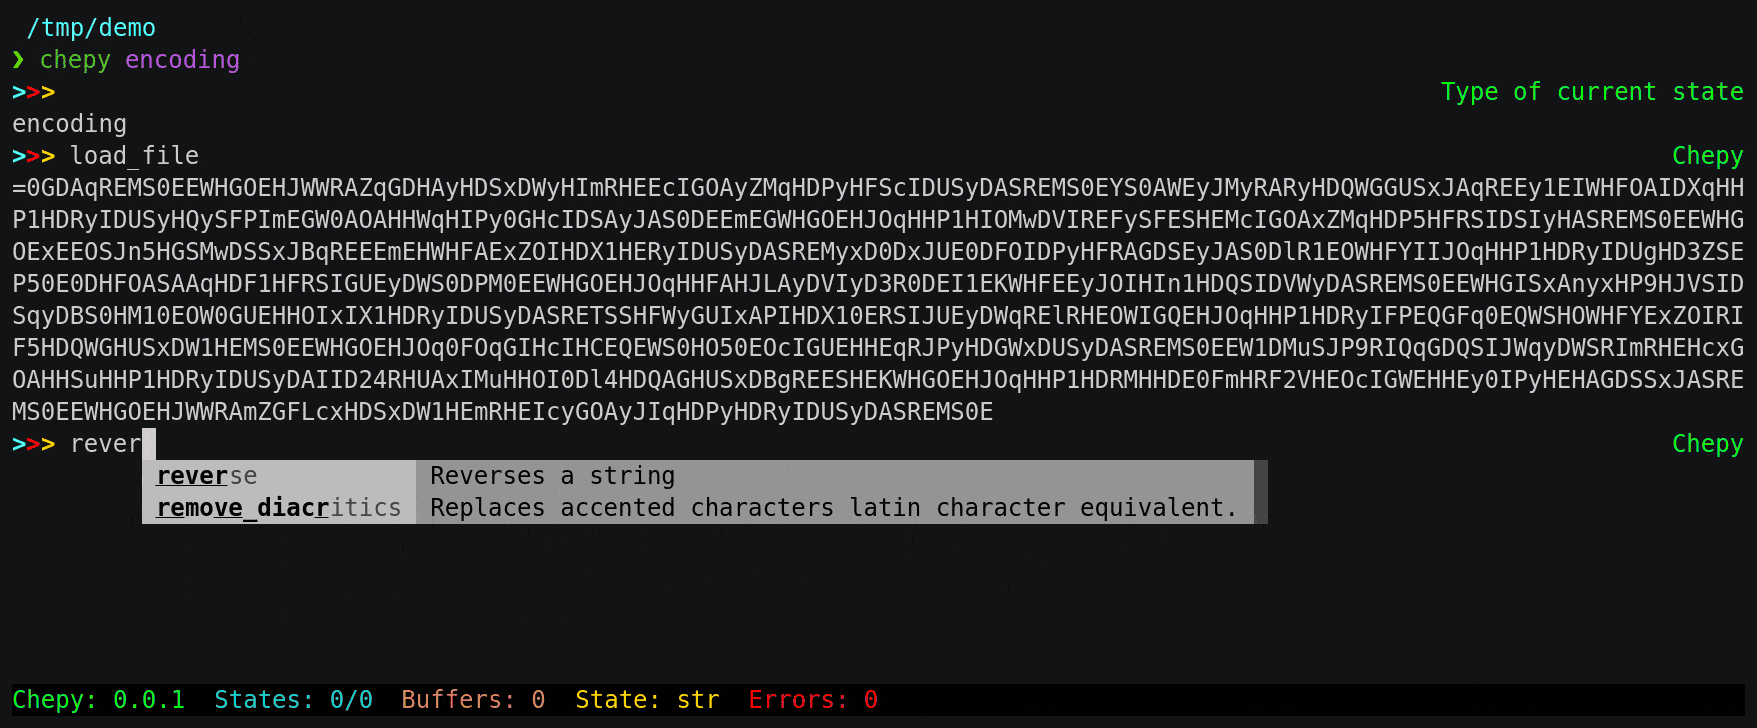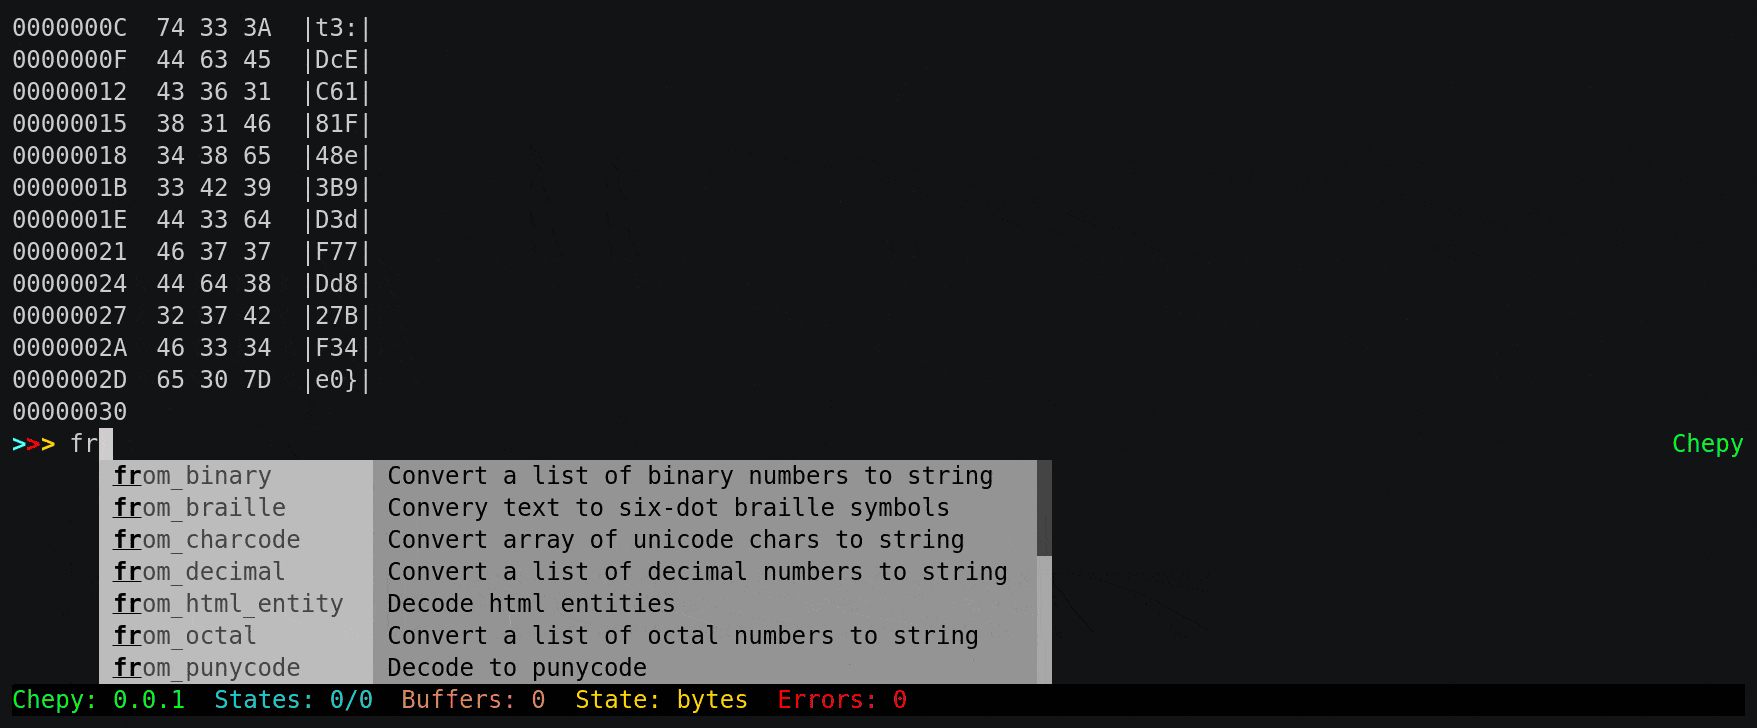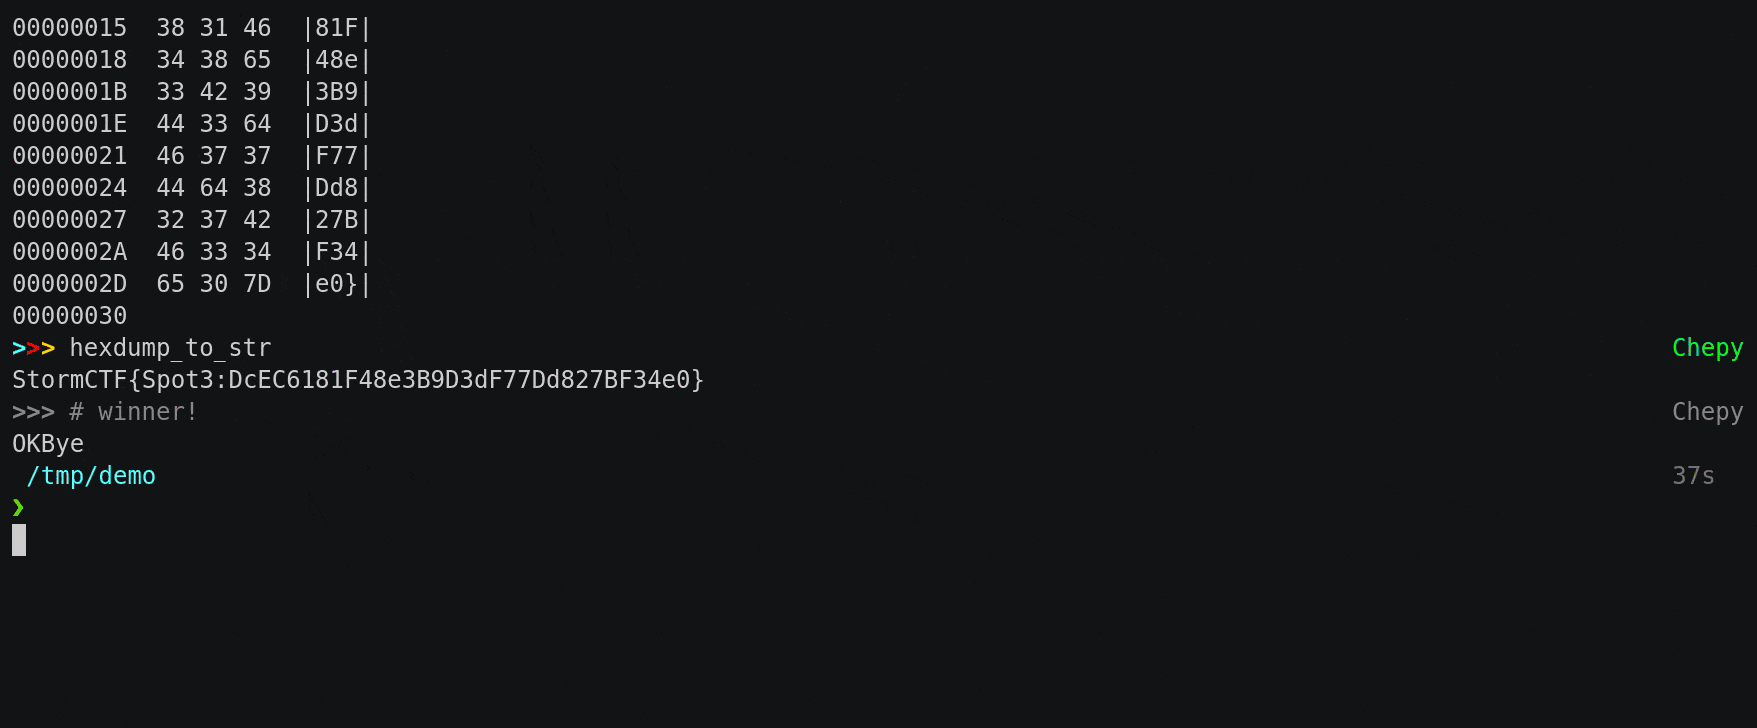
chepy preview

chepy

GitHubsecurisec/chepy

Chepy is a python lib/cli equivalent of the awesome CyberChef tool.

cryptographyctfforensics+2
1.1k4 months ago
apkinspector preview

apkinspector

GitHubhoneynet/apkinspector

APKinspector is a powerful GUI tool for analysts to analyze the Android applications.
android-securitybinary-analysiscode-analysis+7
85213 years ago
Bryobio preview

Bryobio

GitHubemrekybs/bryobio

It was developed to speed up the processes of SOC Analysts during analysis
forensicsinformation-gatheringnetwork-forensics+3
485 months ago
APT-Hunter preview

APT-Hunter

GitHubahmedkhlief/apt-hunter

APT-Hunter is Threat Hunting tool for windows event logs which made by purple team mindset to provide detect APT movements hidden in the sea of…

forensicsincident-responselog-analysis+1
1.4k1 year ago
wholeaked preview

wholeaked

GitHubutkusen/wholeaked

a file-sharing tool that allows you to find the responsible person in case of a leakage

data-exfiltrationforensicsinformation-gathering+2
1.1k4 years ago
Previous12…28Next