
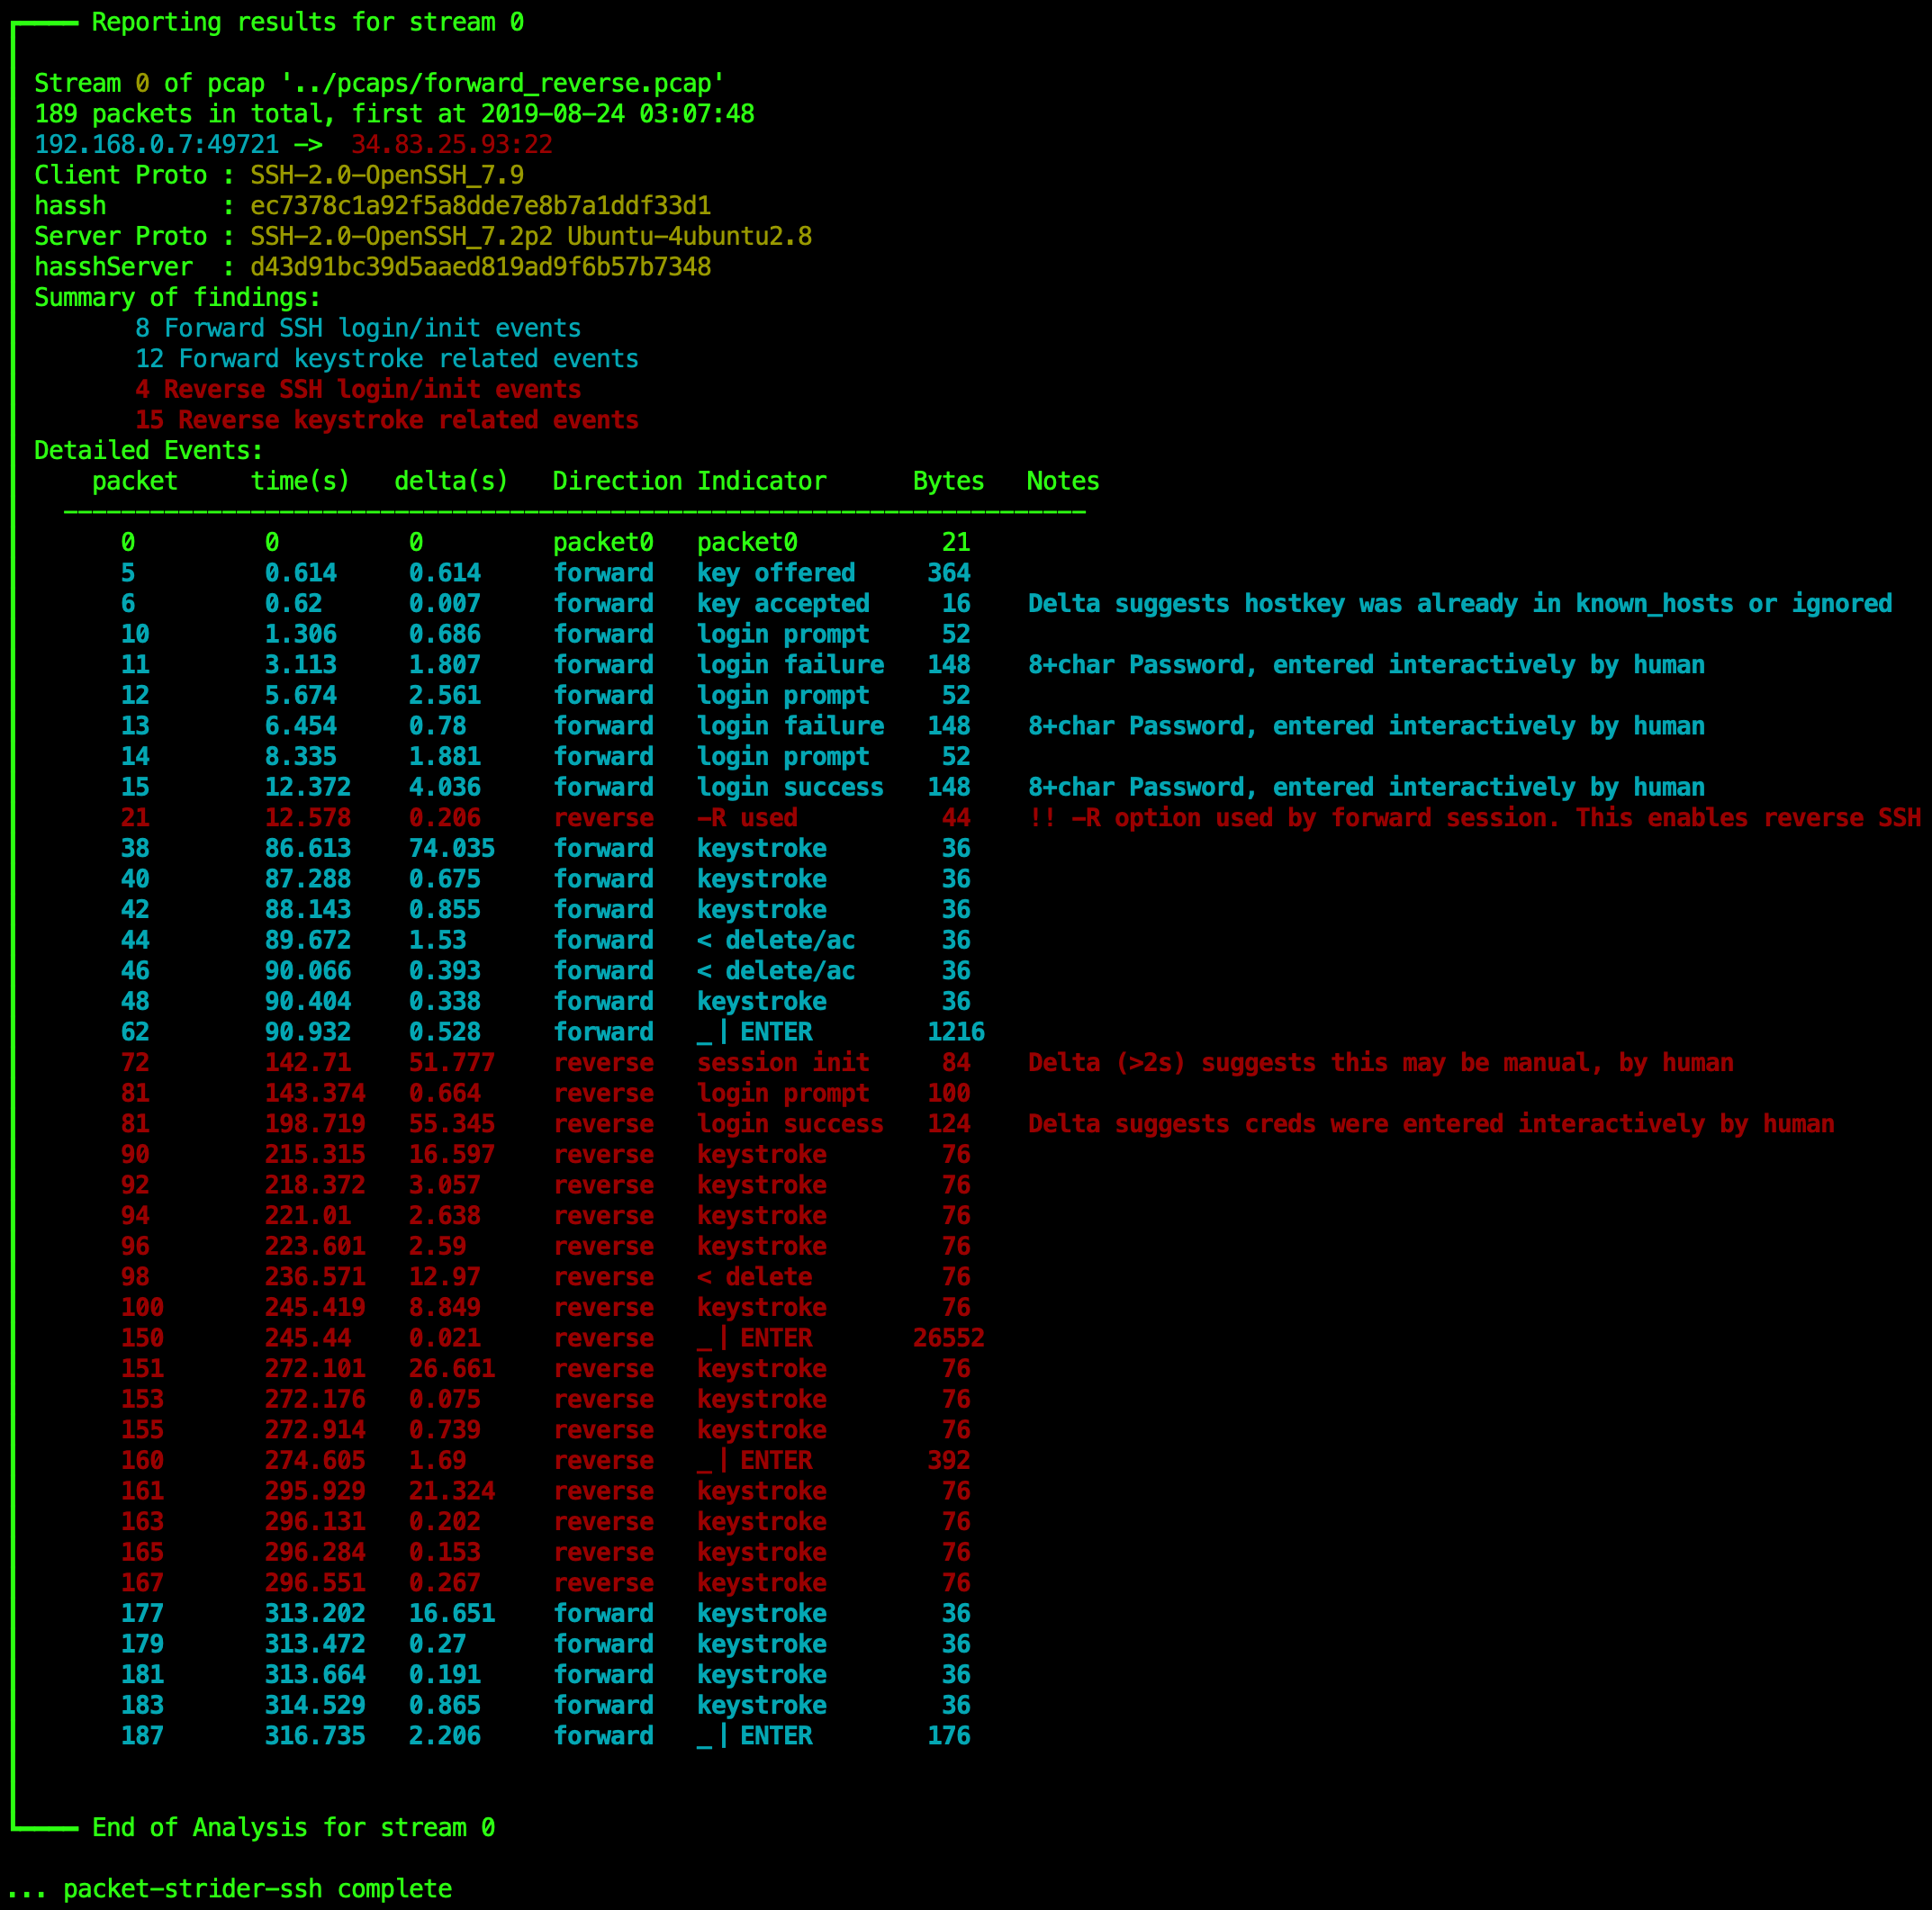
packetStrider
 benjeems/packetstrider
A network packet forensics tool for SSH
anomaly-detectionforensicsintrusion-detection+5
255
benjeems/packetstriderA network packet forensics tool for SSH
 justicerage/freedomfighting
A collection of scripts which may come in handy during your freedom fighting activities.
 stealth/psc
E2E encryption for multi-hop tty sessions or portshells + TCP/UDP port forward
 go-lanz/persistnux
Bash-based Linux persistence detection tool for DFIR investigations. Scans 15+ persistence mechanisms (systemd, cron, kernel modules, SSH,…
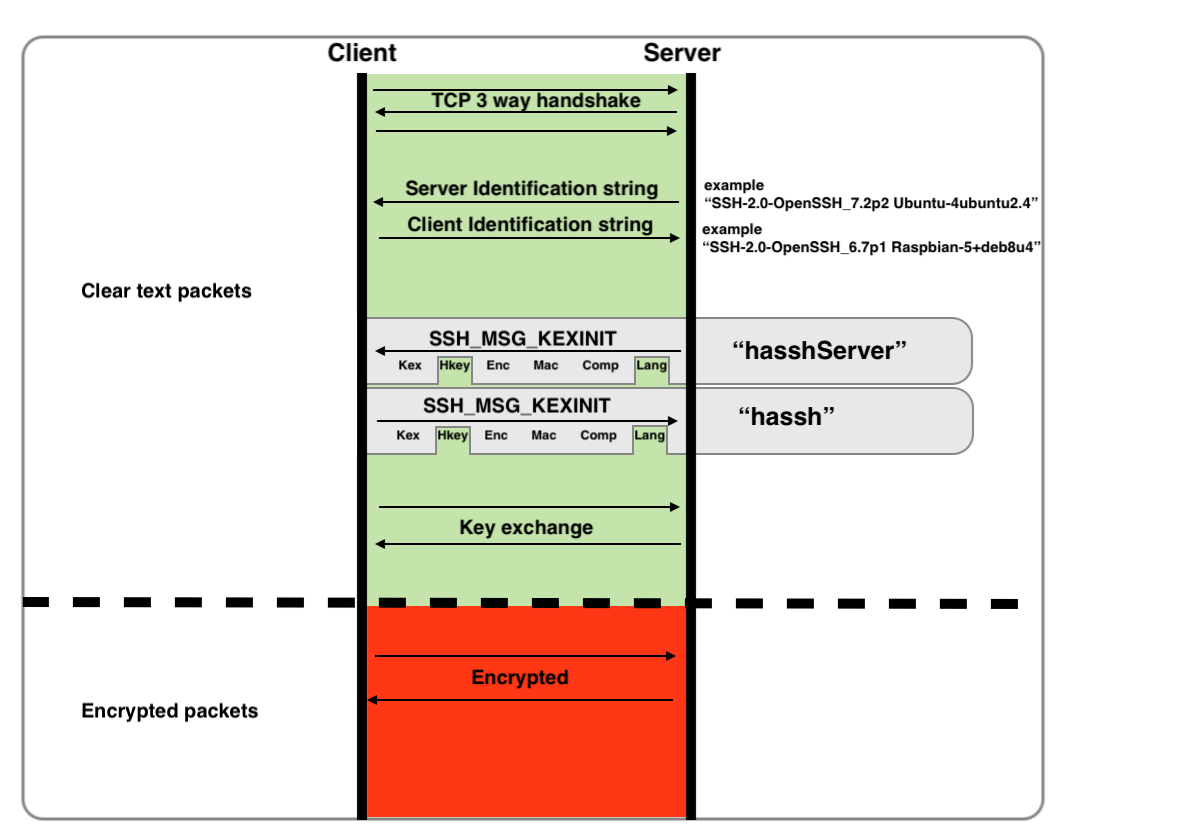 salesforce/hassh
HASSH is a network fingerprinting standard which can be used to identify specific Client and Server SSH implementations. The fingerprints can be…
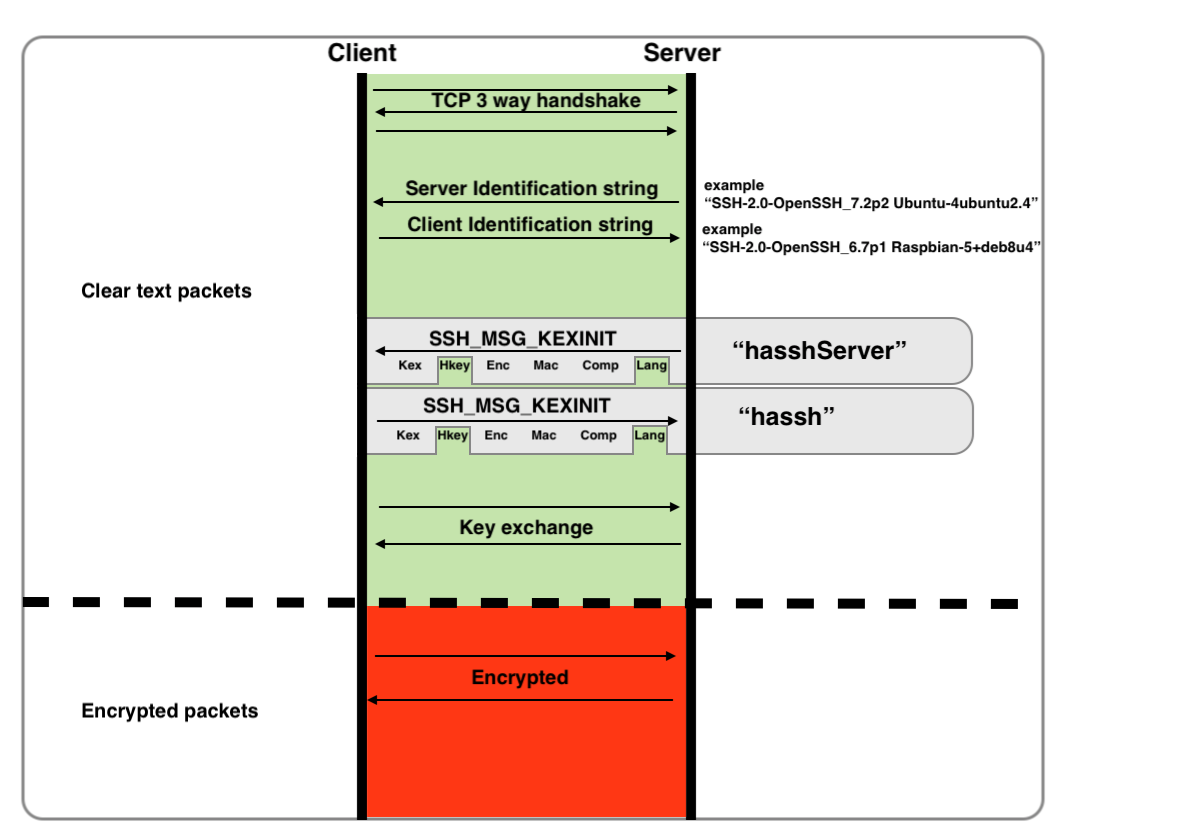 corelight/hassh
Fingerprint SSH clients and servers.
 limo57640-crypto/cpanel-cve-41940-detector
Read-only cPanel CVE-2026-41940 IOC detector for .sorry ransomware, Mr_Rot13 Filemanager backdoors, C2 callbacks, cron, SSH, and logs.
 whereisxuezugi/cplhf
Modular Bash toolkit that hardens Debian/Ubuntu systems for CyberPatriot competitions, automating account, firewall, SSH, PAM, and service hardening…