

MESH
 barghest-ngo/mesh
Encrypted peer-to-peer mesh VPN for remote mobile forensics, enabling wireless ADB and libimobiledevice acquisition, network monitoring, and…
android-securitydigital-forensicsencryption-decryption-tools+8
201
barghest-ngo/meshEncrypted peer-to-peer mesh VPN for remote mobile forensics, enabling wireless ADB and libimobiledevice acquisition, network monitoring, and…
 santoku/santoku-linux
Linux Distro for Mobile Security, Malware Analysis, and Forensics
 0x742/noia
Web-based tool for browsing mobile application sandboxes, previewing SQLite databases and binary files, and downloading app data via Frida…
 labcif/fama
Forensic Analysis for Mobile Apps (FAMA) -- module for the Autopsy Forensic Browser
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
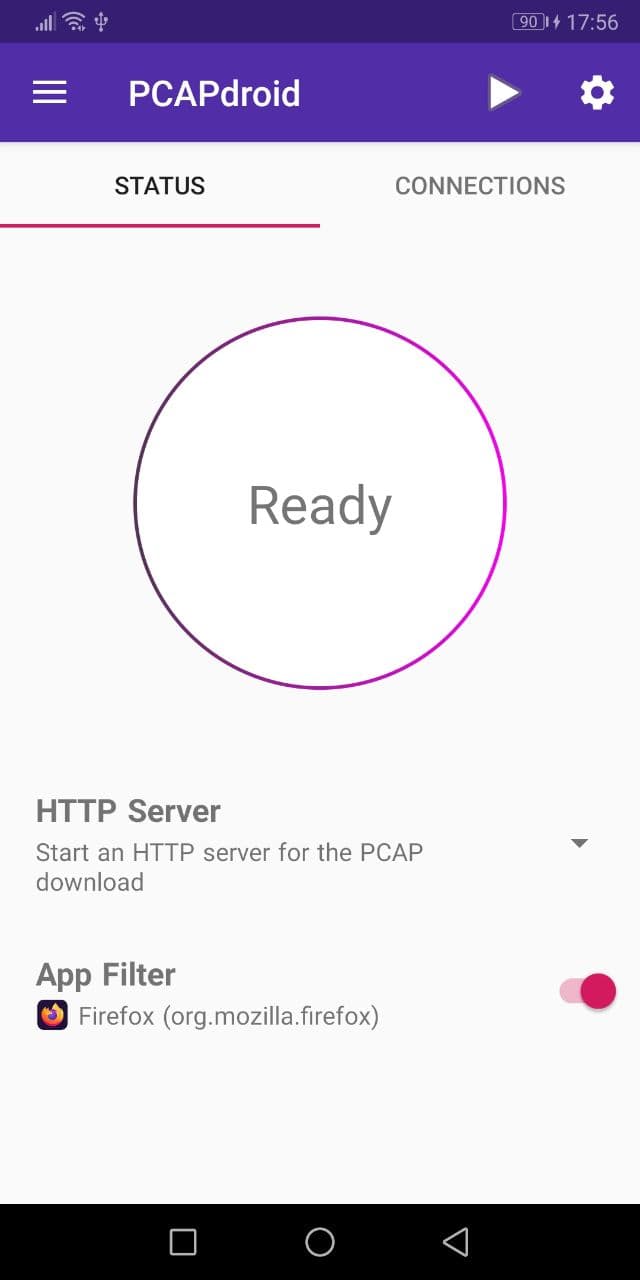 emanuele-f/pcapdroid
No-root network monitor, firewall and PCAP dumper for Android
 cyb3rmx/qu1cksc0pe
All-in-One malware analysis tool.
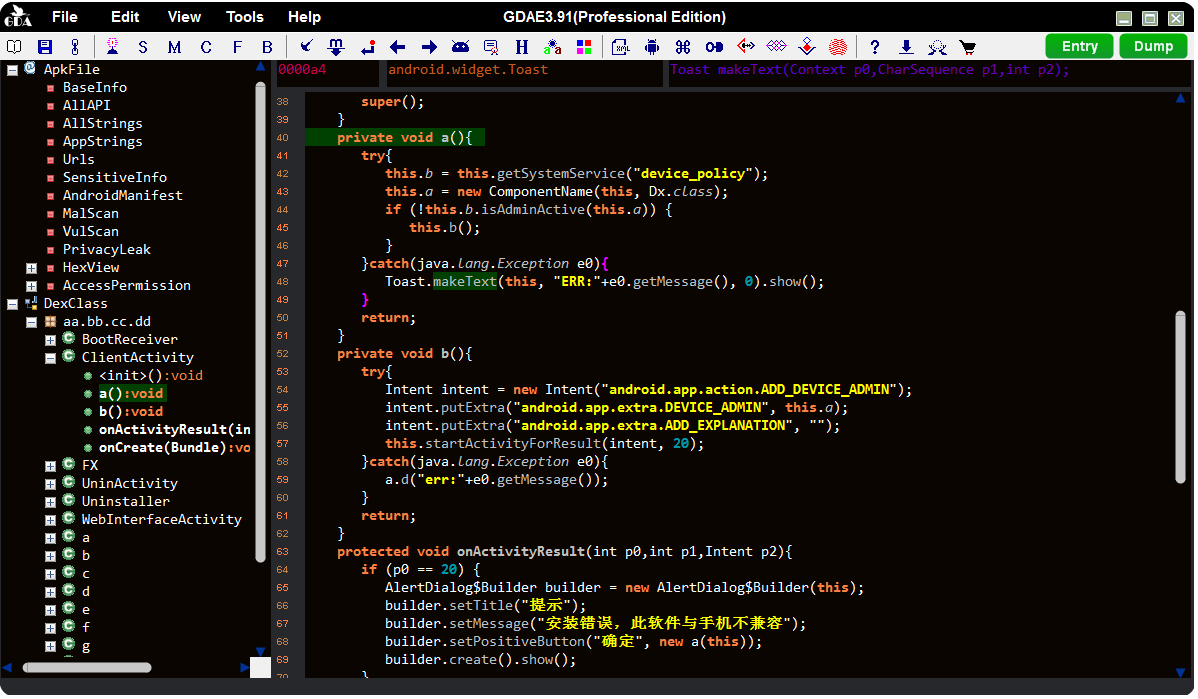 charles2gan/gda-android-reversing-tool
the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…
 b16f00t/whapa
Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…
 nelenkov/android-backup-extractor
Extract and repack Android ADB backups (ICS+). Supports encrypted archives, tar conversion, and standard I/O for forensic analysis or data recovery.
 honeynet/apkinspector
APKinspector is a powerful GUI tool for analysts to analyze the Android applications.
 den4uk/andriller
📱 Andriller - is software utility with a collection of forensic tools for smartphones. It performs read-only, forensically sound, non-destructive…
 thakur2309/pagasus-pro
Python ADB-based Android device management and security audit toolkit with an interactive menu for root detection, permission dumps, debuggable app…
 nowsecure/fsmon
Filesystem monitor tool for Linux/Android iOS/macOS
 yhs0602/android-disassembler
Disassemble ANY files including .so (NDK, JNI), Windows PE(EXE, DLL, SYS, etc), linux binaries, libraries, and any other files such as pictures,…
 mvt-project/androidqf
androidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…
