
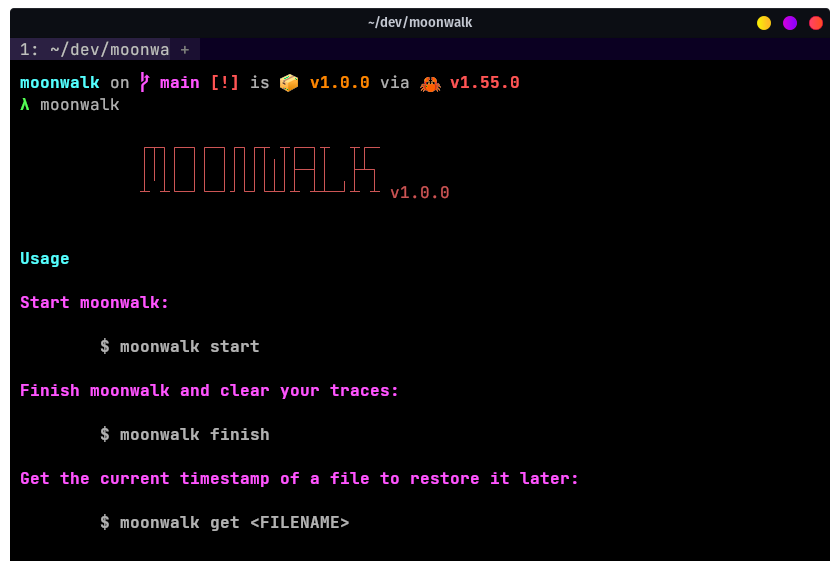
moonwalk
 mufeedvh/moonwalk
Cover your tracks during Linux Exploitation by leaving zero traces on system logs and filesystem timestamps.
forensicspenetration-testingpost-exploitation+2
1.5k4 years ago
mufeedvh/moonwalkCover your tracks during Linux Exploitation by leaving zero traces on system logs and filesystem timestamps.
 sobri3195/pegasus-neo
PEGASUS-NEO is a comprehensive penetration testing framework designed for security professionals and ethical hackers. It combines multiple security…
 rnb-team/loghound
Post-Exploitation EVTX Analyzer for BloodHound Mapping
 onapsis/onapsis_cve-2025-31324_scanner_tools
Python-based scanner for CVE-2025-31324 that identifies vulnerable SAP NetWeaver Visual Composer instances and detects indicators of compromise from…
 ir-huntguardians/cve-2023-38831-hunt
PowerShell-based tool to detect and analyze exploitation attempts targeting CVE-2023-38831, aiding incident response and forensic investigations.
 devploit/awesome-ctf-resources
A list of Capture The Flag (CTF) frameworks, libraries, resources and software for started/experienced CTF players 🚩
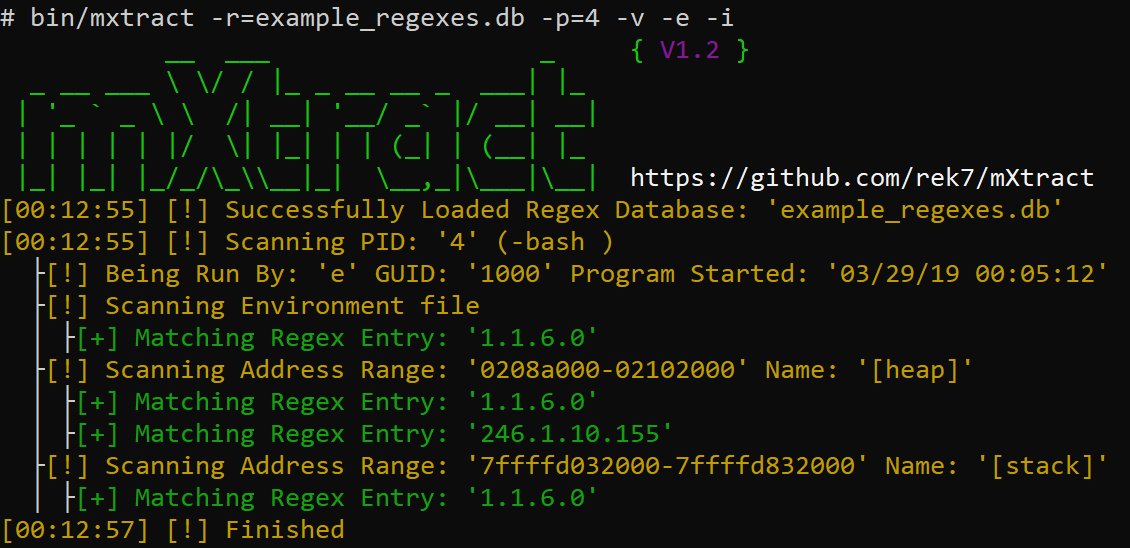 rek7/mxtract
mXtract - Memory Extractor & Analyzer
 fox-it/cisco-ios-xe-implant-detection
Cisco IOS XE implant scanning & detection (CVE-2023-20198, CVE-2023-20273)
 nikaiw/vmkatz
Extract Windows credentials directly from VM memory snapshots and virtual disks
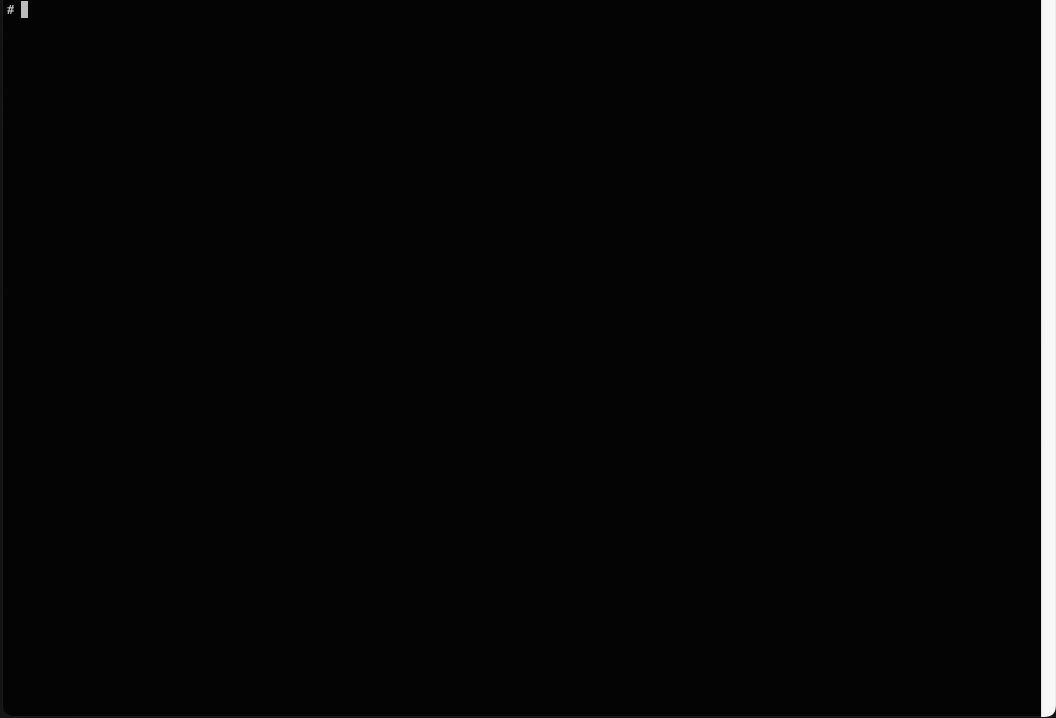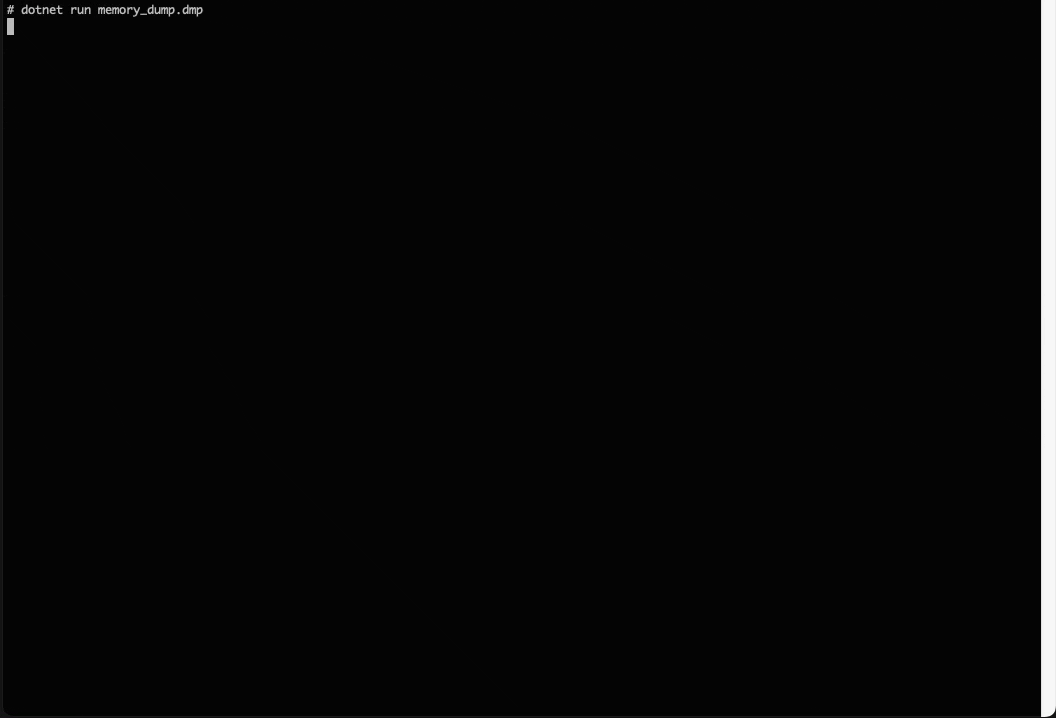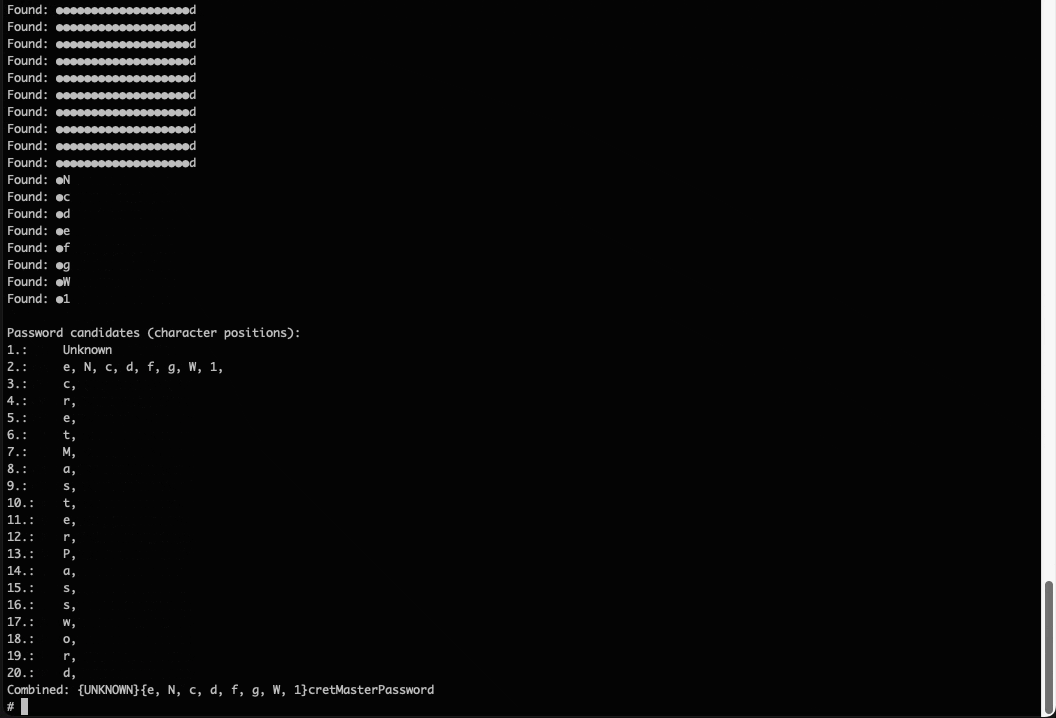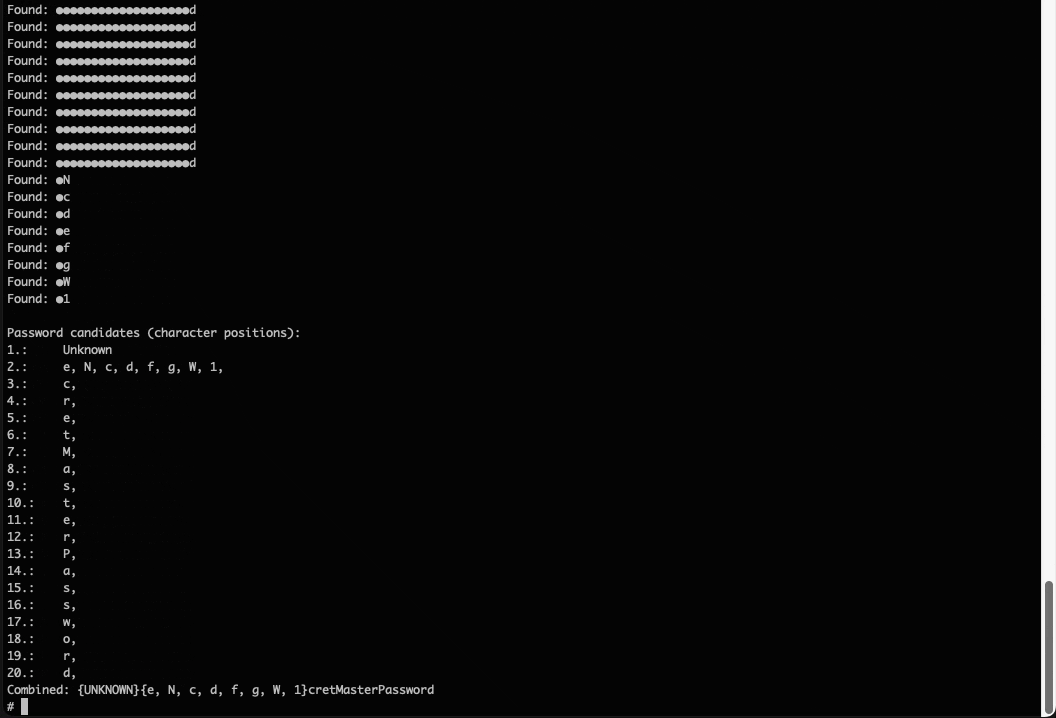 vdohney/keepass-password-dumper
Original PoC for CVE-2023-32784
 forrest-orr/artifacts-kit
Pseudo-malicious usermode memory artifact generator kit designed to easily mimic the footprints left by real malware on an infected Windows OS.
 phxbandit/scripts-and-tools
Scripts and utilities to help your hacking needs
 ioncodes/cve-2020-16938
Bypassing NTFS permissions to read any files as unprivileged user.
 piat0n/baremetal-ram-dumper
A bare-metal x86 utility to dump physical RAM directly to disk. Built and tested for Cold Boot Attack experiments on frozen memory.
 scalabli/sashay
Sashay is an automatic installer for useful tools.
 puckblush/tofu
Windows offline filesystem hacking tool for Linux
 warpedatom/offsetinspect
PowerShell toolkit for AMSI/Defender detection-boundary analysis and static malware triage maps byte offsets to detection triggers, plus YARA,…
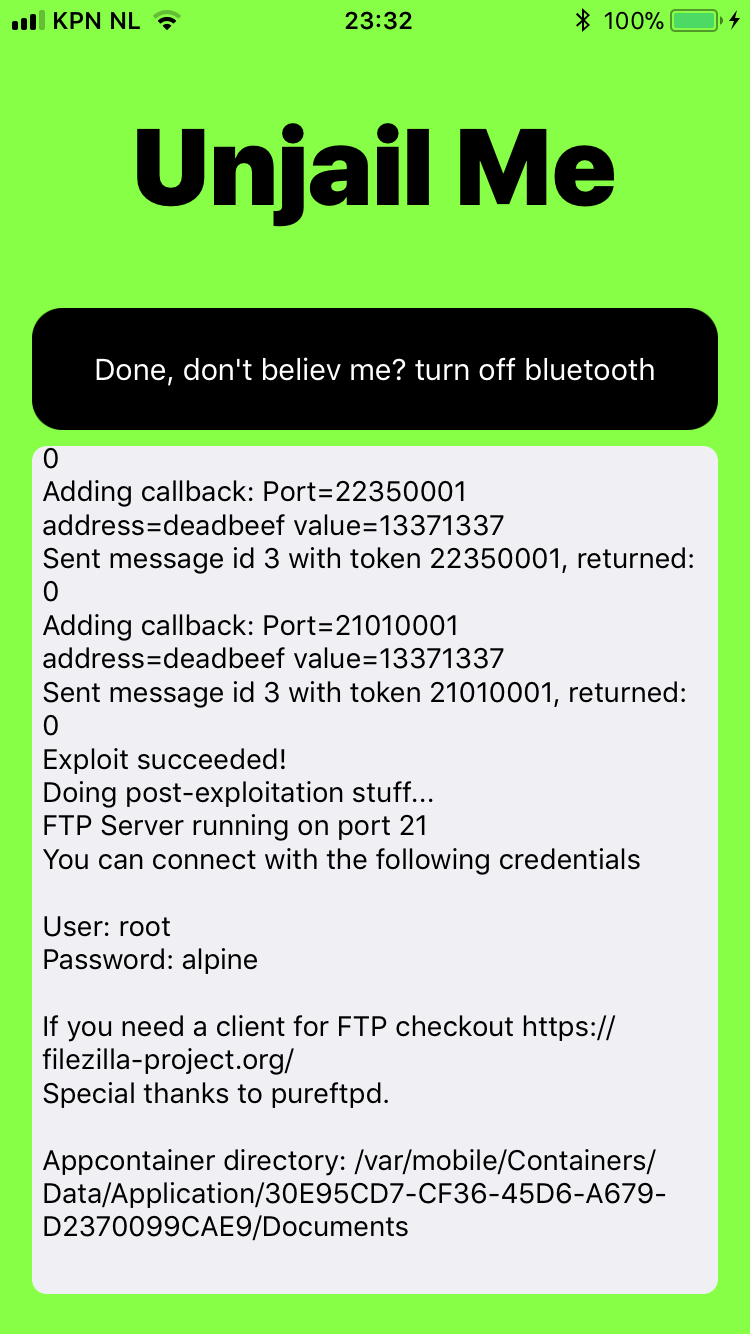 mtjailed/unjailme
A sandbox escape based on the proof-of-concept (CVE-2018-4087) by Rani Idan (Zimperium)