
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
21 results
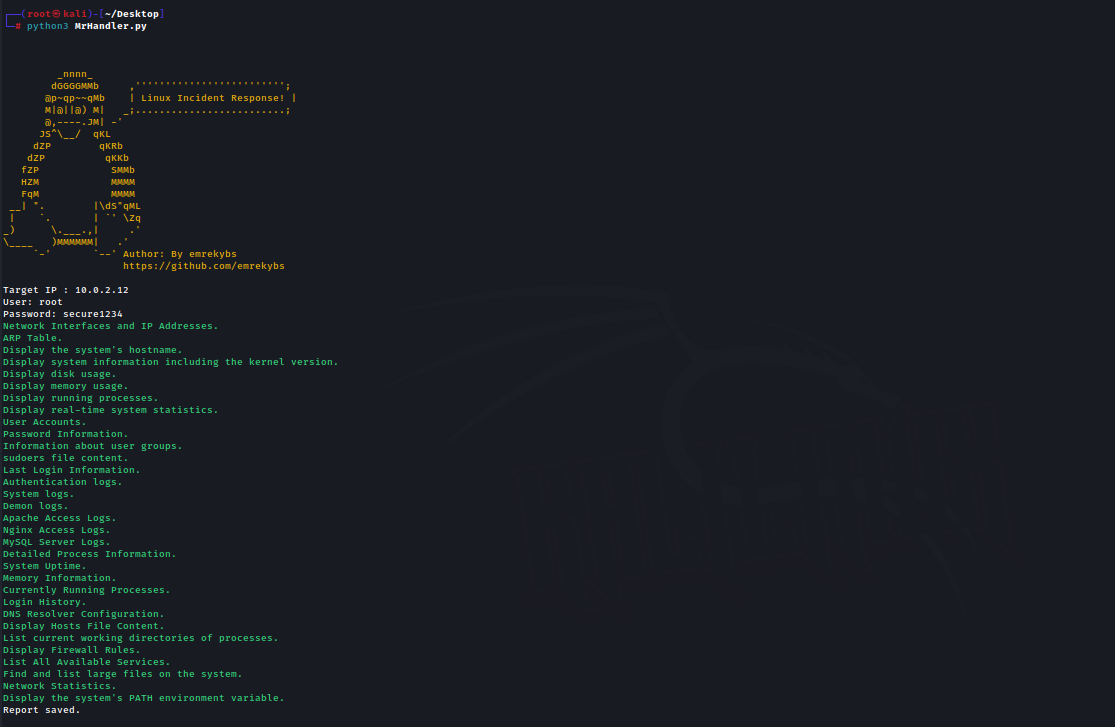
MrHandler preview

MrHandler

GitHubemrekybs/mrhandler

SSH-based Linux incident response tool that executes diagnostic commands to collect network configs, logs, user accounts, and processes, then…
digital-forensicsforensicsincident-response+1
86
6 months ago
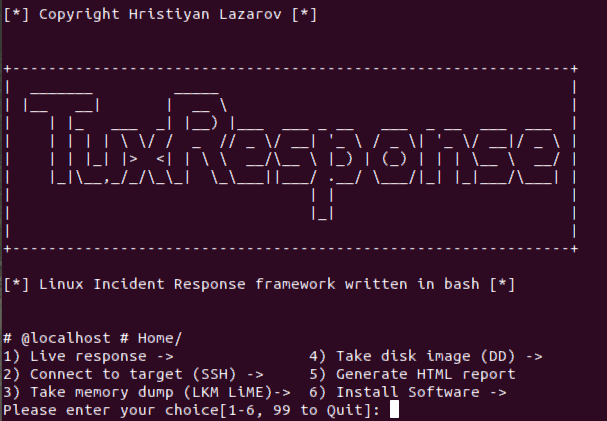
TuxResponse preview

TuxResponse

GitHubla3ar0v/tuxresponse

Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.

digital-forensicsdisk-forensicsforensics+5
915 months ago
Pegasus-Malware-Scan preview

Pegasus-Malware-Scan

GitHubsobri3195/pegasus-malware-scan

Multi-layered malware scanner combining hash-based verification, behavioral analysis, and sandbox execution for threat detection, incident response,…

educationforensicsincident-response+3
61 year ago
LinuxCatScale preview

LinuxCatScale

GitHubwithsecurelabs/linuxcatscale

Incident Response collection and processing scripts with automated reporting scripts

digital-forensicsforensicsincident-response+2
3392 years ago
volatility3 preview

volatility3

GitHubvolatilityfoundation/volatility3

Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…
digital-forensicsforensicsincident-response+2
4.4k14 days ago
LSMS preview

LSMS

GitHubsqall01/lsms

Linux Security and Monitoring Scripts

defensive-toolsforensicsincident-response+2
3301 year ago
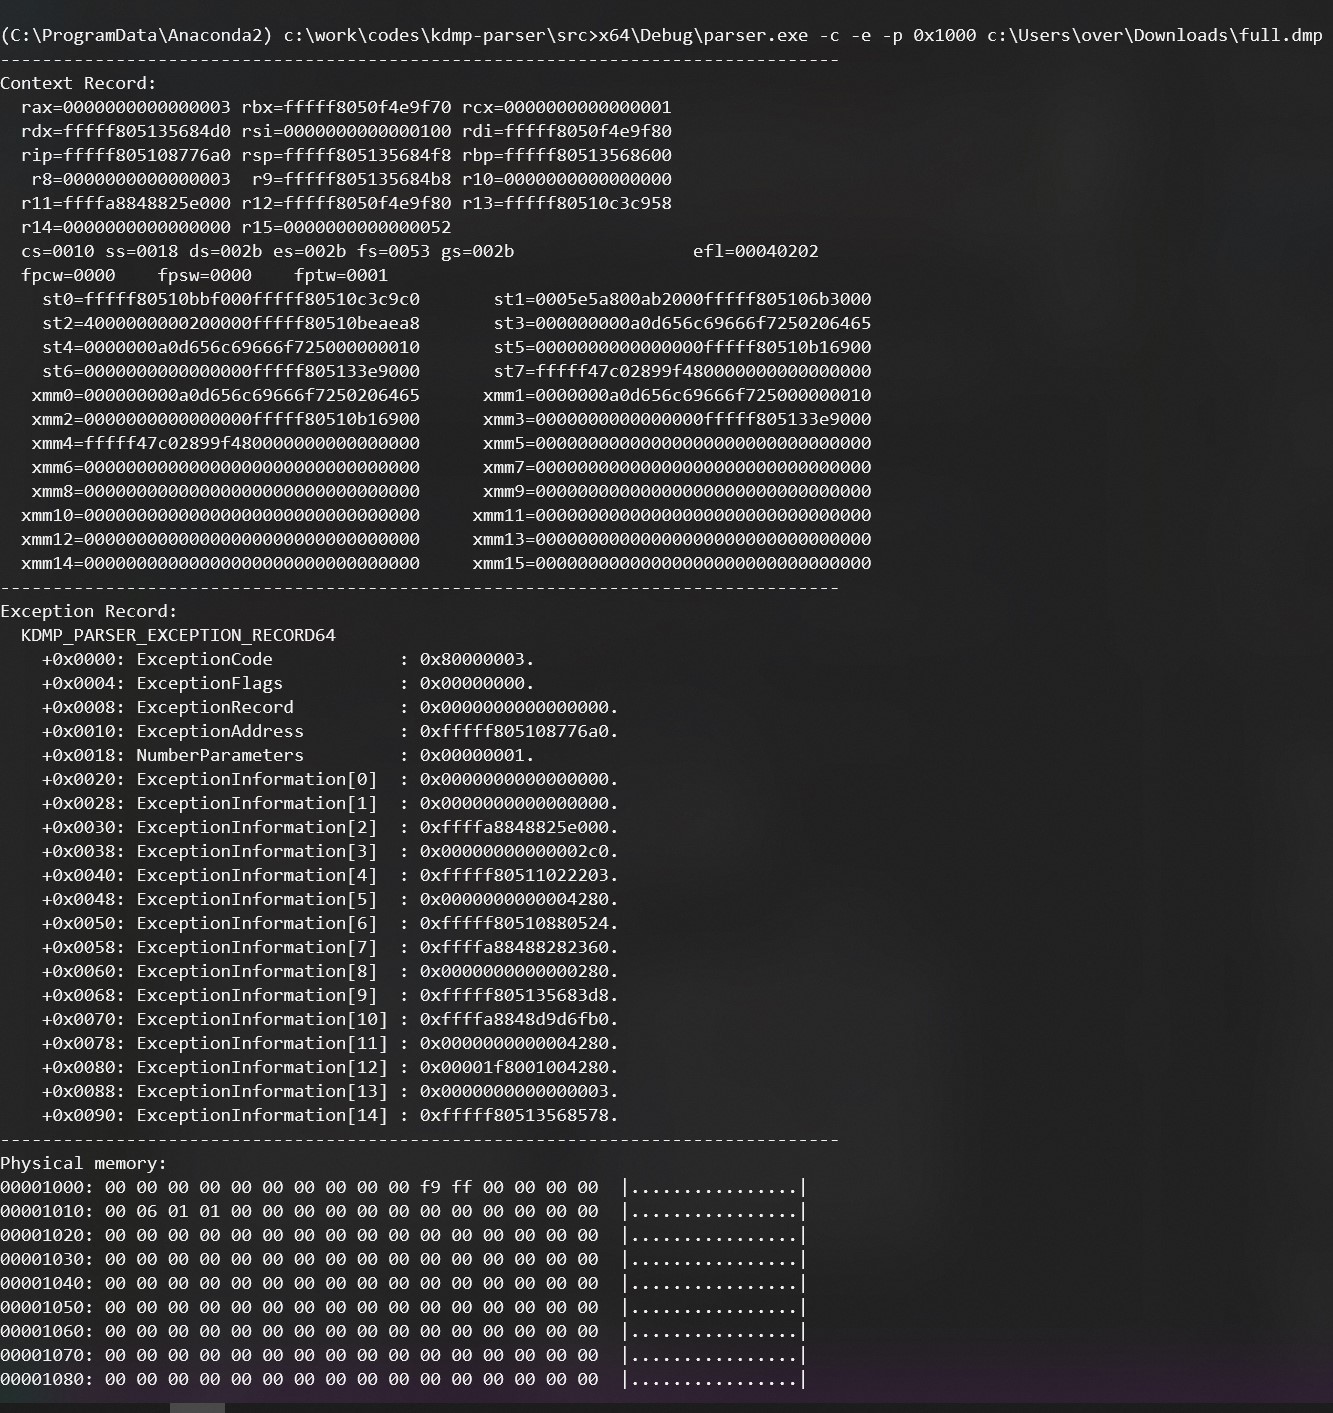
kdmp-parser preview

kdmp-parser

GitHub0vercl0k/kdmp-parser

A Windows kernel dump C++ parser library with Python 3 bindings.
digital-forensicsforensicsincident-response+1
2150 years ago
mini-shai-hulud-scanner preview

mini-shai-hulud-scanner

GitHubintrudify/mini-shai-hulud-scanner

Scanner for the Mini Shai-Hulud npm/PyPI supply chain worm (NHS CC-4781 · CVE-2026-45321). Detects gh-token-monitor persistence, payload artefacts,…
forensicsincident-responseioc-management+6
24 months ago
cve-2025-55182-scanner preview

cve-2025-55182-scanner

GitHubtechgaun/cve-2025-55182-scanner

Python-based scanner for CVE-2025-55182 indicators of compromise. Checks filesystem paths, processes, systemd services, cron persistence, and…

forensicsincident-responsemalware-analysis+3
39 months ago
linux-explorer preview
Archived

linux-explorer

GitHubintezer/linux-explorer

Easy-to-use live forensics toolbox for Linux endpoints
digital-forensicsforensicsincident-response+7
4042 years ago
easy_triage preview

easy_triage

GitHubmsuhanov/easy_triage

Scripts to triage compromised systems (Linux, ESXi, FreeBSD/NetScaler)
defensive-toolsdigital-forensicsforensics+4
524 days ago
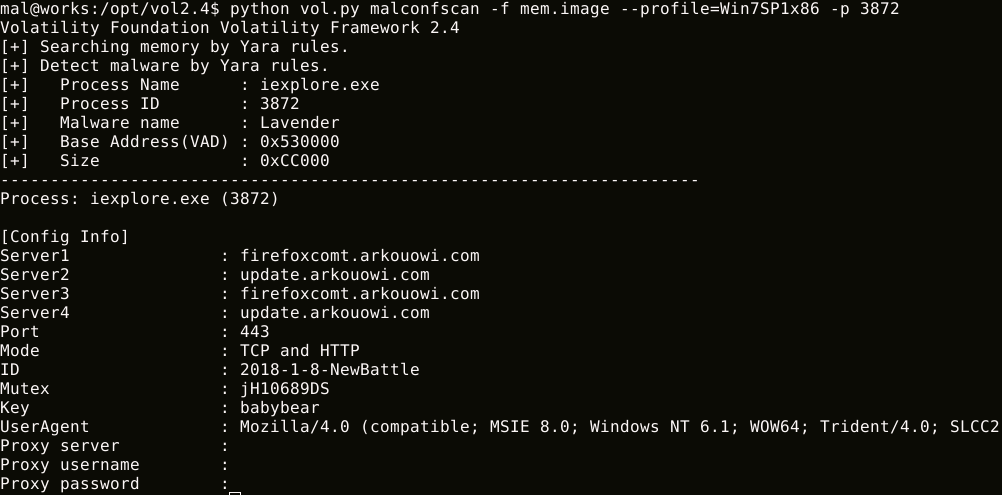
MalConfScan preview

MalConfScan

GitHubjpcertcc/malconfscan

Volatility plugin for extracts configuration data of known malware
digital-forensicsforensicsincident-response+3
4982 years ago
autotimeliner preview

autotimeliner

GitHubandreafortuna/autotimeliner

Automagically extract forensic timeline from volatile memory dump
digital-forensicsforensicsincident-response+1
1337 months ago
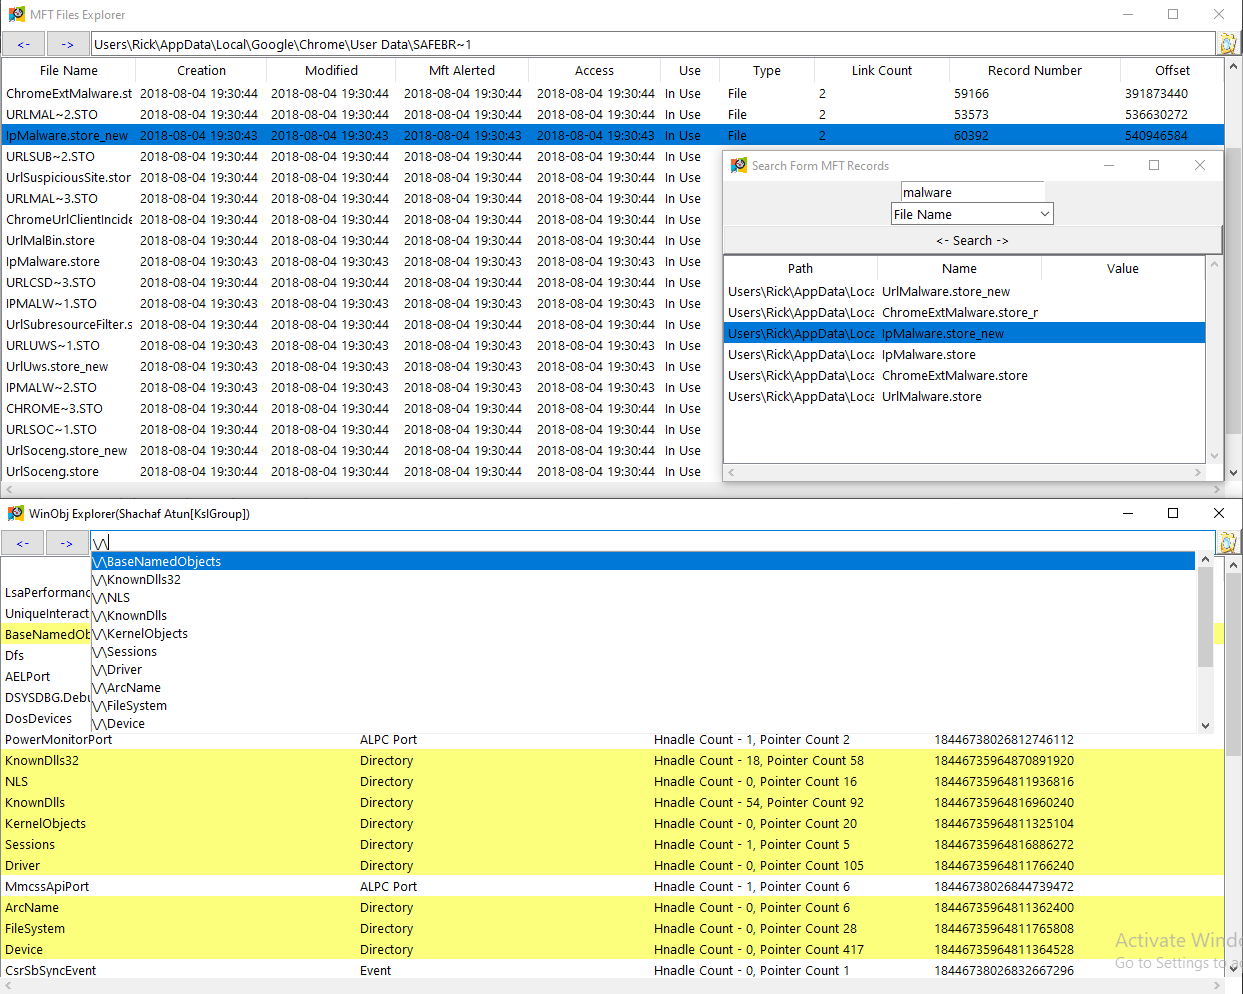
VolExp preview

VolExp

GitHubmemoryforensics1/volexp

volatility explorer (volatility 2)
digital-forensicsforensicsincident-response+2
955 years ago
mongobleed-detector preview

mongobleed-detector

GitHubneo23x0/mongobleed-detector

Detection Script for MongoBleed Exploitation
database-securitydigital-forensicsforensics+5
829 months ago
iLEAPP preview

iLEAPP

GitHubabrignoni/ileapp

Parses iOS and iPadOS forensic extractions into HTML, TSV, timeline, KML, and LAVA reports with modular artifact discovery and encrypted iTunes…
digital-forensicsforensicsincident-response+3
1.3k14h 26m ago
agensic preview

agensic

GitHubalex188dot/agensic

Cryptographic terminal forensics and session replay for AI agents. Tracks, signs, and audits every command with provenance labels, replayable…
ai-securityauthenticationdigital-forensics+5
291 month ago
pacmap preview

pacmap

GitHubm0vi0/pacmap

Graph-first network traffic visualizer for live capture and PCAP replay with checkpoint diffing, path tracing, and Wireshark-style display filters…

dns-analysisforensicsincident-response+4
1326 days ago
Previous12Next