An-Integrated-Wireless-Network-Forensic-Analysis-Framework

This framework combines a set of existing open source tools into an integrated package that automates the forensics investigation process. It is able…

This framework combines a set of existing open source tools into an integrated package that automates the forensics investigation process. It is able…

Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…

Arkime is an open source, large scale, full packet capturing, indexing, and database system.

Volatility plugin to extract X screenshots from a memory dump

An advanced memory forensics framework

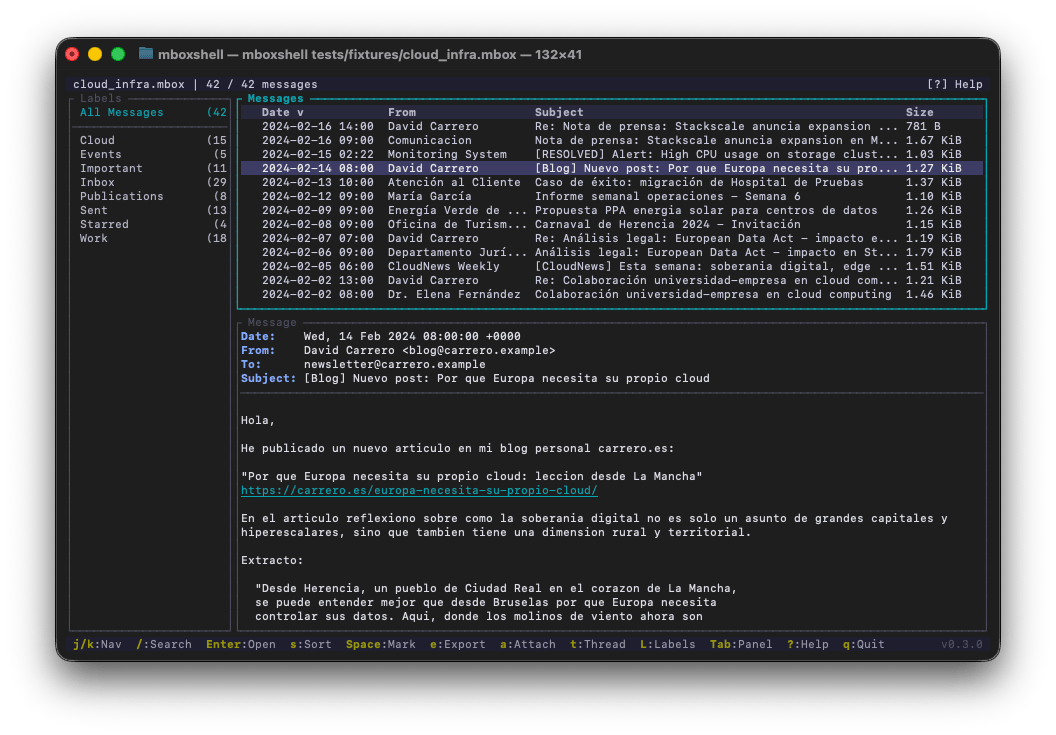
mboxShell. Fast terminal viewer for MBOX files of any size. Open, search and export emails from Gmail Takeout backups (50GB+) without loading them…

Differential Analysis of Malware in Memory

KeePass Master Password Extraction PoC for Linux

AIL framework - Analysis Information Leak framework. Project moved to https://github.com/ail-project

A curated list of awesome Hacking tutorials, tools and resources

IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…

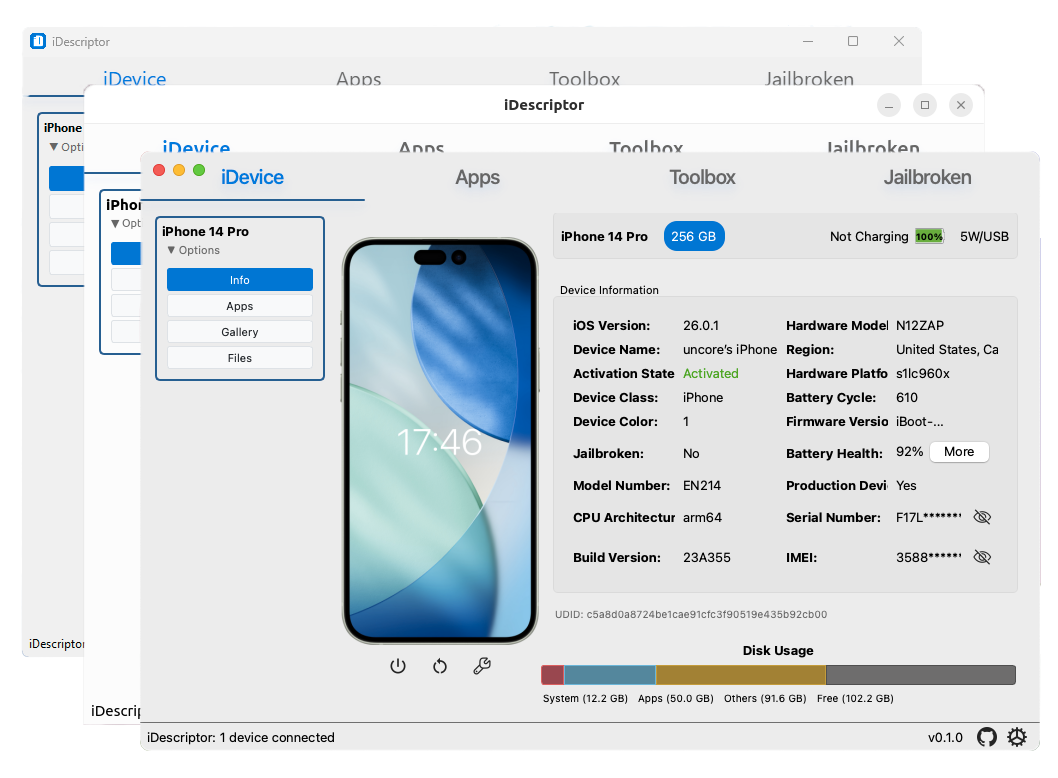
privacy-first, open-source and free idevice management tool written in Rust and Qt

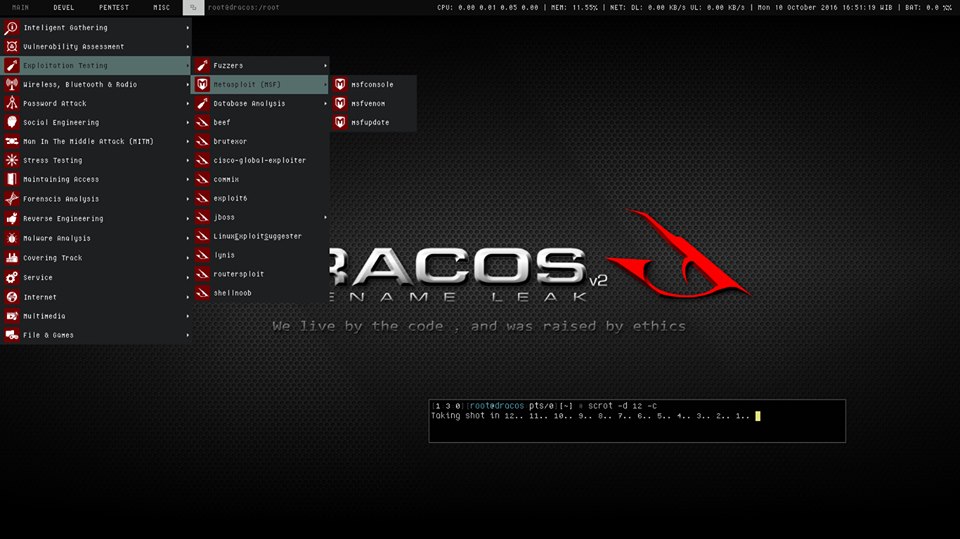
Dracos Linux ( www.dracos-linux.org ) is the Linux operating system from Indonesian

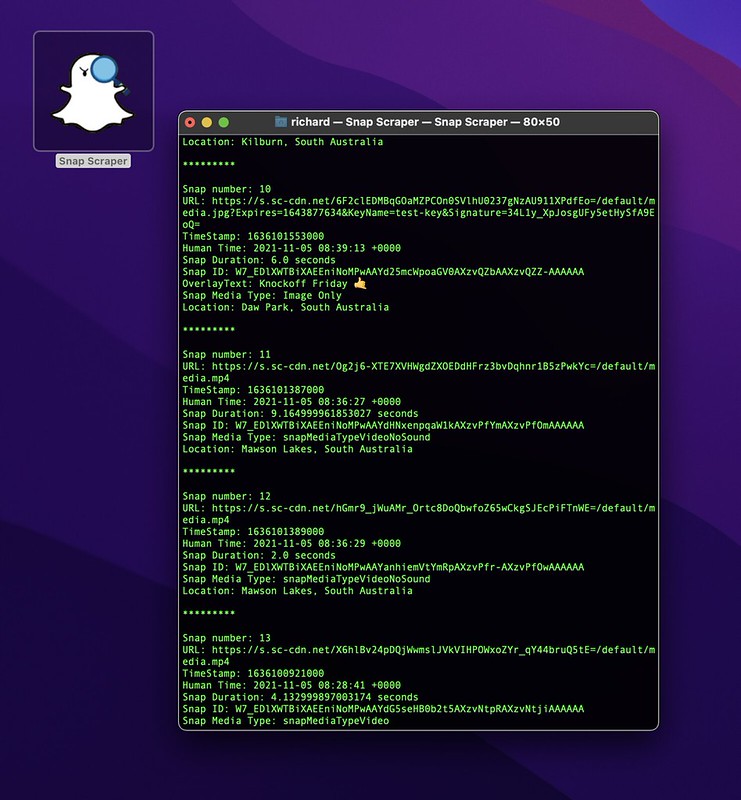
Extracts and downloads Snap Map media by coordinates for OSINT, forensic analysis, and research. Supports metadata logging and bulk download.

OpenFPC, Open Source Full Packet Capture

Cross-platform memory dumper using Frida to extract accessible memory from iOS, Android, and Windows applications for forensic analysis and…

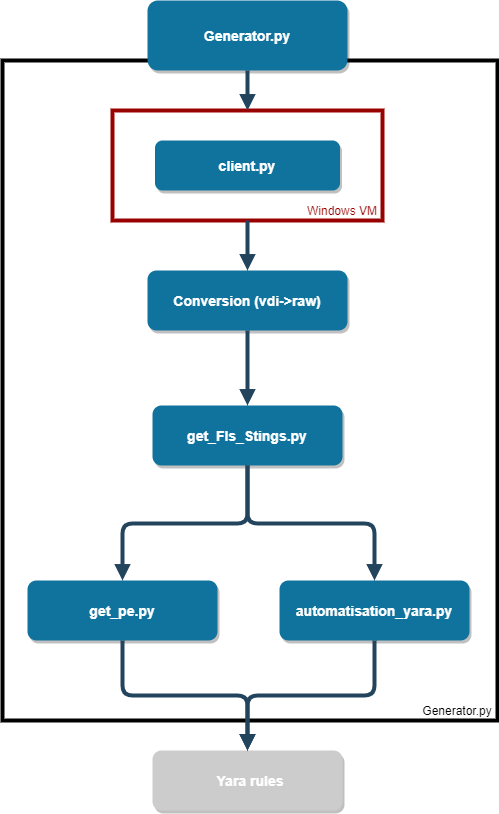
Generates YARA rules from installed software on a running OS to baseline known software and find similar installations across digital forensic…