

oletools
 decalage2/oletools
Python toolkit for analyzing MS OLE2 and Office documents, extracting VBA macros, detecting exploits, and performing forensic analysis of structured…
code-analysisdigital-forensicsforensics+3
3.4k
decalage2/oletoolsPython toolkit for analyzing MS OLE2 and Office documents, extracting VBA macros, detecting exploits, and performing forensic analysis of structured…
 cert-lv/exchange_webshell_detection
Detect webshells dropped on Microsoft Exchange servers exploited through "proxylogon" group of vulnerabilites (CVE-2021-26855, CVE-2021-26857,…
 kaandemir993/vidar-stealer-reverse-engineering
"In-depth reverse engineering analysis of Vidar Stealer 2.0 covering Task Scheduler tampering (1999 timestamps), Explorer.exe process hollowing, and…
 cameloo1/sharepoint-toolshell-micro-postmortem
Reproducible incident micro-postmortem for on-prem Microsoft SharePoint “ToolShell” (CVE-2025-53770): ATT&CK snapshot, “logs that matter” table,…
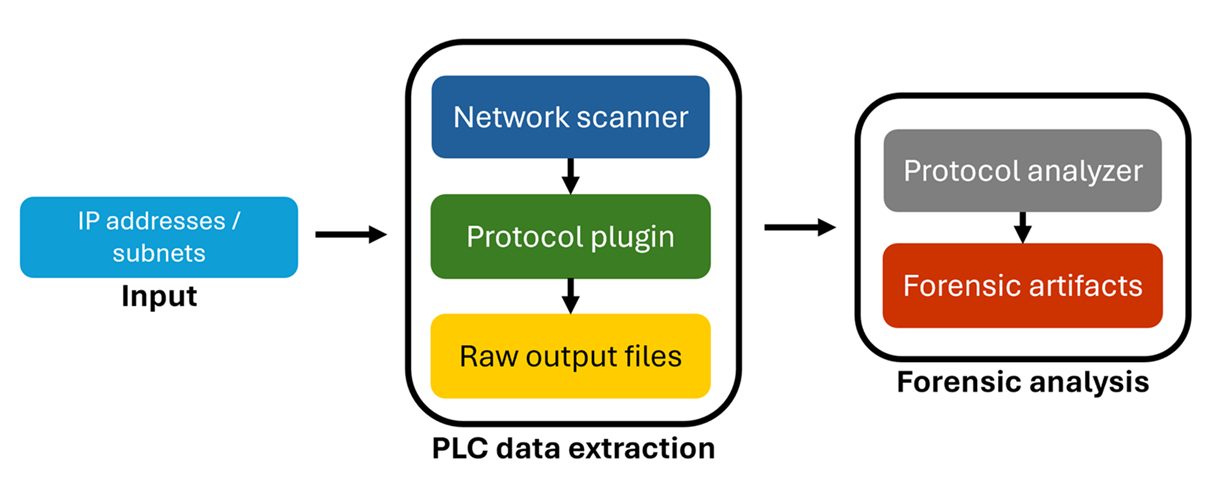 microsoft/ics-forensics-tools
Open-source forensics framework for analyzing Industrial PLC metadata and project files. Scans for suspicious artifacts in ICS environments to…
 zach115th/toolshellfinder
Scans Windows IIS logs for signs of CVE-2025-53770 & CVE-2025-53771
 synacktiv/forensic-msvpn
This repository contains Velociraptor artifact and Chainsaw rules to help detect Microsoft Remote Access VPN activity
 gyaansastra/cve-2022-30190
Comprehensive analysis of CVE-2022-30190 (Follina MSDT vulnerability) with IOCs, detection rules for SIEMs/EDR, YARA signatures, mitigation scripts,…
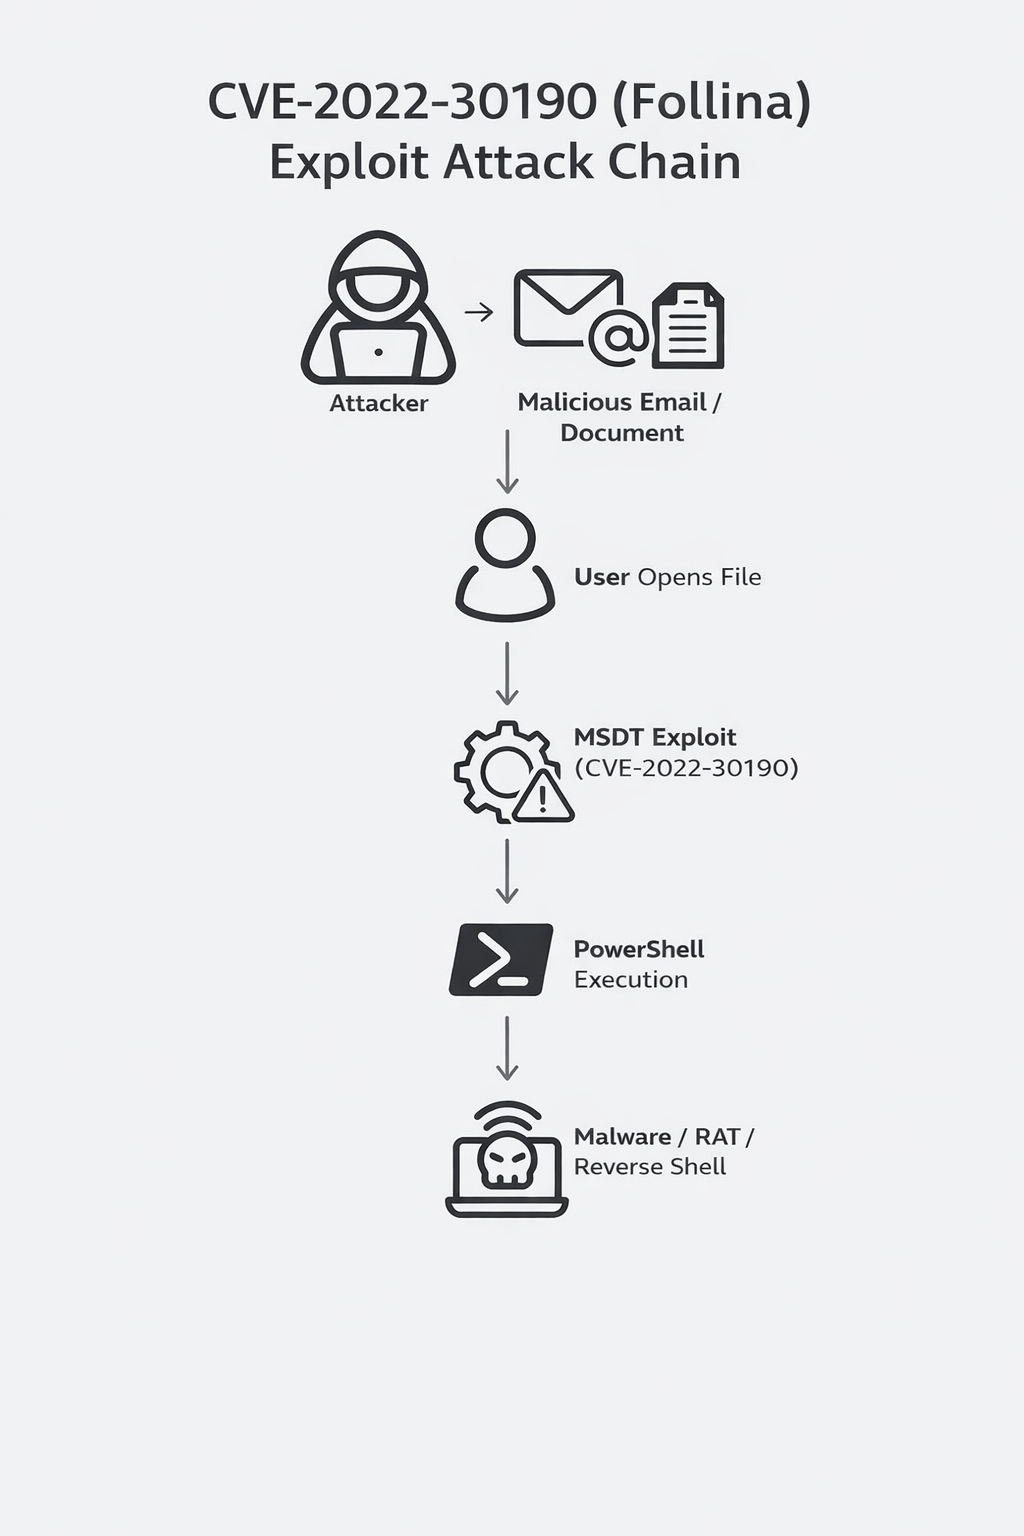 nimesh895/malware-analysis-follina-cve-2022-30190
Step-by-step static malware analysis of a Follina (CVE-2022-30190) exploit document, covering file extraction, VirusTotal correlation, MITRE ATT&CK…
 nccgroup/metadataplus
A tool to use novel locations to extract metadata from Office documents.
 rjsudlow/proxynotshell-ioc-checker
Script to check for IOC's created by ProxyNotShell (CVE-2022-41040 & CVE-2022-41082)
 forentfraps/pe-signgen
Universal signature generation for any system function from all Windows Builds using Winbindex
 microsoft/avml
Portable Linux RAM acquisition tool for forensics and incident response, capturing LiME-compatible images with optional compression and remote…
 microsoft/etl2pcapng
Utility that converts an .etl file containing a Windows network packet capture into .pcapng format.
 microsoft/routeros-scanner
Tool to scan for RouterOS (Mikrotik) forensic artifacts and vulnerabilities.
 maldev-academy/dumpbrowsersecrets
Extracts browser-stored data such as refresh tokens, cookies, saved credentials, credit cards, autofill entries, browsing history, and bookmarks from…
 dfir-orc/dfir-orc
Forensics artefact collection tool for systems running Microsoft Windows
 blacksnufkin/invoke-dumpmdeconfig
PowerShell script to dump Microsoft Defender Config, protection history and Exploit Guard Protection History (no admin privileges required )